
TA416 Resumes Espionage Campaigns Against European Governments, Expands Into Middle East
Summary
Proofpoint details TA416’s renewed espionage targeting of European governments from mid-2025 and Middle Eastern entities in March 2026, describing evolving phishing and malware-delivery chains that deploy a custom PlugX backdoor.
Key points
- Proofpoint observed TA416 resume regular targeting of European government and diplomatic entities in mid-2025, including NATO and EU missions; campaigns expanded to Middle Eastern government and diplomatic targets in March 2026.
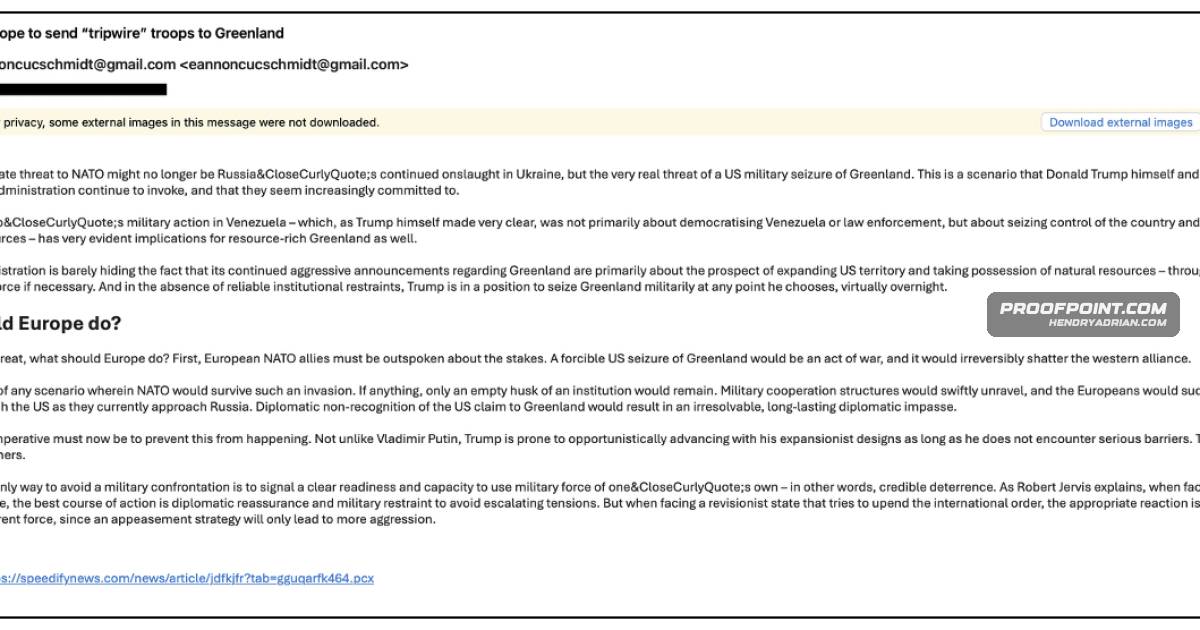
- Web-bug phishing campaigns used unique tracking URLs to assess email delivery and engagement, while malware campaigns also used attacker-controlled or compromised government and diplomatic accounts.
- Delivery chains evolved from fake Cloudflare Turnstile pages and Microsoft Entra ID OAuth redirects to ZIP smuggling with LNK files and MSBuild/CSPROJ downloaders.
- The different chains ultimately delivered a signed executable, malicious DLL, and encrypted payload triad to load a custom PlugX backdoor through DLL sideloading.
- Recent PlugX variants use API hashing and code obfuscation, persist through a Run registry key, and communicate over HTTP using an RC4-encrypted protocol; newer C2 traffic changed its headers and URI construction.
- Proofpoint assessed that TA416’s targeting may reflect intelligence-collection priorities linked to geopolitical events; it also noted that the nature of any relationship with the distinct UNK_SteadySplit cluster remains unclear.
Article Details
- Attack Vectors
- TA416 used spearphishing emails with web bugs and unique tracking URLs to assess delivery and recipient engagement.
- The group sent malicious archive links through attacker-controlled freemail accounts and compromised government or diplomatic mailboxes.
- Fake Cloudflare Turnstile pages and Microsoft Entra ID OAuth redirects led targets to malicious archives or attacker-controlled download domains.
- ZIP smuggling concealed MSI or TAR stages in archives; embedded LNK files ran PowerShell to locate the archive, extract a stage, and execute it.
- Archives containing a renamed MSBuild executable and malicious CSPROJ files used decoded URLs to download payload components.
- TA416 used signed executables, malicious DLLs, and encrypted payloads in DLL-sideloading chains to load its customized PlugX backdoor.
- Defensive Notes
- Proofpoint listed ET rules 2068412 and 2068413 for TA416 PlugX C2 GET activity and 2068414 for POST activity.
- Inspect suspicious archives for embedded LNK files and ZIP smuggling, and for renamed MSBuild executables paired with malicious CSPROJ files.
- The reported PlugX persistence used a Run registry key named Canon to launch CNMNSST.exe from C:UsersPublicCanon.
- The reported PlugX C2 sequence used HTTP GET and POST requests with an RC4-encrypted binary protocol.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cnrelojes[.]com | Listed as a TA416 C2 domain. |
| DOMAIN | ombut[.]com | TA416 PlugX configuration identifies this domain as C2 infrastructure. |
| DOMAIN | phpthemes[.]net | Listed as a domain used for TA416 web-bug campaigns. |
| DOMAIN | speedifynews[.]com | TA416 infrastructure used for web-bug tracking and associated links. |
| DOMAIN | welnetsanda[.]org | Listed as a domain used for TA416 web-bug campaigns. |
emmeline[.]voss@gmail[.]com | Sender address used in TA416 web-bug phishing campaigns. | |
hsuhalingaye26@gmail[.]com | Sender address used in TA416 malware-delivery campaigns. | |
kordula[.]wehrli@gmail[.]com | Sender address used in TA416 web-bug phishing campaigns. | |
office2000005@gmail[.]com | Sender address used in TA416 malware-delivery campaigns. | |
| HOSTNAME | attd[.]z23[.]web[.]core[.]windows[.]net | TA416 actor-hosted Azure Blob Storage delivery host listed in the indicators. |
| HOSTNAME | filesdownld[.]z13[.]web[.]core[.]windows[.]net | TA416 actor-hosted Azure Blob Storage delivery host listed in the indicators. |
| HOSTNAME | filestoretome[.]z23[.]web[.]core[.]windows[.]net | TA416 actor-hosted Azure Blob Storage delivery host listed in the indicators. |
| HOSTNAME | mydownfile[.]z11[.]web[.]core[.]windows[.]net | TA416 actor-hosted Azure Blob Storage delivery host listed in the indicators. |
| HOSTNAME | mydownloadfile[.]z7[.]web[.]core[.]windows[.]net | TA416 actor-hosted Azure Blob Storage delivery host listed in the indicators. |
| HOSTNAME | reloadsite[.]z13[.]web[.]core[.]windows[.]net | Listed as a TA416 malware-delivery hostname. |
| SHA256 | 4ed76fa68ef9e1a7705a849d47b3d9dcdf969e332bd5bcb68138579c288a16d3 | Hash of cnmpaui.exe, a signed executable TA416 abused to load PlugX through DLL sideloading. |
| SHA256 | b6d866054dedf7a882dd1fa405a066de1278e35acf639b3a0e850a637d27c4bc | Identified in the article's indicator summary as the hash of the malicious CNCLID.dll loader. |
| URL | hxxps[:]//gooledives[.]z48[.]web[.]core[.]windows[.]net/election_2026.html | TA416-hosted delivery page listed among campaign URLs. |
| URL | hxxps[:]//mydownload[.]z29[.]web[.]core[.]windows[.]net/nv2199_update_on_situation_of_cambodia-thailand_border.html | Fake Cloudflare Turnstile challenge page used in a TA416 malware-delivery chain. |
| URL | hxxps[:]//mydownload[.]z29[.]web[.]core[.]windows[.]net/nv2230_update_of_situation_on_cambodia-thailand_border.html | Fake Cloudflare Turnstile challenge page used in a TA416 malware-delivery chain. |
| URL | hxxps[:]//web[.]florarevival[.]com/download/a6d6u9ff13?error=interaction_required&error_description=session+information+is+not+sufficient+for+single-sign-on.&state=6 | TA416 redirect URL identified as delivering a malicious archive. |
| URL | hxxps[:]//www[.]bushidomma[.]net/download/l7o9afe?error=interaction_required&error_description=session+information+is+not+sufficient+for+single-sign-on.&state=2 | TA416 redirect URL identified as delivering a malicious archive. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loaders and payloads used obfuscation including API hashing, junk code, and control-flow flattening.T1059.001 · PowerShellLNK files ran embedded PowerShell commands to locate ZIP archives, extract stages, and execute them.T1071.001 · Web ProtocolsPlugX communicated with C2 over HTTP using an RC4-encrypted binary protocol.T1078 · Valid AccountsThe group used compromised government and diplomatic mailboxes to send phishing and delivery emails.T1218 · System Binary Proxy ExecutionA renamed legitimate MSBuild executable ran malicious CSPROJ files that downloaded payload components.T1547.001 · Registry Run Keys / Startup FolderTA416 established persistence with a Run registry key that launched the sideloading executable.T1566.001 · Spearphishing AttachmentTA416 used ZIP archives containing LNK files in its delivery chains.T1566.002 · Spearphishing LinkTA416 used phishing links and web-bug URLs for reconnaissance and to lead targets to payload delivery.T1574.001 · DLLTA416 used signed-executable, malicious-DLL, and encrypted-payload triads to load PlugX.
Threat Actors
TA416Proofpoint tracks TA416 as a China-aligned threat actor that resumed targeting European government and diplomatic entities and expanded to Middle Eastern targets. The article attributes web-bug reconnaissance, phishing delivery chains, and PlugX deployment to the group.UNK_SteadySplitProofpoint tracks UNK_SteadySplit as a distinct malicious cluster using TONESHELL, PUBLOAD, and other malware in phishing campaigns. Proofpoint describes historical technical overlaps with TA416 but says it cannot assess the nature of any organizational, personnel, or hierarchical link.
Malware
PlugXsmuggling with LNK files, and MSBuild/CSPROJ downloaders—ultimately loading a heavily obfuscated custom PlugX backdoor via DLL sideloading.PubloadUNK_SteadySplit is a user of the custom TONESHELL and PUBLOAD malware families, alongside multiple other first-stage malware families delivered in phishing campaigns.TONESHELLUNK_SteadySplit is a user of the custom TONESHELL and PUBLOAD malware families, alongside multiple other first-stage malware families delivered in phishing campaigns.
Vendors
CloudflareThe actor employed waves of web-bug reconnaissance and evolving malware delivery chains—fake Cloudflare Turnstile pages, Microsoft Entra OAuth redirects, ZIP smuggling with LNK files, and MSBuild/CSPROJGoogleMalware delivery used attacker-controlled freemail and compromised government/diplomatic accounts pointing to payloads hosted on Azure Blob Storage, Google Drive, compromised SharePoint, and actor domains.Microsoftwaves of web-bug reconnaissance and evolving malware delivery chains—fake Cloudflare Turnstile pages, Microsoft Entra OAuth redirects, ZIP smuggling with LNK files, and MSBuild/CSPROJ downloaders—ultimately loading a
Products
Cloudflare TurnstileThe actor employed waves of web-bug reconnaissance and evolving malware delivery chains—fake Cloudflare Turnstile pages, Microsoft Entra OAuth redirects, ZIP smuggling with LNK files, and MSBuild/CSPROJGoogle DriveMalware delivery used attacker-controlled freemail and compromised government/diplomatic accounts pointing to payloads hosted on Azure Blob Storage, Google Drive, compromised SharePoint, and actor domains.Microsoft Azure Blob Storage[Hostname ] Microsoft Azure Blob Storage hostnames used to host delivery pages and archives – mydownload.z29.web.core.windows[.]net, gooledives.z48.web.core.windows[.]net (actor-hosted delivery landing pages and fakeMicrosoft Entra IDfrom using fake Cloudflare Turnstile challenge pages that gated access to ZIP archives, to abuse of Microsoft Entra ID thirdâparty applications that redirected users to attacker-controlled malware delivery domains,Microsoft SharePointMalware delivery used attacker-controlled freemail and compromised government/diplomatic accounts pointing to payloads hosted on Azure Blob Storage, Google Drive, compromised SharePoint, and actor domains.
Tools
MSBuildCloudflare Turnstile pages, Microsoft Entra OAuth redirects, ZIP smuggling with LNK files, and MSBuild/CSPROJ downloaders—ultimately loading a heavily obfuscated custom PlugX backdoor via DLL sideloading.PowerShellCloudflare Turnstile pages, Microsoft Entra OAuth silent redirects, ZIP smuggling with LNK-based PowerShell, and MSBuild + CSPROJ downloaders—while keeping DLL sideloading triads to load PlugX.
Countries
Iraninto Middle Eastern diplomatic and government organizations following the outbreak of conflict in Iran.MongoliaFrom mid-2023 until mid-2025, Proofpoint observed minimal TA416 targeting within Europe, with the group mostly active across Southeast Asia, Taiwan, and Mongolia during this period.TaiwanFrom mid-2023 until mid-2025, Proofpoint observed minimal TA416 targeting within Europe, with the group mostly active across Southeast Asia, Taiwan, and Mongolia during this period.
Industries
DefenseIn late September 2025, Proofpoint observed TA416 conduct multiple malware delivery campaigns targeting European ministries of defense and ministries of foreign affairs.Diplomacyand Mongolia, is consistent with a renewed intelligence-collection focus against EU and NATO-affiliated diplomacy entities.GovernmentProofpoint observed China-aligned TA416 resume systematic targeting of European government and diplomatic entities from mid-2025 through early 2026 and expand operations into Middle Eastern diplomatic and government