
Fake Coca-Cola and Ferrari Job Offers Target Google and Facebook Credentials
Summary
Malwarebytes describes two job-themed phishing campaigns impersonating Coca-Cola and Ferrari. One relays Google Workspace credentials and MFA challenges through a fake Chrome window; the other uses a fake careers portal to target Facebook logins.
Key points
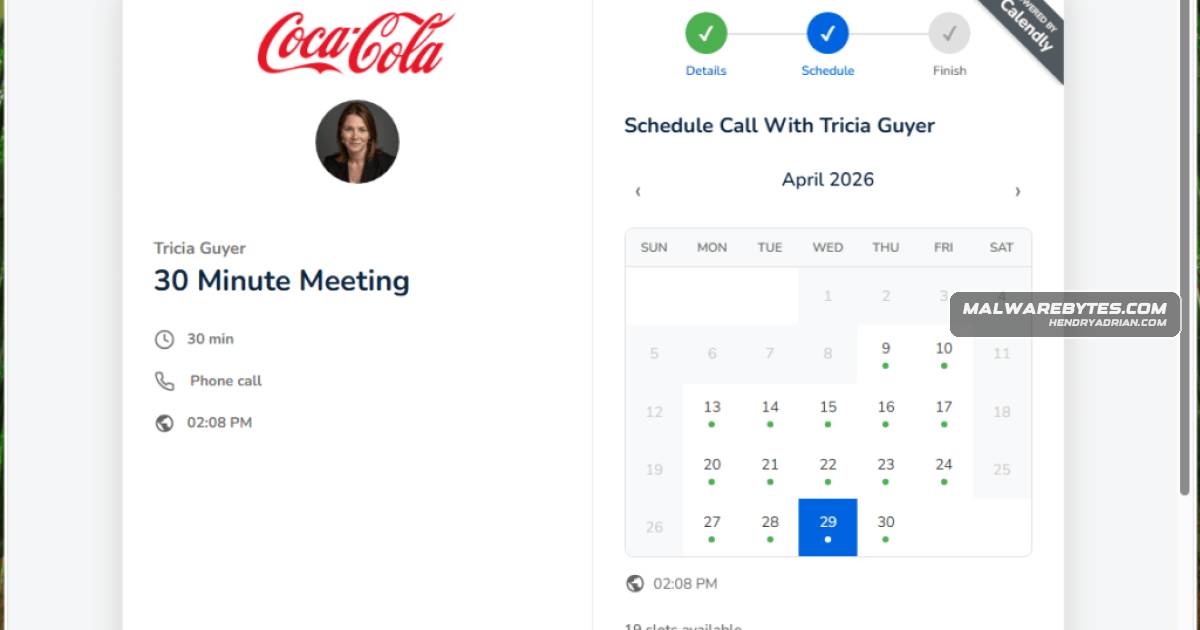
- The Coca-Cola-themed booking page collects job-seeker details before presenting a simulated Chrome window with a fake Google sign-in form.
- The kit sends submitted credentials to an attacker-controlled backend and polls it every three seconds for instructions on which MFA prompt to display.
- The article says the kit can relay credentials and verification challenges in real time, potentially enabling account takeover even when MFA is enabled.
- The Coca-Cola form rejects @gmail.com addresses, which the article says targets corporate Google Workspace accounts.
- The Ferrari-themed careers page offers Facebook sign-in or email entry, then directs users to a fake Facebook login designed to harvest credentials.
- The article recommends independently verifying job offers, never entering passwords on scheduling pages, and changing passwords and revoking sessions if credentials were submitted.
Article Details
- Attack Vectors
- A Coca-Cola-themed fake scheduling page collects job seekers’ details, then presents a simulated Chrome window with a fake Google sign-in form to harvest Google Workspace credentials.
- The Coca-Cola phishing kit sends submitted credentials to an attacker-controlled backend, polls it for instructions every few seconds, and displays matching prompts to capture email, authenticator, SMS, or Google phone verification codes in real time. It rejects @gmail.com addresses.
- A Ferrari-themed fake careers portal uses an application invitation pop-up to redirect victims to a fake Facebook login page or request an email and passcode.
- Defensive Notes
- Treat unsolicited job offers and scheduling links with suspicion; verify the role and recruiter through the company’s official careers page.
- Check whether a purported browser pop-up can move independently, remains visible when the browser is minimized, and has an interactive URL bar.
- Do not enter account passwords on scheduling pages or unfamiliar job-application pages; verify the URL before submitting credentials.
- If credentials were submitted, change the Google password immediately and revoke active sessions.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | hrguxhellito281[.]onrender[.]com | Attacker-controlled backend domain identified as receiving stolen credentials and supporting the phishing kit’s real-time prompts. |
MITRE ATT&CK
T1056.003 · Web Portal CaptureFake Google and Facebook login pages capture credentials entered by victims.T1078 · Valid AccountsThe Coca-Cola kit relays stolen Google Workspace credentials for use against real accounts, potentially enabling account takeover.T1111 · Multi-Factor Authentication InterceptionThe Coca-Cola kit captures verification codes and relays MFA challenges in real time to support account takeover.T1566 · PhishingThe campaigns use deceptive scheduling and careers pages to lure victims into credential phishing.
Products
Calendly[Name ] recruiter identity used in lure – “Tricia Guyer” (name on the fake Calendly scheduling page)FacebookThe Coca-Cola kit notably includes a fake Chrome window that relays credentials and MFA challenges in real time to an attacker-controlled backend, enabling account takeover; the Ferrari lure targets Facebook logins.Google ChromeThe Coca-Cola kit notably includes a fake Chrome window that relays credentials and MFA challenges in real time to an attacker-controlled backend, enabling account takeover; the Ferrari lure targets Facebook logins.Google WorkspaceThe Coca-Cola campaign used a fake in-page Chrome pop-up displaying a Google sign-in URL graphic to collect Google Workspace credentials.