cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2489 articles

Threat Research · trendmicro.com

Void Dokkaebi Uses Fake Job Interviews to Spread Malware Through Developer Repositories

Trend Micro reports that Void Dokkaebi uses fake coding interviews, malicious VS Code tasks, and injected code to spread malware through developer repositories. Its March 2026 scan found more than 750 infected public repositories.
Apr 21, 2026
Threat Research · hunt.io

DinDoor Backdoor Abuses Deno Runtime; Researchers Identify 20 Active C2 Servers

Analysis of two DinDoor samples details their Deno-based execution, victim fingerprinting, and C2 behavior. A query of HTTP response characteristics identified 20 servers active within the week before publication.

Apr 21, 2026
Threat Research · global.ptsecurity.com

CapFix Uses Evolving CapDoor Malware in Attacks on Russian Organizations

Positive Technologies details CapFix campaigns targeting Russian industrial and aviation organizations with phishing lures, compromised infrastructure and evolving CapDoor malware capable of executing commands, downloading payloads and capturing screenshots.

Apr 21, 2026
Threat Research · research.checkpoint.com

Check Point Details The Gentlemen Ransomware's GPO-Based Attack Chain

Check Point Research reconstructs an intrusion involving an affiliate of The Gentlemen RaaS, describing Cobalt Strike, a blocked SystemBC attempt, lateral movement and GPO-based ransomware deployment, and analyzing the locker’s evasion, persistence and encryption.

Apr 20, 2026
Threat Research · bleepingcomputer.com

Check Point Links 1,570-Host SystemBC Botnet to Gentlemen Ransomware Affiliate

Check Point researchers linked a SystemBC botnet of more than 1,570 hosts to a Gentlemen ransomware affiliate, detailing its use for covert payload delivery and an attack chain involving Cobalt Strike, Mimikatz and GPO-based deployment.

Apr 20, 2026
Threat Research · bleepingcomputer.com

Microsoft Details Teams Helpdesk Impersonation Attacks Using Quick Assist

Microsoft describes intrusions using external Teams chats to impersonate helpdesk staff, gain access via Quick Assist, move laterally with WinRM, and collect data with Rclone. It recommends treating external contacts as untrusted and monitoring remote-access tools.

Apr 20, 2026
Threat Research · netskope.com

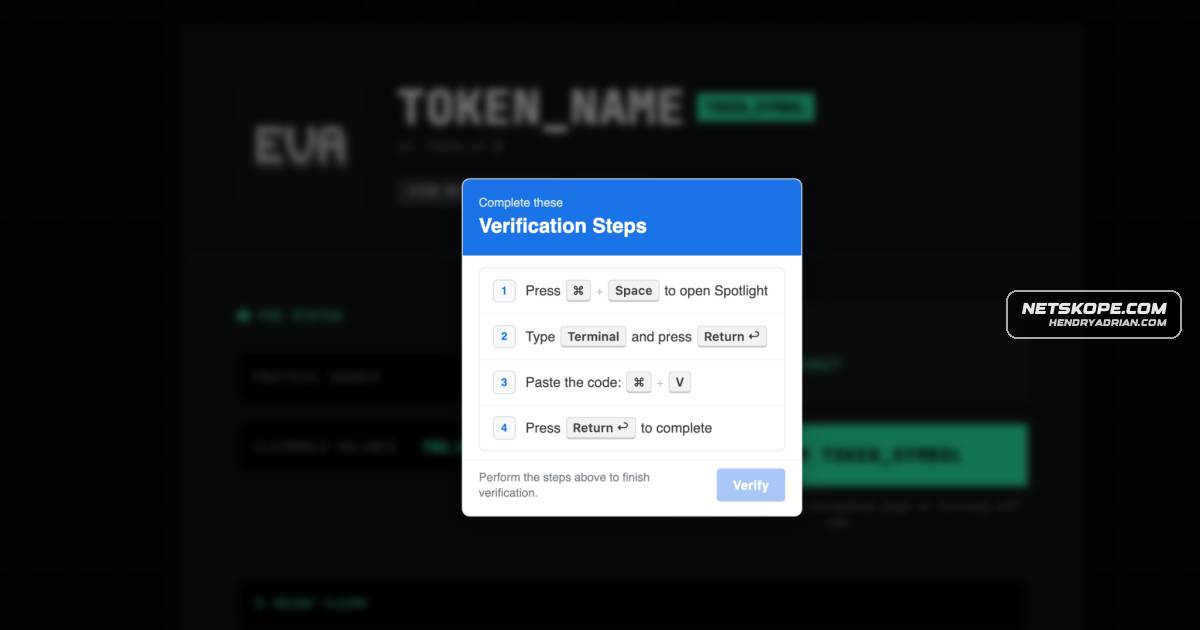
ClickFix Campaign Uses AppleScript Stealer to Target macOS Credentials and Session Cookies

Netskope details a ClickFix campaign that tricks macOS users into running a command, then uses a persistent fake password prompt to steal credentials, keychain and browser data, extension contents, and cryptocurrency wallet files.

Apr 20, 2026
Threat Research · securelist.com

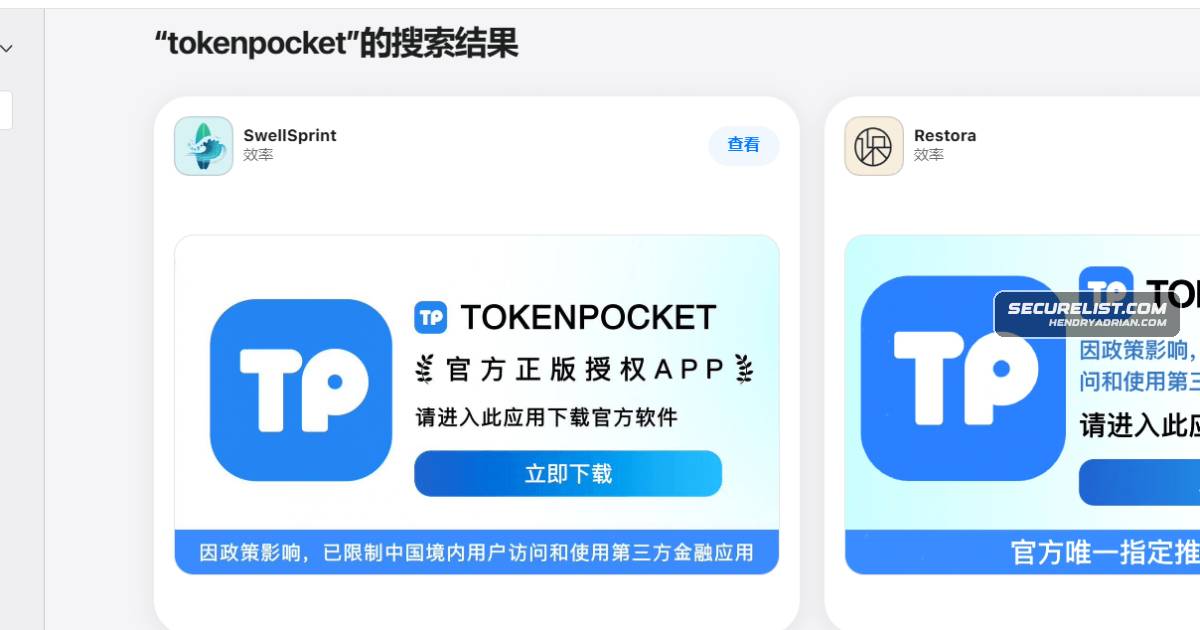
Researchers Find 26 App Store Lures for FakeWallet Crypto-Stealing Campaign

Researchers identified 26 App Store phishing apps that redirect users to trojanized wallets. FakeWallet variants hijack wallet screens or display phishing prompts to capture recovery phrases and send them to command-and-control servers.

Apr 20, 2026
Threat Research · infostealers.com

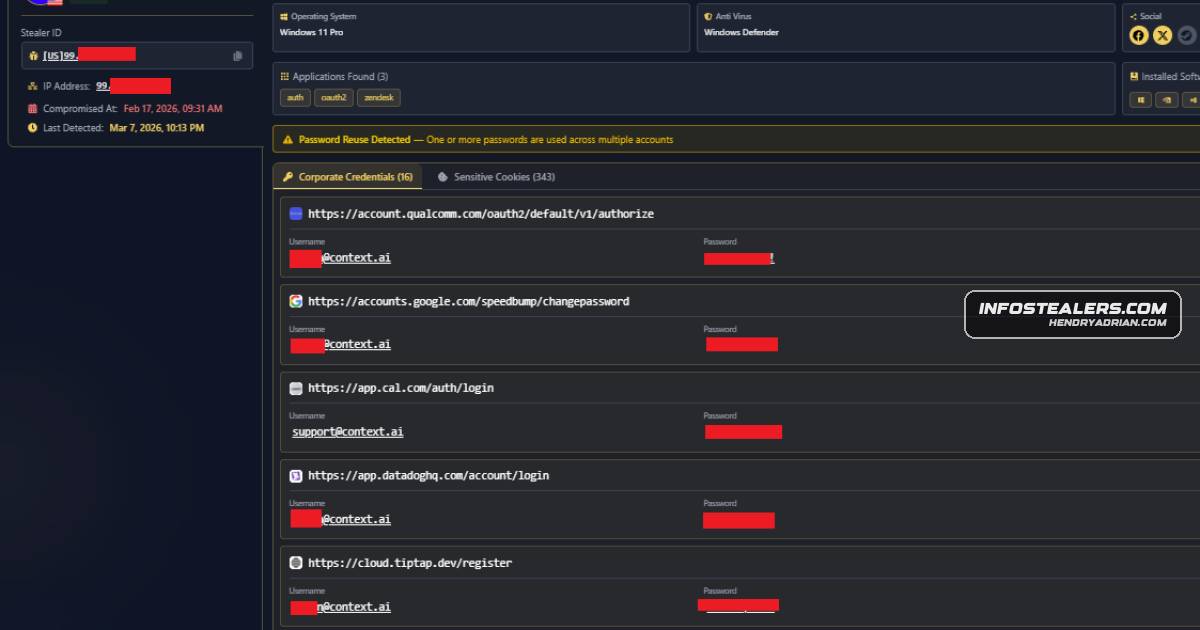
Hudson Rock Says Lumma Infection May Have Enabled Vercel Breach

Hudson Rock says a February 2026 Lumma infection on a Context.ai vendor employee may have exposed credentials later used in the Vercel breach. It cites browser history and access records and recommends checking Google Workspace for a suspicious OAuth app.

Apr 20, 2026
Threat Research · huntress.com

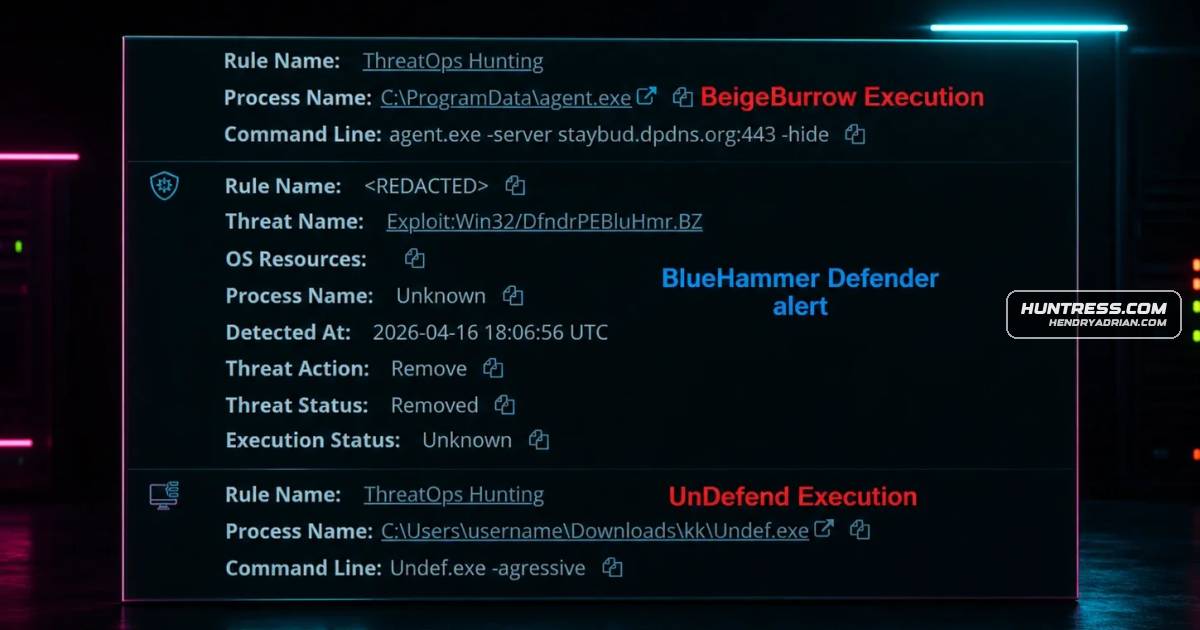
Huntress Links Nightmare-Eclipse Tools to Intrusion Involving FortiGate VPN Access

Huntress details an intrusion involving Nightmare-Eclipse tools, suspicious FortiGate VPN access, reconnaissance and a tunneling agent. The tools appeared unsuccessful; Huntress isolated the organization and recommends reviewing endpoint and VPN telemetry.

Apr 20, 2026
Threat Research · trendmicro.com

Vercel Breach Traced to Stolen OAuth Tokens, Exposing Environment Variables in Compromised Teams

A Lumma Stealer infection at Context.ai led attackers to use stolen OAuth tokens to access Vercel systems and enumerate environment variables in a limited subset of customer projects. The article details the attack chain, risks and defensive steps.

Apr 20, 2026
Threat Research · microsoft.com

Microsoft Details Cross-Tenant Helpdesk Impersonation Intrusion Chain

Microsoft describes a human-operated intrusion chain using cross-tenant Teams helpdesk impersonation to gain Quick Assist access, sideload payloads, pivot with WinRM and exfiltrate data via Rclone. It also provides hunting queries and defenses.

Apr 18, 2026
Threat Research · cyfirma.com

Operation PhantomCLR Abuses .NET AppDomainManager for Stealthy Malware Execution

CYFIRMA analyzes Operation PhantomCLR, a campaign targeting Middle East and EMEA financial organizations. It details AppDomainManager hijacking, JIT-based shellcode execution, reflective loading, sandbox evasion and CloudFront-fronted command-and-control.

Apr 18, 2026
Threat Research · hexastrike.com

109 Fake GitHub Repositories Used to Distribute SmartLoader and StealC

Researchers identified 109 fake GitHub repositories across 103 accounts distributing SmartLoader and StealC. The loader hides execution, collects and exfiltrates host data, resolves C2 through a Polygon contract, and persists with scheduled tasks.

Apr 18, 2026
Threat Research · bleepingcomputer.com

Payouts King Uses Hidden QEMU Virtual Machines to Evade Endpoint Security

Sophos describes two campaigns using hidden Alpine Linux VMs in QEMU to evade host defenses, harvest credentials and enable remote access. One is linked to Payouts King; another exploits CitrixBleed 2. Zscaler says Payouts King is likely tied to former BlackBasta oper​​

Apr 18, 2026
Threat Research · unit42.paloaltonetworks.com

TP-Link CVE-2023-33538 Exploitation Attempts Fail, but Firmware Analysis Confirms Vulnerability

Unit 42 found observed Mirai-like botnet attempts against end-of-life TP-Link routers were flawed, but firmware analysis confirmed authenticated command injection via ssid1 in CVE-2023-33538; default credentials may enable exploitation.

Apr 17, 2026
Threat Research · esentire.com

Kong RAT Campaign Uses SEO Poisoning to Target Chinese-Speaking Developers

eSentire describes a multi-stage Kong RAT campaign that used SEO-poisoned software download sites to target Chinese-speaking developers. Its analysis details the malware’s evasion, persistence, keylogging and modular C2 capabilities.

Apr 17, 2026
Threat Research · zimperium.com

Zimperium Analyzes Four Android Banking Trojan Campaigns Targeting 800+ Apps

Zimperium zLabs investigated RecruitRat, SaferRat, Astrinox, and Massiv, four Android banking trojan campaigns targeting over 800 banking, cryptocurrency, and social media apps. The research details their delivery, evasion, credential theft, and C2 techniques.

Apr 17, 2026
Threat Research · huntress.com

Codex Troubleshooting Complicated Huntress’ Investigation of a Linux Compromise

Huntress says a Linux host targeted by multiple threat actors had a Monero miner, credential theft and data exfiltration. The user’s Codex troubleshooting masked the miner and generated commands that complicated SOC triage.

Apr 17, 2026
Threat Research · huntress.com

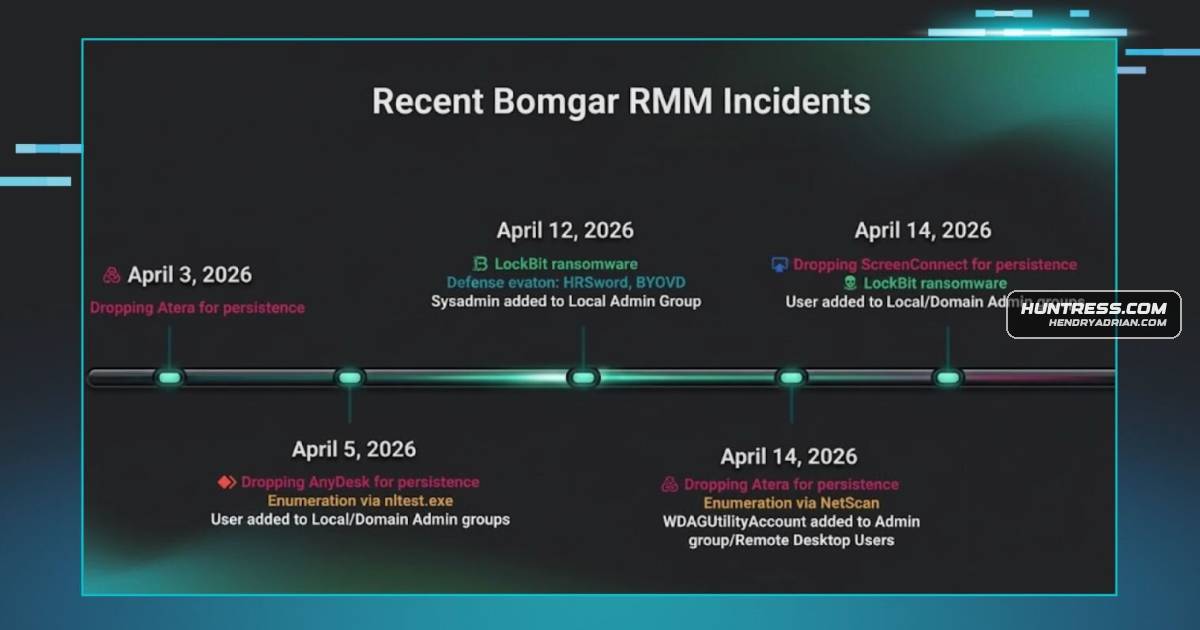
Huntress Reports New Bomgar Exploitation Incidents, Including LockBit Ransomware Attacks

Huntress reports a rise in Bomgar incidents likely exploiting CVE-2026-1731. Attackers used compromised instances for downstream access, persistence, reconnaissance and, in some cases, LockBit ransomware.

Apr 17, 2026
Threat Research · cloudsek.com

RedSun Exploit Uses Windows Defender to Gain SYSTEM Privileges

RedSun exploits a missing reparse-point check in Windows Defender’s remediation process, allowing a local unprivileged user to redirect a file write into System32 and run code as SYSTEM. The article reports that no patch was available at publication.

Apr 17, 2026
Threat Research · bleepingcomputer.com

ZionSiphon OT Malware Targets Water Systems, but Current Sample Is Nonfunctional

Darktrace analyzed ZionSiphon, malware designed to manipulate water-treatment systems. A flawed XOR-based country check currently triggers self-destruction, though the sample includes chlorine-control changes, partial Modbus code, and USB propagation.

Apr 16, 2026
Threat Research · cyble.com

MiningDropper Uses Modular Stages to Deliver Android Malware

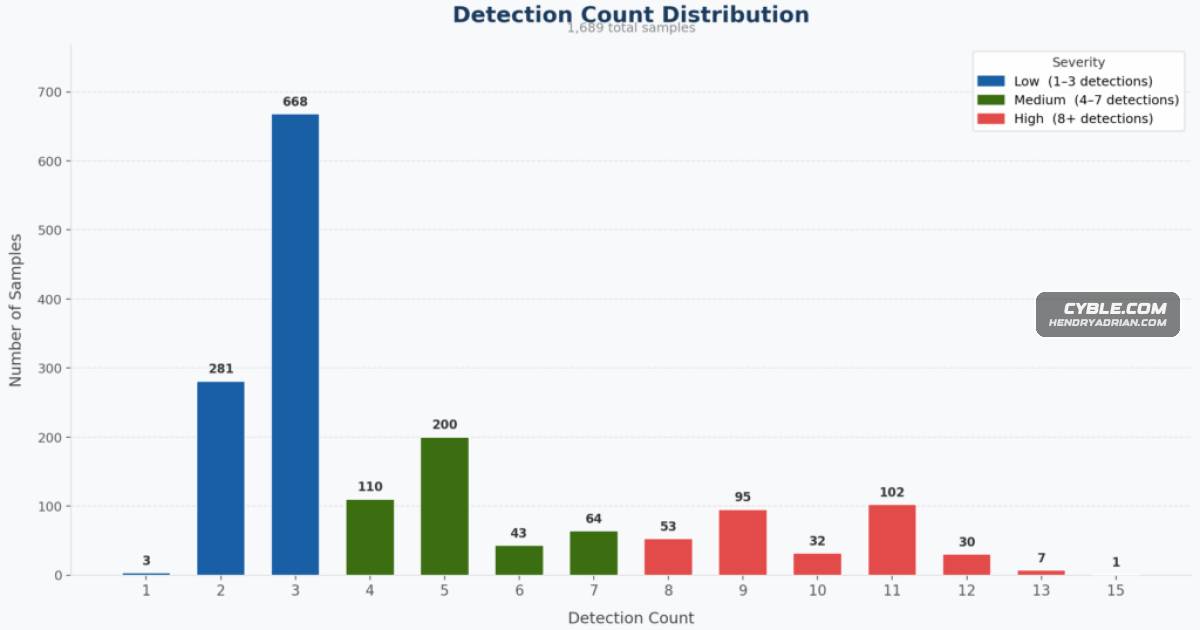
Cyble researchers detail MiningDropper, a modular Android framework that uses obfuscation, staged payload loading and configuration-driven delivery to deploy cryptocurrency miners, infostealers or BTMOB RAT.

Apr 16, 2026
Threat Research · rapid7.com

Rapid7 Analyzes ClickFix Campaign Using Fake Claude Installer

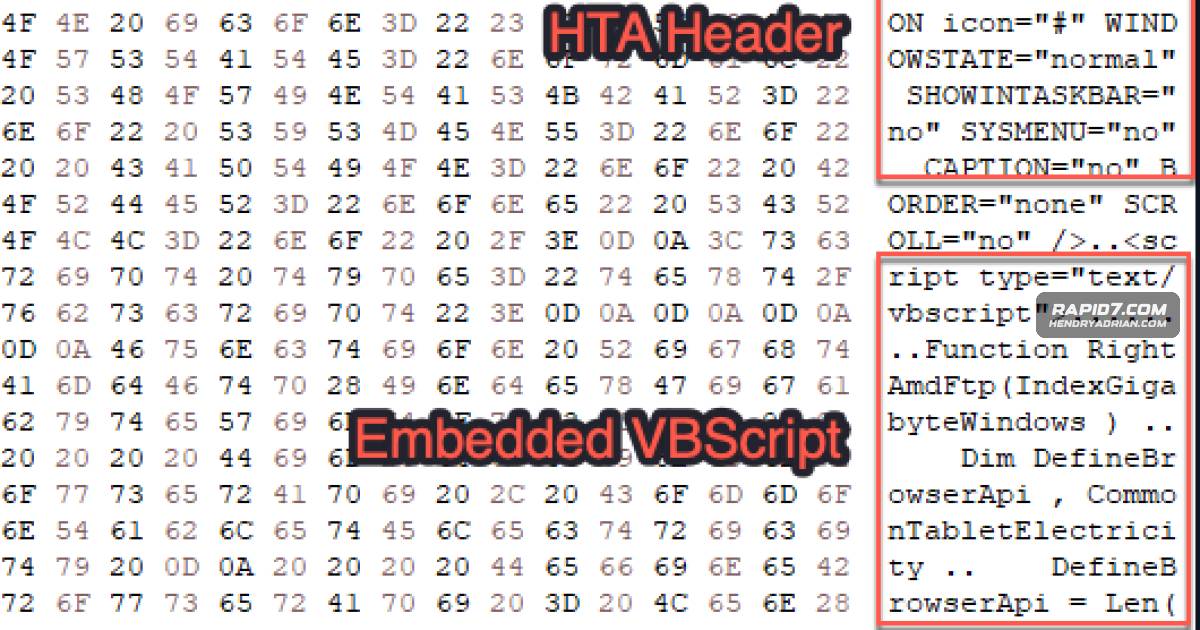
Rapid7 traced a ClickFix campaign impersonating Claude: an MSIX-like archive delivered an HTA that launched staged PowerShell, bypassed AMSI and injected shellcode. Rapid7 detected activity via RunMRU and recommends monitoring it and containing hosts.

Apr 16, 2026
PreviousPage 69 of 104 Next
© 2026 cyber.hendryadrian.com