
Hudson Rock Says Lumma Infection May Have Enabled Vercel Breach
Summary
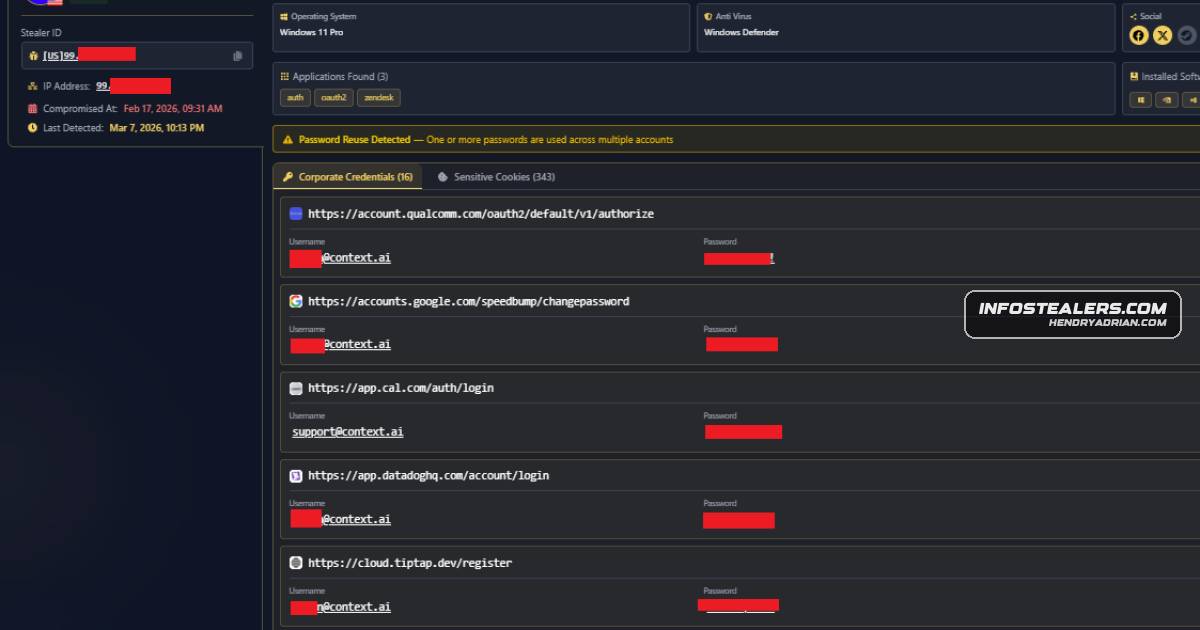
Hudson Rock says a February 2026 Lumma infection on a Context.ai vendor employee may have exposed credentials later used in the Vercel breach. It cites browser history and access records and recommends checking Google Workspace for a suspicious OAuth app.
Key points
- Hudson Rock identifies a February 2026 Lumma infection on a Context.ai vendor employee as a possible initial-access path, citing the employee's browser history and its cybercrime database.
- The browser history reportedly showed searches for and downloads of Roblox “auto-farm” scripts and executors.
- Hudson Rock says the infection exposed Google Workspace, Supabase, Datadog, Authkit, and Vercel credentials, including access to Vercel administrative settings and logs.
- ShinyHunters reportedly advertised stolen Vercel data; the article presents the link between the infection and the breach as likely, not proven.
- The article recommends auditing Google Workspace for a specified OAuth app and revoking its access if present, followed by incident response to check for unauthorized data egress.
Article Details
- Attack Vectors
- A Context.ai employee was reportedly infected with Lumma after downloading Roblox “auto-farm” scripts and executors.
- The infection exposed corporate and administrative credentials for Google Workspace, Supabase, Datadog, Authkit, and Vercel.
- Hudson Rock assesses that ShinyHunters likely used the compromised access to pivot into Vercel; the article also reports claims that stolen Vercel data was being sold.
- Defensive Notes
- Rapidly detect infostealer infections and revoke exposed credentials to limit their use in further intrusions.
- Audit Google Workspace for the OAuth Client ID listed in the article; if present, revoke the application's access and investigate for unauthorized data egress.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| URL | hxxps[:]//110671459871-30f1spbu0hptbs60cb4vsmv79i7bbvqj[.]apps[.]googleusercontent[.]com/ | OAuth Client ID URL that the article identifies as associated with the malicious application to check for in Google Workspace. |
MITRE ATT&CK
Threat Actors
Malware
Vendors
AuthkitCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsContext.aiHudson Rock found that a recent Lumma stealer infection on a Context.ai thirdâparty employee—triggered by downloading Roblox “autoâfarm” scripts—likely provided the initial access that enabled the Vercel breach.DatadogCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsGoogleCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsSupabaseCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsVercelHudson Rock found that a recent Lumma stealer infection on a Context.ai thirdâparty employee—triggered by downloading Roblox “autoâfarm” scripts—likely provided the initial access that enabled the Vercel breach.
Products
AuthkitCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsDatadogCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsGoogle WorkspaceCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsRobloxHudson Rock found that a recent Lumma stealer infection on a Context.ai thirdâparty employee—triggered by downloading Roblox “autoâfarm” scripts—likely provided the initial access that enabled the Vercel breach.SupabaseCompromised Google Workspace, Supabase, Datadog, Authkit, and Vercel admin credentials were reportedly used or sold by ShinyHunters, underscoring that rapid detection and revocation of infostealerâexposed credentialsVercelHudson Rock found that a recent Lumma stealer infection on a Context.ai thirdâparty employee—triggered by downloading Roblox “autoâfarm” scripts—likely provided the initial access that enabled the Vercel breach.