
MiningDropper Uses Modular Stages to Deliver Android Malware
Summary
Cyble researchers detail MiningDropper, a modular Android framework that uses obfuscation, staged payload loading and configuration-driven delivery to deploy cryptocurrency miners, infostealers or BTMOB RAT.
Key points
- CRIL reports MiningDropper campaigns targeting users in India, LATAM, Europe and Asia, using phishing lures impersonating services such as banks, telecom providers and RTOs.
- The dropper uses a trojanized LumoLight app, XOR-obfuscated native code, anti-emulation checks and staged DEX loading.
- AES keys are derived from asset filenames; configuration files determine whether the framework installs a miner or a user-defined payload.
- In the analyzed sample, split APK components are reconstructed to install BTMOB RAT, which the article says supports credential theft, keylogging, data exfiltration and remote control.
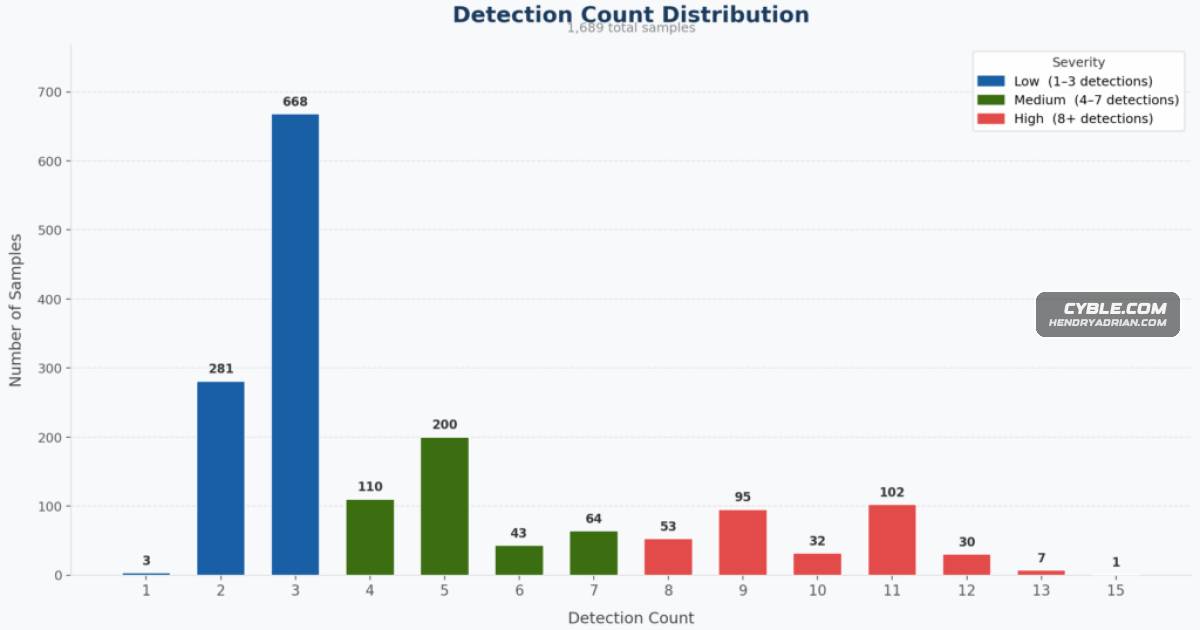
- CRIL identified more than 1,500 samples; it reports that over half had minimal antivirus detection, with about 668 samples showing three detections.
- The researchers recommend installing apps from trusted sources, scrutinizing permissions and suspicious links, enabling MFA for financial apps, and keeping Android devices updated.
Article Details
- Attack Vectors
- Phishing websites distributing malicious APK files
- Smishing, social media links, and fraudulent websites
- Lures impersonating regional transport offices, banks, and telecommunications providers
- Defensive Notes
- Install apps only from trusted sources and avoid APK links received via SMS, social media, or email.
- Verify URLs and avoid suspicious links or websites requesting sensitive information.
- Review app permissions before installing or granting access.
- Enable multi-factor authentication for banking and financial apps.
- Use mobile security software with real-time scanning and keep the operating system and apps updated.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 58a94f889547db8b2327a62e03fb2cce3bda716278d645ee8094178ecda2e9e6 | SHA-256 of the Free Secure – Annulation.apk sample analyzed in the article. |
| URL | hxxps[:]//cardcpp[.]online/imobile.apk | URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//cardhelp[.]live/SBICreditCard.apk | URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//dkfootwearstore[.]shop/Jio%20Free%20Recharge.apk | Specific APK download URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//downloadhdfcapp[.]pythonanywhere[.]com/download/latest.apk | Specific APK download URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//free-secure[.]com/Free%20Secure%20-%20Annulation[.]apk | Specific APK download URL used to distribute the analyzed MiningDropper sample in the BTMOB RAT campaign. |
| URL | hxxps[:]//getchaiian[.]short[.]gy/Getchallan0176 | URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//googleeplaaystore[.]pages[.]dev/assets/AGENDA2026[.]apk | Specific APK download URL identified as distributing MiningDropper in the BTMOB RAT campaign. |
| URL | hxxps[:]//hamzaansari1612-ux[.]github[.]io/ICICI00/imobile.apk | URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//litter[.]catbox[.]moe/o6pxvp[.]apk | Specific APK download URL identified as distributing MiningDropper in the BTMOB RAT campaign. |
| URL | hxxps[:]//protectcc[.]online/imobile.apk | URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/singhsonali3021-pixel/my-apk/main/ICICI%20BANK%20CREDIT%20CARD.apk | Specific APK download URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//tv-pluto[.]vercel[.]app/PlutoTv[.]apk | Specific APK download URL identified as distributing MiningDropper in the BTMOB RAT campaign. |
| URL | hxxps[:]//www[.]dl[.]dropboxusercontent[.]com/scl/fi/r9d5y9ch1k7dwvw6l36rj/TecnoCasaFotosPiso[.]apk?rlkey=z6n2qvft8v3nzm66fgy6acwcx | Specific cloud-hosted APK URL identified as distributing MiningDropper in the BTMOB RAT campaign. |
| URL | hxxps[:]//www[.]icicimanagecards[.]online/iMobile%20Lite.apk | Specific APK download URL identified as distributing MiningDropper in the India-focused infostealer campaign. |
| URL | hxxps[:]//www[.]kavoutai[.]com/signed[.]apk | URL identified as distributing MiningDropper in the BTMOB RAT campaign. |
MITRE ATT&CK
T1406The dropper uses XOR-obfuscated native strings and AES-encrypted payload assets.T1426The dropper queries platform details, system architecture, and device model to identify the execution environment.T1575The trojanized app loads a native library that decrypts payloads and supports their execution.T1633The app checks device details for emulation or rooted environments and terminates malicious execution if detected.T1660MiningDropper was distributed through phishing sites, with victims lured to download malicious APK files.
Malware
BeatBankerRecently, CRIL observed a notable surge in the use of MiningDropper (also referred to as BeatBanker) as an adaptable malware delivery framework for distributing infostealers, Remote Access Trojans (RATs), and bankingBTMOBframework that initially deploys a cryptocurrency miner then can transition to deliver infostealers or BTMOB RAT via staged, configuration-driven payloads.MiningDropperCRIL observed a rapid surge in the distribution of MiningDropper, a modular Android dropper framework that initially deploys a cryptocurrency miner then can transition to deliver infostealers or BTMOB RAT via staged,SpySolrWe first identified BTMOB RAT in February 2024 as a variant of the SpySolr malware, capable of credential harvesting, device takeover, real-time remote control, and facilitating financial fraud operations.