cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2489 articles

Threat Research · blog.sekoia.io

Sekoia Details RePythonNET Automation for .NET Malware Analysis

Sekoia TDR details a pythonnet/dnlib workflow for decrypting strings in an APT28-modified Covenant Grunt, decompiling .NET malware, and automating analysis through its released RePythonNET-MCP server.
Apr 16, 2026
Threat Research · blog.sucuri.net

Obfuscated PHP Backdoor Uses Remote C2 to Inject SEO Spam into Joomla Sites

Sucuri analyzed an obfuscated PHP backdoor in a compromised Joomla site. The loader contacts remote C2 servers to retrieve instructions that can redirect visitors or inject spam and other content.

Apr 16, 2026
Threat Research · proofpoint.com

Proofpoint Details Cargo-Theft Actor’s Post-Compromise Playbook

Proofpoint observed a cargo-theft actor in a decoy environment for over a month, using multiple remote management tools and a third-party signing service for persistence while conducting reconnaissance for financial and transportation-related access.

Apr 16, 2026
Threat Research · darkowl.com

Analysis Links Ashab al-Yamin’s Claims to a Broader Iranian-Aligned Telegram Network

An analysis of Telegram activity finds Ashab al-Yamin’s attack claims and media circulate across Iranian-aligned channels, complicating attribution and leaving its status as a distinct operational group uncertain.

Apr 16, 2026
Threat Research · securityonline.info

Panther Details OtterCookie npm Campaign Attributed to DPRK Actors

Panther reports that obfuscated npm packages found April 6–9, 2026, delivered OtterCookie through benign-looking wrappers. The malware searches for secrets, scans files via a Vercel-hosted C2, and installs an SSH key backdoor on Linux.

Apr 16, 2026
Threat Research · validin.com

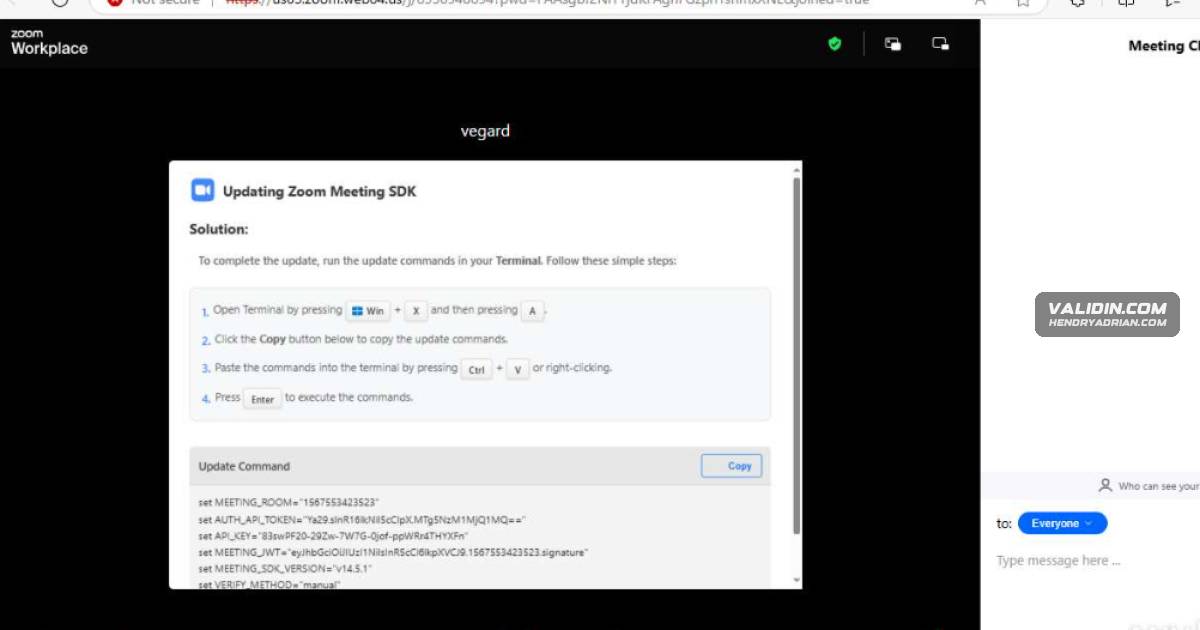
UNC1069 Uses Fake Meetings to Deploy Cross-Platform RATs and Capture Victim Media

Validin details UNC1069 fake-meeting lures against crypto and Web3 targets, browser-based audio/video capture, and Windows, macOS and Linux payload chains deploying apparent updated Cabbage RAT variants and, on macOS, a sample identified as NukeSped.

Apr 16, 2026
Threat Research · sysdig.com

Sysdig Reports marimo CVE-2026-39987 Exploitation and NKAbuse Deployment via Typosquatted Hugging Face Space

Sysdig researchers recorded exploitation of marimo CVE-2026-39987 and analyzed credential harvesting, database pivoting, and an NKAbuse variant delivered via a typosquatted Hugging Face Space. They recommend patching and behavioral hunting.

Apr 16, 2026
Threat Research · bleepingcomputer.com

AgingFly Malware Targets Ukrainian Governments and Hospitals to Steal Credentials

CERT-UA links the UAC-0247 cluster to Ukraine-focused attacks using AgingFly against local governments and hospitals. The C# malware targets browser and WhatsApp data through a phishing-led LNK-to-HTA chain and dynamically compiles C2-delivered handlers.

Apr 16, 2026
Threat Research · zscaler.com

Payouts King Ransomware Uses Evasion Techniques and RSA-AES Encryption

Zscaler researchers detail Payouts King ransomware, linking some activity to former BlackBasta affiliates and describing its social-engineering access methods, evasion, persistence, encryption, and impact on security processes.

Apr 16, 2026
Threat Research · bleepingcomputer.com

Signed adware abuses updates to deploy antivirus-killing payloads

Huntress found Dragon Boss Solutions adware silently deploying SYSTEM-level MSI and PowerShell payloads that disable antivirus. Researchers observed over 23,500 infected hosts seeking instructions and sinkholed the unregistered update domain.

Apr 15, 2026
Threat Research · securityonline.info

JUMPSEC Links Muddy Water to CastleRAT and ChainShell

JUMPSEC reports a direct operational link between Muddy Water infrastructure and TAG-150’s CastleRAT, describing ChainShell, HVNC browser-session access, smart-contract-based C2, and payloads compiled before Feb. 28.

Apr 15, 2026
Threat Research · malwarebytes.com

Phishing-as-a-Service Kit Uses Fake YouTube Copyright Notices to Steal Creator Logins

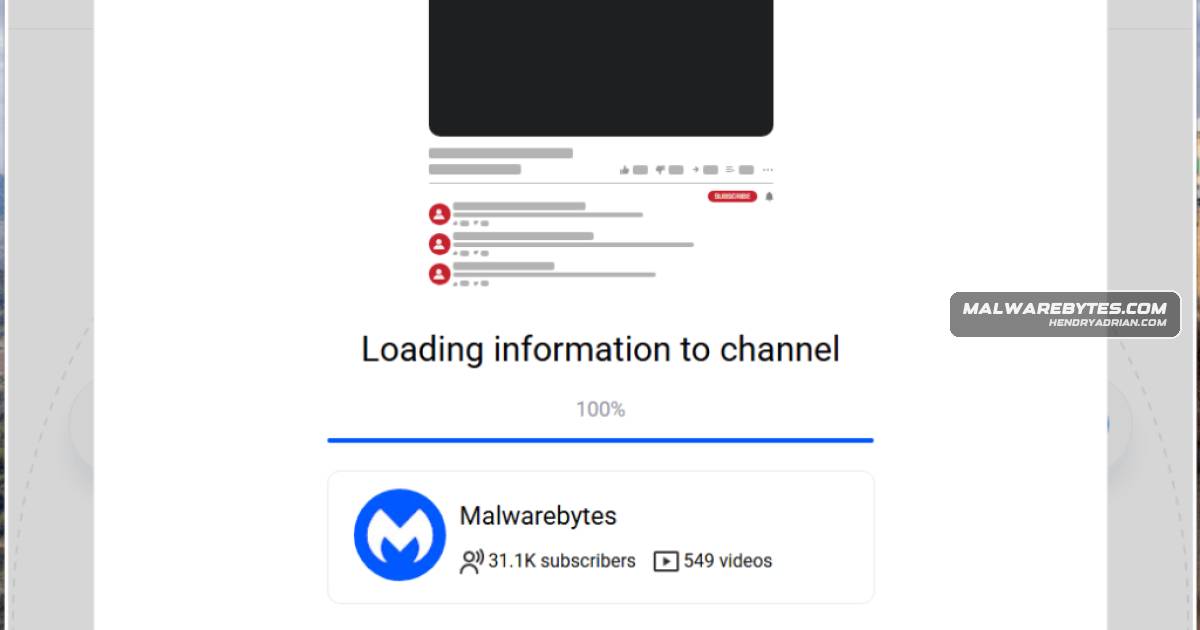
Malwarebytes analyzed a phishing-as-a-service kit targeting YouTube creators with personalized fake copyright notices and a Browser-in-the-Browser Google login overlay. It rotates domains, tracks affiliates, and exempts channels over 3 million subscribers.

Apr 15, 2026
Threat Research · thecyberexpress.com

Acronis Researchers Link JanaWare Ransomware to Customized Adwind RAT Campaign in Turkey

Acronis TRU researchers describe a JanaWare campaign active since at least 2020, linking it to a customized Adwind RAT. The reported operation targets Turkish users through phishing and uses geofencing, obfuscation, defense evasion, and AES encryption.

Apr 15, 2026
Threat Research · circleid.com

DNS and WHOIS Analysis Maps Infrastructure Linked to Keenadu Android Backdoor

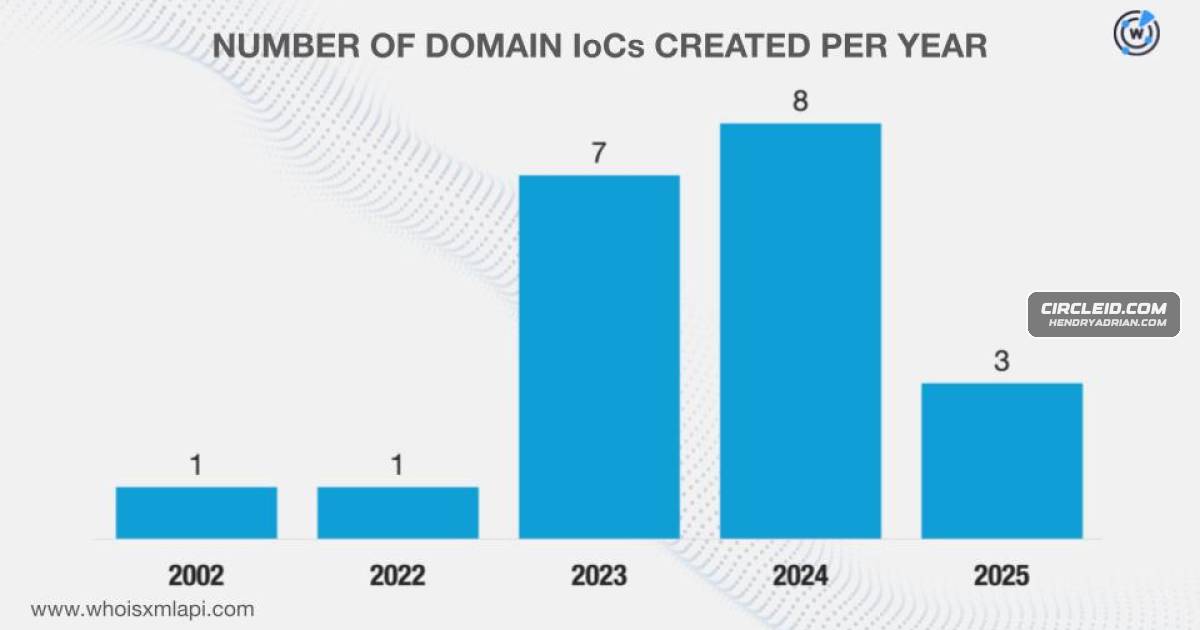
Researchers analyzed 29 DNS and WHOIS indicators linked to the Keenadu Android firmware backdoor, finding related domains and IPs. Traffic data showed 339 client IPs contacting three indicator domains and 61 potential victim IPs contacting two indicator IPs.

Apr 15, 2026
Threat Research · socket.dev

Researchers Link 108 Malicious Chrome Extensions to Shared C2 and Data Theft

Socket researchers identified 108 Chrome extensions (~20,000 installs) sharing C2 infrastructure. They detail Google identity harvesting, Telegram session theft, remote URL execution and defenses; the extensions were live when reported.

Apr 14, 2026
Threat Research · opensourcemalware.com

Stardrop NPM Campaign Uses More Than 200 Packages to Steal Cloud and AI Credentials

Researchers report more than 200 NPM packages posing as an AI coding agent. Their postinstall scripts deploy platform-specific infostealers that harvest credentials; packages removed from NPM may remain available through some mirrors.

Apr 14, 2026
Threat Research · reliaquest.com

Likely Former Black Basta Affiliates Target Executives With Automated Teams Help-Desk Scams

ReliaQuest says a likely former Black Basta affiliate campaign pairs email bombing with Teams help-desk impersonation and RMM tools to target executives, reporting rapid access and recommending verification, tool controls, and targeted training.

Apr 14, 2026
Threat Research · huntress.com

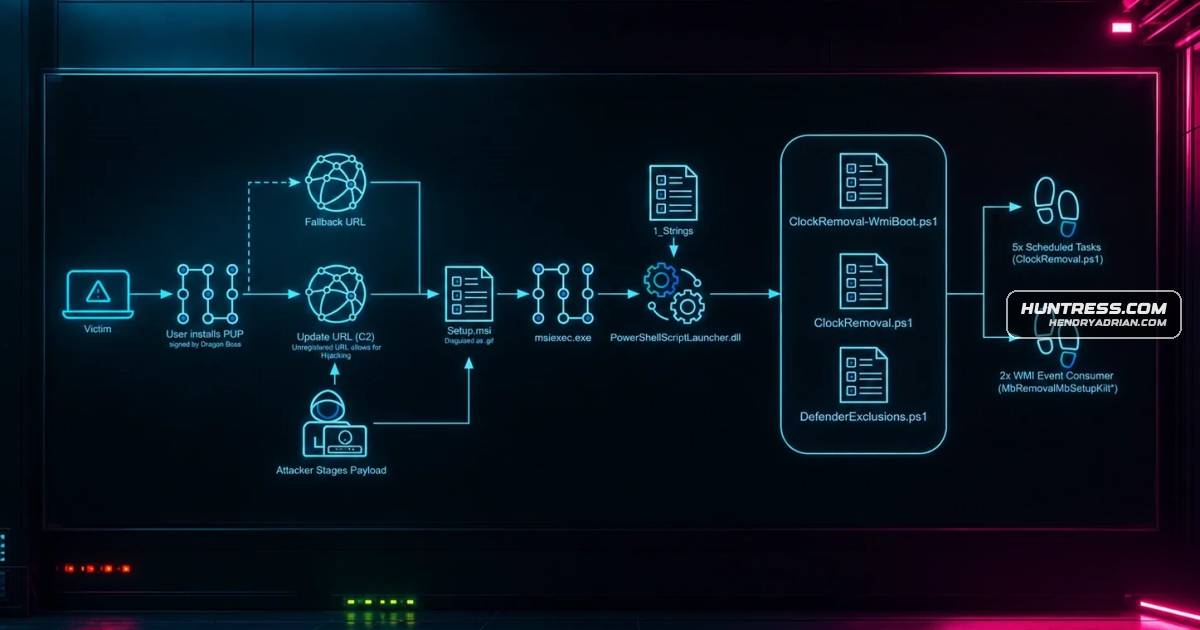
Dragon Boss PUP Disabled Antivirus and Exposed 23,565 Endpoints to Update Hijacking

Huntress analyzed Dragon Boss Solutions software that silently disabled antivirus and persisted on Windows systems. It found an unregistered update domain could let an attacker deliver arbitrary payloads; sinkholed requests came from 23,565 unique IPs in 24 hours.

Apr 14, 2026
Threat Research · thehackernews.com

Kaspersky Reports 14,739 JanelaRAT Attacks Recorded in Brazil in 2025

Kaspersky says JanelaRAT targets Latin American financial institutions using phishing, DLL side-loading and a malicious Chromium extension. Telemetry recorded 14,739 attacks in Brazil and 11,695 in Mexico in 2025; successful compromises are unknown.

Apr 13, 2026
Threat Research · proofpoint.com

Attackers Abuse Microsoft 365 Mailbox Rules for Stealthy Persistence and Email Fraud

Proofpoint describes how attackers use Microsoft 365 mailbox rules to hide messages, exfiltrate email, persist after password resets and hijack threads. It reports malicious rules in about 10% of compromised accounts in Q4 2025 and details ATOLS automation and defenses.

Apr 13, 2026
Threat Research · elastic.co

Elastic Details REF6598 Campaign Abusing Obsidian Plugins to Deliver PHANTOMPULSE RAT

Elastic Security Labs describes REF6598, a LinkedIn- and Telegram-led campaign that abused synced Obsidian plugins to deliver PHANTOMPULL and PHANTOMPULSE on Windows and an AppleScript dropper on macOS. Elastic says it blocked an observed attack early.

Apr 13, 2026
Threat Research · bleepingcomputer.com

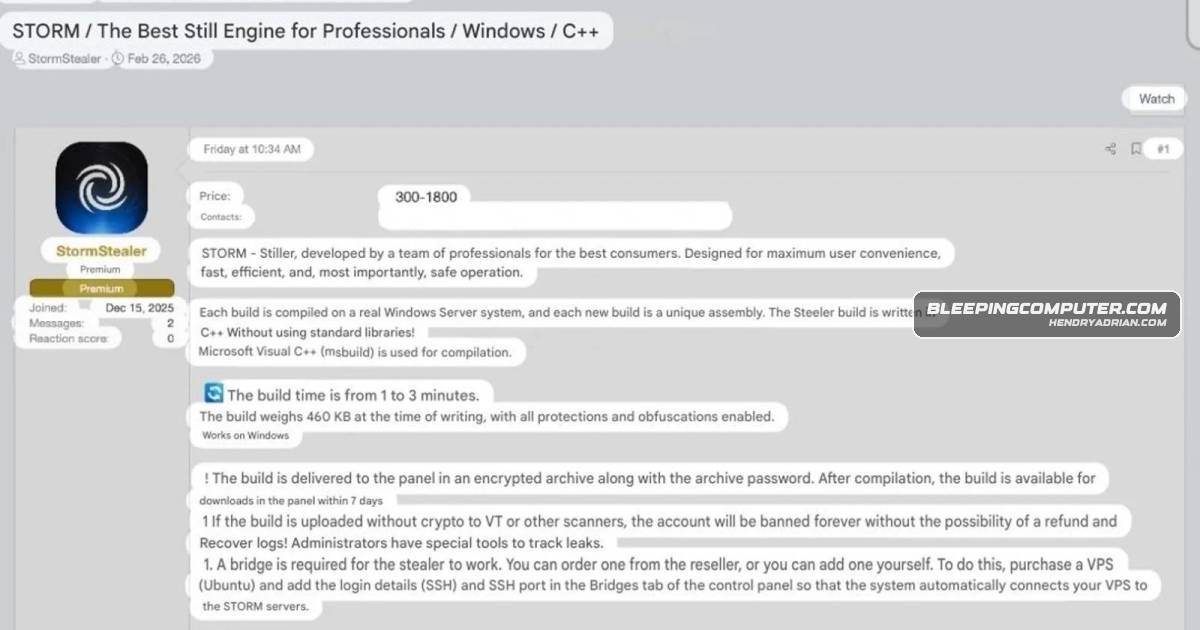
Storm Infostealer Decrypts Browser Data Server-Side to Hijack Sessions

Varonis describes Storm, a subscription infostealer that sends encrypted Chromium and Gecko browser data to operators for server-side decryption, then automates cookie-based session restoration. Its panel showed 1,715 logs, though real-victim status was uncertain.

Apr 13, 2026
Threat Research · cisecurity.org

MacSync Stealer Uses ClickFix to Target U.S. SLTT macOS Users

CIS details a MacSync Stealer campaign targeting U.S. SLTT macOS users through SEO-poisoned fake CAPTCHAs. The malware can steal credentials, system data and crypto assets, and trojanize Ledger apps to capture seed phrases.

Apr 13, 2026
Threat Research · securelist.com

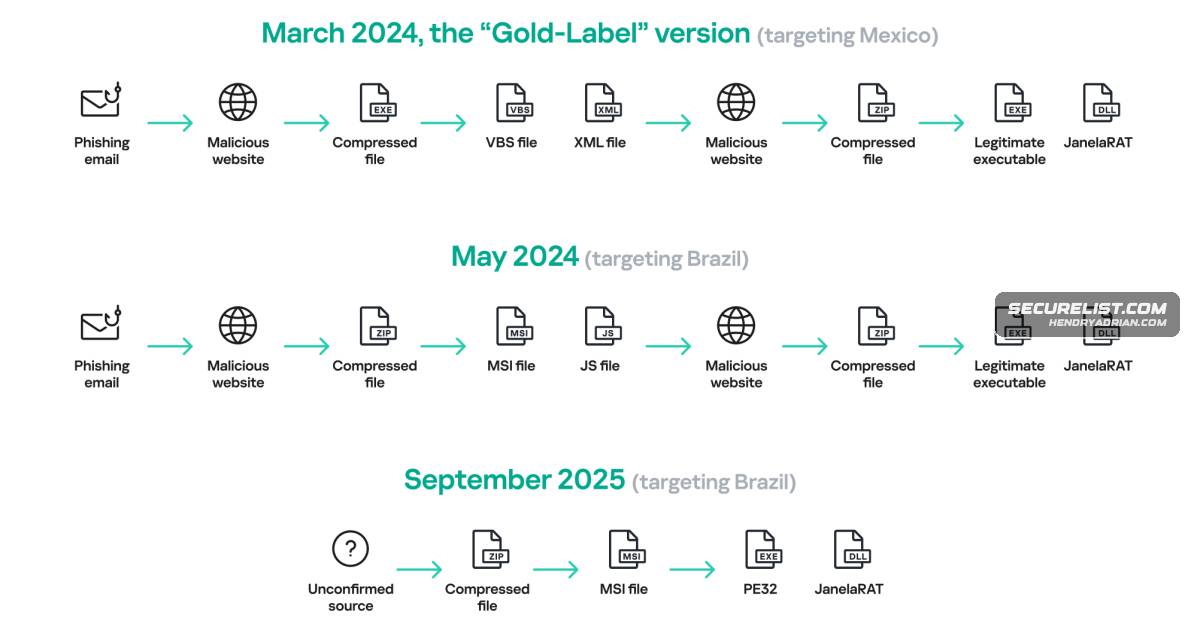
JanelaRAT Evolves Its Delivery Chain and Enables Live Banking-Session Hijacking

The analysis details JanelaRAT’s evolving infection chain and its use of overlays, input injection and remote control to hijack banking sessions. 2025 telemetry recorded thousands of detections in Brazil and Mexico.

Apr 13, 2026
PreviousPage 70 of 104 Next
© 2026 cyber.hendryadrian.com