cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2487 articles

Threat Research · sysdig.com

Sysdig Observes LMDeploy SSRF Exploitation Attempt 12 Hours After Advisory

Sysdig says its honeypot saw an LMDeploy CVE-2026-33626 SSRF exploitation attempt 12 hours 31 minutes after the GitHub advisory. Requests targeted cloud metadata and internal services; the article recommends upgrading to v0.12.3 and restricting egress.
Apr 23, 2026
Threat Research · stepsecurity.io

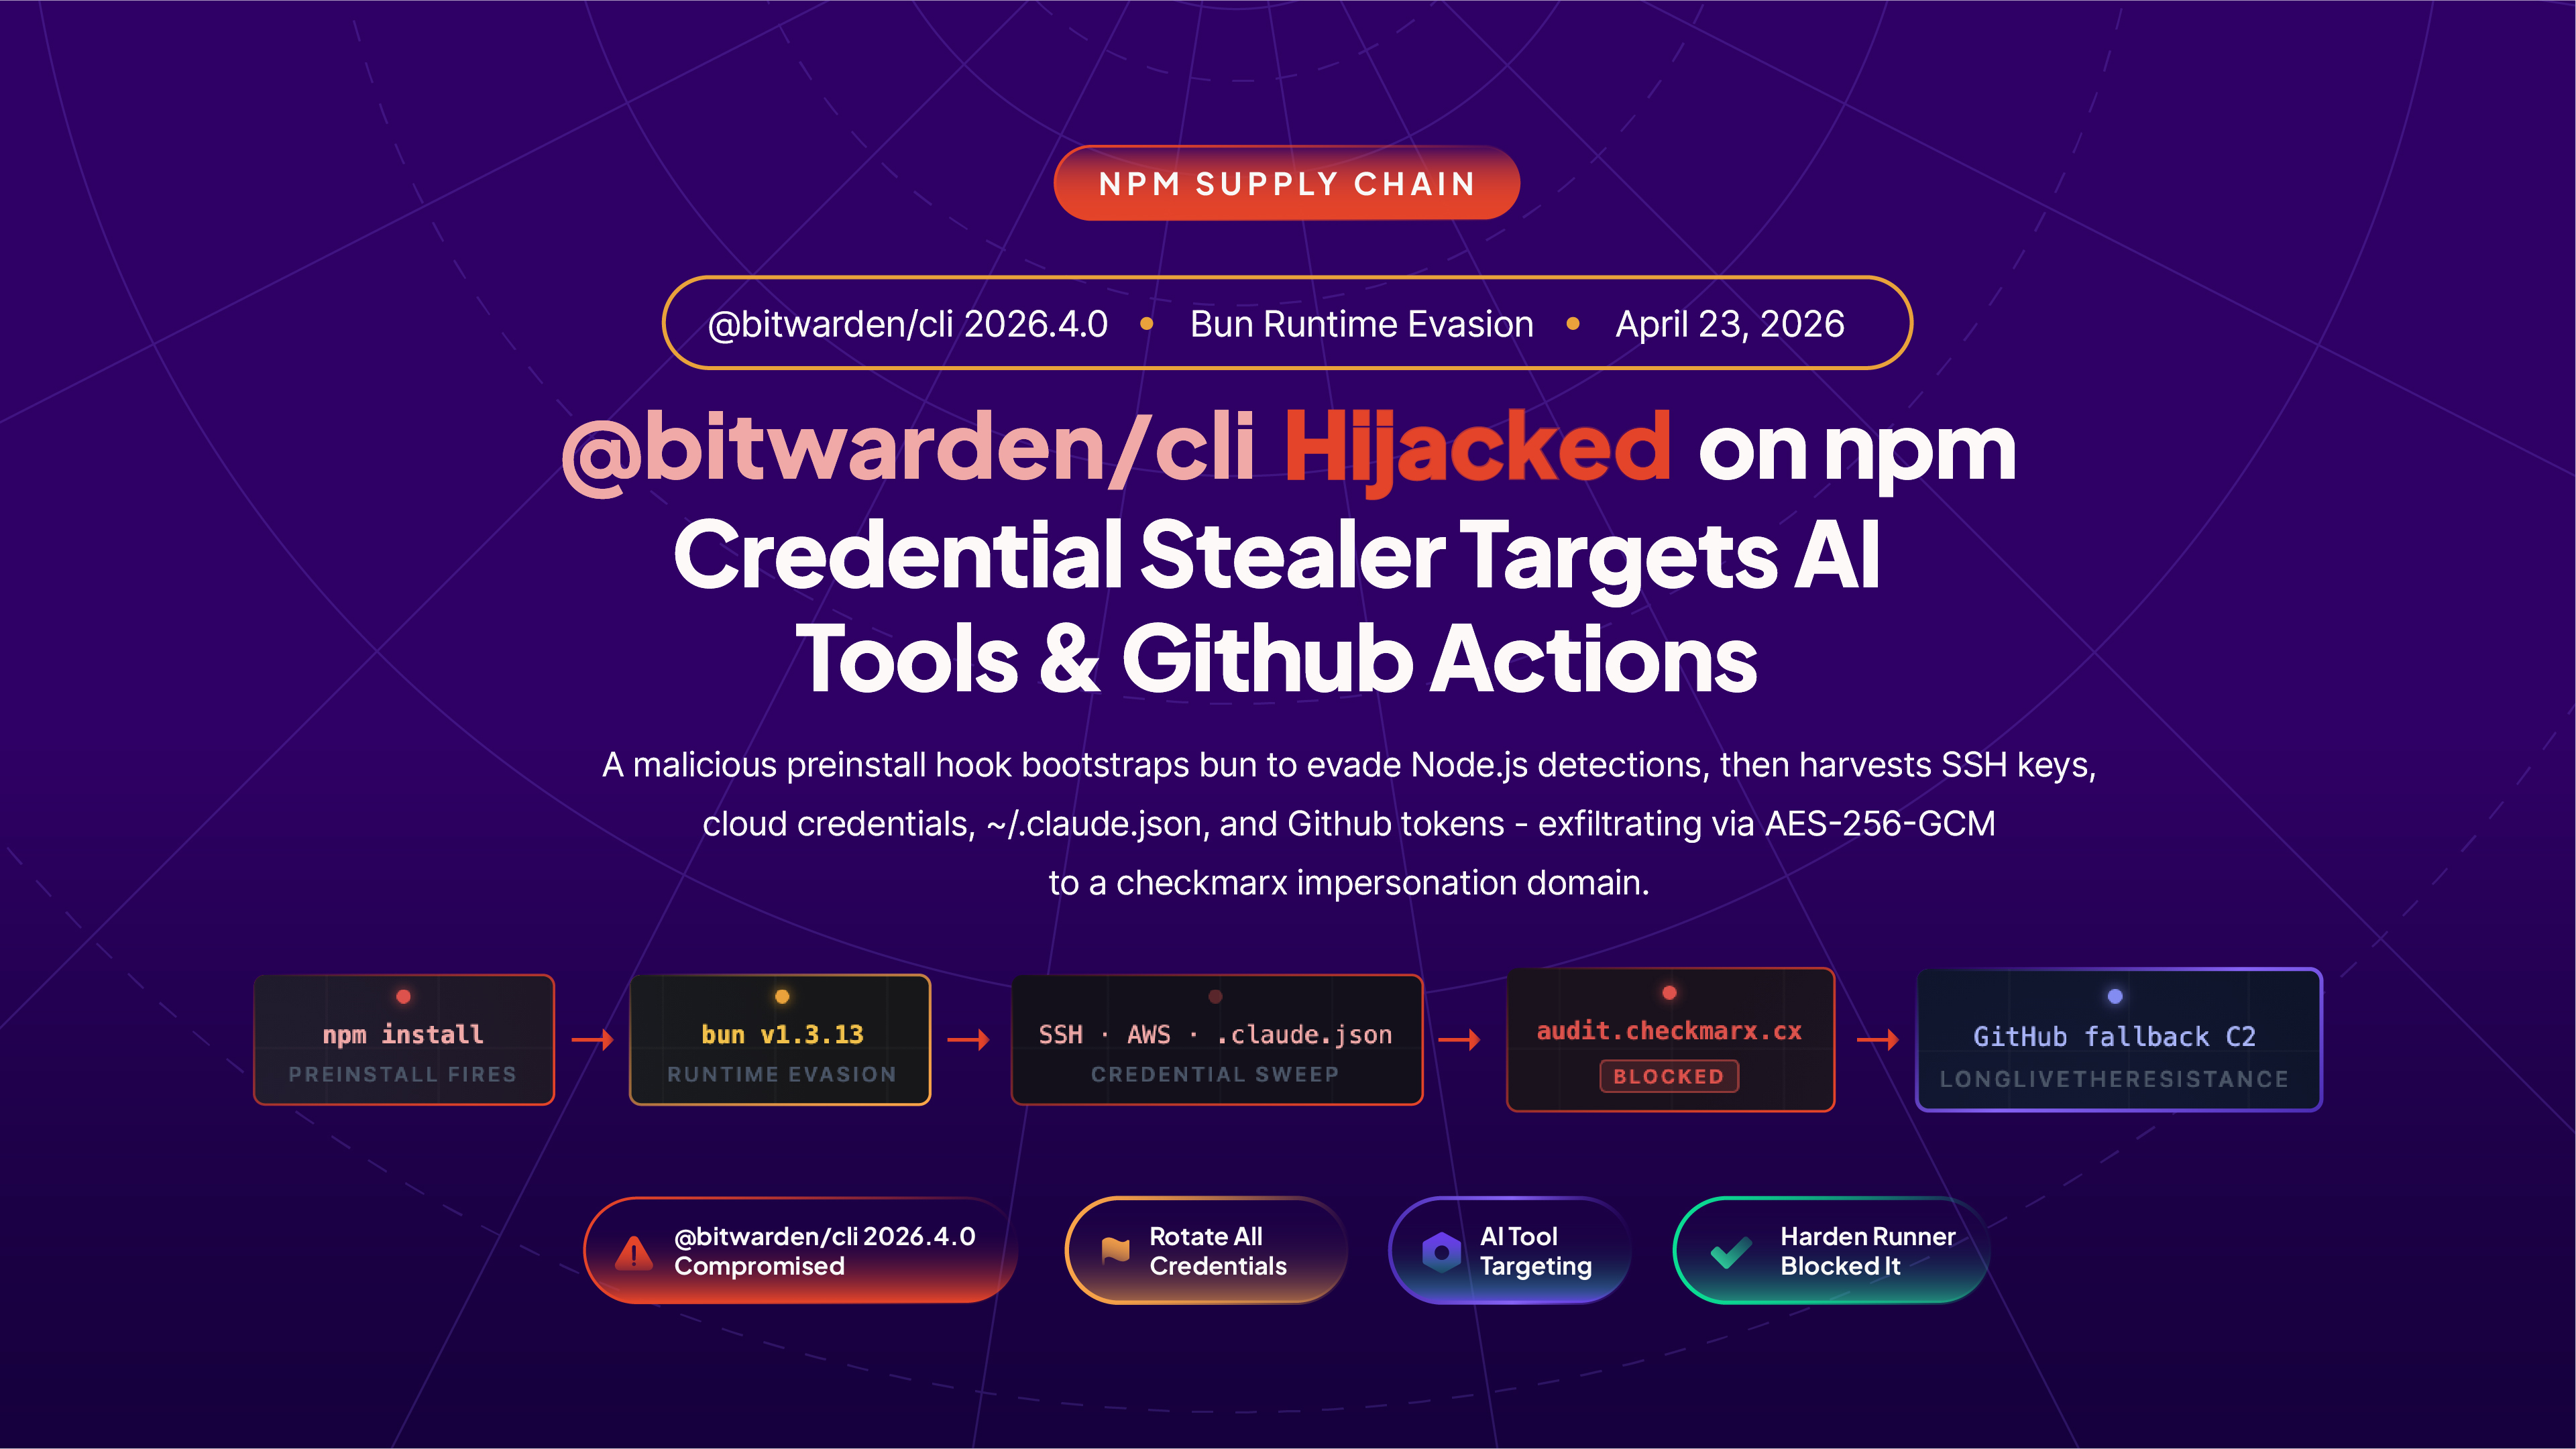
Malicious Bitwarden CLI npm Release Targets Developer Credentials and GitHub Actions

StepSecurity reports that attackers used a compromised Bitwarden engineer account to publish a malicious @bitwarden/[email protected] release, whose Bun-staged payload targets developer credentials, AI-tool configs and GitHub Actions secrets.

Apr 23, 2026
Threat Research · dti.domaintools.com

DomainTools Links Homeland Justice, Karma and Handala to an MOIS-Aligned Cyber Campaign

DomainTools assesses Homeland Justice, Karma and Handala as personas in an MOIS-aligned campaign that has evolved from destructive intrusions into espionage, surveillance, hack-and-leak operations and influence activity.

Apr 22, 2026
Threat Research · bleepingcomputer.com

Rapid7 Finds Kyber Ransomware Uses Post-Quantum Key Protection Only in Windows Variant

Rapid7 analyzed Kyber ransomware variants found on one network in March 2026. The ESXi variant uses ChaCha8 and RSA-4096 despite Kyber1024 claims; the Windows variant uses Kyber1024 and X25519 to protect keys, with AES-CTR for files.

Apr 22, 2026
Threat Research · malwarebytes.com

Needle Stealer Campaign Uses Fake TradingClaw Site to Target Browsers

Researchers detail a campaign distributing the Golang infostealer Needle through a fake TradingClaw site. The malware uses DLL hijacking and process hollowing, steals sensitive data, and can install browser extensions that monitor and manipulate browsing.

Apr 22, 2026
Threat Research · elastic.co

Elastic Research Shows Custom Obfuscation Can Stall LLM Reverse Engineering

Elastic researchers benchmarked Claude Opus 4.6 on Tigress-obfuscated binaries and built three custom obfuscators that exploited static-analysis limits, sharply increasing analysis time and cost and preventing password recovery in some tests.

Apr 22, 2026
Threat Research · thehackernews.com

Harvester Expands GoGra Backdoor to Linux, Uses Outlook for C2

Symantec and Carbon Black report that Harvester’s Linux GoGra backdoor uses Microsoft Graph and an Outlook folder for C2, executing email-delivered commands. VirusTotal artifacts from India and Afghanistan suggest, but do not confirm, South Asian targeting.

Apr 22, 2026
Threat Research · thedfirreport.com

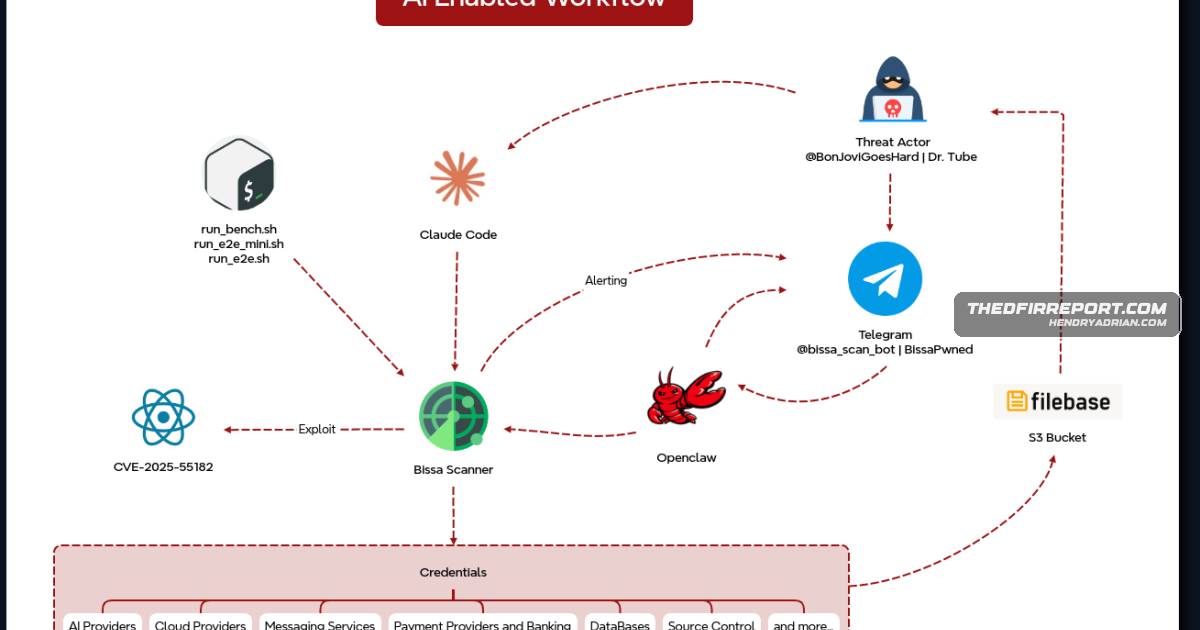
Bissa Scanner Used AI-Assisted Workflows to Exploit 900+ Targets and Harvest Credentials

DFIR Report researchers found an exposed server documenting Bissa Scanner’s large-scale React2Shell exploitation, credential harvesting, and victim-data collection, with Claude Code and OpenClaw supporting the operator’s workflow.

Apr 22, 2026
Threat Research · unit42.paloaltonetworks.com

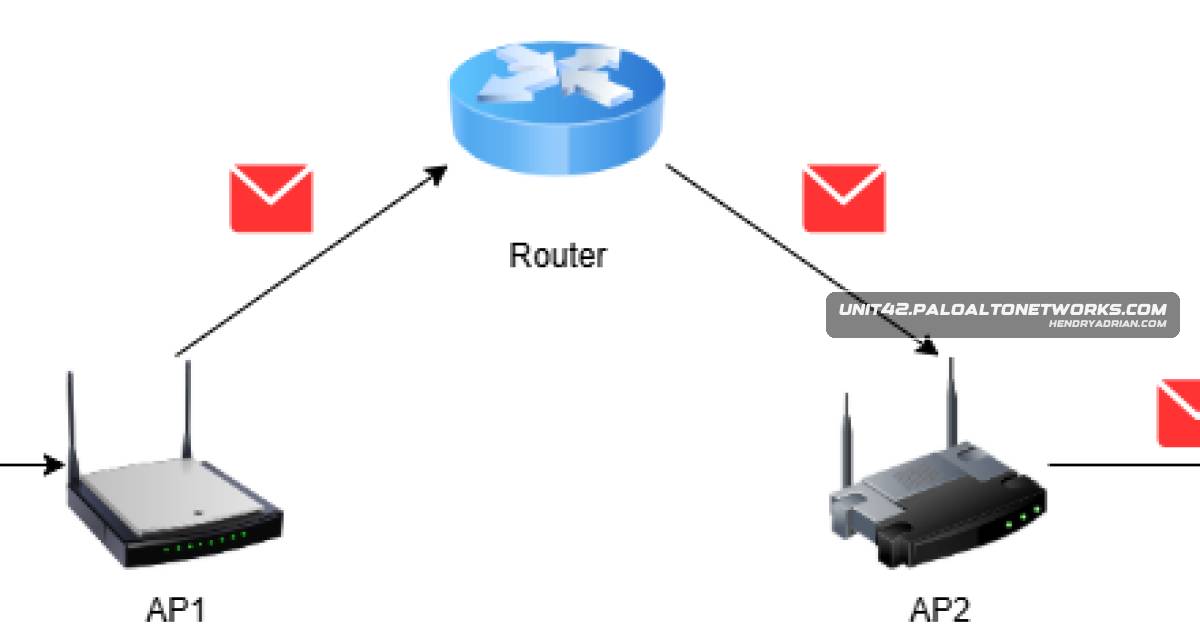
AirSnitch Research Shows How Wi-Fi Isolation Can Be Bypassed

Unit 42 describes AirSnitch techniques that exploit interactions between Wi-Fi encryption, switching and routing to bypass client isolation, intercept or inject traffic, and enable cross-AP attacks. The article also outlines enterprise mitigations.

Apr 22, 2026
Threat Research · securityweek.com

Lotus Wiper Used Against Venezuelan Energy Organization, Kaspersky Says

Kaspersky describes Lotus Wiper, a destructive malware used against a Venezuelan energy organization. Two batch scripts prepare the system before the wiper deletes recovery mechanisms, overwrites physical drives and removes files. Attribution is unknown.

Apr 22, 2026
Threat Research · welivesecurity.com

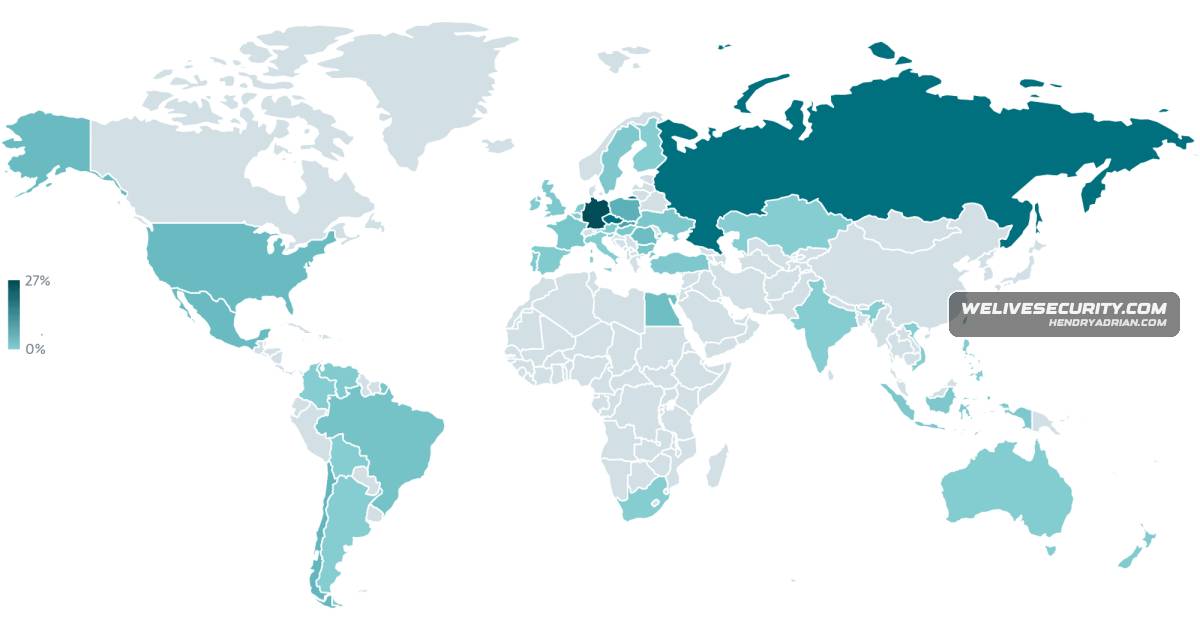
ESET Finds NGate Variant Trojanizing HandyPay to Steal Payment Card PINs

ESET researchers describe an NGate campaign active since November 2025 that trojanizes Android HandyPay to relay payment-card NFC data and steal PINs, distributed through fake Brazilian lottery and Google Play pages.

Apr 22, 2026
Threat Research · forcepoint.com

Forcepoint X-Labs Finds 10 Indirect Prompt-Injection Payloads on Live Websites

Forcepoint X-Labs describes 10 reported indirect prompt-injection payloads on live websites, detailing concealment and spoofing techniques aimed at data theft, fraud, destructive actions, and AI denial of service.

Apr 22, 2026
Threat Research · bleepingcomputer.com

Linux GoGra Backdoor Uses Microsoft Graph for Outlook-Based Command and Control

Symantec researchers report that Linux GoGra uses hardcoded Azure AD credentials and Outlook via Microsoft Graph for command-and-control, with systemd/XDG persistence and encrypted command execution; code similarities link it to Harvester.

Apr 22, 2026
Threat Research · acronis.com

Mustang Panda-Linked LOTUSLITE v1.1 Targets Indian Banks and Korea Policy Circles

Acronis researchers detail LOTUSLITE v1.1 campaigns targeting India’s banking sector and South Korean/U.S. policy circles, describing DLL sideloading, CHM/JavaScript loaders and evasion changes. Attribution to Mustang Panda is assessed with moderate confidence.

Apr 22, 2026
Threat Research · socket.dev

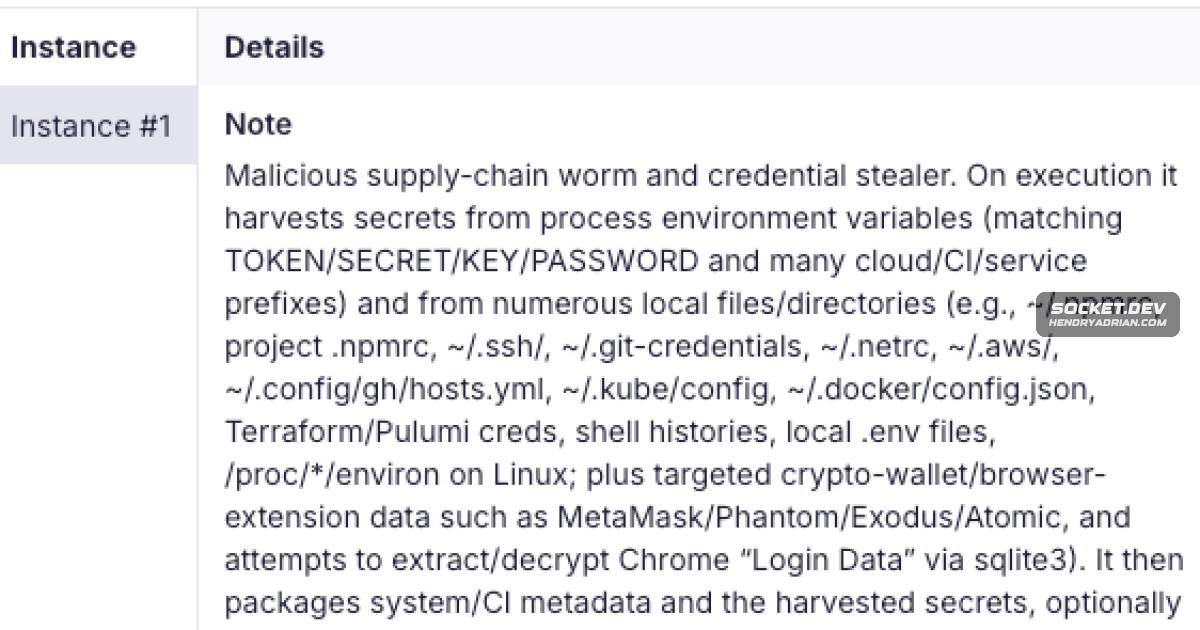
Socket Finds CanisterWorm-Style Malware in Namastex-Linked npm Packages

Socket reports malicious npm packages linked to Namastex’s Automagik ecosystem that steal developer secrets, browser and wallet data, and attempt propagation across npm and PyPI. The upstream cause remains unresolved.

Apr 22, 2026
Threat Research · stepsecurity.io

Malicious xinference PyPI Releases Steal Credentials on Import

StepSecurity says xinference 2.6.0–2.6.2 on PyPI carried an import-triggered, two-stage credential stealer targeting cloud, SSH, Kubernetes and other secrets. Testing blocked exfiltration; the releases were yanked.

Apr 22, 2026
Threat Research · huntress.com

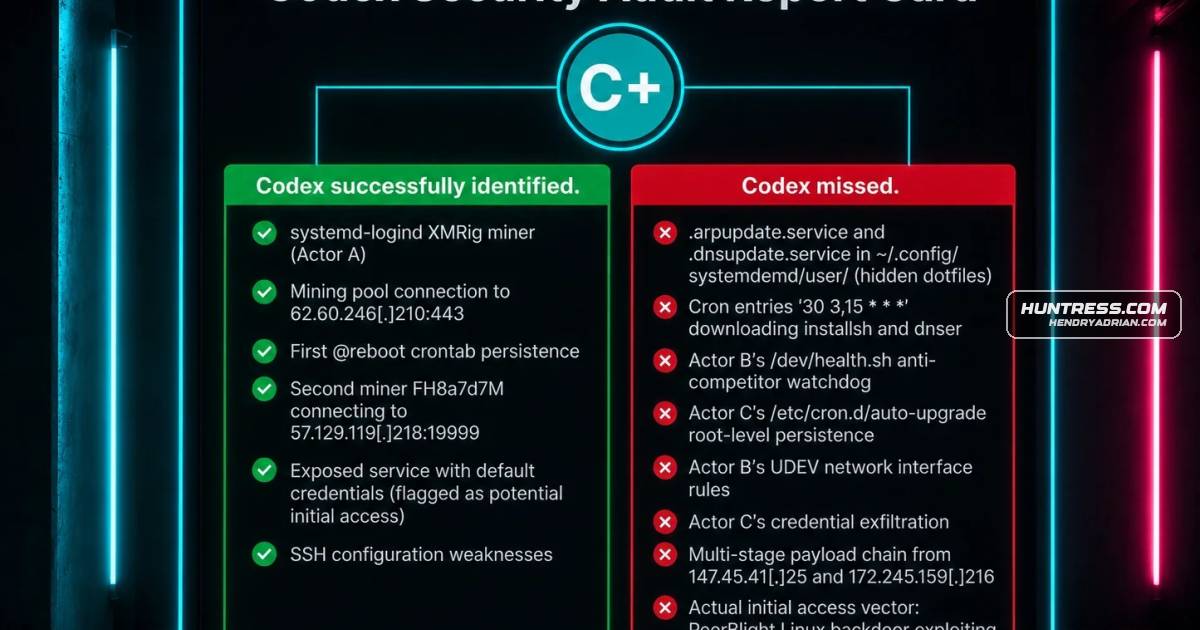
Huntress Details Linux Intrusion Involving Multiple Threat Actors and Codex

Huntress analysts traced multiple Linux threat actors deploying miners, persistence, and credential theft, with data exfiltration and log wiping. Activity later returned via a React2Shell-vulnerable app; investigators highlight limits of AI-only response.

Apr 22, 2026
Threat Research · zscaler.com

Tropic Trooper Uses AdaptixC2 and GitHub C2 to Establish VS Code Tunnel Access

ThreatLabz attributes a campaign targeting Chinese-speaking people in Taiwan, South Korea, and Japan to Tropic Trooper. A trojanized SumatraPDF delivered AdaptixC2 through a custom GitHub listener, with VS Code tunnels used for remote access.

Apr 22, 2026
Threat Research · team-cymru.com

Network Analysis Links Infrastructure to Suspected DPRK Fake IT Workers

A 30-day analysis of network activity around two IPs linked to luckyguys[.]site found VPN use, residential connections, and activity associated with freelance work. Traffic fell sharply after public exposure, consistent with infrastructure abandonment.

Apr 22, 2026
Threat Research · malwarebytes.com

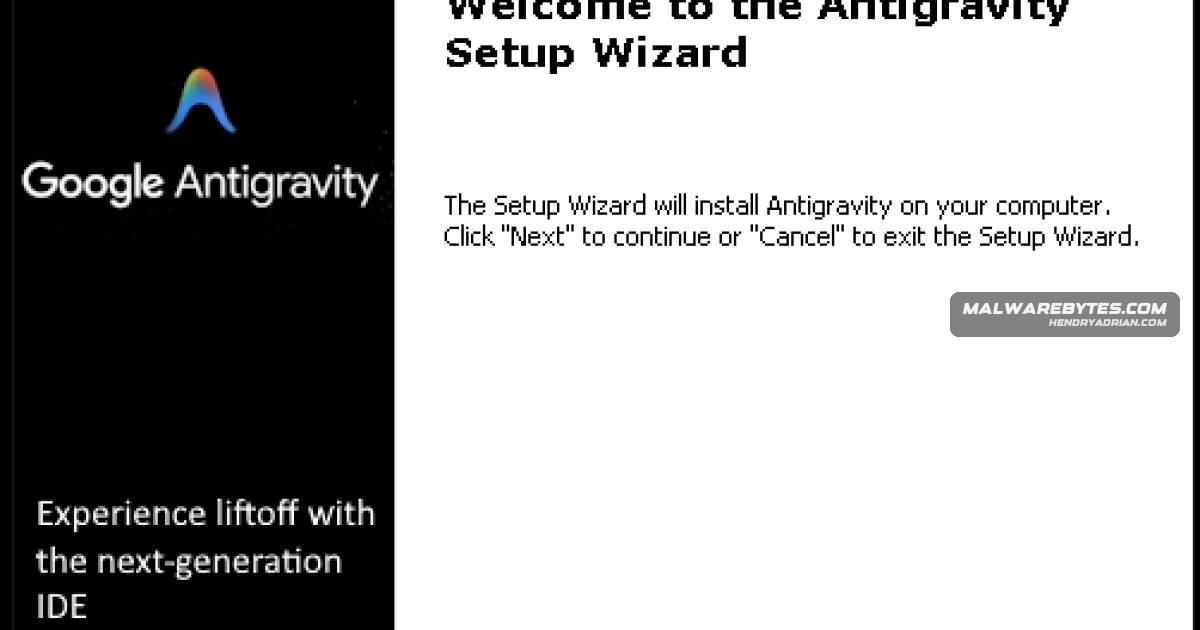
Trojanized Google Antigravity Installer Can Deploy Credential-Stealing Malware

A trojanized Antigravity installer from a lookalike site runs a PowerShell downloader that checks in to opus-dsn[.]com. Researchers found the operator can selectively deploy a .NET stealer targeting credentials, cookies and tokens.

Apr 21, 2026
Threat Research · bleepingcomputer.com

Lotus Wiper Used in Attacks on Venezuelan Energy and Utilities Organizations

Kaspersky analyzed Lotus, a previously undocumented wiper reportedly used against Venezuelan energy and utilities organizations. Preparatory scripts disable defenses and hinder recovery before Lotus overwrites disks and removes recovery options.

Apr 21, 2026
Threat Research · helpnetsecurity.com

Infrawatch Links ProxySmart to SIM Farms Across 17 Countries

Infrawatch linked many SIM-farm deployments across 17 countries to ProxySmart, which manages mobile devices, rotates IPs and spoofs OS fingerprints. The firm assesses the networks are likely facilitating large-scale fraud.

Apr 21, 2026
Threat Research · levelblue.com

LevelBlue Details Phishing Campaign Abusing Microsoft OAuth Device Code Flow

LevelBlue details a phishing campaign using a fake Adobe site, Mandrill redirects and Microsoft OAuth Device Code Flow to trick users into authorizing tokens, potentially enabling persistent access. It shares KQL detections and Conditional Access mitigations.

Apr 21, 2026
Threat Research · stepsecurity.io

Malicious pgserve npm Releases Harvest Credentials and Spread to Other Packages

StepSecurity reports that pgserve versions 1.1.11–1.1.13 added a credential-stealing postinstall script with npm and PyPI propagation. In a controlled run, it observed encrypted data exfiltration to an ICP canister; 1.1.10 was the last legitimate release.

Apr 21, 2026
PreviousPage 68 of 104 Next
© 2026 cyber.hendryadrian.com