cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2486 articles

Threat Research · cyble.com

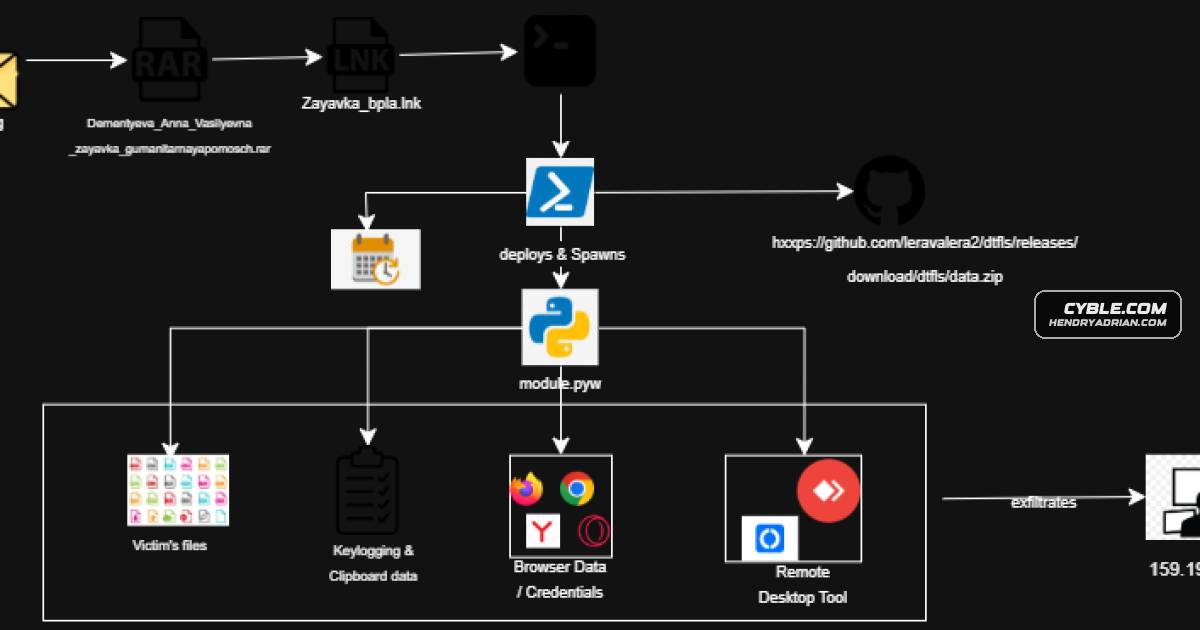
Operation HumanitarianBait Uses Aid-Themed Lures to Deploy a Python Infostealer

Cyble describes a campaign using Russian-language humanitarian-aid lures and malicious LNK files to deploy a persistent Python implant. Analysis found credential and data theft, surveillance, and covert remote-access capabilities; attribution remains inconclusive.
May 10, 2026
Threat Research · seqrite.com

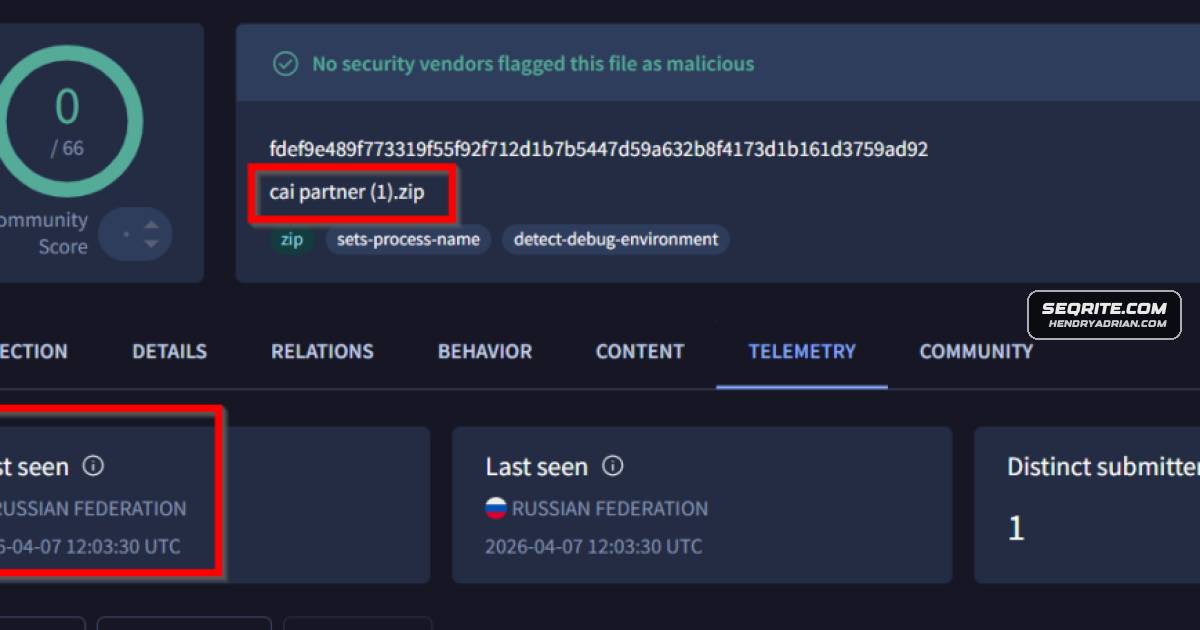
Operation Silent Rotor Uses Rust Malware to Target Eurasian Aviation Sector

SEQRITE Labs describes a spear-phishing campaign targeting Eurasian aviation professionals with Russian-language lures. Its Rust malware profiles systems, sends data to cdn[.]kleymarket[.]ru, and downloads a second-stage payload; no actor attribution is established.

May 9, 2026
Threat Research · bleepingcomputer.com

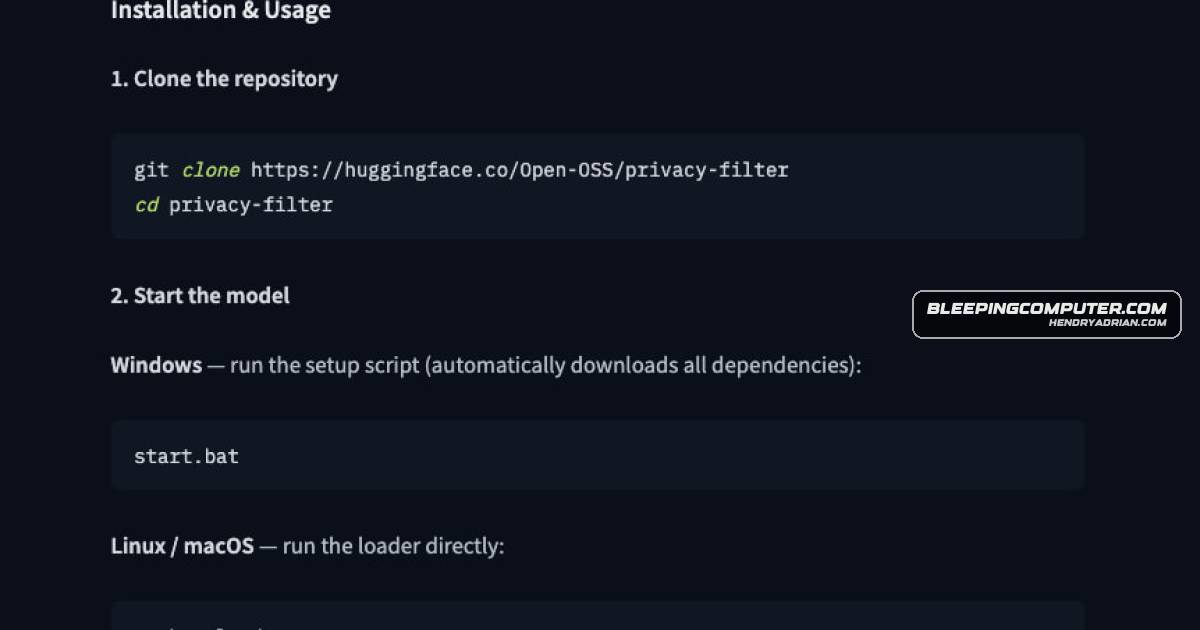
Fake Hugging Face Repository Used to Deliver Sefirah Infostealer

HiddenLayer found a typosquatted Hugging Face repository impersonating OpenAI’s Privacy Filter. Its loader deployed the Sefirah infostealer against Windows users; the repo reached 244,000 downloads, a count researchers said may have been inflated.

May 9, 2026
Threat Research · cyfirma.com

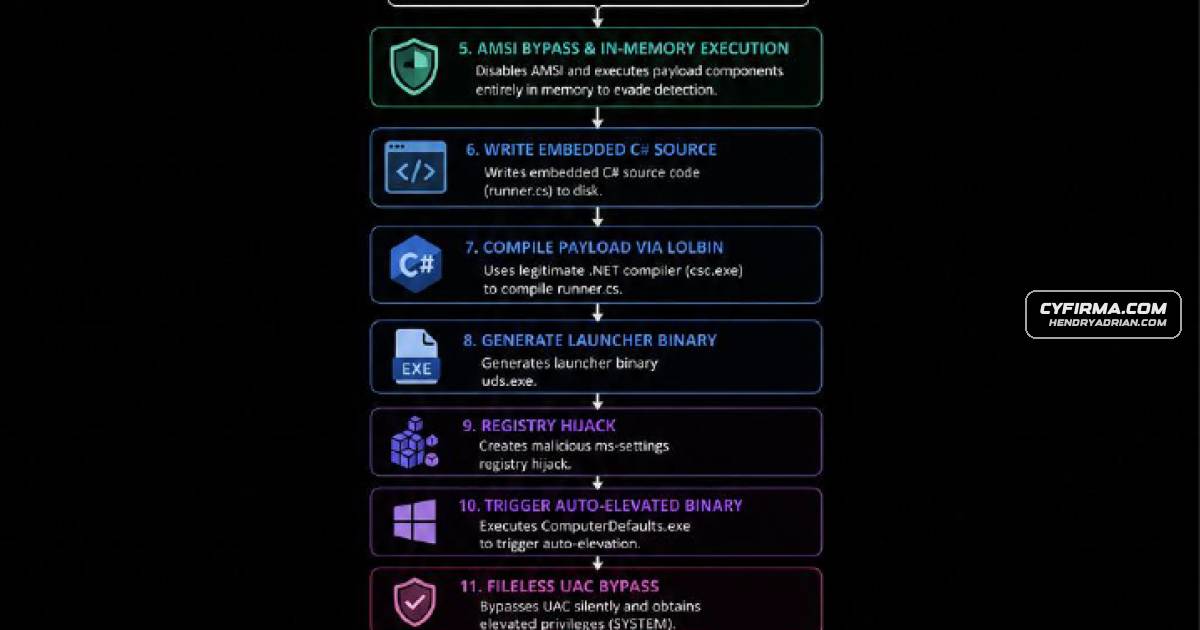
Operation SilentCanvas Uses JPEG-Disguised PowerShell to Deploy Trojanized ScreenConnect

CYFIRMA details Operation SilentCanvas, a multi-stage intrusion using a PowerShell payload disguised as a JPEG, on-host .NET compilation, a fileless UAC bypass and trojanized ScreenConnect for persistent encrypted remote access.

May 9, 2026
Threat Research · feeds.fortinet.com

FortiGuard Details Nexcorium IoT Botnet Campaign Exploiting TBK DVR Flaw

FortiGuard Labs analyzes a campaign exploiting CVE-2024-3721 in TBK DVR devices to install Nexcorium, a Mirai variant with multiple persistence methods, brute-force capabilities and DDoS functions. A link to “Nexus Team” is suspected.

May 9, 2026
Threat Research · welivesecurity.com

ESET Uncovers 28 CallPhantom Android Apps That Faked Call Logs to Charge Users

ESET identified 28 CallPhantom Android apps with more than 7.3 million downloads. The apps fabricated call and message histories, charged users for fake results, and were removed from Google Play after ESET reported them.

May 9, 2026
Threat Research · levelblue.com

LevelBlue Shows How Backdoored Electron Apps Can Evade Defenses

LevelBlue GSOC demonstrates how modifying Electron app files can deliver a Meterpreter payload for persistence or hollow Microsoft Teams to run Loki C2 despite WDAC. The report details detection indicators and defensive measures.

May 8, 2026
Threat Research · thehackernews.com

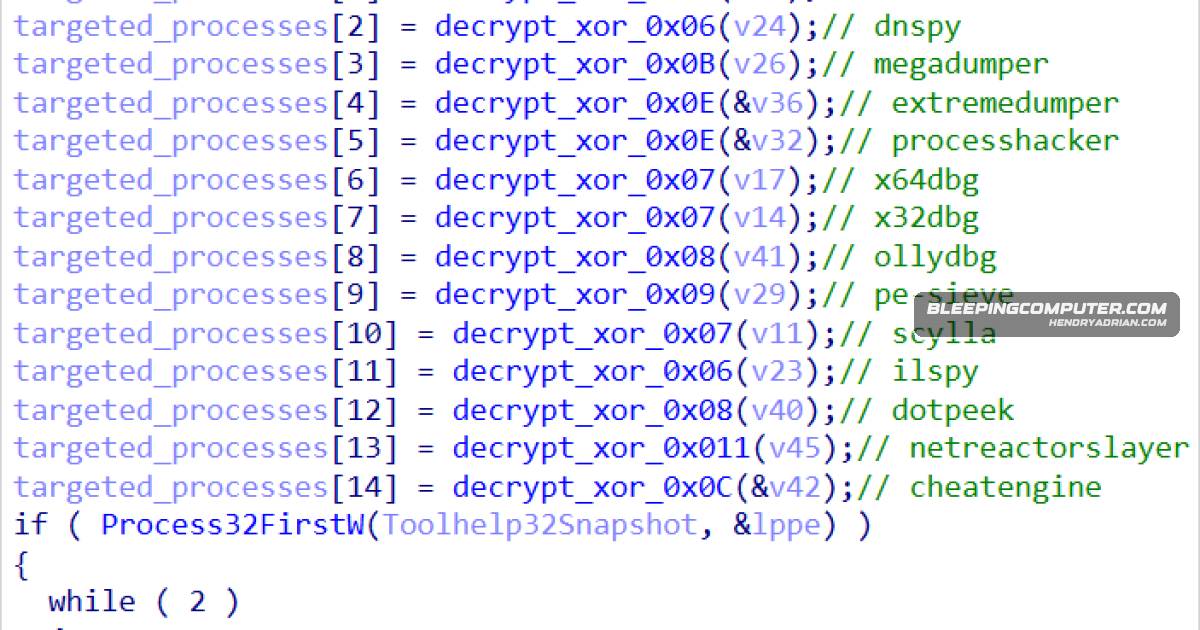
TCLBANKER Targets 59 Financial Platforms and Spreads via WhatsApp and Outlook

Elastic Security Labs describes TCLBANKER, a Brazilian banking trojan targeting 59 financial platforms. It uses anti-analysis checks, browser monitoring and credential overlays, and spreads through hijacked WhatsApp sessions and Outlook accounts.

May 8, 2026
Threat Research · seqrite.com

Seqrite Details Operation GriefLure Spear-Phishing Campaign in Vietnam and the Philippines

Seqrite Labs describes Operation GriefLure, a spear-phishing campaign targeting Viettel-linked personnel in Vietnam and St. Luke’s Medical Center in the Philippines, and analyzes its LNK/ftp.exe loader, DLL sideloading, RAT capabilities and C2.

May 8, 2026
Threat Research · sentinelone.com

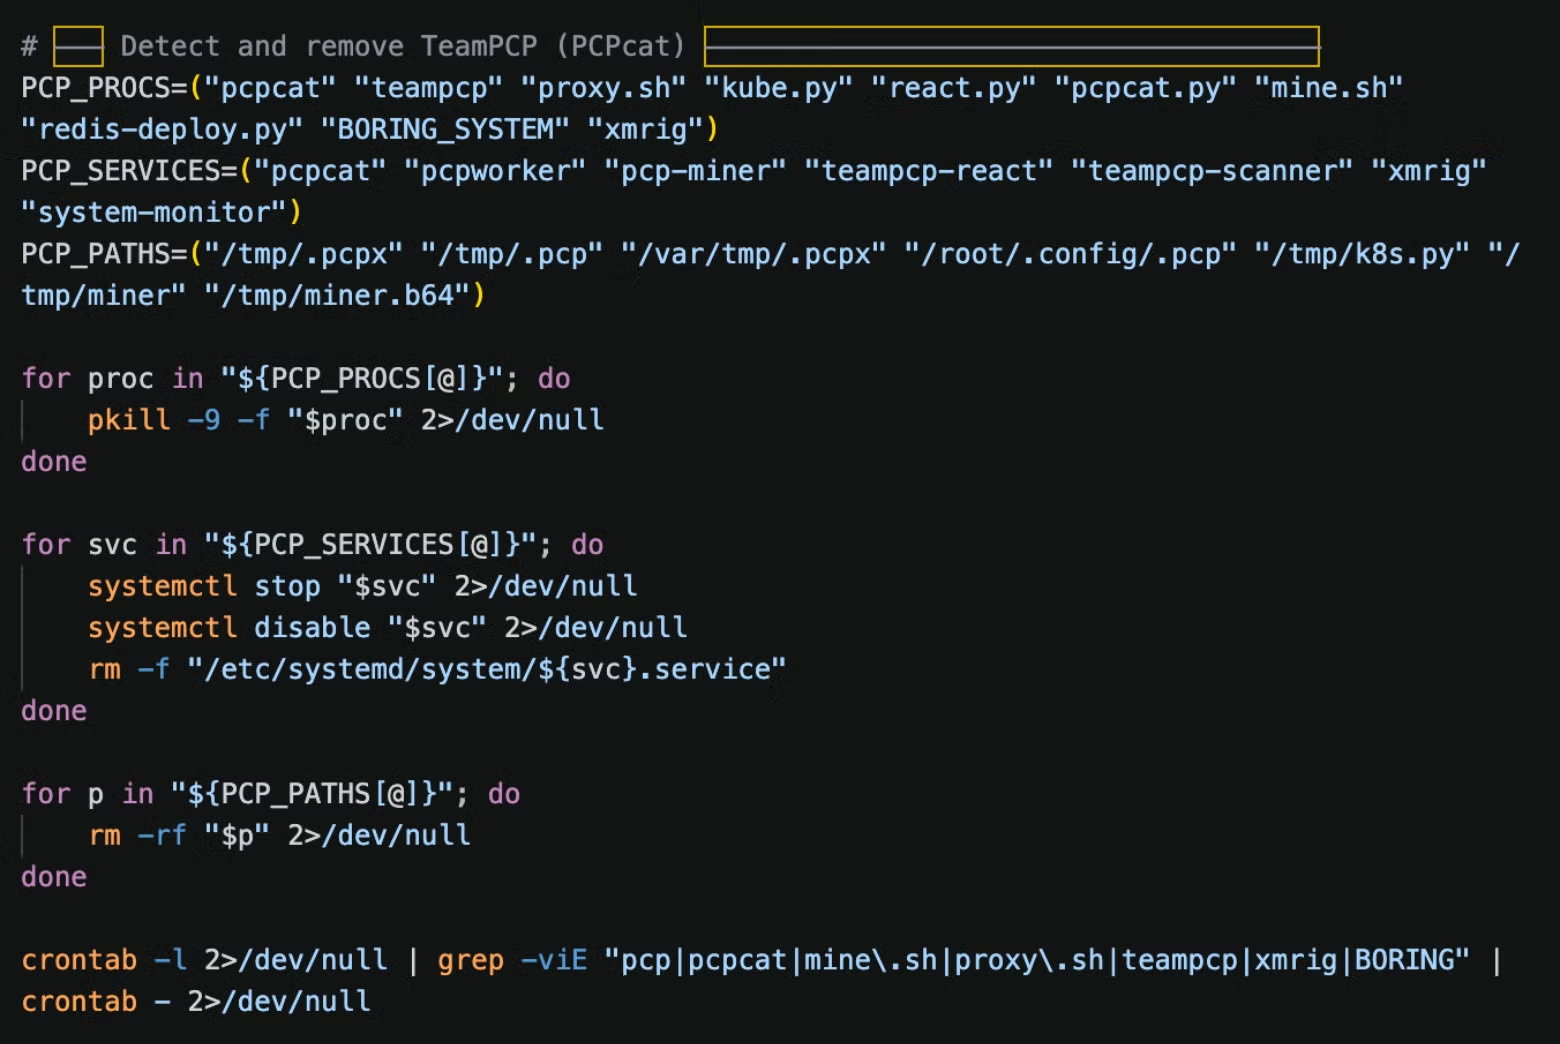
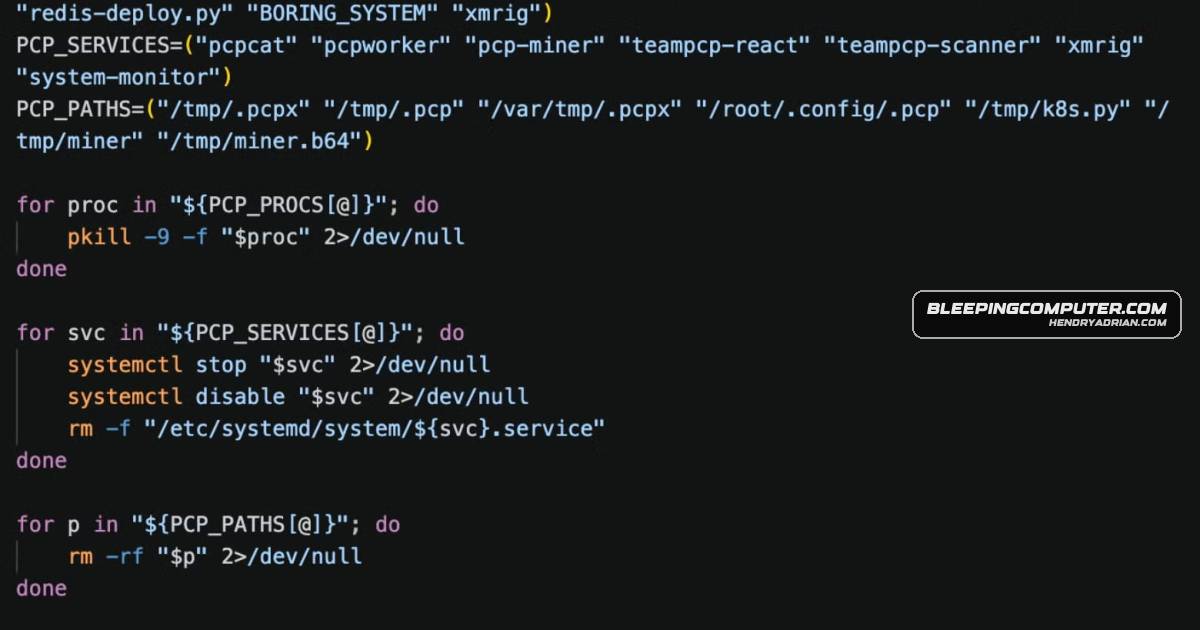
PCPJack Cloud Worm Evicts TeamPCP Tools and Steals Credentials

SentinelLABS analyzed PCPJack, a modular worm that removes TeamPCP artifacts, harvests cloud and developer credentials, and propagates through exposed services. A separate toolset deploys Sliver beacons and steals credentials from more than 30 services.

May 8, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details Limited Exploitation of PAN-OS CVE-2026-0300

Unit 42 reports limited exploitation of PAN-OS CVE-2026-0300, an unauthenticated root-code-execution flaw, by likely state-sponsored cluster CL-STA-1132. Observed activity included shellcode injection, tunneling tools, Active Directory enumeration and log cleanup.

May 8, 2026
Threat Research · cyfirma.com

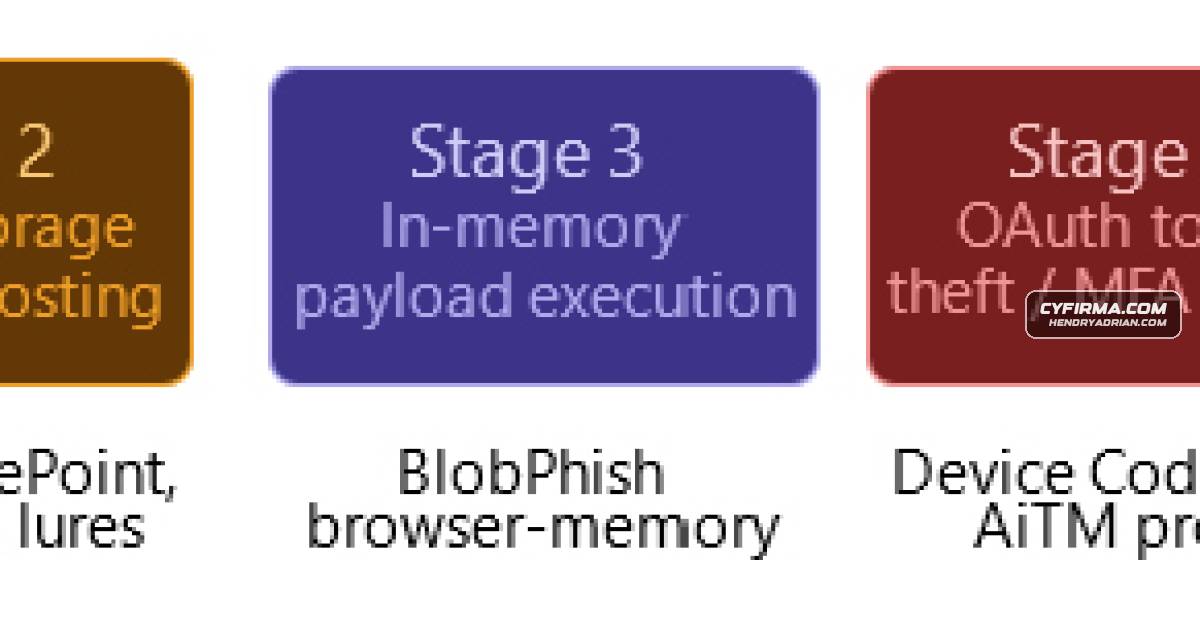
CYFIRMA Details Phishing Campaigns Abusing Trusted Cloud Infrastructure

CYFIRMA describes Trusted Infrastructure Phishing campaigns abusing legitimate cloud services for delivery, hosting, token theft and persistence, including browser-memory phishing and OAuth device-code abuse, and recommends identity-focused monitoring and stronger than

May 8, 2026
Threat Research · securityweek.com

PCPJack Worm Removes TeamPCP Artifacts and Steals Credentials

SentinelOne reports that PCPJack removes artifacts from TeamPCP infections, steals credentials across cloud and other services, and attempts to spread through vulnerable web applications and exposed deployments.

May 8, 2026
Threat Research · levelblue.com

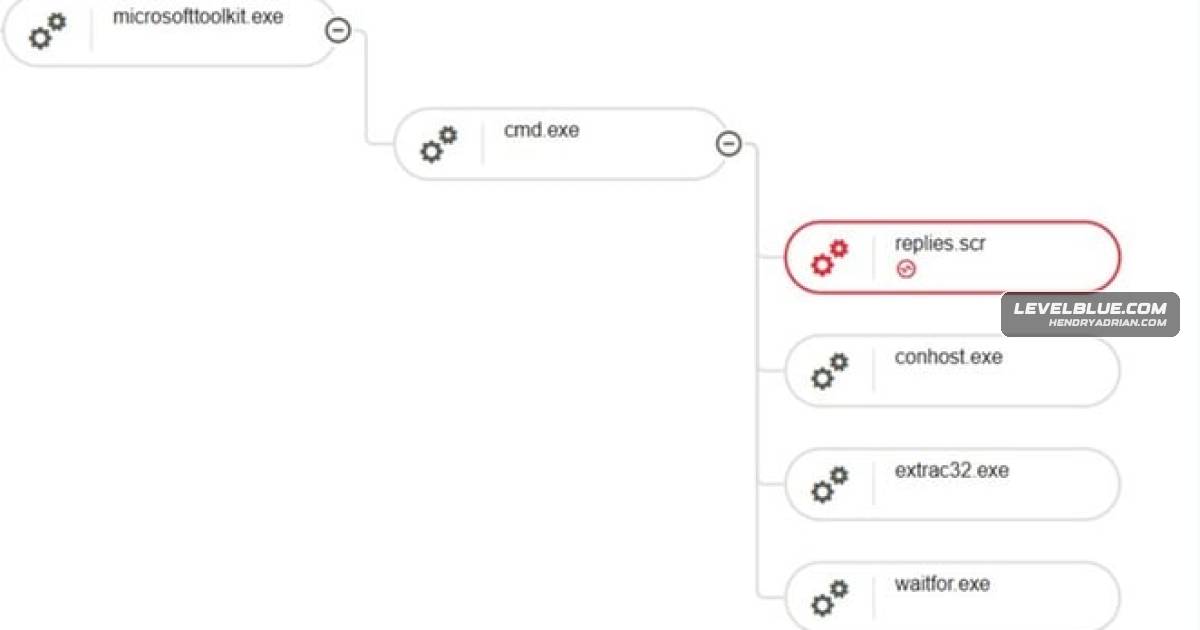
LevelBlue Details AutoIt Loader Chain Linked to Vidar Stealer

LevelBlue traced a Windows infection chain from MicrosoftToolkit.exe through a disguised script and AutoIt loader to communications associated with Vidar. The analysis found anti-analysis and cleanup behavior; credential theft was a potential outcome, not confirmed.

May 8, 2026
Threat Research · bleepingcomputer.com

PCPJack Malware Steals Cloud Credentials and Removes TeamPCP Access

SentinelLabs says PCPJack targets exposed cloud systems, steals credentials, and removes TeamPCP artifacts. The malware spreads through vulnerable services, moves laterally, establishes persistence, and sends encrypted, chunked data to Telegram.

May 8, 2026
Threat Research · bleepingcomputer.com

TCLBanker Banking Trojan Spreads Through WhatsApp and Outlook

Elastic Security Labs describes TCLBanker, a banking trojan delivered through a trojanized Logitech AI Prompt Builder installer. It targets 59 financial and crypto platforms and can spread through victims’ WhatsApp and Outlook accounts.

May 8, 2026
Threat Research · netskope.com

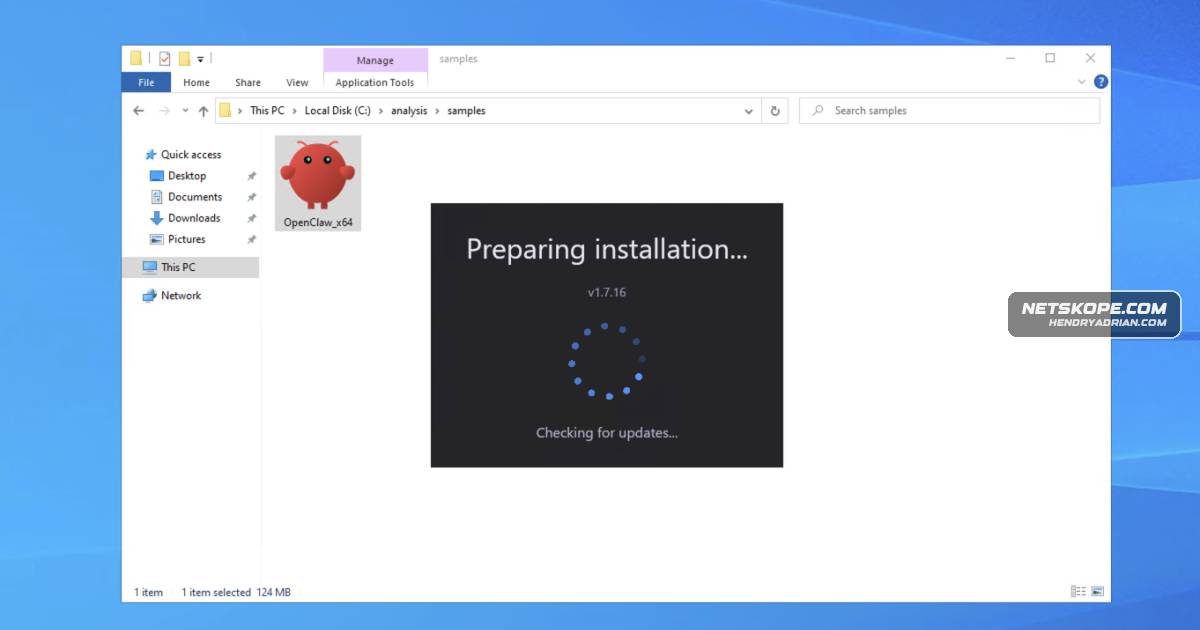
Fake OpenClaw Installers Deliver Rust Malware Targeting Crypto Wallets and Password Managers

Netskope details three waves of a fake OpenClaw installer campaign delivering Rust malware that evades sandboxes, steals credentials from more than 250 browser extensions, and uses layered C2 infrastructure. Hookdeck disabled an abused relay endpoint.

May 7, 2026
Threat Research · huntress.com

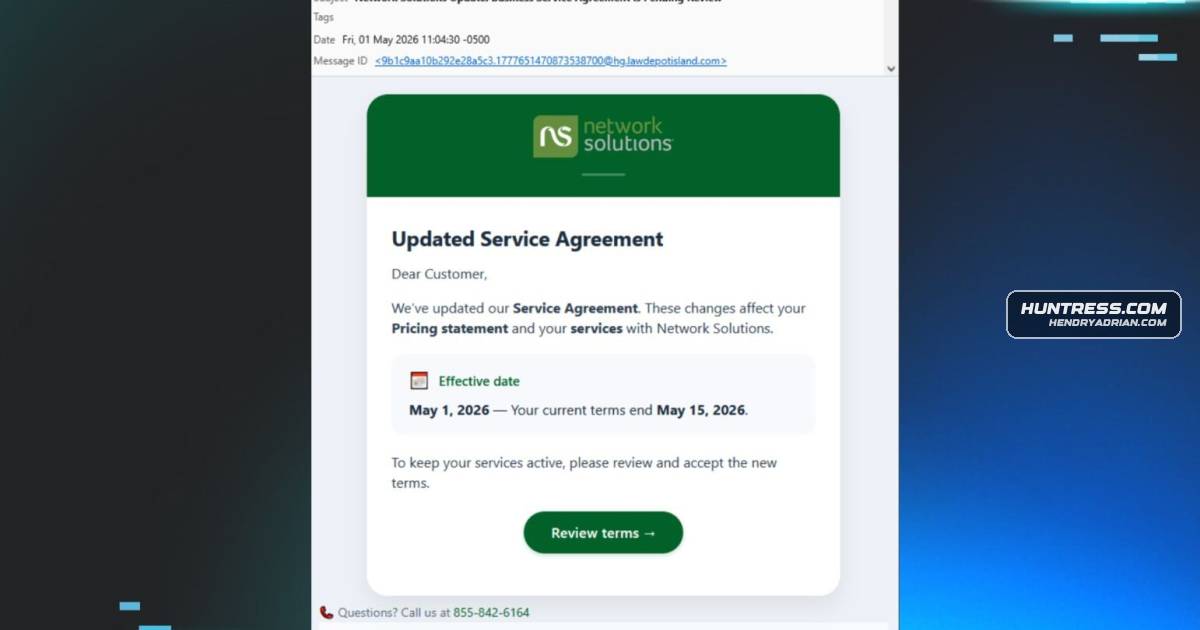
Phishing Campaign Uses Tiflux RMM to Deploy Multiple Remote-Access Tools

Huntress analyzed phishing incidents using Tiflux to install additional remote-access tools, collect system information and screenshots, and establish persistence. The installer also contained outdated components and a driver previously abused for privilege escalation.

May 7, 2026
Threat Research · socket.dev

Five Malicious NuGet Packages Target Developers with Credential and Crypto Wallet Stealer

Socket researchers found five malicious NuGet packages impersonating Chinese .NET libraries. The packages deliver an infostealer targeting browser credentials, crypto wallets, SSH keys, and files; about 65,000 downloads are reported, and the packages remain available.

May 6, 2026
Threat Research · opensourcemalware.com

Lazarus Group Hides Malware in Git Hooks Used in Fake Coding Assessments

OpenSourceMalware reports that Lazarus-linked fake coding-assessment repositories use Git hooks to fetch OS-specific payloads, potentially leading to credential and crypto-wallet theft. It shares infrastructure and a GitHub hunt query.

May 6, 2026
Threat Research · bleepingcomputer.com

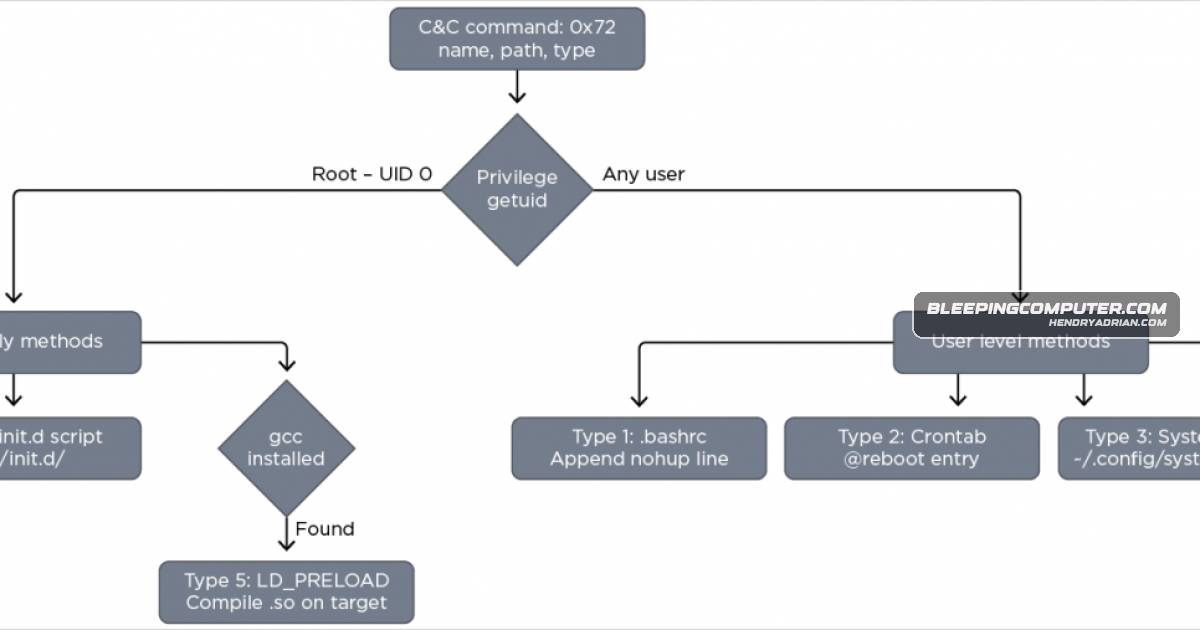
Quasar Linux Malware Targets Developers With Rootkit and Credential-Stealing Capabilities

Trend Micro describes QLNX, a Linux implant targeting developer and DevOps environments with fileless execution, multiple persistence methods, a dual-layer rootkit, and credential theft. Its deployment scale and attribution are unknown.

May 6, 2026
Threat Research · welivesecurity.com

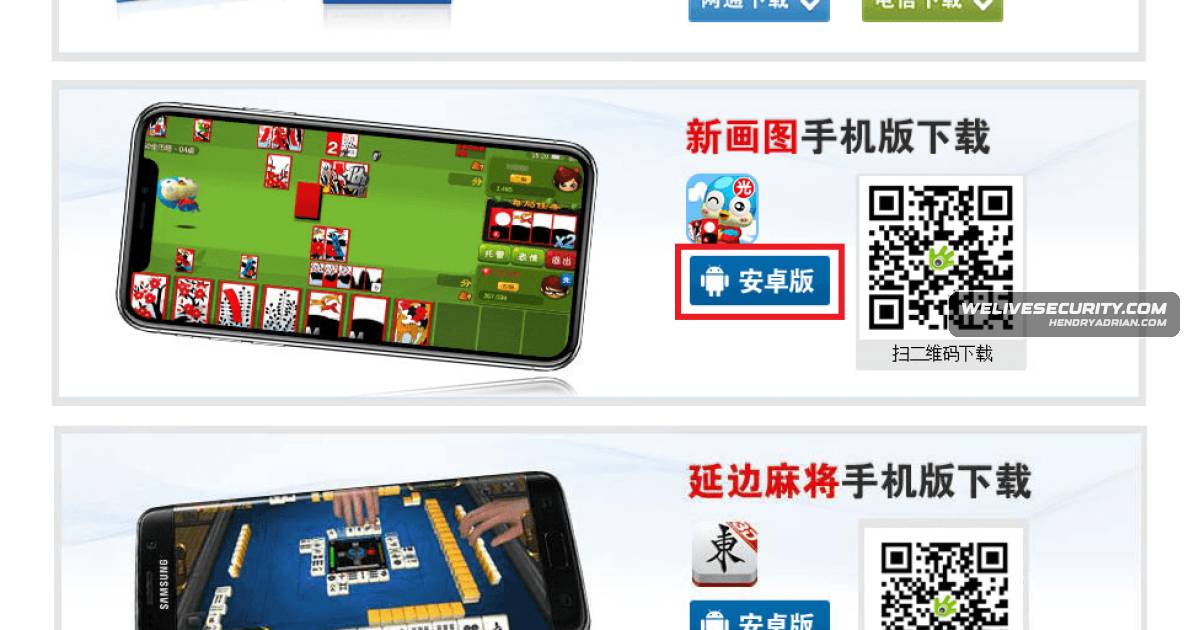
ScarCruft Used Trojanized Gaming Updates and Android Apps to Deliver BirdCall

ESET details a ScarCruft supply-chain campaign targeting a Yanbian gaming platform: trojanized Windows updates delivered RokRAT and BirdCall, while Android games carried a newly analyzed BirdCall variant built for surveillance and data theft.

May 5, 2026
Threat Research · censys.com

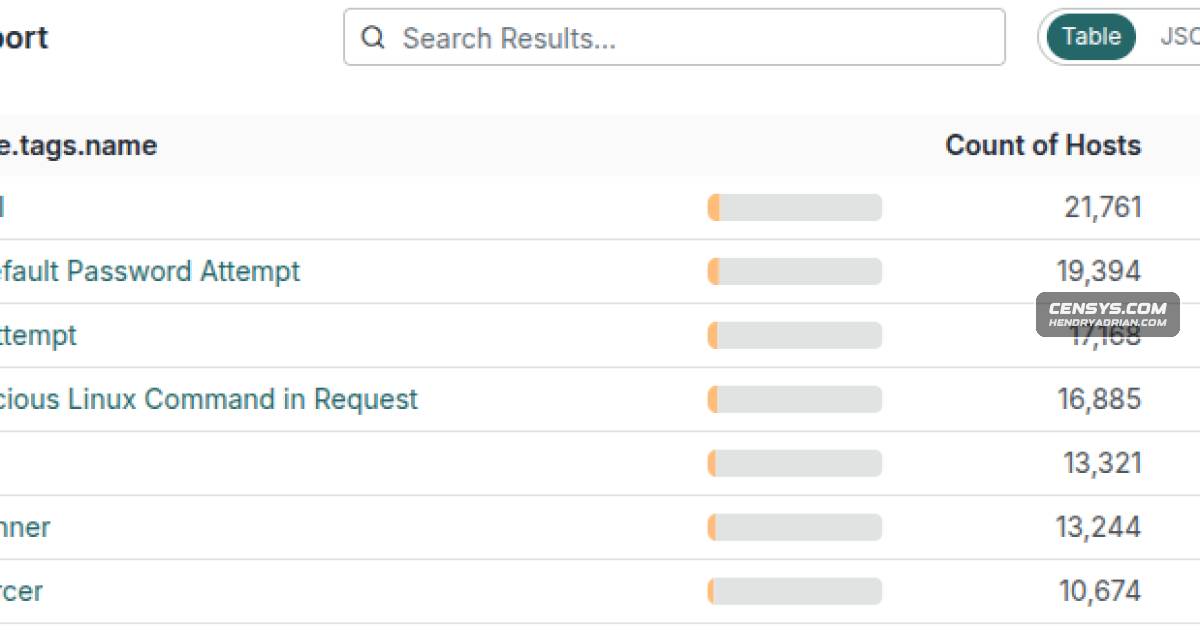
Censys Investigates cPanel Surge Amid Mirai and “.sorry” Ransomware Activity

Censys reports that cPanel/WHM hosts accounted for nearly 80% of newly malicious hosts on May 1, alongside Mirai deployments and a possible ransomware campaign marked by exposed files renamed “.sorry”; the campaign’s full scope remains unclear.

May 5, 2026
Threat Research · kudelskisecurity.com

Compromised DAEMON Tools Installers Deliver Malware in Targeted Supply-Chain Attack

Kaspersky reports that trojanized DAEMON Tools versions 12.5.0.2421–12.5.0.2434 have distributed malware since April 8, 2026. The active campaign uses compromised installers to deliver targeted payloads and communicate with env-check[.]daemontools[.]cc.

May 5, 2026
PreviousPage 64 of 104 Next
© 2026 cyber.hendryadrian.com