cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2486 articles

Threat Research · trendmicro.com

Fake Claude Code Install Pages Deliver Multi-Stage Malware

Trend Micro details InstallFix, a campaign using Google Ads and fake Claude Code installation pages to trick users into running commands that launch multi-stage malware with evasion, persistence, and data-collection capabilities.
May 5, 2026
Threat Research · zscaler.com

Malicious OpenClaw Skill Delivers Remcos RAT and GhostLoader

A deceptive OpenClaw skill identified in March 2026 used installation instructions to deliver Remcos RAT on Windows and GhostLoader across platforms, stealing credentials and other sensitive data from developer environments.

May 5, 2026
Threat Research · hunt.io

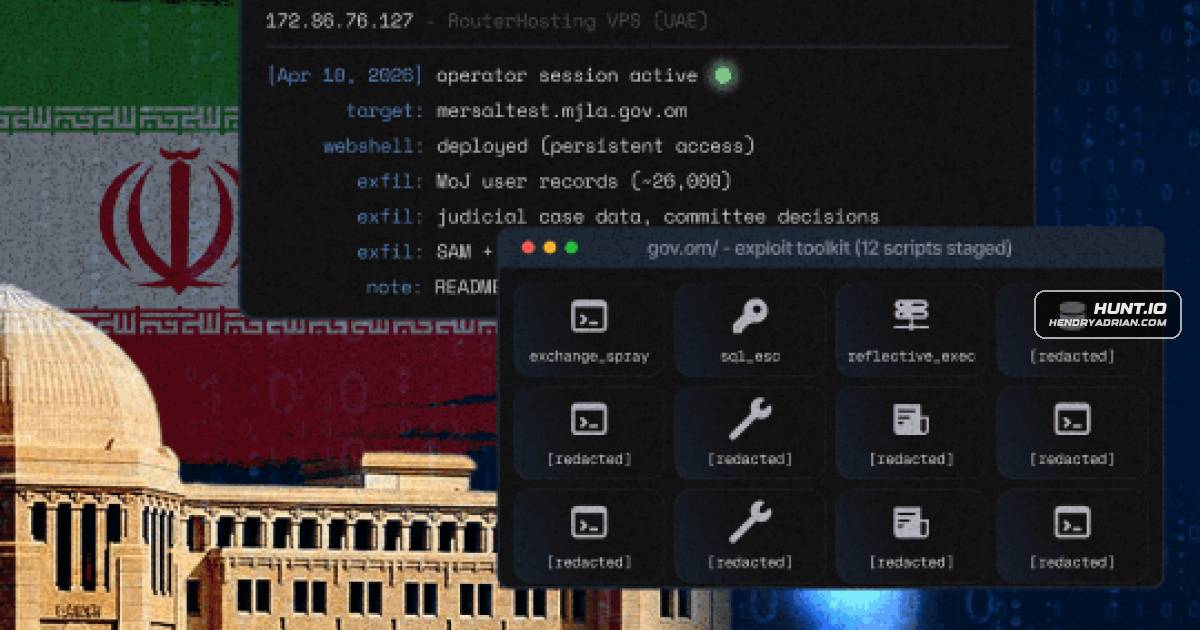
Investigation Details Intrusion Targeting 12 Omani Government Entities, With 26,000 Records Extracted

An exposed server revealed tooling and logs from an intrusion targeting Omani government entities. Evidence shows access to the Ministry of Justice and Legal Affairs and extraction of more than 26,000 user records, judicial data, and registry hives.

May 5, 2026
Threat Research · microsoft.com

Microsoft Details Multi-Stage AiTM Phishing Campaign Targeting 35,000 Users

Microsoft analyzed an April 2026 phishing campaign that targeted more than 35,000 users with compliance-themed emails and PDF lures, leading to an AiTM flow designed to capture authentication tokens. Microsoft recommends email, browser, and phishing-resistant MFA mitig

May 4, 2026
Threat Research · thehackernews.com

VENOMOUS#HELPER Phishing Campaign Uses Dual RMM Tools Against 80+ Organizations

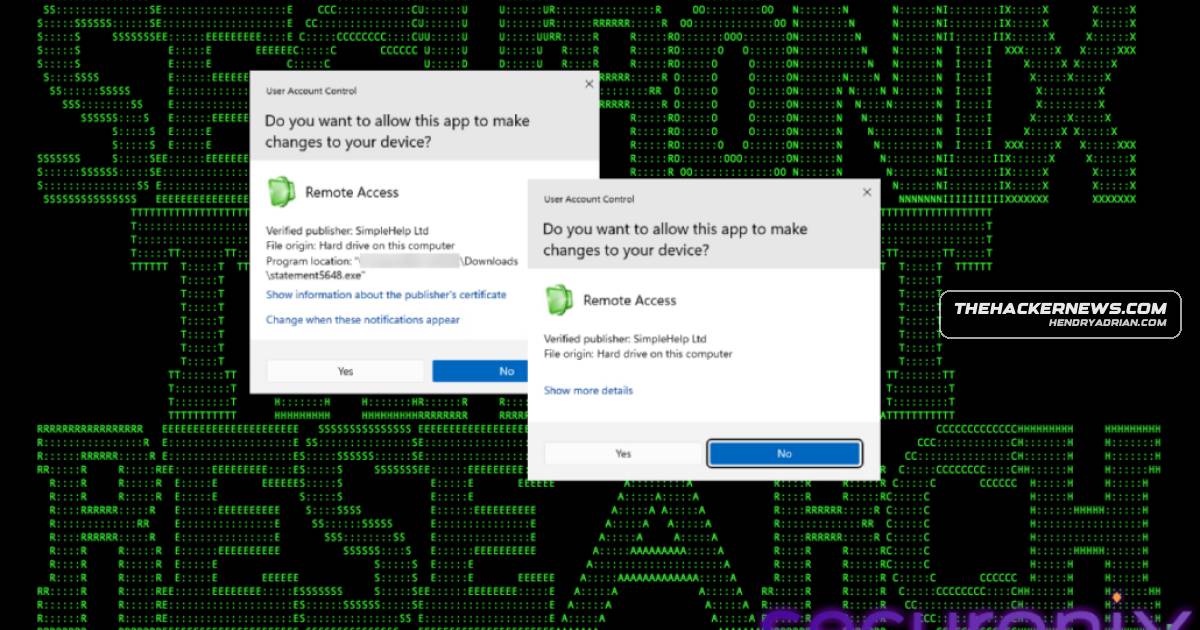
Securonix reports that VENOMOUS#HELPER has affected 80+ organizations, mostly in the U.S. SSA-themed phishing delivers SimpleHelp with persistent access and SYSTEM-level privileges, then installs ScreenConnect as a fallback; the actor is unknown.

May 4, 2026
Threat Research · huntress.com

Ouroboros Enables Persistent Credential Extraction from Windows Server 2025 dMSAs

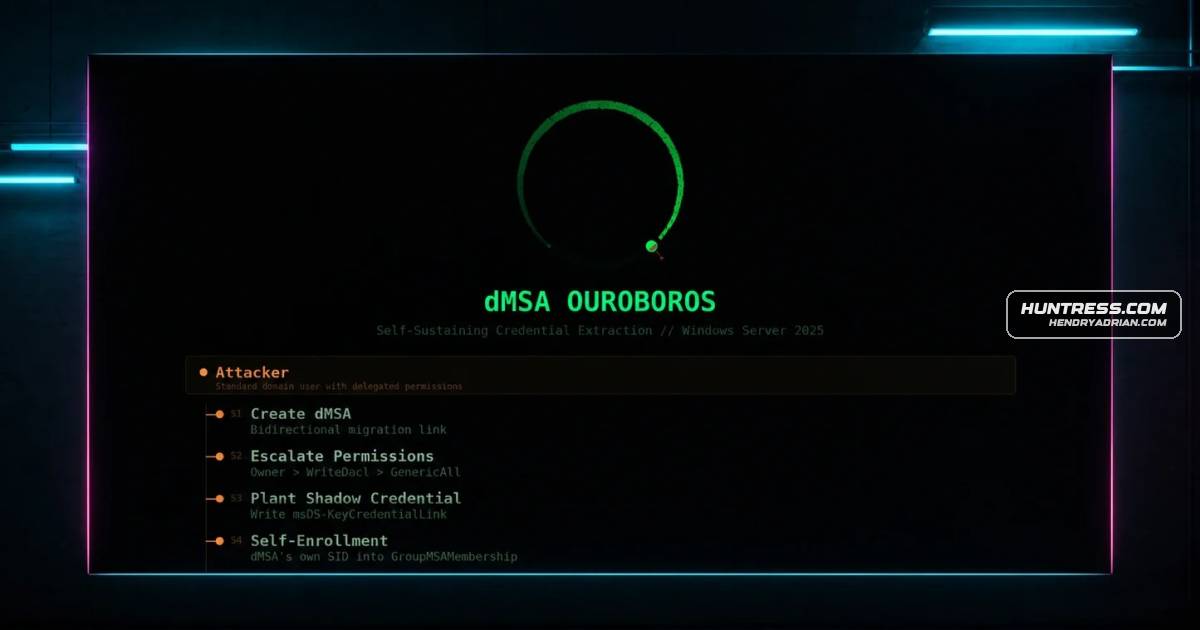
Researchers describe Ouroboros, an Active Directory technique that uses a planted Shadow Credential and dMSA self-enrollment to extract a superseded account’s NT hash, persisting through password rotation and attacker-account deletion.

May 4, 2026
Threat Research · trendmicro.com

Researchers Detail QLNX Linux RAT With Rootkit, PAM Backdoor and Developer Credential Theft

Trend Micro analyzes QLNX, a previously undocumented Linux RAT that uses stealth, multiple persistence methods, rootkit and PAM backdoor capabilities, and credential harvesting to target developer and cloud access.

May 4, 2026
Threat Research · bleepingcomputer.com

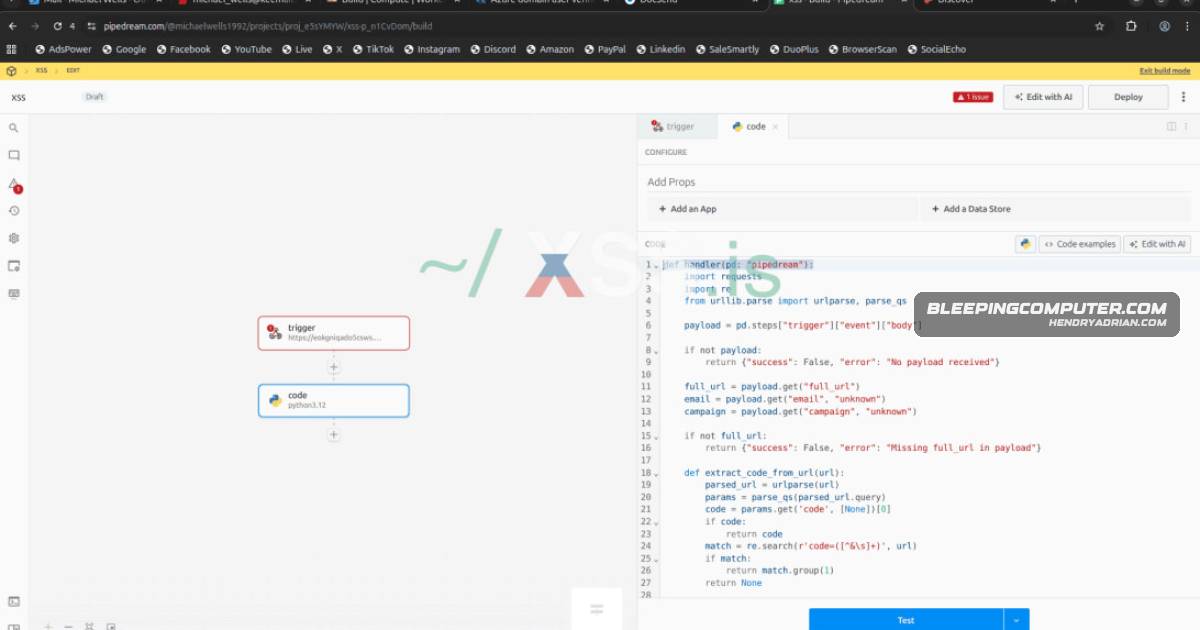
ConsentFix v3 Automates OAuth Phishing Against Azure Accounts

ConsentFix v3 automates OAuth authorization-code phishing using pre-consented Microsoft apps and Pipedream to capture refresh tokens; the article says the variant's uptake among cybercriminals remains unclear.

May 2, 2026
Threat Research · securityweek.com

Securonix Details Deep#Door Backdoor’s Espionage and Disruption Capabilities

Securonix describes Deep#Door, a Python-based Windows backdoor that disables security controls, establishes layered persistence, evades analysis, and supports espionage and destructive actions.

May 1, 2026
Threat Research · unit42.paloaltonetworks.com

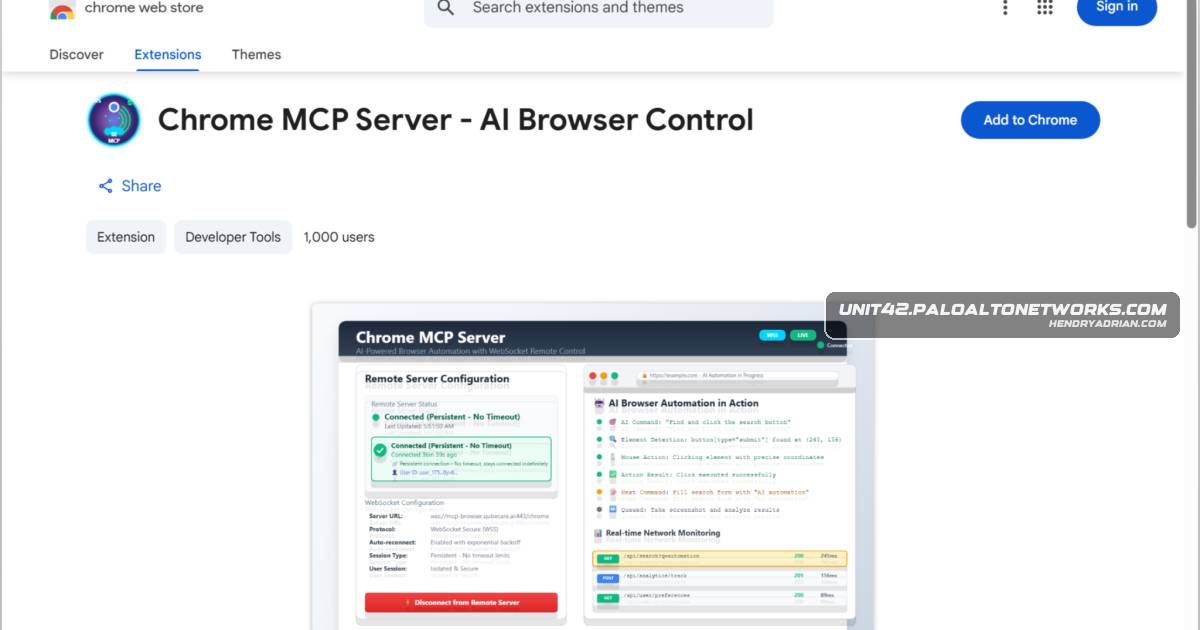
Unit 42 Details Malicious Behaviors in 18 GenAI-Themed Chrome Extensions

Unit 42 analyzed 18 GenAI-themed Chrome extensions and found RAT, data-theft, search-hijacking and spyware behaviors, including email and API-key theft. Google removed extensions or warned owners; researchers recommend least-privilege controls and runtime monitoring.

May 1, 2026
Threat Research · acronis.com

Acronis Finds 575 Malicious OpenClaw Skills in AI Supply-Chain Attacks

Acronis TRU reports 575 malicious OpenClaw skills across 13 developer accounts and analyzes trojanized Hugging Face artifacts delivering Windows and macOS payloads, including AMOS Stealer. It details indirect prompt injection, staged execution, evasion and defenses.

May 1, 2026
Threat Research · socket.dev

Malicious Ruby Gems and Go Modules Steal Secrets and Tamper With CI

Socket researchers detail a BufferZoneCorp campaign using malicious Ruby gems and Go modules to steal developer credentials, tamper with CI dependency settings, intercept Go execution, and establish SSH persistence.

May 1, 2026
Threat Research · socket.dev

Malicious Intercom PHP Package Spreads Mini Shai-Hulud Supply-Chain Attack to Packagist

A compromised intercom/intercom-php 5.0.2 artifact used a Composer plugin to download Bun and run credential-stealing malware during installation or updates. Packagist removed the artifact; affected users should investigate hosts and rotate exposed credentials.

Apr 30, 2026
Threat Research · netskope.com

Compromised Intercom npm Package Steals GitHub Credentials Using Shai-Hulud-Style Attack

Intercom TypeScript Library version 7.0.4 runs an install-time infostealer that harvests GitHub credentials and retrieves C2 instructions through GitHub commit search. Users are advised to check for suspicious activity and rotate credentials.

Apr 30, 2026
Threat Research · levelblue.com

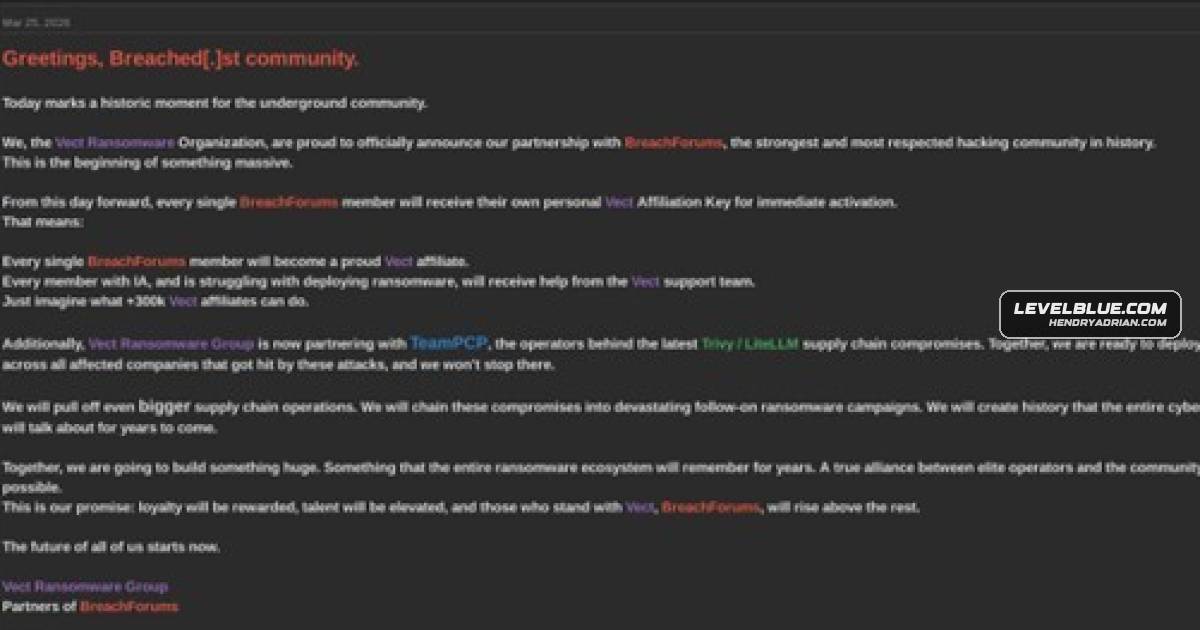
Researchers Detail Vect Ransomware’s Multi-Platform Payloads and Tactics

SpiderLabs analyzes Vect RaaS payloads for Windows, Linux and ESXi, detailing lateral movement, credential use, ChaCha20 encryption and process/VM termination. It reports links to TeamPCP and assesses a possible Devman connection that remains uncertain.

Apr 30, 2026
Threat Research · socket.dev

Compromised Lightning PyPI Releases Steal Credentials and Spread Through GitHub and npm

Socket reports that malicious lightning versions 2.6.2 and 2.6.3 run an obfuscated payload on import, stealing credentials and attempting to poison GitHub repositories and infect npm packages.

Apr 30, 2026
Threat Research · wiz.io

Research Finds Permission Bypasses and Secret-Exposure Risks in AI-Powered GitHub Actions

Wiz researchers found permission-check bypasses and prompt-injection paths to expose local credentials in AI-powered GitHub Actions. OpenAI changed bot controls, Anthropic updated its documentation, and Wiz reported vulnerable workflows to maintainers.

Apr 30, 2026
Threat Research · opensourcemalware.com

Mini Shai-Hulud Worm Reuses VS Code Task Execution Technique in SAP CAP npm Attack

Mini Shai-Hulud spread through four SAP CAP npm packages, using VS Code tasks and Claude Code hooks to execute payloads and propagate across repositories. The article details its links to PolinRider and recommends hunting and credential rotation.

Apr 30, 2026
Threat Research · securelist.com

Silver Fox Uses Modified RustSL to Deliver ValleyRAT and ABCDoor

Researchers attribute tax-themed phishing campaigns in India and Russia to Silver Fox, detailing modified RustSL loaders, ValleyRAT delivery and the ABCDoor Python backdoor, which they traced in the group's arsenal to at least late 2024.

Apr 30, 2026
Threat Research · stepsecurity.io

Obfuscated Credential Stealer Found in Compromised PyPI lightning Releases

StepSecurity reports that lightning 2.6.2 and 2.6.3 contain an import-triggered, obfuscated JavaScript payload that steals credentials, abuses GitHub to exfiltrate data, and infects npm tarballs. Full payload analysis is ongoing.

Apr 30, 2026
Threat Research · stepsecurity.io

Step Security Reports Shai-Hulud Worm in Hijacked Intercom npm Package, Targeting Cloud Credentials

Step Security reports [email protected] was published with a Shai-Hulud payload that runs through a new preinstall hook, targets GitHub/npm and AWS, GCP and Azure credentials, and uses private GitHub repositories for exfiltration and npm tokens to propagate.

Apr 30, 2026
Threat Research · huntress.com

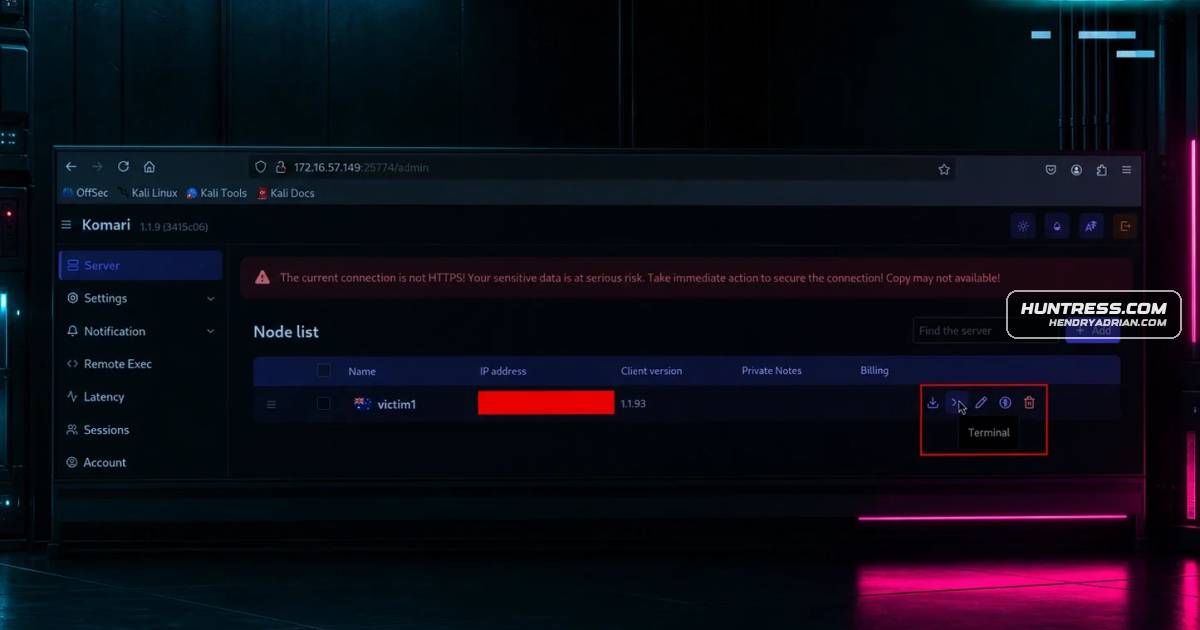
Threat Actor Used Komari Monitoring Agent as a SYSTEM-Level Backdoor in VPN Intrusion

Huntress details an intrusion using stolen VPN credentials and Impacket to install Komari as a persistent SYSTEM-level backdoor. The partner network was isolated before the operator issued Komari commands; no data loss was reported.

Apr 30, 2026
Threat Research · huntress.com

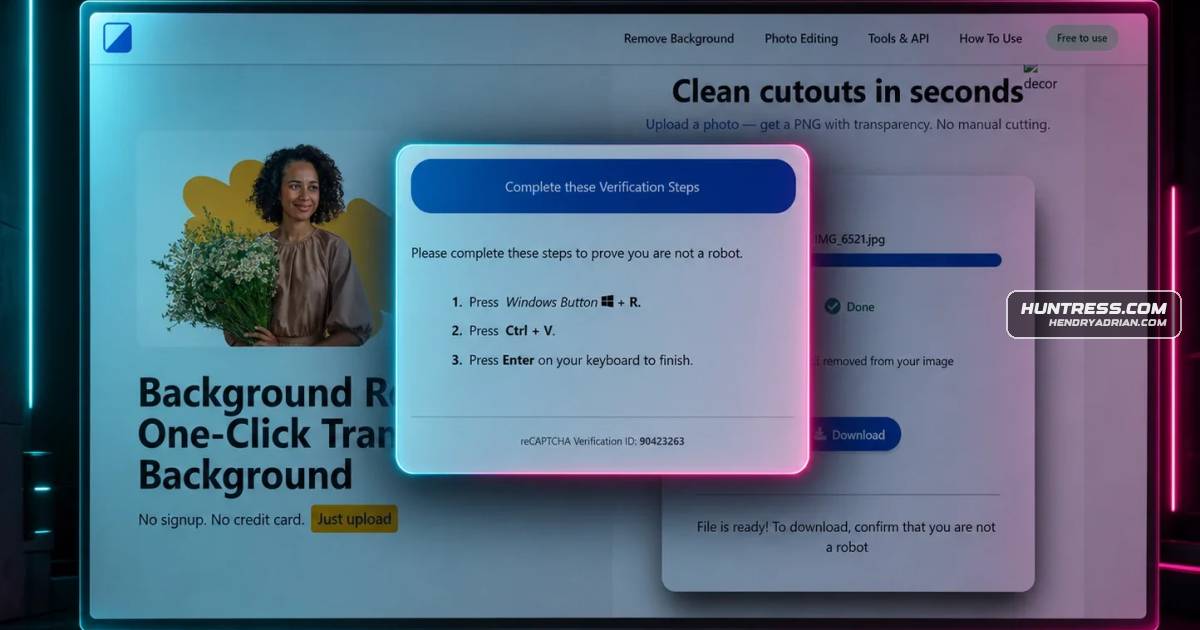
ClickFix Lure Delivers CastleLoader, NetSupport RAT and Credential-Stealing Malware

Huntress details a fake image-background remover campaign that uses ClickFix to deliver CastleLoader, NetSupport RAT and a .NET stealer targeting browser credentials, wallet data and Telegram sessions. The analysis also describes the malware chain and defensive controls

Apr 30, 2026
Threat Research · kudelskisecurity.com

Mini Shai Hulud Supply-Chain Campaign Expands to PyPI and npm Packages

Kudelski Security reports that the TeamPCP-attributed Mini Shai Hulud campaign compromised npm and PyPI packages to steal developer and CI/CD credentials, with propagation through maintainer accounts and automated workflows.

Apr 30, 2026
PreviousPage 65 of 104 Next
© 2026 cyber.hendryadrian.com