
ScarCruft Used Trojanized Gaming Updates and Android Apps to Deliver BirdCall
Summary
ESET details a ScarCruft supply-chain campaign targeting a Yanbian gaming platform: trojanized Windows updates delivered RokRAT and BirdCall, while Android games carried a newly analyzed BirdCall variant built for surveillance and data theft.
Key points
- ESET says ScarCruft compromised the sqgame gaming platform, distributing malicious Windows updates and two trojanized Android games.
- A modified Windows mono.dll downloaded RokRAT, which was then used to deploy BirdCall; ESET found the update package had been malicious since at least November 2024, but it was no longer malicious at the time of writing.
- The Android games contained a BirdCall backdoor repackaged into the apps; ESET identified seven versions developed between approximately October 2024 and June 2025.
- Android BirdCall can collect contacts, SMS, call logs, documents, media, and private keys, and can take screenshots and record audio.
- The backdoor used cloud storage, including Zoho WorkDrive, for command-and-control and data exfiltration; compromised South Korean websites hosted payloads or configuration data.
- ESET assesses that the campaign likely targeted ethnic Koreans in Yanbian for espionage, possibly including people of interest to North Korea; this targeting and motive are presented as assessments.
- ESET said it notified sqgame of the compromise in December 2025 and had not received a response; the trojanized Android files were still available at the time of writing.
Article Details
- Attack Vectors
- The sqgame Windows update package was compromised with a trojanized mono.dll downloader that fetched RokRAT; RokRAT was then used to install BirdCall.
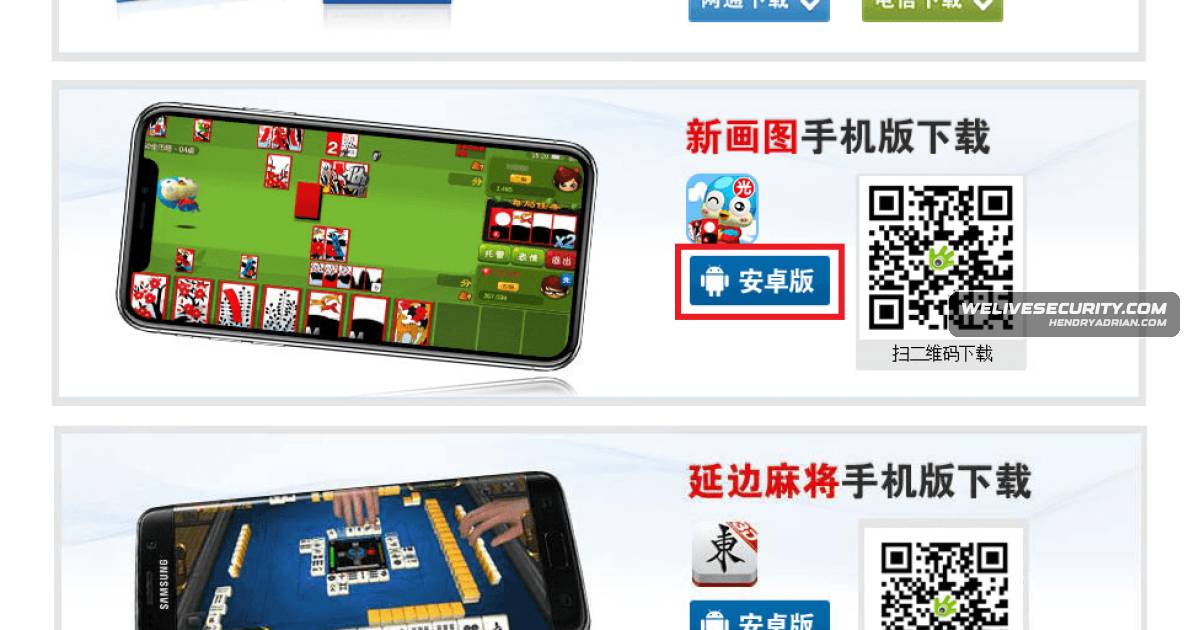
- Two Android games, ybht.apk and sqybhs.apk, were repackaged with Android BirdCall and distributed through the sqgame platform. ESET found evidence that victims likely downloaded and installed them through a web browser.
- Compromised South Korean websites hosted shellcode, clean mono.dll files, and images containing Android BirdCall cloud-configuration updates.
- BirdCall used Zoho WorkDrive cloud drives for command-and-control and data exfiltration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 1980food[.]co[.]kr | Compromised South Korean site used to host Android BirdCall configuration. |
| DOMAIN | cndsoft[.]co[.]kr | Compromised South Korean site used to host shellcode. |
| DOMAIN | colorncopy[.]co[.]kr | Compromised South Korean site associated with hosting shellcode. |
| DOMAIN | inodea[.]com | Compromised South Korean site used to host Android BirdCall configuration. |
| DOMAIN | sejonghaeun[.]com | Compromised South Korean site used to host a clean mono.dll library. |
| DOMAIN | sqgame[.]com[.]cn | Compromised gaming-platform domain used to host trojanized games and malicious updates. |
| DOMAIN | swr[.]co[.]kr | Compromised South Korean site associated with hosting shellcode. |
| DOMAIN | www[.]lawwell[.]co[.]kr | Compromised South Korean site used to host shellcode and a clean mono.dll library. |
| IPV4 | 114[.]108[.]128[.]157 | IP address hosting the compromised inodea[.]com site used to host Android BirdCall configuration. |
| IPV4 | 211[.]239[.]117[.]117 | IP address hosting the compromised 1980food.co[.]kr site used to host Android BirdCall configuration. |
| IPV4 | 221[.]143[.]43[.]214 | IP address hosting the compromised www.lawwell.co[.]kr site used for shellcode and a clean mono.dll library. |
| IPV4 | 222[.]231[.]2[.]20 | IP address associated with compromised South Korean sites used to host shellcode. |
| IPV4 | 222[.]231[.]2[.]23 | IP address hosting the compromised sejonghaeun[.]com site used to host a clean mono.dll library. |
| IPV4 | 222[.]231[.]2[.]41 | IP address hosting the compromised cndsoft.co[.]kr site used to host shellcode. |
| IPV4 | 39[.]106[.]249[.]68 | IP address hosting the compromised sqgame site and its trojanized games and malicious updates. |
| SHA1 | 01a33066fbc6253304c92760916329abd50c3191 | Hash of sqybhs.apk, identified as a trojanized game containing Android BirdCall version 2.0. |
| SHA1 | 03e3ece9f48cf4104aafc535790ca2fb3c6b26cf | Hash of ybht.apk, identified as a trojanized game containing Android BirdCall version 1.3. |
| SHA1 | 2b81f78ec4c3f8d6cf8f677d141c5d13c35333af | Hash of sqybhs.apk, identified as a trojanized game containing Android BirdCall version 1.5. |
| SHA1 | 409c5acaed587f62f7e23da47f72c4d9ec3144d9 | Hash of a malicious downloader that led to the RokRAT backdoor. |
| SHA1 | 59a9b9d47ae36411b277544f25ad2cc955d8dd2c | Hash of ybht.apk, identified as a trojanized game containing Android BirdCall version 1.0. |
| SHA1 | 7356d7868c81499fb4e720f7c9530e5763b4c1d0 | Hash of sqybhs.apk, identified as a trojanized game containing Android BirdCall version 1.0. |
| SHA1 | 95bdb94f6767a3cce6d92363bbf5bc84b786bdb0 | Hash of the trojanized mono.dll library used in the Windows update attack. |
| SHA1 | b06110e0feb7592872e380b7e3b8f77d80dd1108 | Hash of a Windows BirdCall backdoor sample identified in the article as a publicly available dump. |
| SHA1 | fc0c691db7e2d2bd3b0b4c1e24d18df72168b7d9 | Hash of sqybhs.apk, identified as a trojanized game containing Android BirdCall version 1.5. |
| URL | hxxp[:]//sqgame[.]com[.]cn/sqybhs.apk | URL serving the trojanized New Drawing game containing Android BirdCall. |
| URL | hxxp[:]//sqgame[.]com[.]cn/ybht.apk | URL serving the trojanized Yanbian Red Ten game containing Android BirdCall. |
| URL | hxxp[:]//xiazai[.]sqgame[.]com[.]cn/dating/20240429.zip | URL of the malicious Windows update package containing the trojanized mono.dll. |
MITRE ATT&CK
T1027.013 · Encrypted/Encoded FileThe article reports encrypted strings and loading-chain components in BirdCall, as well as encrypted shellcode in the trojanized mono library.T1056.001 · KeyloggingThe Windows BirdCall version can log keystrokes.T1059.003 · Windows Command ShellThe Windows BirdCall version can execute shell commands, including commands through cmd.exe.T1102.002 · Bidirectional CommunicationBirdCall uses cloud-storage drives, including Zoho WorkDrive, to receive commands and communicate with its operators.T1113 · Screen CaptureThe Windows BirdCall version can capture screenshots.T1195.002 · Compromise Software Supply ChainScarCruft compromised the sqgame Windows update server to distribute an update containing a trojanized mono.dll.T1407Android BirdCall can download and load a newer version of itself from an APK update file.T1429Android BirdCall can record audio through the device microphone.T1474.003Android games distributed through the compromised sqgame platform were repackaged with the BirdCall backdoor.T1497 · Virtualization/Sandbox EvasionThe downloader in the trojanized mono.dll checked for analysis tools and virtual-machine environments before proceeding.T1513Android BirdCall can periodically capture screenshots on infected devices.T1555 · Credentials from Password StoresThe Windows BirdCall version can obtain saved passwords from browsers and other software.T1567.002 · Exfiltration to Cloud StorageBirdCall exfiltrates collected information through cloud-storage services.T1584.004 · ServerCompromised South Korean websites hosted BirdCall configuration images, shellcode, and other attack components.T1608.001 · Upload MalwareTrojanized Android games and malicious updates were hosted on the compromised sqgame site.
Threat Actors
Malware
BirdCallScarCruft (APT37) conducted a multiplatform supplyâchain attack against a Yanbian-themed gaming platform, trojanizing Windows update components and Android game APKs to deliver the BirdCall backdoor for espionage.RokRATThe Windows update package contained a patched mono.dll downloader that fetched RokRAT and subsequently deployed the BirdCall backdoor.
Vendors
Products
New Drawing[Filenames ] Malicious or modified installers and libraries – ybht.apk (trojanized Yanbian Red Ten), sqybhs.apk (trojanized New Drawing), mono.dll (trojanized library used in Windows update).sqgameScarCruft compromised the sqgame gaming platform serving the Yanbian region to distribute malicious updates and trojanized Android games.Yanbian Red Ten[Filenames ] Malicious or modified installers and libraries – ybht.apk (trojanized Yanbian Red Ten), sqybhs.apk (trojanized New Drawing), mono.dll (trojanized library used in Windows update).Zoho WorkDriveThe campaign targeted ethnic Koreans in the Yanbian region and used compromised South Korean websites and Zoho WorkDrive cloud accounts for command-and-control.
Countries
Chinasupply-chain attack by North Korea-aligned APT group ScarCruft, targeting the Yanbian region in China – home to ethnic Koreans and a crossing point for North Korean refugees and defectors.North KoreaVictims are likely ethnic Koreans in Yanbian, a border region with North Korea, suggesting espionage goals focused on defectors or individuals of interest to the DPRK.South KoreaIt primarily focuses on South Korea, but other Asian countries have also been targeted.