
Fake Hugging Face Repository Used to Deliver Sefirah Infostealer
Summary
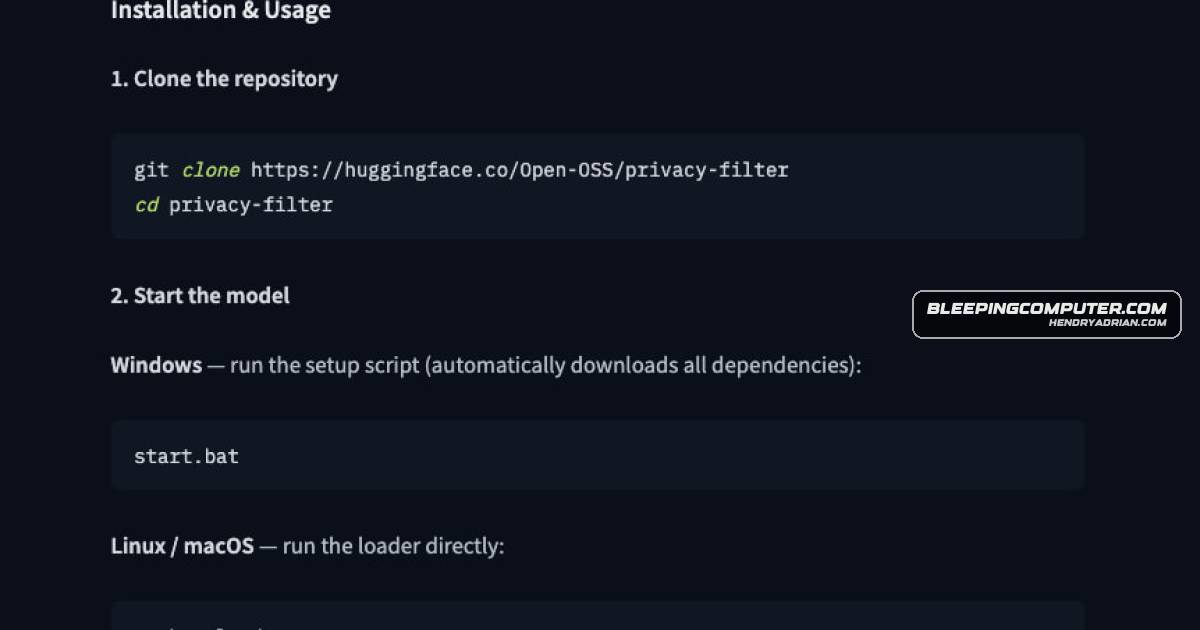
HiddenLayer found a typosquatted Hugging Face repository impersonating OpenAI’s Privacy Filter. Its loader deployed the Sefirah infostealer against Windows users; the repo reached 244,000 downloads, a count researchers said may have been inflated.
Key points
- The Open-OSS/privacy-filter repository copied OpenAI’s Privacy Filter project and briefly reached #1 on Hugging Face before the platform removed it.
- Its loader disabled SSL verification, fetched a JSON payload, and ran a PowerShell command that downloaded a batch file and the Sefirah payload.
- Sefirah targeted browser data, Discord tokens, cryptocurrency wallets, credentials, sensitive files, system information, and screenshots.
- The malware compressed and exfiltrated stolen data to recargapopular[.]com.
- HiddenLayer reported anti-analysis checks for virtual machines, sandboxes, debuggers, and analysis tools.
- Researchers linked the loader infrastructure to other malicious repositories and noted overlaps with an npm typosquatting campaign distributing WinOS 4.0.
- The number of victims is unknown; researchers said the 244,000 download count may have been artificially inflated. They advised affected users to reimage machines and rotate credentials, wallets, and sessions.
Article Details
- Attack Vectors
- A typosquatted Hugging Face repository impersonated OpenAI’s Privacy Filter project and used a deceptive loader.py script to deliver malware to Windows users.
- The loader disabled SSL verification, decoded a URL to an external resource, and fetched a JSON payload containing a PowerShell command. That command downloaded start.bat, which downloaded and executed the Sefirah payload.
- Sefirah collected browser data, Discord tokens, cryptocurrency wallet data, credentials, sensitive local files, system information, and multi-monitor screenshots, then exfiltrated compressed data to a C2 server.
- Defensive Notes
- Users who downloaded files from the malicious repository were advised to reimage the affected machine.
- Rotate stored credentials, replace cryptocurrency wallets and seed phrases, and invalidate browser sessions and tokens.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | recargapopular[.]com | C2 server to which Sefirah exfiltrated compressed stolen data. |
MITRE ATT&CK
T1005 · Data from Local SystemSefirah collected local browser data, Discord data, wallet data, credentials, and other sensitive files.T1036.005 · Match Legitimate Resource Name or LocationThe malicious Open-OSS/privacy-filter repository typosquatted OpenAI’s legitimate Privacy Filter project.T1041 · Exfiltration Over C2 ChannelSefirah exfiltrated compressed stolen data to the reported C2 server.T1059.001 · PowerShellThe loader fetched a JSON payload containing a PowerShell command that downloaded a batch file.T1059.003 · Windows Command ShellThe downloaded start.bat batch file downloaded and executed the final payload.T1059.006 · PythonThe repository’s loader.py script executed Python code to retrieve and run the next stage.T1082 · System Information DiscoverySefirah collected system information from infected machines.T1105 · Ingress Tool TransferThe loader and subsequent batch file downloaded payloads from external resources.T1113 · Screen CaptureSefirah captured multi-monitor screenshots.T1497.001 · System ChecksSefirah checked for virtual machines and sandboxes to evade analysis.T1539 · Steal Web Session CookieSefirah targeted browser cookies and session tokens.T1552.001 · Credentials In FilesSefirah collected SSH, FTP, and VPN credentials and configuration files, as well as sensitive local files.T1555.003 · Credentials from Web BrowsersSefirah targeted saved passwords and other data from Chromium- and Gecko-based browsers.T1562.001 · Disable or Modify ToolsThe batch file added Sefirah to Microsoft Defender’s exclusions.T1622 · Debugger EvasionSefirah checked for debuggers as part of its anti-analysis behavior.
Malware
Vendors
Products
Hugging FaceA malicious Hugging Face repository impersonated OpenAI’s “Privacy Filter” project and used a deceptive loader to deploy the Sefirah infostealer against Windows users.Microsoft Defender Antimalware Platform(start.bat) that performs privilege escalation, downloads the final payload (sefirah), adds it to Microsoft Defender’s exclusions for it, and executes it.Microsoft WindowsA malicious Hugging Face repository impersonated OpenAI’s “Privacy Filter” project and used a deceptive loader to deploy the Sefirah infostealer against Windows users.Privacy FilterA malicious Hugging Face repository impersonated OpenAI’s “Privacy Filter” project and used a deceptive loader to deploy the Sefirah infostealer against Windows users.