cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2486 articles

Threat Research · circleid.com

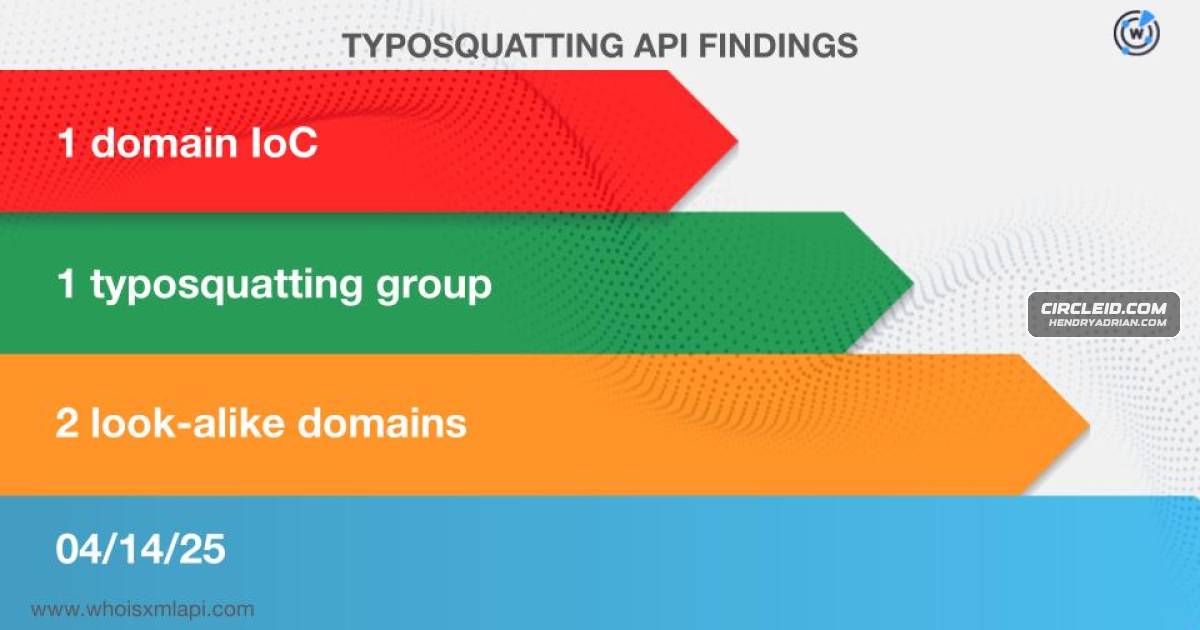
DNS and WHOIS Analysis Maps Infrastructure Linked to Eight Iran-Affiliated APT Groups

Researchers analyzed 191 DNS, domain, IP and WHOIS indicators linked to eight Iran-affiliated APT groups, identifying historical resolutions, likely malicious registrations, look-alike domains and infrastructure assessed as part of an impersonation campaign.
May 13, 2026
Threat Research · securitylabs.datadoghq.com

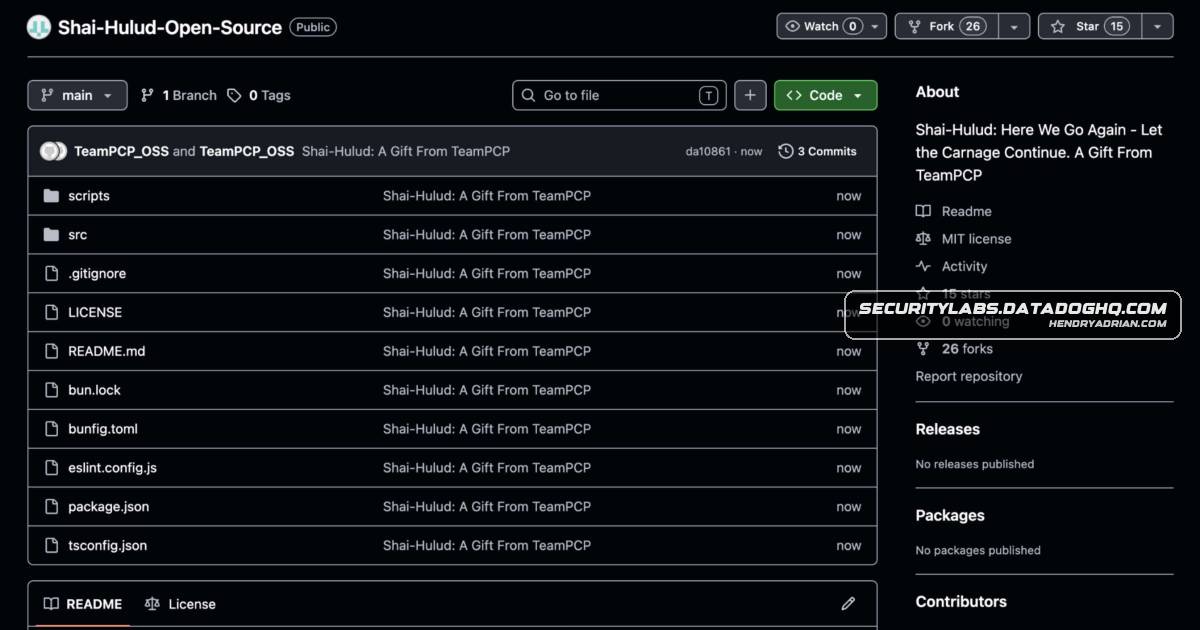
Shai-Hulud Source Code Reveals Extensive Credential Theft and Supply-Chain Capabilities

Static analysis of a GitHub repository attributed to TeamPCP describes a modular framework for stealing credentials, exfiltrating data, and poisoning repositories and npm packages, including through developer-tool hooks and forged provenance.

May 13, 2026
Threat Research · cloudsek.com

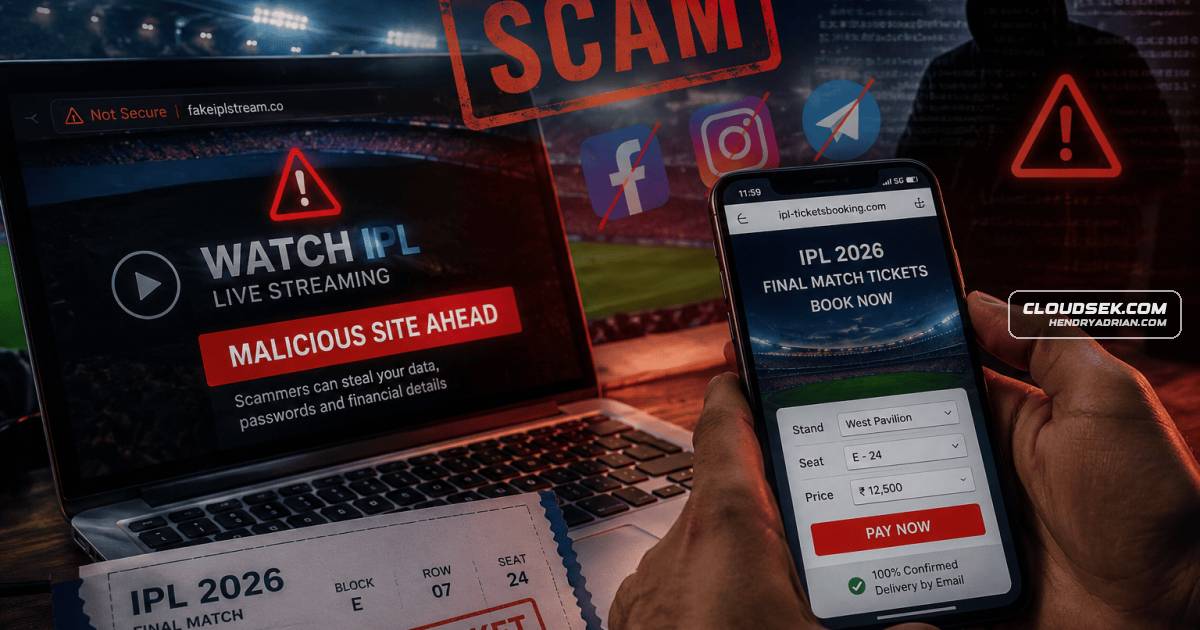
CloudSEK Details IPL Ticket Scams and Streaming Sites Delivering macOS Infostealer

CloudSEK identified more than 600 fake IPL ticket domains and 400-plus streaming sites. Some streaming redirects deliver SHub Stealer, which targets macOS credentials, browser data, crypto wallets and other files, and establishes persistence.

May 13, 2026
Threat Research · trendmicro.com

TeamPCP Supply-Chain Attacks Steal Credentials Through KICS and elementary-data

Trend Micro analyzes two TeamPCP supply-chain attacks that abused CI/CD and release workflows to distribute credential stealers, compromise downstream software, and access cloud secrets.

May 13, 2026
Threat Research · cyberscoop.com

Mini Shai-Hulud Campaign Injected Credential-Stealing Malware Into Open-Source Packages

The Mini Shai-Hulud campaign reportedly compromised hundreds of packages through manipulated GitHub Actions pipelines, targeting developer and cloud credentials. TanStack says affected versions were removed; researchers reported limited community spread and no evidence

May 12, 2026
Threat Research · sysdig.com

Scanner Probed PraisonAI Auth Bypass 3 Hours After CVE-2026-44338 Disclosure

Sysdig says a scanner probed PraisonAI’s unauthenticated legacy API 3 hours 44 minutes after CVE-2026-44338 was disclosed. The flaw can trigger configured workflows; upgrade to 4.6.34 or later and restrict exposure.

May 12, 2026
Threat Research · reversinglabs.com

ReversingLabs Identifies 163 Samples Tied to Linux Dirty Frag Flaw

ReversingLabs says it identified 163 samples tied to Linux CVE-2026-31431, including ELF, Python and PyPI variants, with samples dating to April 29, 2026. It released YARA rules and hunting queries; Ubuntu fixes are available.

May 12, 2026
Threat Research · bleepingcomputer.com

TeamPCP-Attributed Shai-Hulud Campaign Uses Stolen OIDC Tokens to Publish Malicious Packages

A Shai-Hulud campaign attributed to TeamPCP used stolen OIDC tokens and CI/CD credentials to publish malicious packages across npm, PyPI and Composer, stealing developer secrets and establishing persistence.

May 12, 2026
Threat Research · security.com

Seedworm Campaign Used DLL Sideloading in Espionage Against South Korean Electronics Maker

A technical report details a Seedworm espionage campaign targeting at least nine organizations across four continents in early 2026, including a South Korean electronics maker, using DLL sideloading, credential theft and public-service data staging.

May 12, 2026
Threat Research · thehackernews.com

TeamPCP’s Mini Shai-Hulud Worm Spreads Through Compromised npm and PyPI Packages

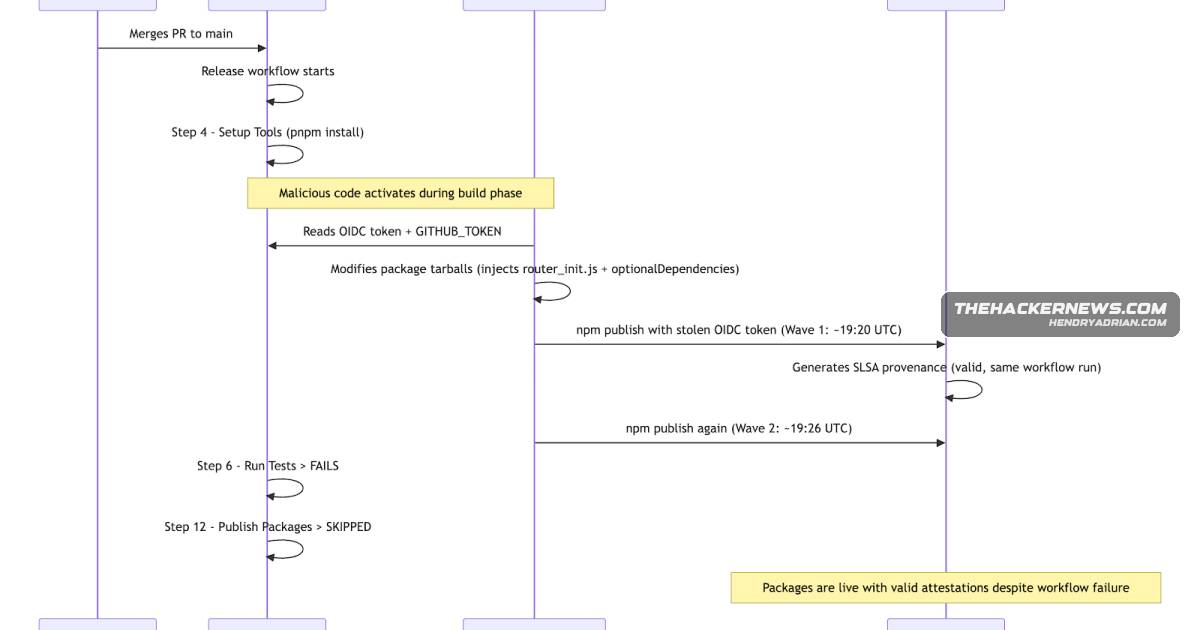
Reports link TeamPCP’s Mini Shai-Hulud worm to compromised npm and PyPI packages. The malware steals credentials, abuses GitHub Actions and OIDC tokens, persists in developer IDEs, and propagates through package publishing.

May 12, 2026
Threat Research · reliaquest.com

ReliaQuest Details ClickFix Intrusion Using PySoxy for Backup Access

ReliaQuest investigated an April 2026 ClickFix intrusion that paired scheduled-task persistence and PowerShell C2 with PySoxy proxying. Endpoint controls blocked both channels, but the task kept trying to restart the activity.

May 12, 2026
Threat Research · wiz.io

TeamPCP Supply-Chain Attack Compromises npm and PyPI Packages

TeamPCP compromised npm and PyPI packages using a credential-stealing worm. The report details a GitHub Actions cache-poisoning attack, exfiltration methods, destructive persistence, affected packages, and recommended response steps.

May 12, 2026
Threat Research · esentire.com

Tycoon 2FA Operators Turn to OAuth Device-Code Phishing to Steal Microsoft 365 Tokens

eSentire analyzes a Tycoon 2FA campaign that uses a multi-layer phishing chain to trick victims into authorizing OAuth device codes, giving operators Microsoft 365 tokens despite successful MFA.

May 12, 2026
Threat Research · hunt.io

CVE-2025-32975 KACE SMA Breach Revealed HIQ Data and 60+ Downstream Clients

Hunt.io says attackers exploited KACE SMA's CVSS 10.0 authentication bypass to compromise HIQ, exposing a database tied to 60+ client organizations and a 308 MB post-exploitation toolkit. More than 12,000 internet-facing appliances reportedly show pre-patch versions.

May 12, 2026
Threat Research · socket.dev

Mini Shai-Hulud Supply-Chain Campaign Compromises TanStack and Other npm, PyPI Packages

Socket reports malicious npm and PyPI package releases linked to Mini Shai-Hulud. The malware targets CI, cloud, and developer credentials, can propagate through package publishing, and prompted TanStack to remove affected versions and harden workflows.

May 11, 2026
Threat Research · thehackernews.com

Mr_Rot13 Linked to Active Exploitation of cPanel CVE-2026-41940

QiAnXin XLab links Mr_Rot13 to active exploitation of cPanel CVE-2026-41940. The reported chain uses SSH persistence, a web shell, credential theft, and the cross-platform Filemanager backdoor.

May 11, 2026
Threat Research · bleepingcomputer.com

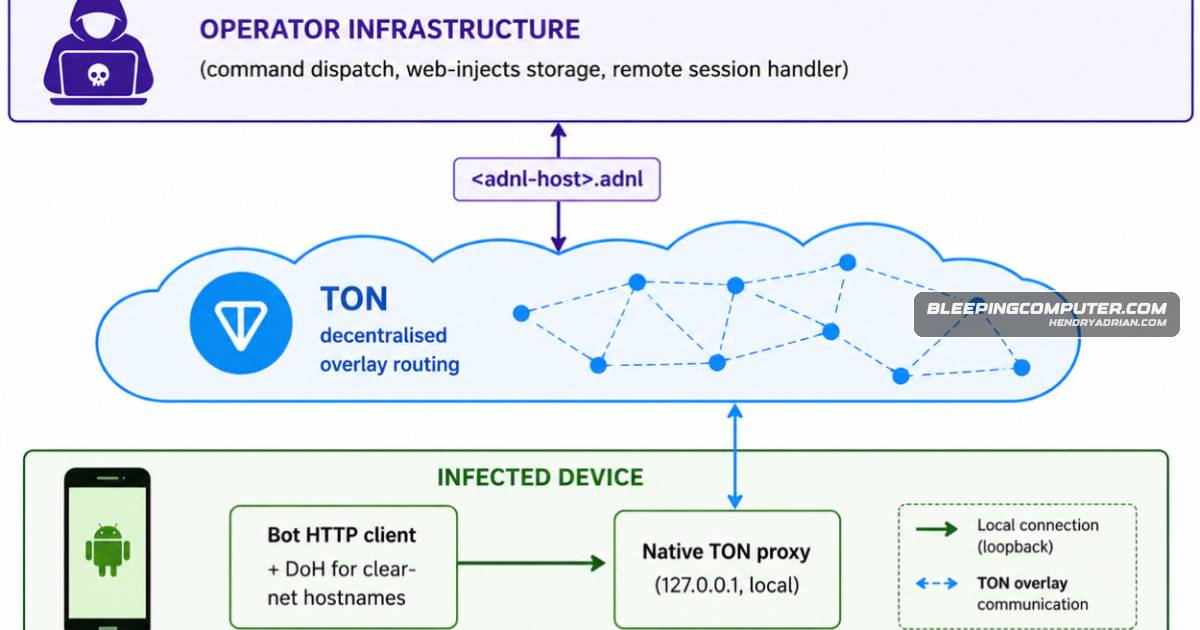
Trickmo.C Android Banker Uses TON for Covert Command-and-Control

ThreatFabric reports that Trickmo.C, delivered through fake TikTok and streaming apps, targets banking and crypto-wallet users in France, Italy, and Austria. It uses TON .ADNL addresses for C2 and adds networking and tunneling commands.

May 11, 2026
Threat Research · thedfirreport.com

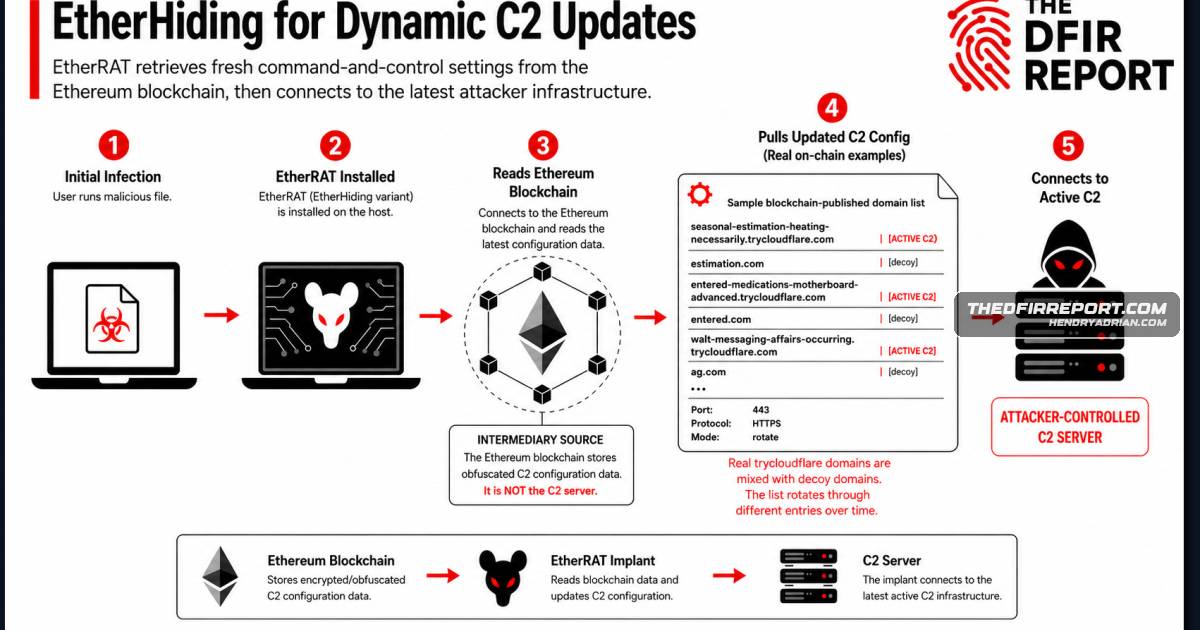
EtherRAT and TukTuk C2 Lead to The Gentlemen Ransomware Deployment

A DFIR investigation details an intrusion that began with a malicious MSI, used EtherRAT and TukTuk for access and C2, exfiltrated data to Wasabi, and ended in domain-wide The Gentlemen ransomware deployment.

May 11, 2026
Threat Research · guardsix.com

Supply-Chain Attacks Exploit Trusted Maintainers, CI/CD Workflows and Software Tools

An analysis of recent supply-chain campaigns finds a recurring pattern: attackers compromise trusted people or components, abuse release and automation workflows, steal secrets, and propagate through connected software ecosystems.

May 11, 2026
Threat Research · varonis.com

Azure Cosmos for PostgreSQL Flaw Allowed RCE via Configuration Injection

Varonis Threat Labs found that Azure Cosmos for PostgreSQL’s management API validation could be bypassed with control characters to inject PostgreSQL settings and enable potential RCE via archive_command. Microsoft confirmed the issue and fixed it in summer 2025.

May 11, 2026
Threat Research · stepsecurity.io

TeamPCP's Mini Shai-Hulud Worm Compromises TanStack npm Packages

StepSecurity analyzes Mini Shai-Hulud's npm supply-chain campaign, detailing runner-memory credential theft, self-propagation and malicious releases with valid provenance. TanStack confirmed 84 malicious versions across 42 packages.

May 11, 2026
Threat Research · threatfabric.com

TrickMo Android Malware Adds TON-Based C2 and Network Tunnelling

A new TrickMo variant targeting banking and wallet users in France, Italy, and Austria moves C2 to TON and adds SSH tunnelling and SOCKS5 proxying, turning infected Android devices into network pivots.

May 11, 2026
Threat Research · trendmicro.com

AI-Augmented Campaigns Target Government and Financial Organizations in Latin America

Trend Micro details two campaigns using agentic AI to support intrusions against government and financial organizations in Latin America, including reconnaissance, lateral movement, backdoor deployment, and data exfiltration.

May 11, 2026
Threat Research · genians.co.kr

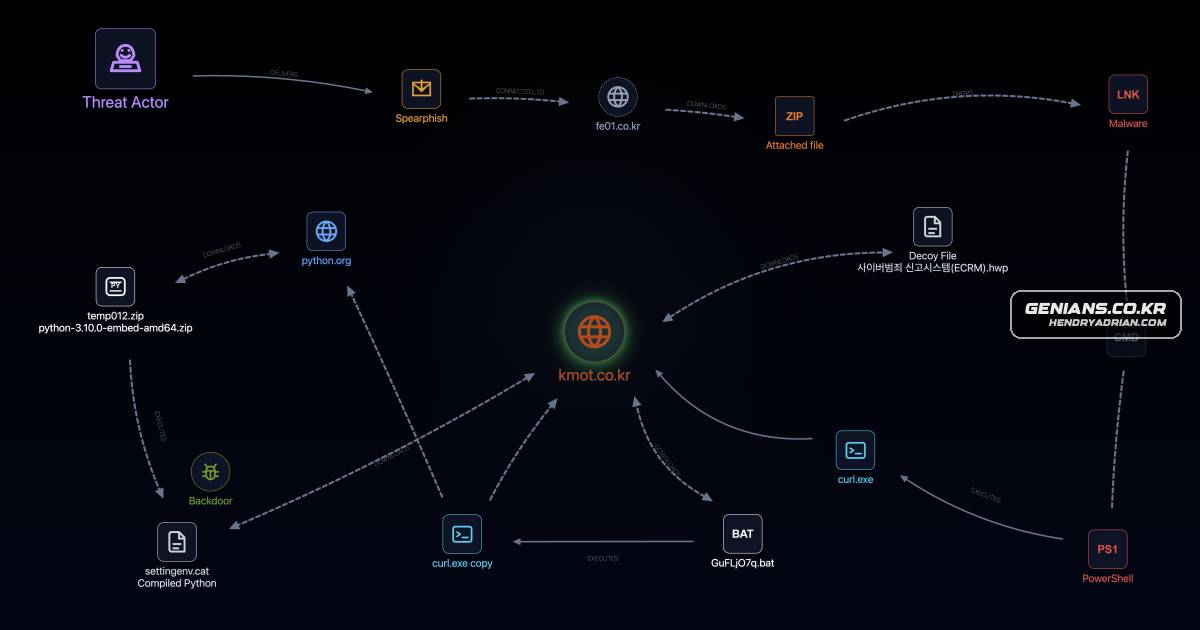
APT37-Linked Campaign Uses Phishing and Obfuscated Scripts to Deploy Python Backdoor

Genians details a suspected APT37-linked spear-phishing campaign that uses ZIP-delivered LNK files, obfuscated scripts, and a disguised Python bytecode payload to install a persistent backdoor for remote command execution.

May 10, 2026
PreviousPage 63 of 104 Next
© 2026 cyber.hendryadrian.com