
ESET Uncovers 28 CallPhantom Android Apps That Faked Call Logs to Charge Users
Summary
ESET identified 28 CallPhantom Android apps with more than 7.3 million downloads. The apps fabricated call and message histories, charged users for fake results, and were removed from Google Play after ESET reported them.
Key points
- The 28 apps claimed to retrieve call logs, SMS records, and WhatsApp call history for any number, but could not access real records.
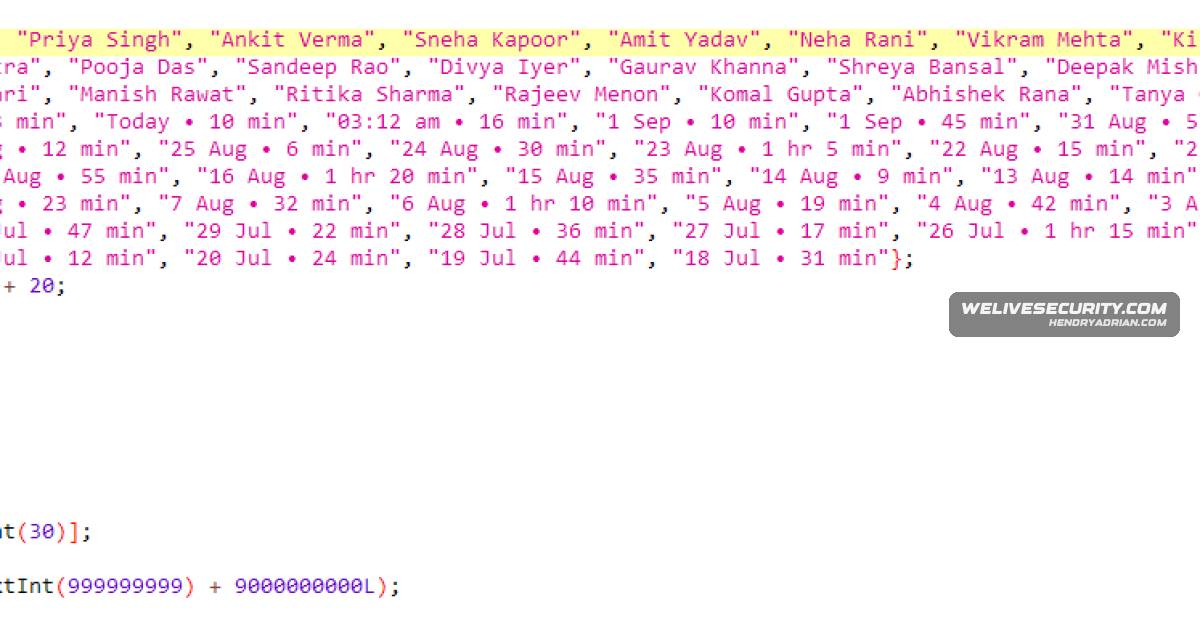
- The apps generated fake results using hardcoded names and templates, timestamps, and randomly generated phone numbers.
- Some apps used Firebase infrastructure to communicate and dynamically fetch payment URLs, allowing operators to change payment destinations.
- Payment methods included Google Play billing, third-party UPI apps, and card checkout forms embedded in the apps.
- One app used fake email-style alerts about supposedly completed results to direct users to a subscription screen.
- ESET reported the apps to Google; all identified apps were removed from Google Play, and existing subscriptions were canceled.
Article Details
- Attack Vectors
- The 28 fraudulent Android apps advertised access to call histories, SMS records, and WhatsApp call logs for any number, then showed fabricated results after users paid.
- The apps generated fake results using hardcoded names, country codes, call times, and durations combined with randomly generated phone numbers.
- Some apps used third-party UPI payment apps or embedded card checkout forms instead of Google Play billing; payment URLs could be fetched dynamically from Firebase Realtime Database.
- One app displayed deceptive email-style alerts claiming results were ready and linked users to a subscription screen.
- CallPhantom used Firebase Cloud Messaging for command-and-control communication.
- Defensive Notes
- Subscriptions purchased through Google Play billing can be reviewed and canceled in the Play Store; the article reports that subscriptions for the removed apps were canceled.
- For purchases made through third-party payment services or direct card entry, contact the payment provider or app developer; Google cannot cancel or refund those payments.
- Google Play refunds may be possible for eligible purchases, subject to Google's refund policy and timing.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | call-history-7cda4-default-rtdb[.]firebaseio[.]com | Firebase Realtime Database domain listed as CallPhantom C&C infrastructure. |
| DOMAIN | call-history-ecc1e-default-rtdb[.]firebaseio[.]com | Firebase Realtime Database domain listed as CallPhantom C&C infrastructure. |
| DOMAIN | ch-ap-4-default-rtdb[.]firebaseio[.]com | Firebase Realtime Database domain listed as CallPhantom C&C infrastructure. |
| DOMAIN | chh1-ac0a3-default-rtdb[.]firebaseio[.]com | Firebase Realtime Database domain listed as CallPhantom C&C infrastructure. |
| IPV4 | 34[.]120[.]160[.]131 | IP address listed as a CallPhantom C&C server. |
| IPV4 | 34[.]120[.]206[.]254 | IP address listed as a CallPhantom C&C server. |
| SHA1 | 04d2221967ffc4312afdc9b06a0b923bf3579e93 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.E. |
| SHA1 | 053a6a723fa2bfda8a1b113e8a98dd04c6eef72a | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.W. |
| SHA1 | 28d3f36bd43d48f02c5058edd1509e4488112154 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.D. |
| SHA1 | 47cee9ded41b953a84fc9f6ed556ec3af5bd9345 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.V. |
| SHA1 | 4b537a7152179bba19d63c9ef287f1ac366ab5cb | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.I. |
| SHA1 | 55d46813047e98879901fd2416a23acf8d8828f5 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.T. |
| SHA1 | 56a4fd71d1e4bba2c5c240be0d794dcff709d9eb | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.M. |
| SHA1 | 6f72ff58a67ef7aaa79ce2342012326c7b46429d | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.H. |
| SHA1 | 77c8b7bec79e7d9ae0d0c02dec4e9ac510429ad8 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.G. |
| SHA1 | 799bb5127ca54239d3d4a14367db3b712012cf14 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.K. |
| SHA1 | 89ecec01ccb15fcdd2f64e07d0e876a9e79dd3ce | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.B. |
| SHA1 | 8ec557302145b40fe0898105752fff5e357d7ac9 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.U. |
| SHA1 | 9199a376b433f888afe962c9bbd991622e8d39f9 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.P. |
| SHA1 | 9484efd4c19969f57afb0c21e6e1a4249c209305 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.L. |
| SHA1 | b7b80fa34a41e3259e377c0d843643ff736803b8 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.O. |
| SHA1 | bb6260ca856c37885bf9e952ca3d7e95398ddabf | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.S. |
| SHA1 | c840a85b5fbaf1ed3e0f18a10a6520b337a94d4c | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.J. |
| SHA1 | cb31ed027fadbfa3bffdbc8a84ee1a48a0b7c11d | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.Q. |
| SHA1 | ce97ca7feecdcafc6b8e9bd83a370dfa5c336c0a | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.B. |
| SHA1 | d021e7a0cf45eecc7ee8f57149138725dc77dc9a | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.Q. |
| SHA1 | e23d3905443cdbf4f1b9ca84a6ff250b6d89e093 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.D. |
| SHA1 | ec5e470753e76614cd28ecf6a3591f08770b7215 | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.F. |
| SHA1 | f0a8ebd7c4179636be752eccfc6bd9e4cd5c7f2c | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.C. |
| SHA1 | fc3ba2edac0bb9801f8535e36f0bcc49ada5fa5a | SHA-1 of an Android CallPhantom sample identified as Android/CallPhantom.N. |
MITRE ATT&CK
Vendors
Products
AndroidCallPhantom is a cluster of 28 fraudulent Android apps on Google Play that falsely claimed to provide call logs, SMS records, and WhatsApp call history for any phone number after payment.Firebase Cloud Messaginginfrastructure for command-and-control communication and payment URL delivery (‘CallPhantom uses Firebase Cloud Messaging for C&C communication’ and URLs were ‘fetched dynamically from a Firebase realtime database’).Firebase Realtime Databaseuses Firebase Cloud Messaging for C&C communication’ and URLs were ‘fetched dynamically from a Firebase realtime database’).Google PlayCallPhantom is a cluster of 28 fraudulent Android apps on Google Play that falsely claimed to provide call logs, SMS records, and WhatsApp call history for any phone number after payment.