
TCLBanker Banking Trojan Spreads Through WhatsApp and Outlook
Summary
Elastic Security Labs describes TCLBanker, a banking trojan delivered through a trojanized Logitech AI Prompt Builder installer. It targets 59 financial and crypto platforms and can spread through victims’ WhatsApp and Outlook accounts.
Key points
- The trojanized Logitech AI Prompt Builder MSI loads TCLBanker through DLL side-loading.
- TCLBanker targets 59 banking, fintech, and cryptocurrency platforms and currently appears focused on Brazil, according to the researchers.
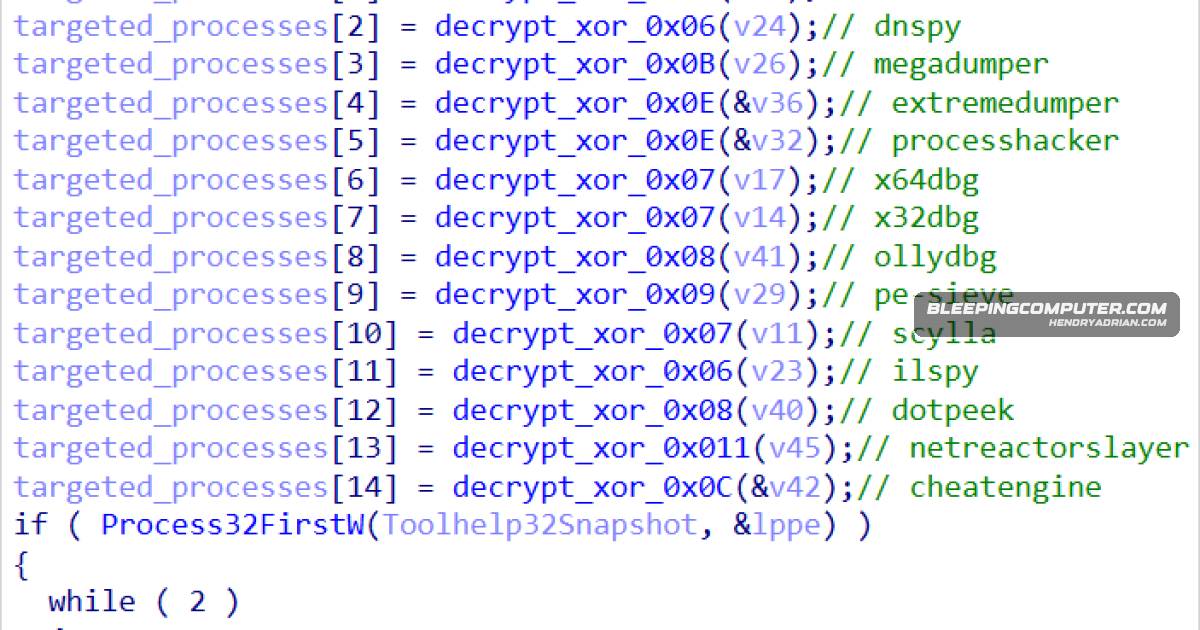
- It uses environment-dependent decryption and monitors for analysis tools to hinder investigation.
- The malware monitors browser activity and can provide operators with remote control, keylogging, screen capture, and file access.
- Fake credential prompts and other overlays can be used to deceive victims and support data theft.
- It searches Chromium profiles for authenticated WhatsApp Web data, then messages contacts; an Outlook module uses COM automation to harvest contacts and send phishing emails.
Article Details
- Attack Vectors
- A trojanized MSI installer for Logitech AI Prompt Builder is used to infect systems; TCLBanker is loaded through DLL side-loading.
- TCLBanker uses WhatsApp Web account data to hijack the victim's account, harvest contacts, and send spam messages linking to distribution platforms.
- A worm module uses Outlook COM automation to harvest contacts and sender addresses, then sends phishing emails from the victim's account.
- Fake credential prompts, PIN keypads, and other overlays are used to collect information from victims.
MITRE ATT&CK
T1056.001 · KeyloggingKeylogging is among the remote capabilities available to TCLBanker's operators.T1057 · Process DiscoveryTCLBanker can enumerate processes and monitors for analysis tools and targeted processes.T1059 · Command and Scripting InterpreterThe malware gives operators the ability to execute shell commands remotely.T1113 · Screen CaptureTCLBanker's operators can capture screenshots and stream the victim's screen.T1115 · Clipboard DataClipboard hijacking is among the malware's remote capabilities.T1140 · Deobfuscate/Decode Files or InformationTCLBanker uses payload decryption routines that are environment-dependent.T1185 · Browser Session HijackingThe malware launches a hidden Chromium instance and uses authenticated WhatsApp Web data to hijack the victim's account.T1497.001 · System ChecksIts payload decryption routines fail in sandboxes or analyst environments, according to Elastic Security Labs.T1566.002 · Spearphishing LinkThe Outlook worm sends phishing emails from the victim's account to direct recipients to TCLBanker distribution platforms.T1574.002 · DLL Side-LoadingTCLBanker is loaded in the legitimate Logitech application through DLL side-loading.T1622 · Debugger EvasionThe malware hunts for analysis and debugging tools, including x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, and de4dot.
Malware
MaverickIt also includes self-spreading worm modules for WhatsApp and Outlook, and Elastic Security Labs says it may represent a major evolution of the Maverick/Sorvepotel family.SORVEPOTELIt also includes self-spreading worm modules for WhatsApp and Outlook, and Elastic Security Labs says it may represent a major evolution of the Maverick/Sorvepotel family.TCLBANKERTCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems.
Products
ChromiumThe malware searches Chromium browser profiles for authenticated WhatsApp Web IndexedDB data, and launches a hidden Chromium instance that hijacks the victim’s account.Logi AI Prompt BuilderTCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems.Microsoft WindowsThe banking module monitors the browser address bar every second using Windows UI Automation APIs, watching for when the victim opens a website of one of its 59 targeted platforms.OutlookIt also includes self-spreading worm modules for WhatsApp and Outlook, and Elastic Security Labs says it may represent a major evolution of the Maverick/Sorvepotel family.WhatsAppIt also includes self-spreading worm modules for WhatsApp and Outlook, and Elastic Security Labs says it may represent a major evolution of the Maverick/Sorvepotel family.
Tools
de4dotIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.dnSpyIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.FridaIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.GhidraIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.IDAIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.Process HackerIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.x64dbgIt also runs a persistent watchdog thread that continuously hunts for analysis tools like x64dbg, IDA, dnSpy, Frida, ProcessHacker, Ghidra, de4dot, and others.
Countries
Industries
BankingTCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems.CryptocurrencyTCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems.fintechTCLBanker is a new banking trojan that targets 59 banking, fintech, and cryptocurrency platforms using a trojanized MSI installer for Logitech AI Prompt Builder to infect systems.