
zLabs Details Android Carrier-Billing Fraud Campaign Using Nearly 250 Apps
Summary
zLabs reports that nearly 250 Android apps targeted users in four countries for carrier-billing and premium SMS fraud. Its analysis describes three malware variants using WebViews, OTP interception, cookie theft and Telegram reporting.
Key points
- zLabs says it detected the campaign in March 2025 and observed activity through the second week of January 2026; portions of its infrastructure remained operational at publication.
- The nearly 250 malicious apps allegedly targeted users in Malaysia, Thailand, Romania and Croatia, checking SIM operator details before initiating fraud.
- One variant used hidden WebViews, JavaScript and intercepted OTPs to automate carrier-billing subscriptions; other variants sent premium SMS messages.
- A variant targeting Thai users reportedly stole carrier-session cookies, captured HTML from billing pages and scheduled SMS messages at delayed intervals.
- Another variant sent attackers Telegram reports containing device identifiers, fake app names, distribution sources, operators and action details.
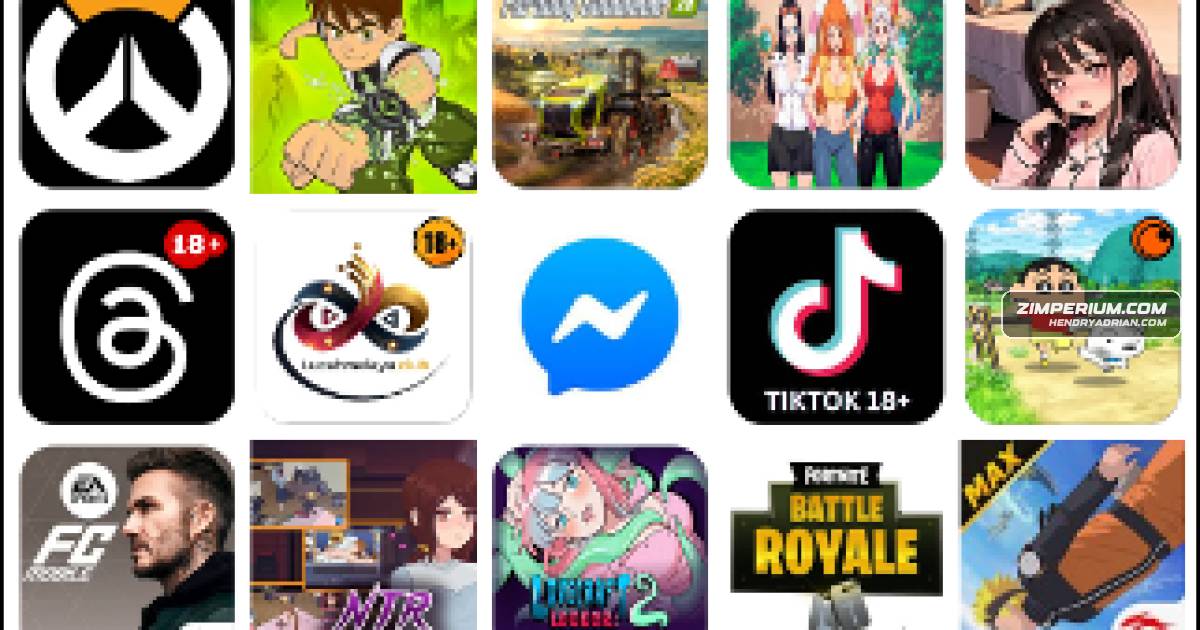
- The apps impersonated popular social media and gaming brands; zLabs describes distribution through social media and search engines.
Article Details
- Attack Vectors
- Nearly 250 malicious Android apps impersonated popular apps and games and were distributed through social media and search engines.
- The apps checked SIM operator codes to target users in Malaysia, Thailand, Romania, and Croatia, while showing benign content to users on non-targeted operators.
- The malware automated carrier-billing subscriptions using hidden WebViews, JavaScript interaction with billing portals, intercepted OTPs, and unauthorized premium SMS messages.
- Some variants fetched subscription instructions from attacker infrastructure, stole carrier-session cookies, and exfiltrated device metadata and billing-page HTML.
- A variant sent installation, permission, and premium-SMS activity reports to a private Telegram channel via the Telegram Bot API; delayed SMS actions were also used.
- Defensive Notes
- The article says Zimperium’s on-device dynamic detection engine and web content filtering can detect and block the malicious applications and traffic before unauthorized premium SMS messages are sent or session tokens are extracted.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | api[.]modobomco[.]com | Alternative command-and-control endpoint identified by the article. |
| DOMAIN | apizep[.]mwmze[.]com | Attacker-operated infrastructure hosting DiGi carrier-billing subscription pages. |
| DOMAIN | modobomz[.]com | Attacker-operated referrer-tracking and campaign-analytics domain. |
| DOMAIN | onesignal[.]mwmze[.]com | Attacker-operated endpoint used to exfiltrate device metadata and carrier-billing HTML. |
| DOMAIN | onesignalmdb[.]modobomz[.]com | Attacker-operated victim-tracking and referrer-validation endpoint that returns short codes and keywords. |
MITRE ATT&CK
T1412The malware abused Google’s SMS Retriever API to capture carrier-billing OTP messages.T1417A variant captured HTML from background-loaded pages and carrier billing portals and sent it to attacker infrastructure.T1422The apps checked SIM operator codes to determine whether a device belonged to a targeted carrier.T1426The malware collected device identifiers, model, OS version, IP address, and user agent for tracking.T1437.001The malware used HTTPS to communicate with attacker servers, fetch subscription targets, and report activity.T1476The campaign distributed malicious apps through social media and search engines while disguising them as legitimate apps.T1582The malware sent unauthorized premium SMS messages, scheduled them, and disabled WiFi to force cellular connectivity.T1603A variant scheduled fraudulent SMS messages for 60 and 90 seconds after an initial burst.T1628.001On devices with non-targeted operators, the malware displayed benign web content to avoid suspicion.T1643The campaign subscribed victims to premium services without consent through automated carrier-billing workflows.T1646The malware exfiltrated device metadata, HTML source, subscription status, and tracking data to attacker infrastructure.
Vendors
Products
AndroidzLabs uncovered a 10-month Android campaign that used nearly 250 malicious apps to conduct carrier billing fraud and premium SMS abuse across Malaysia, Thailand, Romania, and Croatia.Google SMS Retriever API[T1412 ] Capture SMS Messages – It used the Google SMS Retriever API to automatically capture OTP messages for billing confirmation (‘abuse of Google’s SMS Retriever API to intercept carrier billing confirmation codes’).Mobile Runtime Protection (zDefend)Zimperium’s Mobile Threat Defense (MTD) and Mobile Runtime Protection (zDefend) protect customers from the 250 malicious applications identified in this fraudulent operation through its advanced, on-device dynamicTelegramThe operation impersonated popular apps and brands, used WebView automation, OTP interception, and Telegram reporting, and remains partially active with several infrastructure domains still operational.
Countries
CroatiazLabs uncovered a 10-month Android campaign that used nearly 250 malicious apps to conduct carrier billing fraud and premium SMS abuse across Malaysia, Thailand, Romania, and Croatia.MalaysiazLabs uncovered a 10-month Android campaign that used nearly 250 malicious apps to conduct carrier billing fraud and premium SMS abuse across Malaysia, Thailand, Romania, and Croatia.RomaniazLabs uncovered a 10-month Android campaign that used nearly 250 malicious apps to conduct carrier billing fraud and premium SMS abuse across Malaysia, Thailand, Romania, and Croatia.ThailandzLabs uncovered a 10-month Android campaign that used nearly 250 malicious apps to conduct carrier billing fraud and premium SMS abuse across Malaysia, Thailand, Romania, and Croatia.