
Ghostwriter Uses Prometheus-Themed Phishing to Target Ukrainian Government
Summary
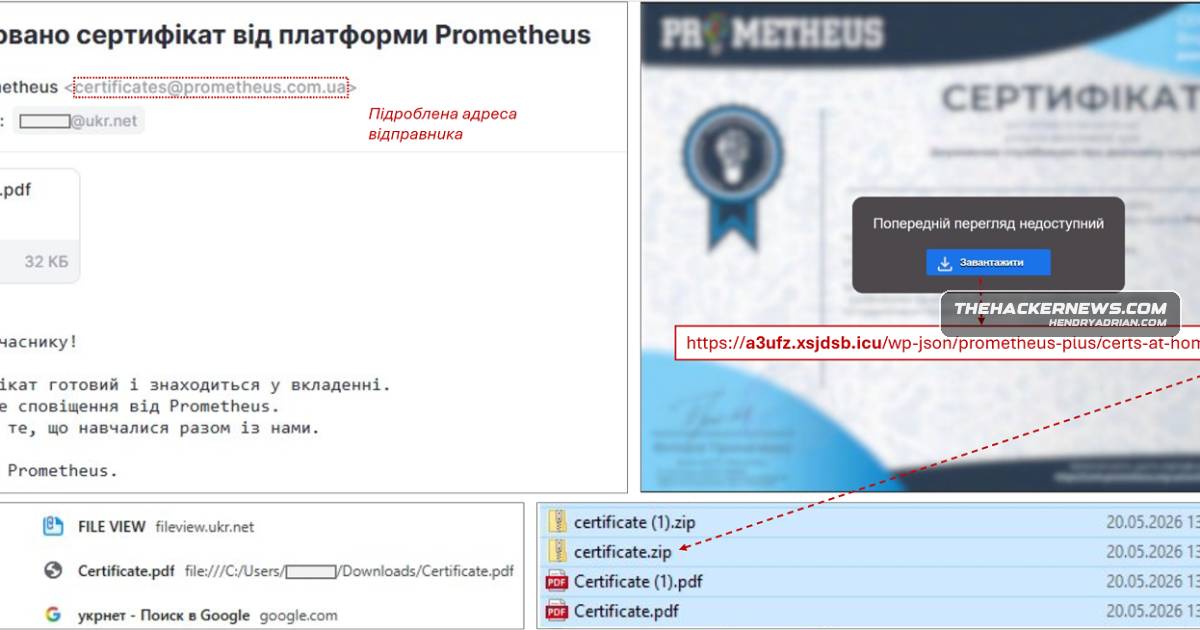
CERT-UA reports that Ghostwriter has targeted Ukrainian government organizations since spring 2026 with phishing that deploys OYSTER malware and a final payload assessed to be Cobalt Strike. It advises restricting wscript.exe for standard users.
Key points
- CERT-UA says Belarus-aligned Ghostwriter has targeted Ukrainian government organizations since spring 2026 using phishing emails sent from compromised accounts.
- Emails typically contain a PDF link that leads to a ZIP archive with a JavaScript file.
- OYSTERFRESH displays a decoy document, writes an encrypted OYSTERBLUES payload to the Windows Registry, and downloads OYSTERSHUCK to decode it.
- OYSTERBLUES collects system details and running processes, sends them to a C2 server over HTTP POST, then executes returned JavaScript using eval().
- The final payload is assessed to be Cobalt Strike.
- CERT-UA recommends restricting standard users' ability to run wscript.exe.
Article Details
- Attack Vectors
- Phishing emails sent from compromised accounts to Ukrainian government organizations used Prometheus-themed lures and PDF attachments containing links to ZIP archives with JavaScript files.
- The JavaScript chain deployed OYSTERFRESH, which wrote an obfuscated and encrypted OYSTERBLUES payload to the Windows Registry and downloaded and launched OYSTERSHUCK to decode it.
- OYSTERBLUES collected system information, sent it to a command-and-control server over HTTP POST, and executed returned JavaScript using eval(). The final payload was assessed to be Cobalt Strike.
- Ukraine’s National Security and Defense Council reported that Russia used AI tools for target scouting and to generate malicious commands at runtime, and cited social engineering, vulnerability exploitation, compromised RDP and VPN accounts, supply-chain attacks, and unlicensed software containing backdoors as initial penetration vectors in 2025.
- A pro-Kremlin propaganda campaign linked to Matryoshka was attributed to Social Design Agency and involved hijacking Bluesky accounts to post fake content.
- Defensive Notes
- CERT-UA advised restricting the ability of standard user accounts to run wscript.exe.
MITRE ATT&CK
T1033 · System Owner/User DiscoveryOYSTERBLUES collected the user account on the infected system.T1057 · Process DiscoveryOYSTERBLUES collected a list of running processes.T1059.007 · JavaScriptThe downloaded JavaScript file ran as OYSTERFRESH; OYSTERBLUES also executed returned JavaScript using eval().T1071.001 · Web ProtocolsOYSTERBLUES sent collected information to its C2 server using HTTP POST and awaited further responses.T1082 · System Information DiscoveryOYSTERBLUES collected the computer name and operating-system version.T1105 · Ingress Tool TransferThe infection chain downloaded a ZIP archive and OYSTERSHUCK, which was launched to decode OYSTERBLUES.T1112 · Modify RegistryOYSTERFRESH wrote the obfuscated and encrypted OYSTERBLUES payload to the Windows Registry.T1204.001 · Malicious LinkThe reported infection chain began when a recipient clicked a link in a PDF attachment to download a ZIP archive.T1566.001 · Spearphishing AttachmentGhostwriter's phishing emails to Ukrainian government organizations included PDF attachments containing links to ZIP archives.
Threat Actors
Social Design AgencyThe article says the pro-Kremlin campaign hijacking Bluesky accounts to post fake content was attributed to Social Design Agency.UNC1151CERT-UA reported that Ghostwriter targeted Ukrainian government organizations with phishing emails and a multi-stage malware chain. The article identifies UAC-0057 and UNC1151 as aliases for Ghostwriter.
Malware
OYSTERBLUESthat use Prometheus-themed lures, leading to a multi-stage infection chain that deploys OYSTERFRESH, OYSTERBLUES, and OYSTERSHUCK before loading Cobalt Strike.OYSTERFRESHemails that use Prometheus-themed lures, leading to a multi-stage infection chain that deploys OYSTERFRESH, OYSTERBLUES, and OYSTERSHUCK before loading Cobalt Strike.OYSTERSHUCKlures, leading to a multi-stage infection chain that deploys OYSTERFRESH, OYSTERBLUES, and OYSTERSHUCK before loading Cobalt Strike.
Products
Bluesky#GhostwriterMicrosoft Windowsmechanism, while stealthily writing an obfuscated and encrypted payload called OYSTERBLUES to the Windows Registry, as well as downloading and launching OYSTERSHUCK, which is responsible for decoding OYSTERBLUES.PrometheusGhostwriter is targeting Ukrainian government organizations with phishing emails that use Prometheus-themed lures, leading to a multi-stage infection chain that deploys OYSTERFRESH, OYSTERBLUES, and OYSTERSHUCK before
Tools
ChatGPTSecurity and Defense Council revealed Russia’s use of artificial intelligence (AI) tools like OpenAI ChatGPT and Google Gemini to scout targets and embed the technology into malware to generate maliciousCobalt Strikea multi-stage infection chain that deploys OYSTERFRESH, OYSTERBLUES, and OYSTERSHUCK before loading Cobalt Strike.Google GeminiDefense Council revealed Russia’s use of artificial intelligence (AI) tools like OpenAI ChatGPT and Google Gemini to scout targets and embed the technology into malware to generate malicious commands at runtime,
Countries
BelarusThe Belarus-aligned threat actor known as Ghostwriter (aka UAC-0057 and UNC1151Ukraine’s National Security and Defense Council) has been observed using lures related to Prometheus, a Ukrainian online learning platform,RussiaThe broader report also highlights Russia-linked use of AI tools for target scouting and malware generation, along with a pro-Kremlin propaganda campaign tied to Social Design Agency and Matryoshka.UkraineThe activity, per the Computer Emergency Response Team of Ukraine (CERT-UA), involves sending phishing emails to government entities using compromised accounts.