
Researchers Link Showboat Linux Malware to Middle East Telecom Campaign
Summary
Researchers link the Showboat Linux post-exploitation framework, used since at least mid-2022, to attacks on a Middle East telecom provider and other possible victims. It supports remote shell, file transfer and SOCKS5 proxy functions.
Key points
- Showboat is a modular Linux post-exploitation framework with remote shell, file transfer and SOCKS5 proxy capabilities.
- Researchers say it has been used since at least mid-2022 against a Middle East telecommunications provider; the initial access method is unknown.
- Showboat sends system information to command-and-control servers in an encrypted, Base64-encoded PNG field and can manage C2 servers.
- The malware retrieves a Pastebin-hosted code snippet to conceal itself and can use SOCKS5 to reach devices accessible only over a local network.
- Researchers linked the activity to China-aligned threat clusters, including Calypso, based on infrastructure and other correlations; the attribution is an assessment.
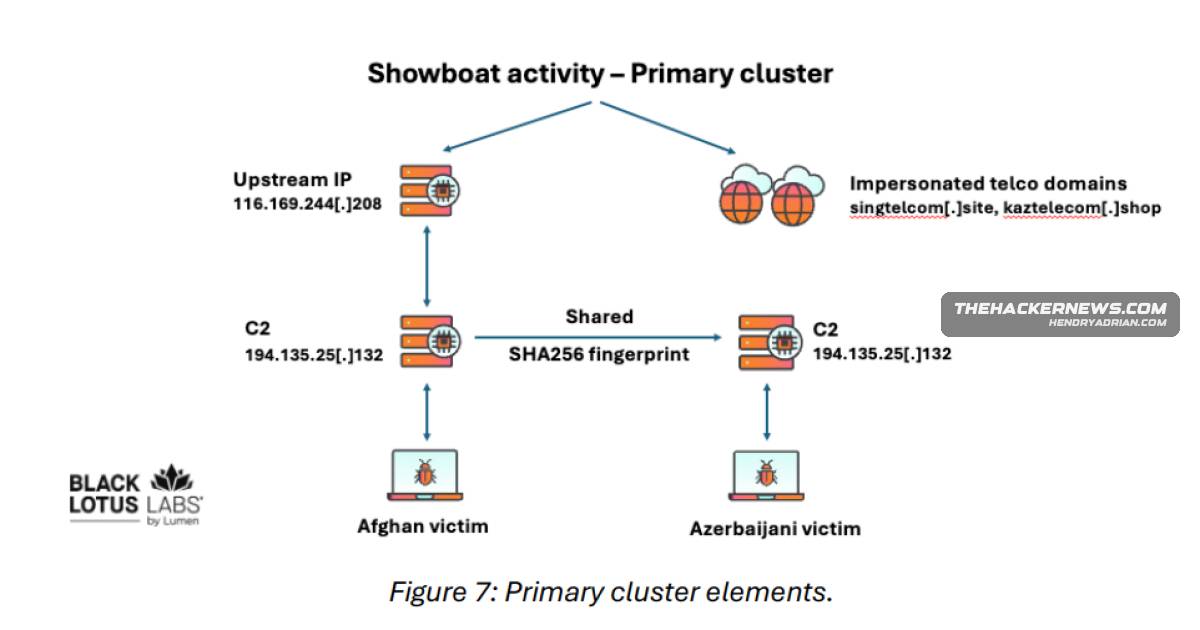
- Infrastructure analysis identified an Afghanistan-based ISP and an entity in Azerbaijan, plus possible compromises in the U.S. and Ukraine.
- Calypso also used the Windows implant JFMBackdoor, delivered through DLL side-loading; its capabilities include remote shell, file operations and network proxying.
Article Details
- Attack Vectors
- The initial access vector for Showboat delivery is unknown, according to Black Lotus Labs researcher Danny Adamitis.
- Calypso has previously been observed using an ASPX web shell after exploiting a flaw or accessing a default remote-access account.
- In the reported Afghanistan telecommunications campaign, JFMBackdoor was delivered through DLL side-loading: a batch script launched a legitimate executable that loaded a rogue DLL.
- Defensive Notes
- Black Lotus Labs described the presence of such threats as an early warning sign of potential broader and more serious security issues within affected networks.
MITRE ATT&CK
T1018 · Remote System DiscoveryShowboat can scan for other devices and connect to them through its SOCKS5 proxy.T1041 · Exfiltration Over C2 ChannelShowboat transmits gathered system information to its C2 server in an encrypted, Base64-encoded string in a PNG field.T1059.003 · Windows Command ShellA batch script launched a legitimate executable in the JFMBackdoor DLL side-loading chain.T1059.004 · Unix ShellShowboat supports spawning a remote shell on Linux systems.T1082 · System Information DiscoveryShowboat gathers system information and sends it to its C2 server.T1090 · ProxyShowboat provides SOCKS5 proxy functionality, including access to other devices on a LAN.T1105 · Ingress Tool TransferShowboat supports uploading and downloading files to and from the compromised host.T1573 · Encrypted ChannelShowboat uses encrypted communication with its C2 server.T1574.002 · DLL Side-LoadingJFMBackdoor was delivered by DLL side-loading, with a legitimate executable loading a rogue DLL.
CVE
People
Threat Actors
CalypsoThe article identifies Calypso as one threat actor linked to Showboat-related activity and reports that it used JFMBackdoor in the campaign targeting an Afghanistan telecommunications provider. The article says Calypso has previously been observed exploiting CVE-2021-26855.SixLittleMonkeysThe article says use of Mikroceen was attributed to SixLittleMonkeys, which it describes as sharing tactical overlaps with Webworm.WebwormThe article describes Webworm as a China-linked group with tactical overlaps with SixLittleMonkeys.
Malware
BYEBYSome of the key tools in its arsenal include PlugX and backdoors like WhiteBird and BYEBY, the latter of which is part of a broader cluster tracked by ESET under the moniker Mikroceen.EvaRATKaspersky is tracking the artifact as EvaRAT.JFMBackdoor#ShowboatNetDraft (NosyDoor)#ShowboatPlugX#ShowboatShadowPad#ShowboatShowboatResearchers uncovered Showboat, a modular Linux post-exploitation framework used since at least mid-2022 in attacks against a telecommunications provider in the Middle East and related victims in Afghanistan,WhiteBirdSome of the key tools in its arsenal include PlugX and backdoors like WhiteBird and BYEBY, the latter of which is part of a broader cluster tracked by ESET under the moniker Mikroceen.
Vendors
Products
Countries
Afghanistanmid-2022 in attacks against a telecommunications provider in the Middle East and related victims in Afghanistan, Azerbaijan, the U.S., and Ukraine.Azerbaijanin attacks against a telecommunications provider in the Middle East and related victims in Afghanistan, Azerbaijan, the U.S., and Ukraine.ChinaThe activity is linked to China-aligned clusters such as Calypso, alongside shared tooling and infrastructure that suggest a broader resource-pooling ecosystem.Ukraineprovider in the Middle East and related victims in Afghanistan, Azerbaijan, the U.S., and Ukraine.United Statesa telecommunications provider in the Middle East and related victims in Afghanistan, Azerbaijan, the U.S., and Ukraine.