
Google Details Chinese-Language Phishing Services Using OTP Interception and Wallet Fraud
Summary
Google GTIG analyzed a mature Chinese-language PhaaS ecosystem using RCS and iMessage delivery, live OTP interception and digital-wallet provisioning to monetize stolen payment data. Darcula and YY Lai Yu illustrate AI-assisted, localized operations, including Japan.
Key points
- GTIG analyzed a dozen current Chinese-language PhaaS offerings, describing a mature ecosystem that targets the public and victims outside China.
- Operators use RCS and iMessage to deliver phishing links; end-to-end encryption can make server-side filtering more difficult.
- Live administration panels display credentials as victims enter them. Operators can trigger matching OTP requests and capture the codes in real time to bypass MFA.
- The services use stolen payment details and OTPs to provision cards in attacker-controlled digital wallets, enabling transactions and ATM withdrawals.
- GTIG links Darcula to UNC5814 and describes its use of AI-powered page generation and browser automation to create unique phishing pages.
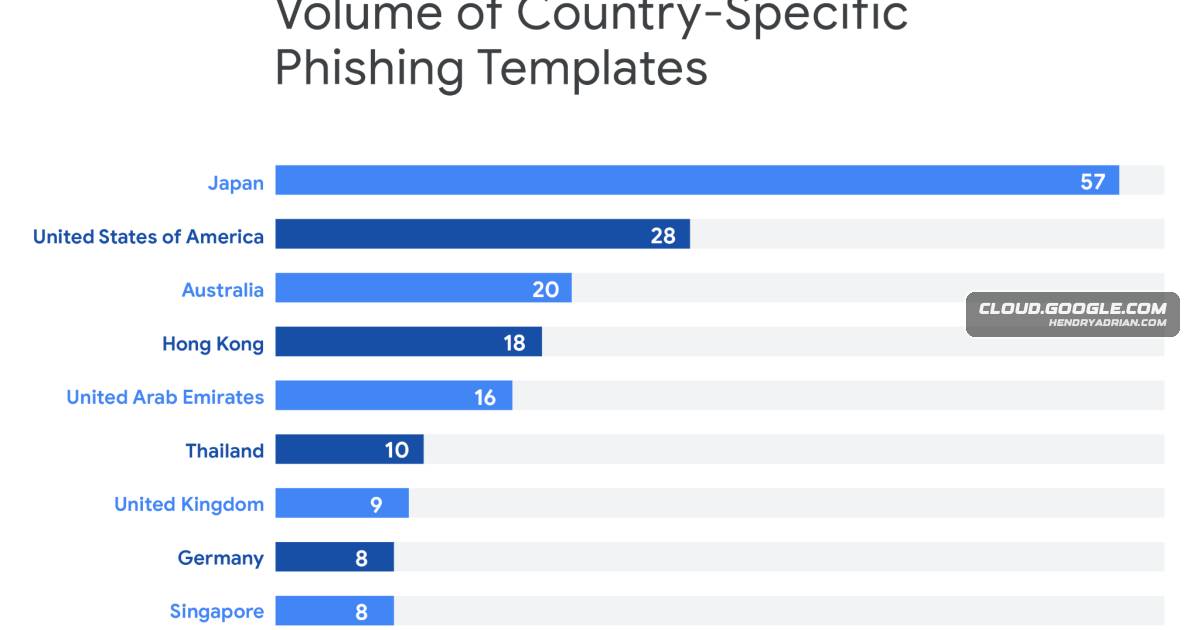
- YY Lai Yu supports phishing across 119 countries; GTIG reports more than 400 templates since November 2025, with a strong focus on Japan and anti-bot checks.
- GTIG recommends FIDO2/WebAuthn, risk-based verification and device fingerprinting during digital-wallet provisioning as defenses.
Article Details
- Attack Vectors
- Phishing links are delivered through RCS and iMessage messages, often using localized lures that impersonate organizations and services.
- Phishing pages capture credentials and OTPs in real time; operators use the captured OTPs to attempt to bypass MFA.
- Captured payment details and OTPs are used to provision victims' cards into digital wallets on attacker-controlled devices for unauthorized transactions and ATM withdrawals.
- YY Lai Yu phishing pages use a human-verification screen requiring a manual click to hinder automated analysis.
- Darcula uses AI-powered page generation and browser automation to create unique, localized phishing pages.
- Defensive Notes
- The article recommends FIDO2/WebAuthn to reduce the effectiveness of real-time OTP interception.
- Pair authentication upgrades with risk-based verification and device fingerprinting during digital-wallet provisioning.
- User awareness training remains useful, but the article emphasizes technical controls beyond user education.
- On-device protections are important because end-to-end encrypted messaging can make malicious links harder to inspect or filter server-side.
MITRE ATT&CK
T1056.003 · Web Portal CapturePhishing pages capture credentials and OTPs and display entered data in an administrative panel.T1111 · Multi-Factor Authentication InterceptionOperators trigger an OTP request and capture the code entered by the victim in real time to bypass MFA.T1204.001 · Malicious LinkThe described attack begins when a victim clicks a malicious link in a message.T1566.002 · Spearphishing LinkOperators send phishing links through RCS and iMessage to direct victims to credential- and OTP-collection pages.T1583.001 · DomainsYY Lai Yu users can register and manage domains for phishing pages through the administration panel.T1657 · Financial TheftOperators use stolen payment details to provision cards into attacker-controlled digital wallets for transactions and ATM withdrawals.
Threat Actors
Vendors
Products
iMessageIntelligence Group analyzed a growing Chinese-language phishing-as-a-service ecosystem that uses RCS and iMessage, real-time OTP interception, and digital wallet tokenization to bypass MFA and monetize stolen paymentRCSThreat Intelligence Group analyzed a growing Chinese-language phishing-as-a-service ecosystem that uses RCS and iMessage, real-time OTP interception, and digital wallet tokenization to bypass MFA and monetize stolenTelegram[Messaging Platforms ] delivery and coordination channels – RCS, iMessage, Telegram
Tools
Countries
ChinaNearly all the legitimate organizations mimicked by these phishing services are non-Chinese entities, suggesting they rarely target China.JapanThe report highlights mature services such as Darcula and YY Lai Yu, extensive localization for global targets like Japan, and the use of AI automation to generate unique phishing pages and evade detection.