cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2477 articles

Threat Research · thehackernews.com

Kimsuky Uses Fake Security and Webex Lures to Deploy HTTPSpy

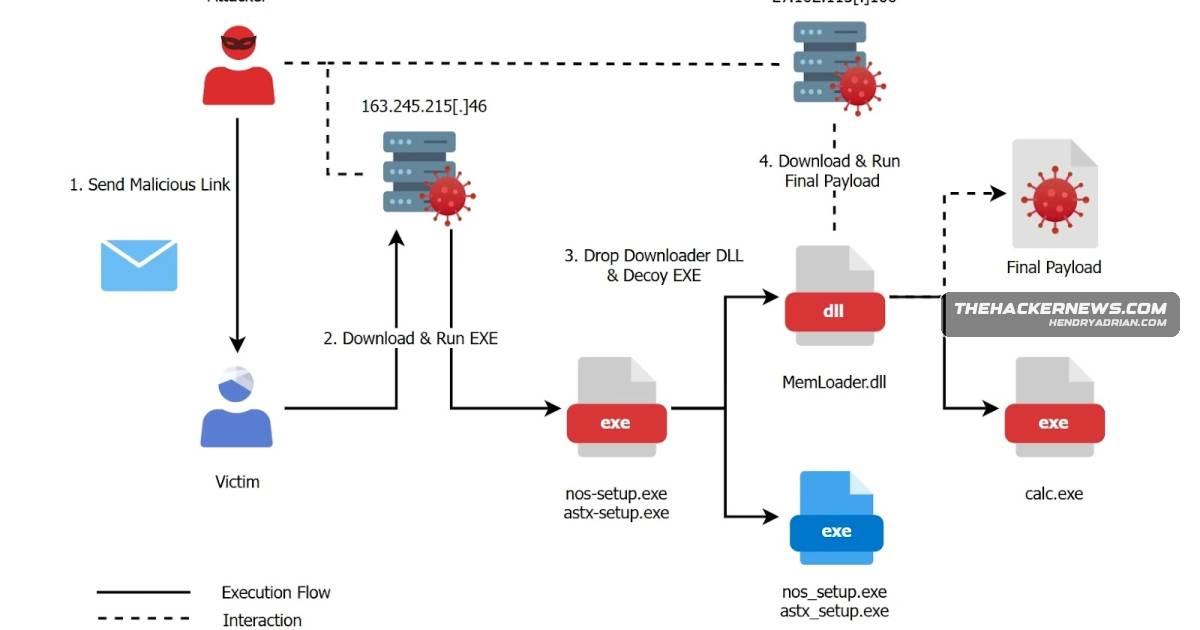
ENKI described Kimsuky campaigns targeting South Korean organizations with fake security-software and Webex lures that delivered HTTPSpy and other payloads. Kaspersky also reported expanded use of malware, remote-access tools and VS Code tunneling.

May 29, 2026
Threat Research · circleid.com

DNS Analysis Maps Infrastructure Linked to Axios Supply-Chain Attack

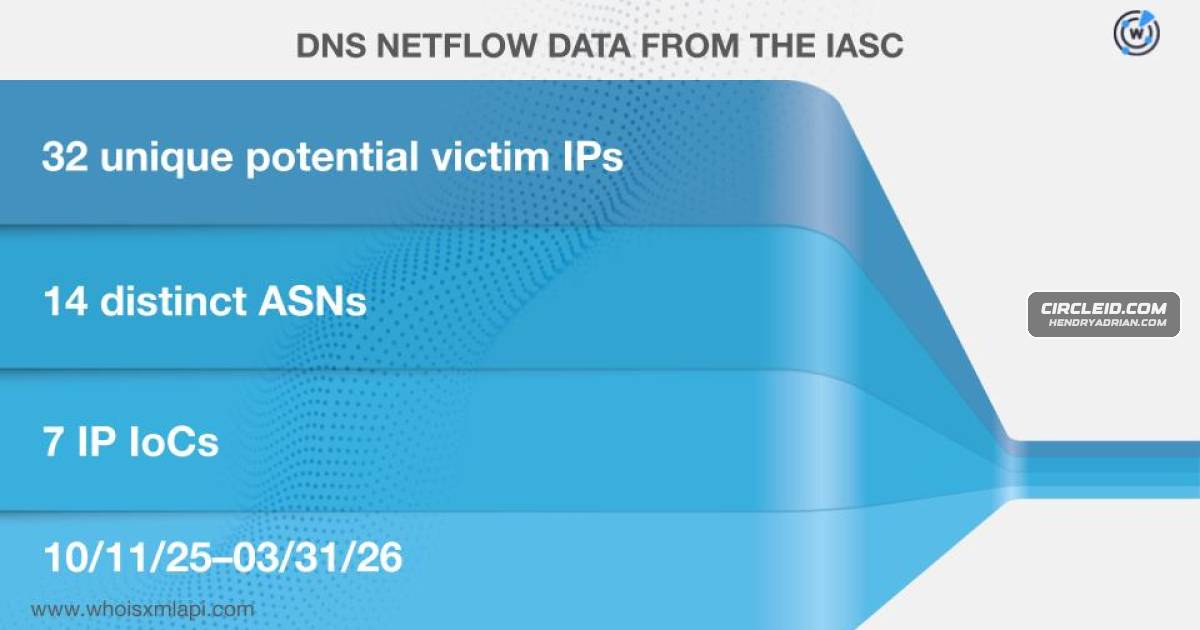
An analysis of the March 31, 2026 Axios npm supply-chain attack combined 22 IoCs from GTIG, Elastic Security Labs and GitHub, using DNS, WHOIS and related data to map suspected phishing infrastructure and connected artifacts.

May 29, 2026
Threat Research · cyberscoop.com

Researchers Say Chained Zapier Flaws Could Enable Account Takeover

Token Security researchers chained five Zapier flaws, using a free account to reach credentials, private software images and browser code, potentially enabling actions across users’ connected services. Zapier patched the flaws and reports no evidence of exploitation.

May 28, 2026
Threat Research · socket.dev

Malicious Sicoob NuGet SDK Exfiltrated Banking Credentials and Certificates

Socket analyzed Sicoob.Sdk versions 2.0.0–2.0.4, which sent client IDs, PFX passwords, and encoded certificates to a hardcoded Sentry endpoint. NuGet blocked the package after a report.

May 28, 2026
Threat Research · sysdig.com

Sysdig Traces LLM-Driven Intrusion from marimo CVE to PostgreSQL Exfiltration

Sysdig TRT reports an intrusion that began with CVE-2026-39987 in an internet-facing marimo notebook and reached an internal PostgreSQL database. It presents command-stream evidence for real-time LLM-agent execution and recommends patching and rotating exposed secrets.

May 28, 2026
Threat Research · levelblue.com

LevelBlue Details Sapphire Sleet macOS Campaign Using Fake Zoom SDK Update

LevelBlue describes a Sapphire Sleet campaign targeting macOS users in financial, Web3, and cryptocurrency sectors. A fake Zoom SDK update delivered AppleScript payloads that abused TCC permissions, established persistence, and collected credentials and sensitive data.

May 28, 2026
Threat Research · labs.k7computing.com

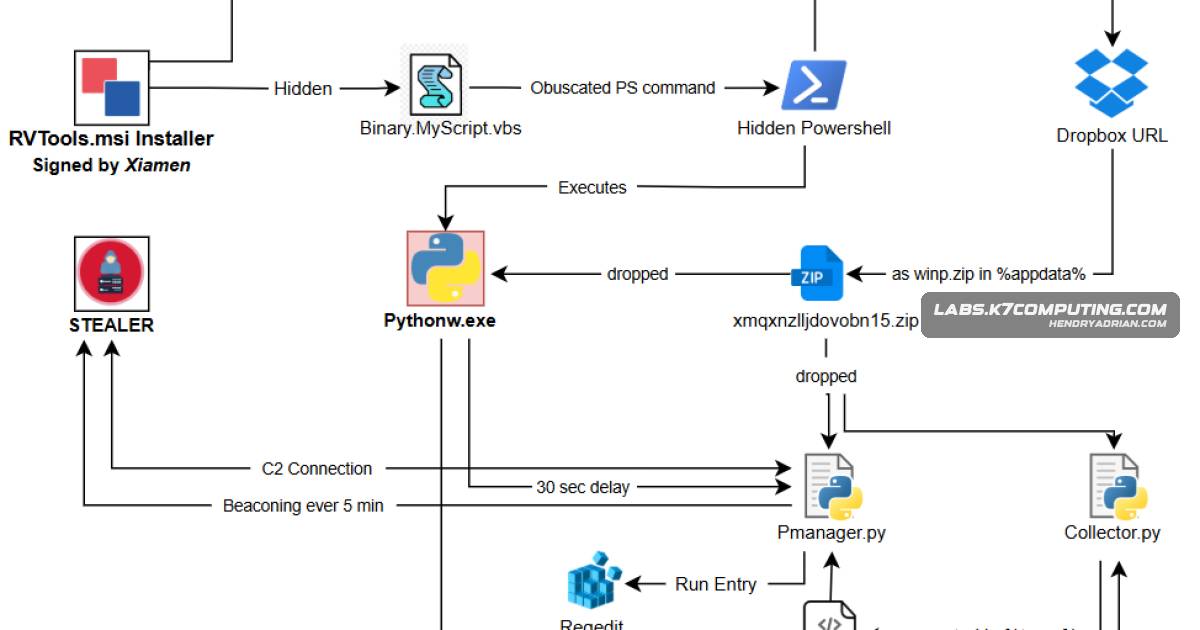
Fake RVTools Installer Deploys Modular Python RAT

A malicious MSI impersonating RVTools, signed with a subsequently revoked Sectigo certificate, uses embedded VBScript and hidden PowerShell to download a WinPython bundle and deploy a modular Python RAT with AD reconnaissance, persistence and encrypted C2.

May 28, 2026
Threat Research · securelist.com

Pirated Content Sites Distribute SilentCryptoMiner Fork and RAT

Researchers detail a campaign active since at least 2022 that uses fake player updates on pirated streaming and library sites to install a SilentCryptoMiner fork and RAT, with DNS-based system checks, persistence, defense evasion and rotating C2.

May 28, 2026
Threat Research · isc.sans.edu

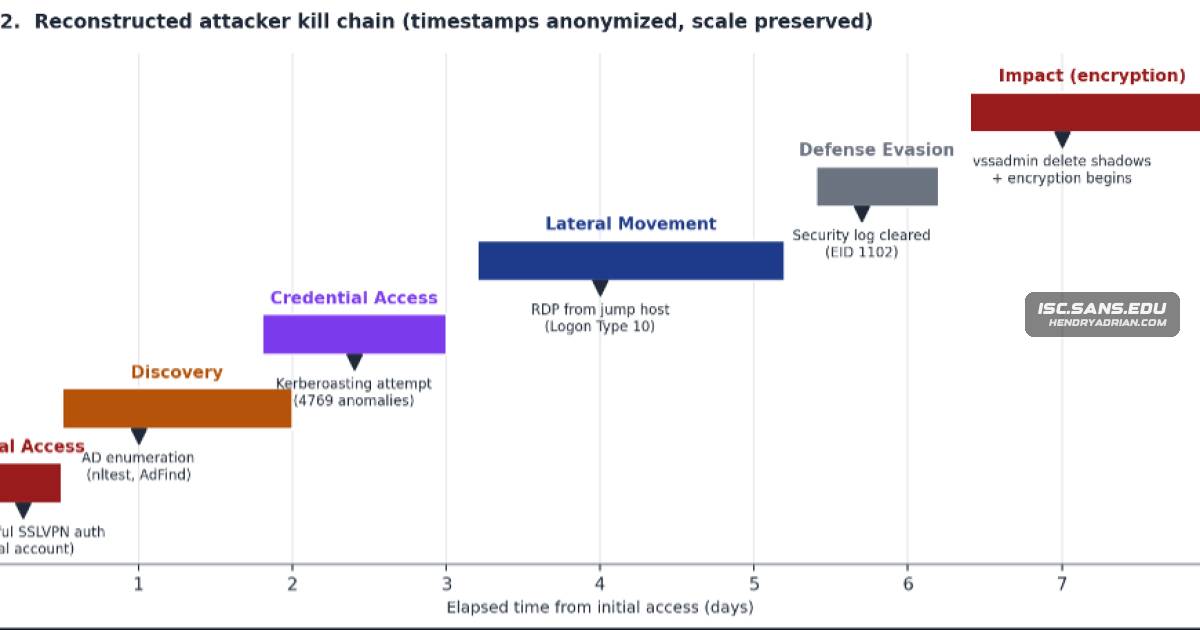
Reconstructing an Akira-Attributed Ransomware Kill Chain from Firewall and Windows Logs

A log-based reconstruction of an Akira-attributed intrusion traced SSLVPN brute force, Kerberoasting, RDP movement and pre-encryption actions. Joining firewall and Windows logs exposed the sequence and informed practical detection and retention guidance.

May 28, 2026
Threat Research · cyble.com

OverlayPhantom Android Trojan Uses Accessibility Abuse to Steal Banking Credentials

Cyble researchers detail OverlayPhantom, an Android banking trojan distributed through app-impersonating URLs. It abuses Accessibility Service, targets more than 180 financial apps in 10 countries, steals credentials through overlays and streams screens to operators.

May 28, 2026
Threat Research · esentire.com

Teams Vishing Campaign Deploys Nimbus RAT Using Quick Assist and Google Drive

eSentire investigated a Teams-vishing intrusion that used inbox flooding and Quick Assist to deploy Nimbus RAT. The Java malware uses Google Drive for C2 and can steal credentials; telemetry showed 1,540 suspicious Teams events across 172 customer environments.

May 28, 2026
Threat Research · bleepingcomputer.com

SEO Poisoning Campaign Spreads GPU Miners, With Some Victims Routed by AI Chatbots

Microsoft researchers describe a campaign that uses SEO-poisoned utility downloads—and, in some reported cases, AI chatbot recommendations—to install ScreenConnect, evade detection, and deploy GPU miners on Windows systems.

May 27, 2026
Threat Research · asec.ahnlab.com

AhnLab Details LNK Campaign Disguised as Korean Credit Card Security Emails

AhnLab describes a malicious LNK campaign disguised as security emails from a Korean credit card company. Payload delivery varies with Windows Defender status; resulting malware can steal browser and mail data, log keystrokes, collect clipboard data, and enable remote C

May 27, 2026
Threat Research · wiz.io

JINX-0164 Targets Crypto Developers With macOS Malware and a Malicious npm Package

Wiz describes JINX-0164 campaigns targeting cryptocurrency developers with social engineering, macOS malware, credential theft and CI/CD compromise, including a trojanized npm package used to deliver a backdoor.

May 27, 2026
Threat Research · picussecurity.com

NightSpire Ransomware Uses Remote-Access Tools and Cloud Exfiltration in Double-Extortion Attacks

The article describes NightSpire’s use of remote-access tools, file discovery and archiving utilities, and MEGAsync for data theft before encryption. Its Go encryptor appends .nspire, while ransom notes also claim OneDrive files were encrypted.

May 27, 2026
Threat Research · feeds.fortinet.com

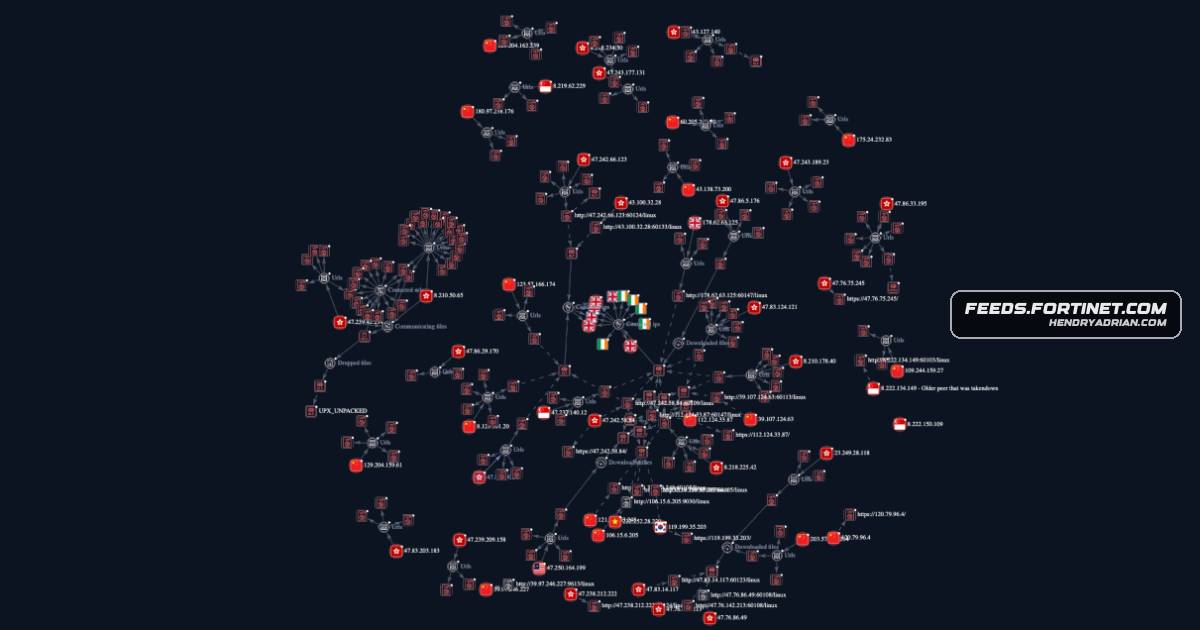
FortiGuard Finds Persistent P2Pinfect Infections in GKE and Links Peers to Metro4Shell

FortiGuard Labs reports persistent P2Pinfect infections in GKE clusters traced to exposed Redis. Telemetry links peers and binaries to Metro4Shell exploitation; RediShell use is a low-confidence possibility. No second-stage payload ran in observed cases.

May 27, 2026
Threat Research · hunt.io

Hunt.io Traces Smishing Campaign Targeting Services in 19 Countries

Hunt.io traced a multi-country smishing campaign using 1,628 URLs to impersonate government, postal, telecom, and other services. Fake payment pages harvest card details; shared page fingerprints link the infrastructure.

May 27, 2026
Threat Research · malwarebytes.com

Fake Software Installers Deliver DinDoor Backdoor and Deno-Based RAT

Malwarebytes describes fake software promoted through GitHub, SourceForge, and compromised YouTube channels. The campaign installs DinDoor and an unnamed Deno-based RAT that steals data and uses Edge for peer-to-peer streaming.

May 26, 2026
Threat Research · circleid.com

Hexastrike Attributes AtlasCross RAT Campaign to Silver Fox APT

Hexastrike attributes an AtlasCross RAT campaign using look-alike domains impersonating software brands to Silver Fox APT. Its infrastructure analysis identified 13 network IoCs and used DNS and WHOIS pivots to map potential victim connections and related domains.

May 26, 2026
Threat Research · thehackernews.com

MuddyWater Campaign Used DLL Side-Loading and ChromElevator to Steal Browser Data

Researchers linked MuddyWater to a Q1 2026 espionage campaign targeting at least nine organizations, using DLL side-loading, Node.js and PowerShell to steal browser data and credentials. Separate Iran-linked operations used FileFiend and other exfiltration methods.

May 26, 2026
Threat Research · darkatlas.io

Technical Analysis Details Payload Ransomware’s Encryption and Anti-Forensics

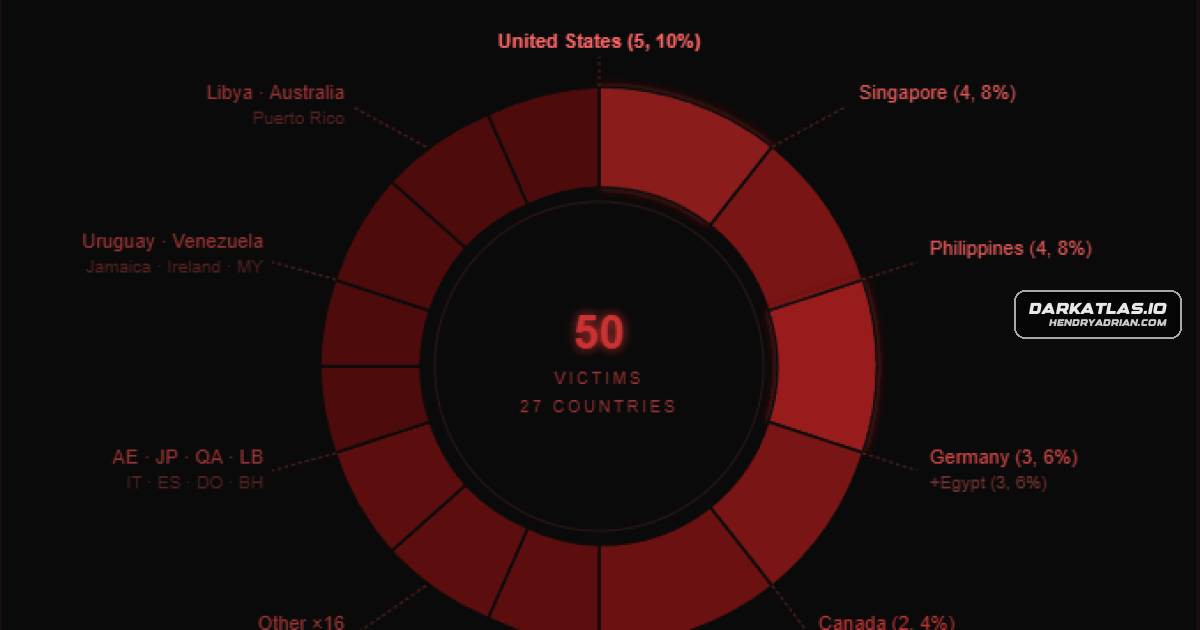
A technical analysis says Payload ransomware uses per-file Curve25519 ECDH-derived ChaCha20 encryption, an RC4-protected file footer, and ETW, VSS and event-log tampering. It reports 50 organizations listed on the group’s leak site by March 24, 2026.

May 26, 2026
Threat Research · cloud.google.com

Mandiant Details KnowledgeDeliver Exploitation via Shared ASP.NET Machine Keys

Mandiant linked a KnowledgeDeliver compromise to shared ASP.NET machine keys enabling unauthenticated RCE. The actor deployed BLUEBEAM and tampered with JavaScript to deliver Cobalt Strike BEACON; the report provides hunting and mitigation guidance.

May 26, 2026
Threat Research · trendmicro.com

ClearFake Uses BNB Smart Chain Testnet Contracts to Deliver SectopRAT and ACRStealer

Trend Micro analyzed a ClearFake campaign that used BNB Smart Chain testnet contracts to route ClickFix lures to Windows and macOS victims, delivering SectopRAT and ACRStealer and tracking successful executions on-chain.

May 26, 2026
Threat Research · thehackernews.com

Ghost CMS CVE-2026-26980 Exploited to Target 700+ Sites with ClickFix Attacks

QiAnXin XLab reports that attackers used Ghost CMS CVE-2026-26980 to steal admin API keys and inject ClickFix loaders across 700+ sites, delivering Windows malware. Ghost fixed the flaw in version 6.19.1.

May 25, 2026
PreviousPage 58 of 104 Next
© 2026 cyber.hendryadrian.com