cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · threatlabs.netskope.com

Fake AI and Developer Repositories Deliver Infostealer via SmartLoader

Netskope details a campaign using cloned AI and developer repositories to deliver infostealers through a two-stage SmartLoader chain, with C2 addresses resolved from the Polygon blockchain.
Aug 3, 2026
Threat Research · cloudsek.com

Exposed Directory Reveals Russian-Speaking Broker’s Intrusions and Ukraine-Focused Collection

CloudSEK says an exposed server documented a Russian-speaking access broker exploiting internet-facing systems, stealing credentials and compromising domains. The investigation also found collection targeting Ukrainian defence and aerospace organizations, alongside ties

Aug 3, 2026
Threat Research · securitylabs.datadoghq.com

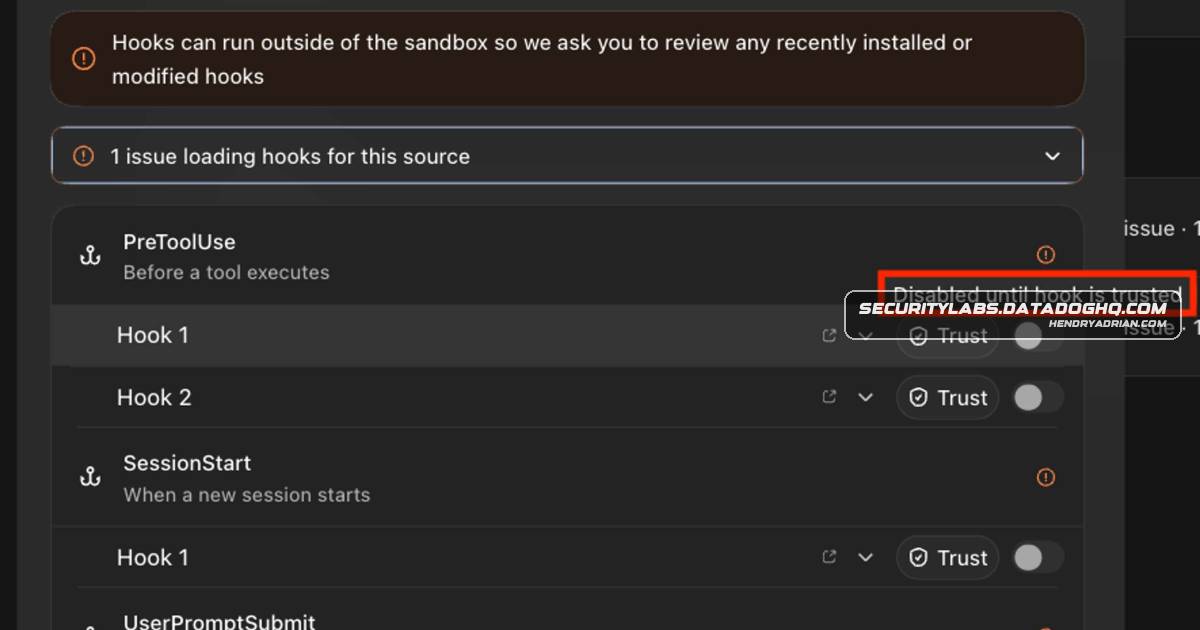
Datadog Finds Pre-Prompt Code Execution Paths in Trusted Coding-Agent Projects

Datadog describes how trusted repositories can run code before a coding agent's first prompt: Codex can start project-configured MCP processes, while Claude Code can run a repository-controlled Git wrapper through PATH settings.

Aug 3, 2026
Threat Research · zscaler.com

BINDCLOAK Backdoor Targets Middle East Government Entities

Zscaler analyzes BINDCLOAK, a modular Windows backdoor deployed in attacks targeting Middle East government entities. The report details its C2 protocol, commands, plugin loading, and links to the OctLurk backdoor.

Aug 3, 2026
Threat Research · asec.ahnlab.com

Larva-24009 Uses Phishing to Deploy PowerShell Backdoors and Steal Data

AhnLab reports that Larva-24009 continues phishing attacks in 2026, using malicious LNK files to deploy PowerShell backdoors, remote-control tools, and credential- and information-stealing tools.

Aug 2, 2026
Threat Research · opensourcemalware.com

DPRK-Linked npm Malware Hides C2 IP in Blank Ethereum Transfer Addresses

Researchers found two trojanized npm packages using a new blockchain-based C2 technique: decoding an IP address from the recipient address of a zero-value, zero-data Ethereum transfer.

Aug 2, 2026
Threat Research · thehackernews.com

Microsoft Details CaptiveCrunch Hotel Wi-Fi Malware and Token Theft

Microsoft says CaptiveCrunch hijacked hotel Wi-Fi captive portals to redirect users to fake updates delivering CornFlake RAT; related device-code phishing and ChocoShell token theft targeted Microsoft 365 and Azure AD. Successful compromise scale is unknown.

Aug 1, 2026
Threat Research · thehackernews.com

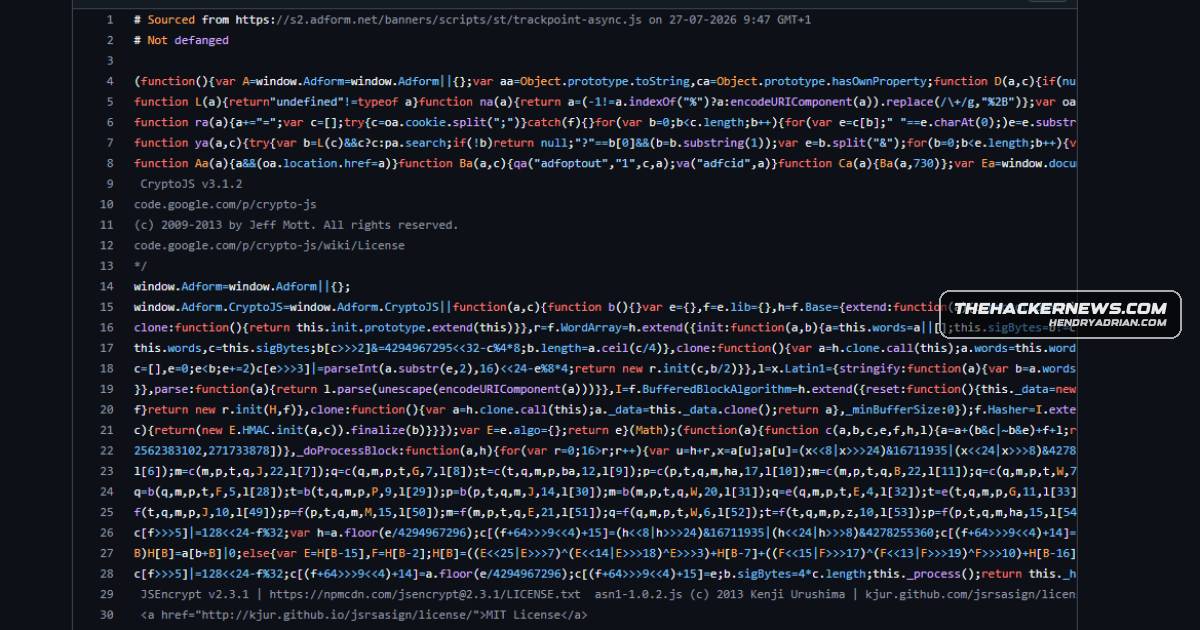
Compromised Adform Script Rewrote Crypto Wallet Addresses on Customer Sites

A compromised Adform script rewrote Bitcoin, Ethereum and Tron addresses on pages that loaded it. Adform removed the code July 27, 2026, but exposure scope and any diverted funds remain unknown; sample analysis details clipboard, form-field and page-data behaviors.

Aug 1, 2026
Threat Research · thehackernews.com

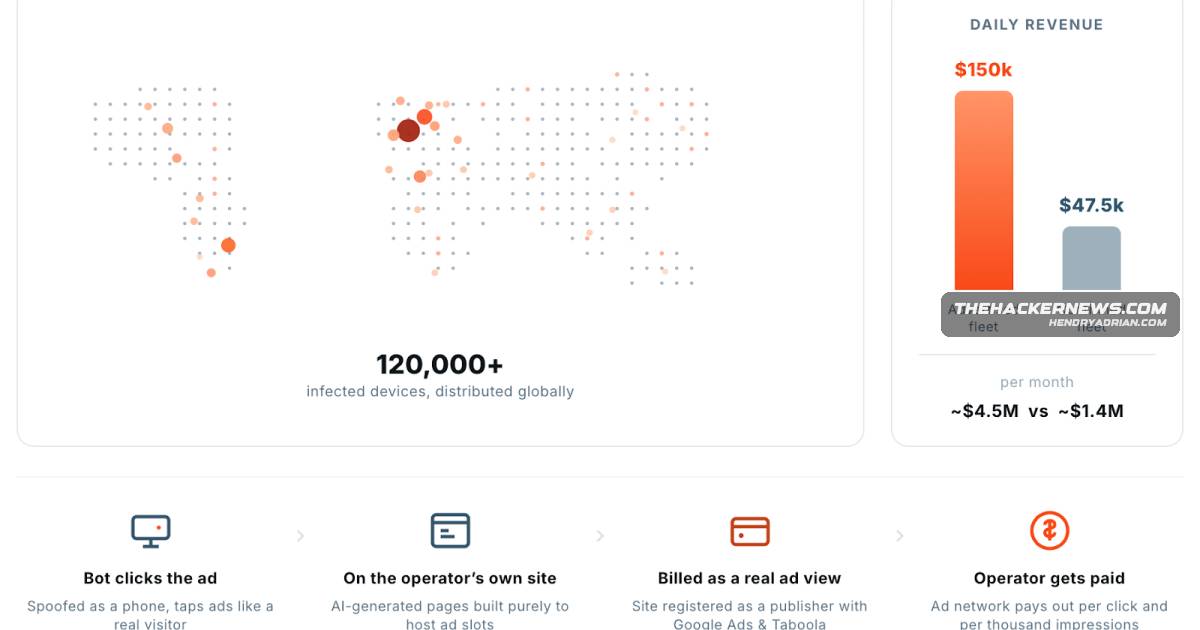
Bitsight Links Fuyao Android TV Boxes to Ad Fraud and SOCKS5 Proxying

Bitsight says Fuyao apps on some cheap Android TV boxes spoof phone identities for ad fraud and can relay traffic as SOCKS5 exit nodes. Its findings link the operation to Zhejiang Fengwo, but affected devices and the company's role remain incompletely established.

Aug 1, 2026
Threat Research · thehackernews.com

HollowFrame and Matryoshka Malware Target Law Firm in Multi-Stage Intrusion

Blackpoint Cyber describes HollowFrame and Matryoshka malware used in a spear-phishing intrusion targeting two endpoints at an unspecified law firm, detailing DLL side-loading, persistence, reconnaissance, and HTTP- and GitHub-based command-and-control.

Jul 31, 2026
Threat Research · thehackernews.com

OctLurk and SilkLurk Target Government Organizations Across Central Asia and Syria

Kaspersky reports a campaign targeting government-related organizations across Central Asia and Syria since January 2025. A Chinese-speaking actor is suspected but not linked to a known group; the activity uses OctLurk, SilkLurk, and LurkProxy.

Jul 31, 2026
Threat Research · unit42.paloaltonetworks.com

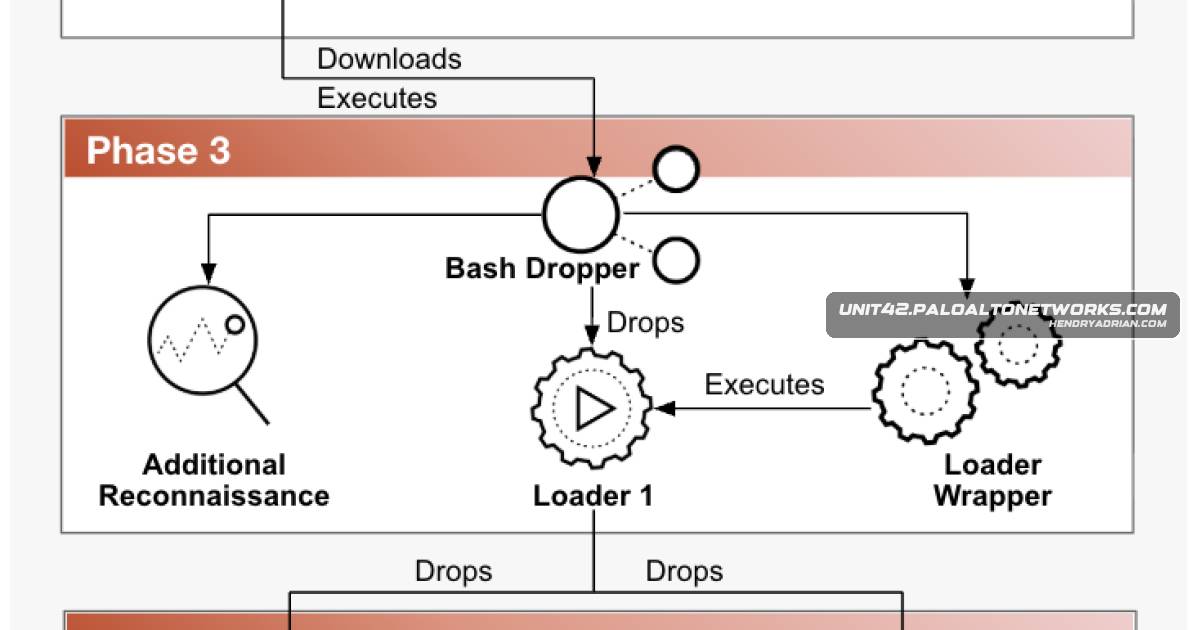
XCSSET v40 Uses Memory-Resident Execution to Hijack macOS Browsers and Trojanize Telegram

Unit 42 details XCSSET v40, macOS malware spread through poisoned Xcode projects, with memory-resident payloads, Chrome CDP hijacking, a Telegram trojanizer, and techniques to impair Apple security mechanisms.

Jul 31, 2026
Threat Research · circleid.com

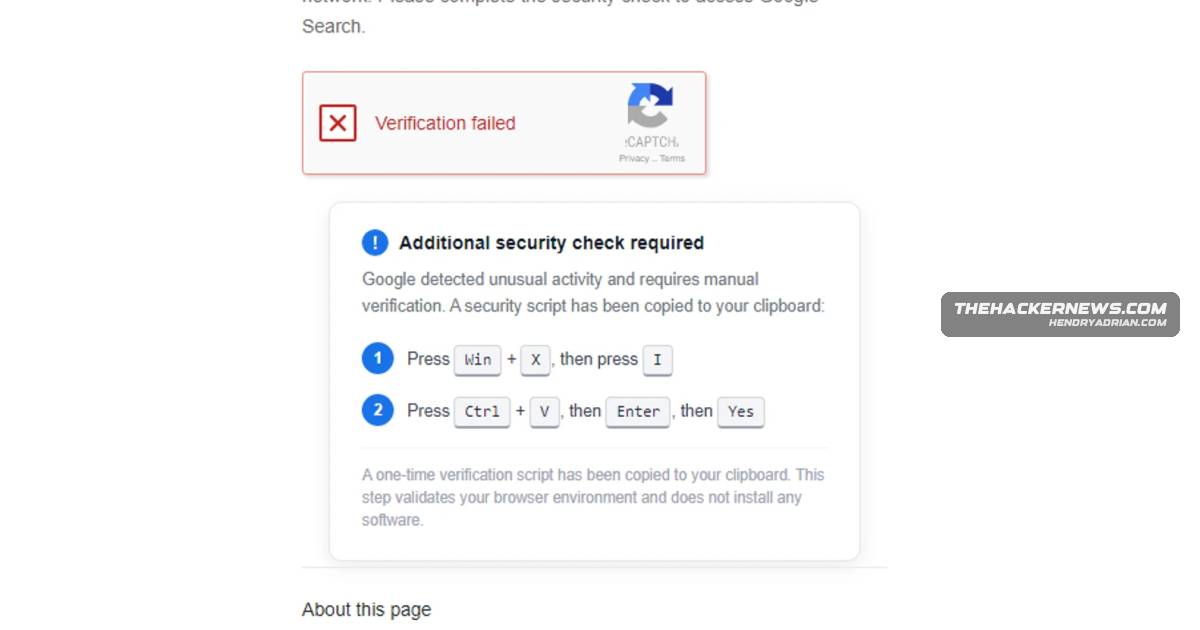
DNS Investigation Maps ErrTraffic ClickFix Infrastructure

DNS/WHOIS analysis of 71 ErrTraffic ClickFix domain indicators found 12 of 16 associated IPs flagged as malicious, 12 email-connected domains, and historical resolution data. Sekoia reported WordPress-focused clusters and fake AI lures; LenAI involvement was suspected.

Jul 31, 2026
Threat Research · thehackernews.com

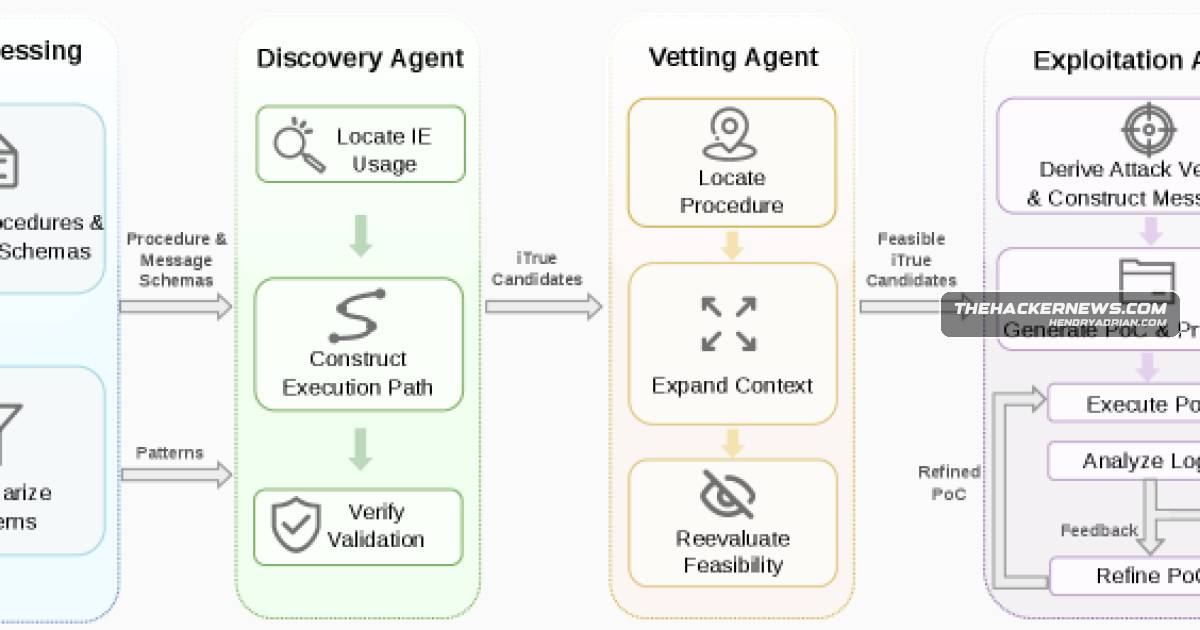
Researchers Find 84 Implicit Trust Flaws in 4G and 5G Core Networks

NTU researchers report 84 previously unknown flaws in seven LTE/5G core implementations, linked to implicit trust between components. Their iFinder system helped identify the issues, including a PFCP flaw that can redirect a victim’s traffic.

Jul 31, 2026
Threat Research · opensourcemalware.com

PolinRider Linked to 20 Compromised npm and Go Packages

An analysis links 20 compromised npm and Go packages to PolinRider, detailing how malware used developer access to spread payloads, steal credentials, and backdate commits. Malicious Go module versions remain available from the proxy cache.

Jul 31, 2026
Threat Research · aikido.dev

PyPI Package anthropickit Was Designed to Collect SSH Keys and Secrets; Anthropic Says It Was Not Its Agent’s Package

Aikido analyzed anthropickit, a PyPI package whose setup.py attempts to collect SSH keys and matching environment variables during installation. Its Pipedream endpoint was defunct; Anthropic later said it was not the package from its agent incident.

Jul 31, 2026
Threat Research · bleepingcomputer.com

Sophos Details STAC4749 Teams Vishing Campaign Linked to Chaos Ransomware

Sophos says STAC4749 targeted dozens of North American organizations through fake IT-support calls on Teams. Attackers used remote-access tools and backdoors; at least three intrusions led to Chaos ransomware, including one that reached encryption in under 17 hours.

Jul 30, 2026
Threat Research · securelist.com

OctLurk and SilkLurk Backdoors Target Central Asia and Syria in Espionage Campaign

Kaspersky researchers detail OctLurk and SilkLurk backdoors used against organizations in Central Asia and Syria since January 2025. Victim-specific loaders, in-memory plugins and related LurkProxy tooling support espionage and persistent access.

Jul 30, 2026
Threat Research · thehackernews.com

DPRK-Linked macOS Campaign Uses Fake Updates and EtherHiding to Target Crypto Wallets

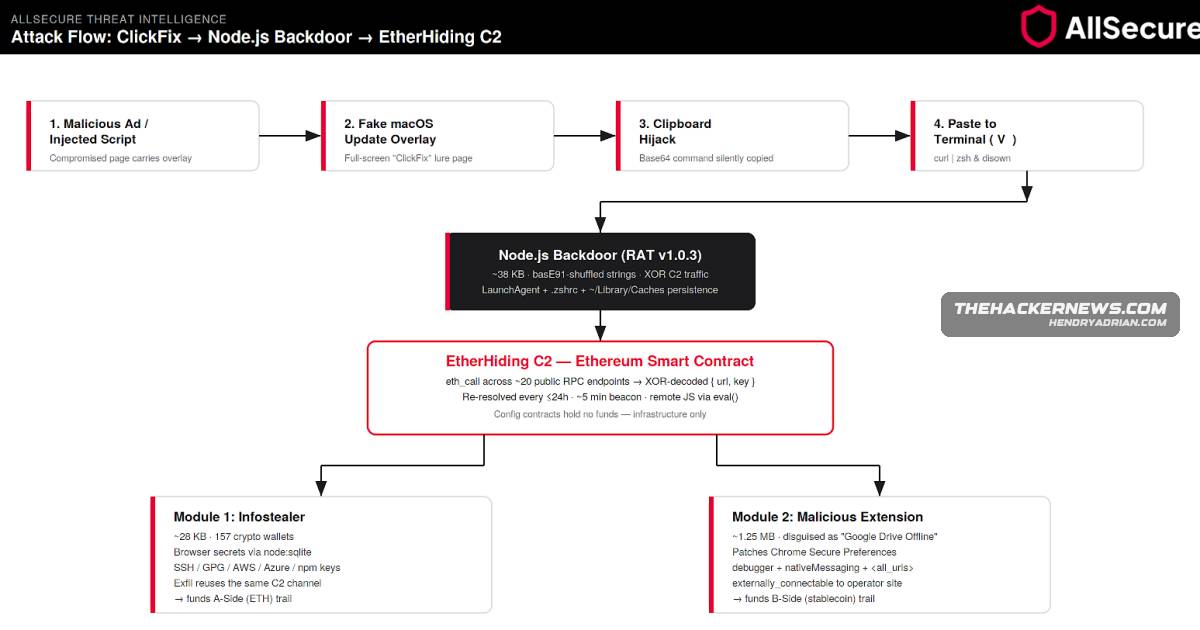
AllSecure reports a Contagious Interview campaign that uses fake macOS updates and clipboard abuse to install a Node.js backdoor, an information stealer targeting 157 crypto wallets, and a malicious Chrome extension.

Jul 30, 2026
Threat Research · bleepingcomputer.com

Huntress Details SQL Injection Attack and Attacker’s Post-Compromise Activity

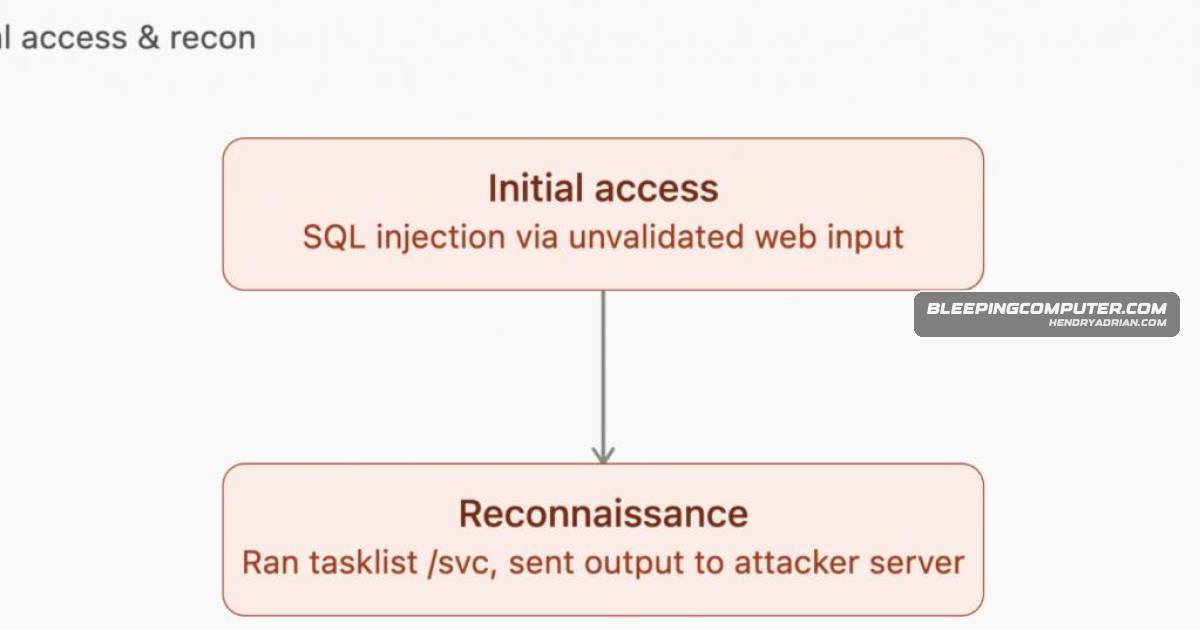
Huntress describes an attacker entering a Windows server through SQL injection, then enabling Remote Desktop, creating an admin account, disabling Defender, and installing BadIIS and XMRig. It urges fixing the entry point as well as removing payloads.

Jul 30, 2026
Threat Research · toxsec.com

LLM Routers Can Rewrite Tool Calls After Safety Checks, Enabling Code Execution

An LLM router that terminates TLS can read and rewrite tool-call responses before an agent receives them. The article says this can bypass model-side safeguards and enable code execution, while unsigned responses leave clients unable to verify changes.

Jul 30, 2026
Threat Research · wiz.io

CosmosEscape flaw could have exposed every Azure Cosmos DB account

Wiz researchers found that a Gremlin sandbox flaw in Azure Cosmos DB could enable code execution and cross-tenant access to databases. Microsoft says it fully remediated the issue and found no evidence of exploitation beyond the research.

Jul 30, 2026
Threat Research · darkowl.com

OSINT Investigation Traces Iranian-Linked Campaign of Assassination Bounties Targeting Trump

DarkOwl researchers trace a campaign of online assassination bounties targeting Donald Trump across Iranian-linked domains, social media, and state-aligned channels, including amplification by the Handala hacking group.

Jul 30, 2026
Threat Research · securelist.com

Kaspersky Details GenieLocker Ransomware Attributed to Toy Ghouls

Kaspersky analyzes GenieLocker, a custom ransomware family attributed to Toy Ghouls and active since March 2026 against Russian organizations. Attackers likely used stolen partner VPN credentials; Windows, Linux and ESXi variants encrypted systems, with no evidence of [

Jul 30, 2026
PreviousPage 38 of 100 Next
© 2026 cyber.hendryadrian.com