cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · bleepingcomputer.com

XCSSET v40 Spreads Through Compromised Xcode Projects, Adds Chrome and Telegram Modules

Unit 42 reports that XCSSET v40 infects developers who build compromised Xcode projects, then spreads through shared source code. New modules hijack Chrome and replace Telegram Desktop, while the malware adds evasion tactics and attempts to disable macOS protections.
Aug 4, 2026
Threat Research · netskope.com

Shai-Hulud npm Stealer Uses Ethereum Contract to Resolve C2

Netskope analyzed 28 malicious npm package versions across four namespaces. Their stealer downloads Bun, harvests developer and CI/CD credentials, and resolves its exfiltration host through an Ethereum smart contract.

Aug 4, 2026
Threat Research · bleepingcomputer.com

ChainDrop Worm Compromises Over 1,300 npm Packages, Targets Developer Credentials

ChainDrop spread through compromised npm packages after a maintainer’s GitHub account was breached. The worm uses GitHub Actions releases and Bun-based payloads to steal developer and cloud credentials and propagate to more packages.

Aug 4, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Finds 45% of C2 Malware Samples Connect Directly to IPs

Unit 42 analyzed more than 4 million dynamic reports and found 45.32% of malware samples with C2 activity made at least one direct-to-IP connection, exposing limits in DNS-based defenses. The research details Phorpiex, SectopRAT, Mozi and Boatnet activity and proposes Z

Aug 4, 2026
Threat Research · aquasec.com

Aqua Details Fileless Cryptomining Campaign Targeting Containerized Apps

Aqua describes a multistage XMRig cryptojacking campaign in containerized Node.js applications, including memory-based execution, persistence and mining traffic. The exact initial exploit was not determined, and Aqua found no evidence of access to customer secrets.

Aug 4, 2026
Threat Research · feeds.fortinet.com

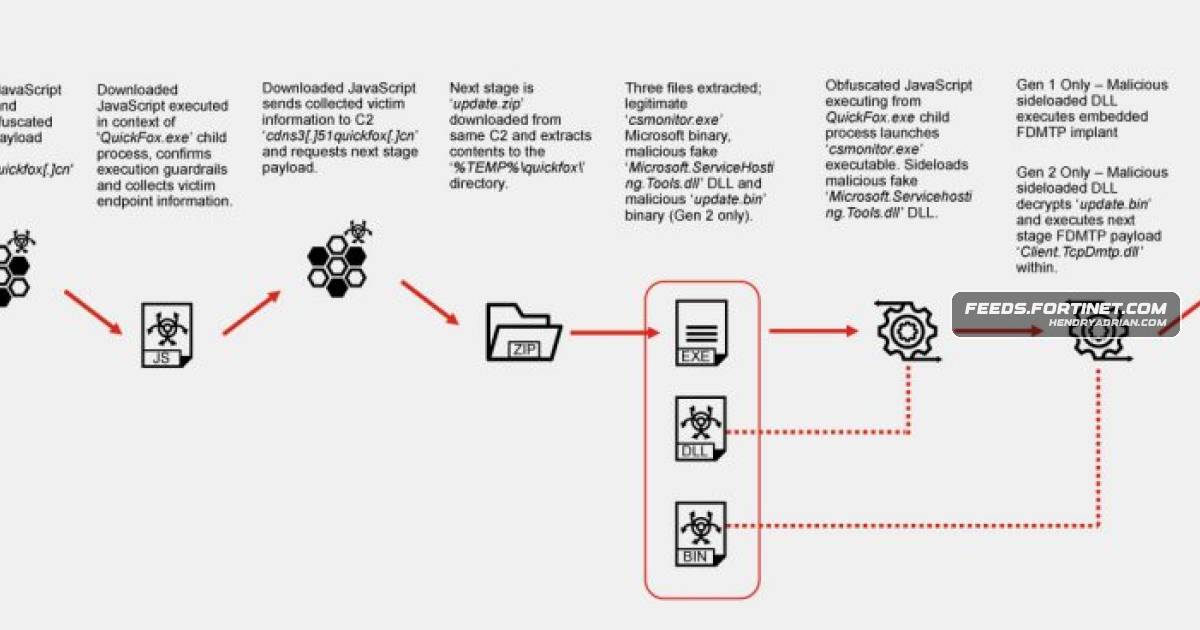
QuickFox Supply-Chain Attack Deployed FDMTP Implant on Windows Systems

FortiGuard Labs detailed a QuickFox supply-chain compromise that delivered an FDMTP implant to selected Windows users. QuickFox removed the malicious components from its Windows installer in version 3.59.6 after Fortinet's notification.

Aug 4, 2026
Threat Research · wiz.io

Wiz Details npm Supply-Chain Attack Spreading Malicious Packages to 400+ Packages

Wiz says attackers used a compromised maintainer account to publish malicious npm packages that spread to more than 400 packages. The malware steals credentials and secrets, establishes persistence, and retrieves C2 domains from an Ethereum contract.

Aug 4, 2026
Threat Research · socket.dev

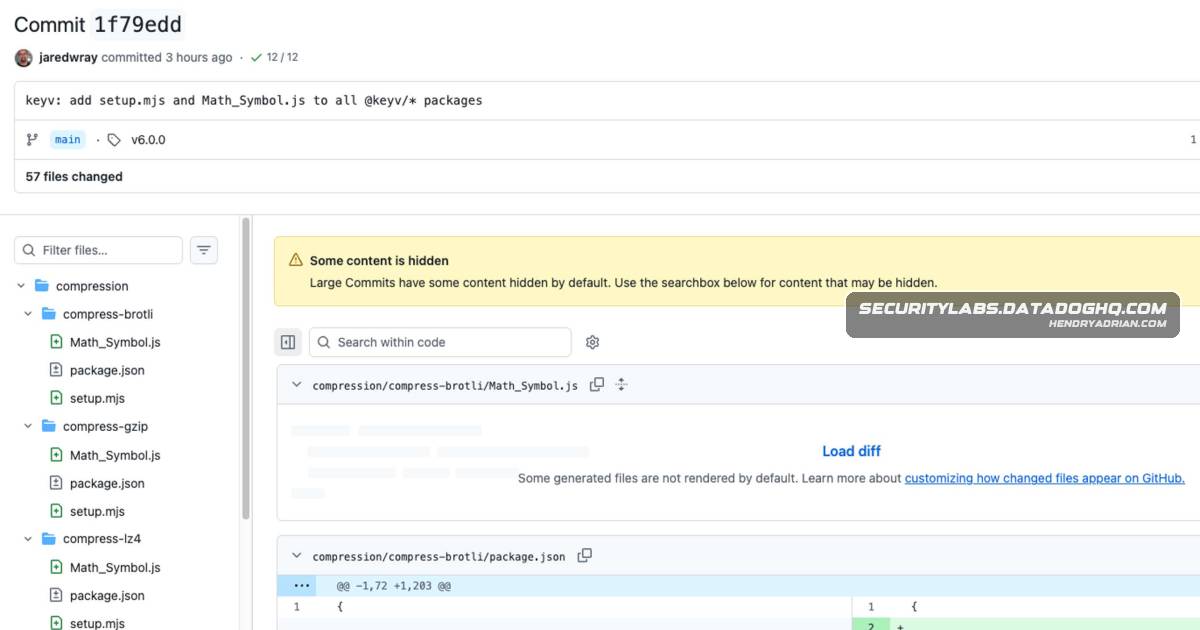
Active npm Supply-Chain Attack Compromises Keyv and Cacheable Packages

A malicious npm preinstall hook in Keyv, Cacheable, and other packages steals developer and CI credentials, spreads by republishing trojanized packages, and installs persistence. The investigation remains ongoing.

Aug 4, 2026
Threat Research · blog.talosintelligence.com

Talos Details How Adversaries Use AI to Build Malware, Scale Attacks and Steal Credentials

Talos analyzed AI-related artifacts from adversaries and found models helping with malicious software, fraud, credential theft and vulnerability research. Simple claims of authorization and task-splitting often bypassed safeguards.

Aug 4, 2026
Threat Research · netskope.com

Netskope Details SmartLoader Infostealer Campaign Using Fake AI Repositories

Netskope analyzed a campaign delivering infostealers through ClickFix and trojanized GitHub repositories impersonating AI and developer resources. Its two-stage SmartLoader chain uses EtherHiding on Polygon to resolve C2 at runtime.

Aug 4, 2026
Threat Research · bleepingcomputer.com

DOUBLECUP ClickFix Service Hides Malware in Browser Cache PNGs

SOCRadar says DOUBLECUP has been active since early June 2026, using fake CAPTCHA ClickFix pages and PNG steganography to deliver CountLoader on Windows and macOS and the DeviceManager RAT on Windows.

Aug 4, 2026
Threat Research · bleepingcomputer.com

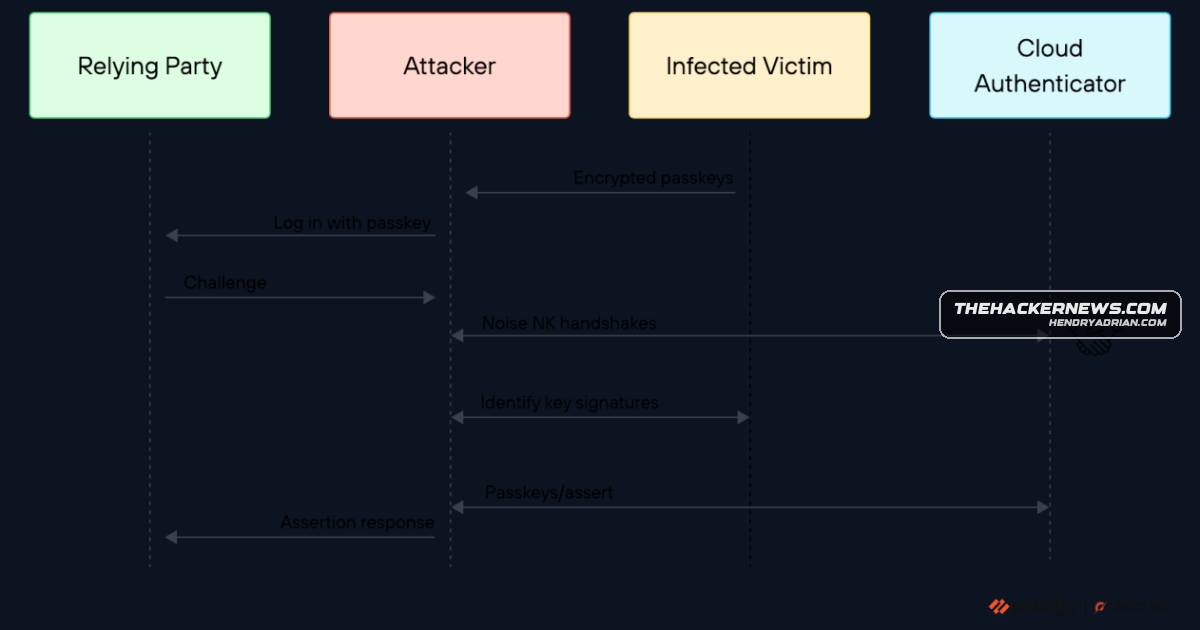
Unit 42 Details Three Pass-ta-key Attacks on Google-Synced Passkeys

Unit 42 says malware already running on Windows can abuse Google Password Manager’s synced passkeys through three Pass-ta-key attacks, bypassing user verification or extracting private keys. Google removed one log exposure, and eBay fixed a validation flaw.

Aug 4, 2026
Threat Research · aikido.dev

Shai-Hulud Worm Spreads Through Keyv and Hundreds of npm Packages

Aikido reports that a Shai-Hulud supply-chain worm compromised Keyv and related npm packages, using install scripts to steal credentials and spread through npm packages and GitHub repositories; at least 444 packages were affected.

Aug 4, 2026
Threat Research · jamf.com

How iOS Exploit Kits Fingerprint Devices Before Deploying Exploits

Analysis of Coruna and Predator shows how spyware checks device and browser signals to avoid unsuitable targets and research environments. Tests found that Coruna’s IndexedDB probe can indicate private browsing and its checks can detect Lockdown Mode.

Aug 4, 2026
Threat Research · threatlabs.netskope.com

Shai-Hulud npm Stealer Uses Ethereum Contract to Resolve Its C2

Netskope analyzed 28 malicious npm package versions across four namespaces. Their stealer collected developer and CI/CD credentials, then sent encrypted data to a C2 domain resolved at runtime through an Ethereum contract.

Aug 4, 2026
Threat Research · threatlabs.netskope.com

Fake CAPTCHA PDFs Funnel Search Traffic to Malware and Scams

Netskope traced more than 12,700 FakeCaptcha PDFs on Webflow’s CDN to an active traffic-distribution network that filters visitors and routes them to malware, ad landers, or a premium-SMS scam.

Aug 4, 2026
Threat Research · huntress.com

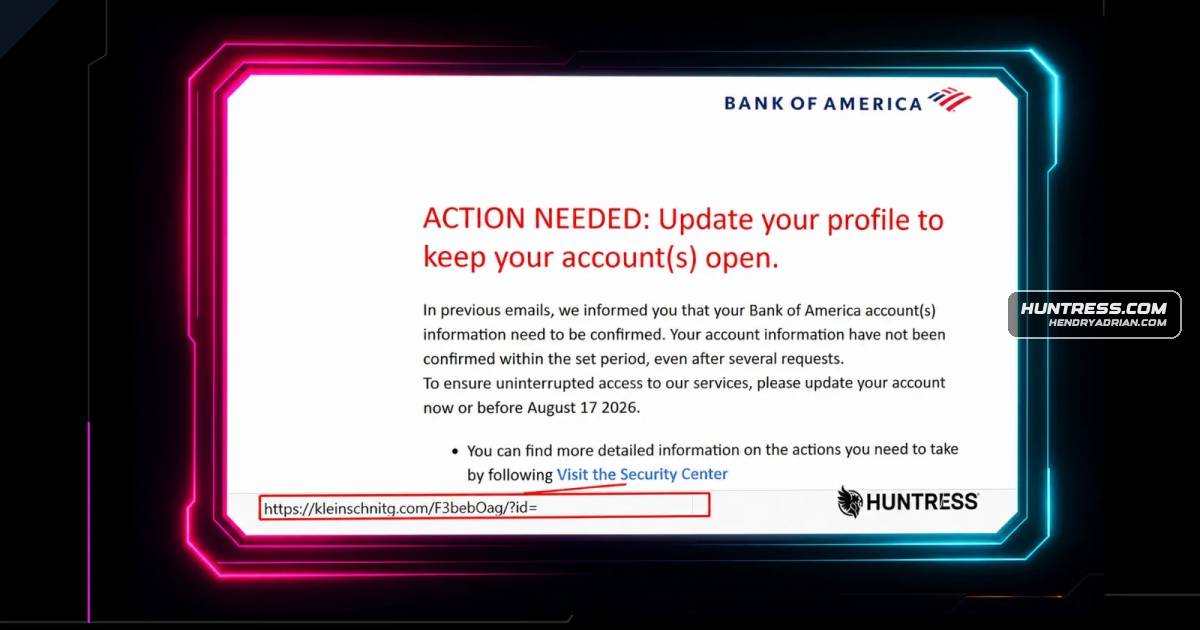
Phishing Campaign Uses Fake Bank of America Alert to Install Hidden ScreenConnect Client

A fake Bank of America alert leads Windows users to a multi-stage script chain that bypasses UAC, installs and hides ScreenConnect, and connects to attacker infrastructure. Mac users are directed to pages harvesting banking credentials and personal data.

Aug 4, 2026
Threat Research · securitylabs.datadoghq.com

ChainDrop Worm Compromises Hundreds of npm Packages to Steal Credentials and Spread

A worm dubbed ChainDrop compromised hundreds of npm packages, including widely used projects. Its payload can collect credentials and cloud secrets, exfiltrate data, and spread through npm packages and GitHub repositories.

Aug 4, 2026
Threat Research · hunt.io

The Gentlemen Affiliate Deploys EtherRAT Across Windows Networks Using Ethereum-Based C2

Hunt.io researchers analyzed files from an exposed directory, detailing a Windows intrusion attributed to The Gentlemen. The toolkit used EtherRAT, which retrieves rotating C2 domains from an Ethereum smart contract, alongside other tools for persistence and access.

Aug 4, 2026
Threat Research · thehackernews.com

Unit 42 Details Three Chrome Passkey Attack Paths Requiring Existing Windows Malware

Unit 42 describes three post-compromise attacks against Chrome’s Google Password Manager on Windows that could expose passkey accounts or keys. The article says they require existing malware and that current exploitability and remediation remain unclear.

Aug 3, 2026
Threat Research · thehackernews.com

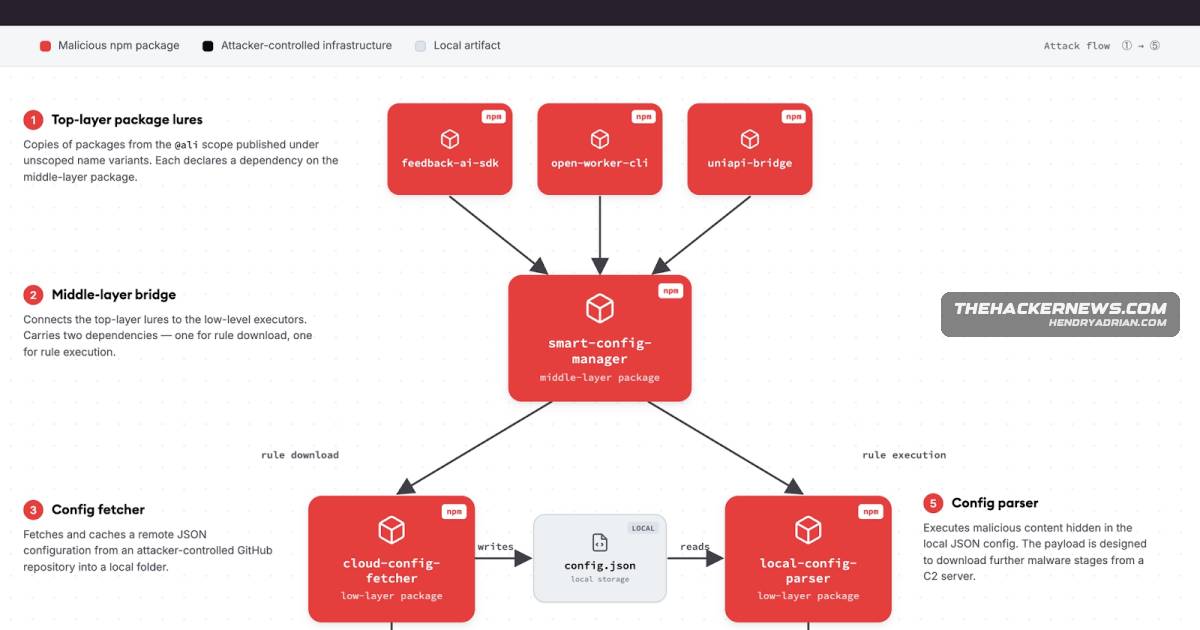
18 Malicious npm Packages Target Alibaba Tool Users With Cross-Platform RAT

Researchers describe malicious npm packages impersonating Alibaba private packages to deliver a cross-platform RAT to developers. The article also reports a poisoned mrmustard release capable of stealing developer and cloud credentials.

Aug 3, 2026
Threat Research · asec.ahnlab.com

ASEC Links Xctdoor Campaigns to Earlier CRAT Attacks in Korea

ASEC links Larva-26005’s current Xctdoor activity in Korea to earlier CRAT attacks, detailing delivery through disguised installers and LNK files, malware behavior, and suspected ties to North Korean actors.

Aug 3, 2026
Threat Research · bitdefender.com

Fake Roblox Xeno Cheats Deliver Java Stealer Through Discord and Forums

Bitdefender researchers detail a multi-stage Java malware campaign spread as fake Xeno Roblox cheats. The final payload steals accounts and financial data, spies on victims, and enables remote control of infected Windows systems.

Aug 3, 2026
Threat Research · labs.k7computing.com

Octagon Android Malware Uses Fake Bahrain Alert App to Capture Lock-Screen Credentials

K7 researchers analyzed Octagon, an Android threat impersonating Bahrain’s BH Alert app. It decrypts and dynamically loads payloads, abuses VPN and Accessibility services, and uses fake accounts for persistence; the child app captures lock-screen credentials.

Aug 3, 2026
PreviousPage 37 of 100 Next
© 2026 cyber.hendryadrian.com