
Compromised Adform Script Rewrote Crypto Wallet Addresses on Customer Sites
Summary
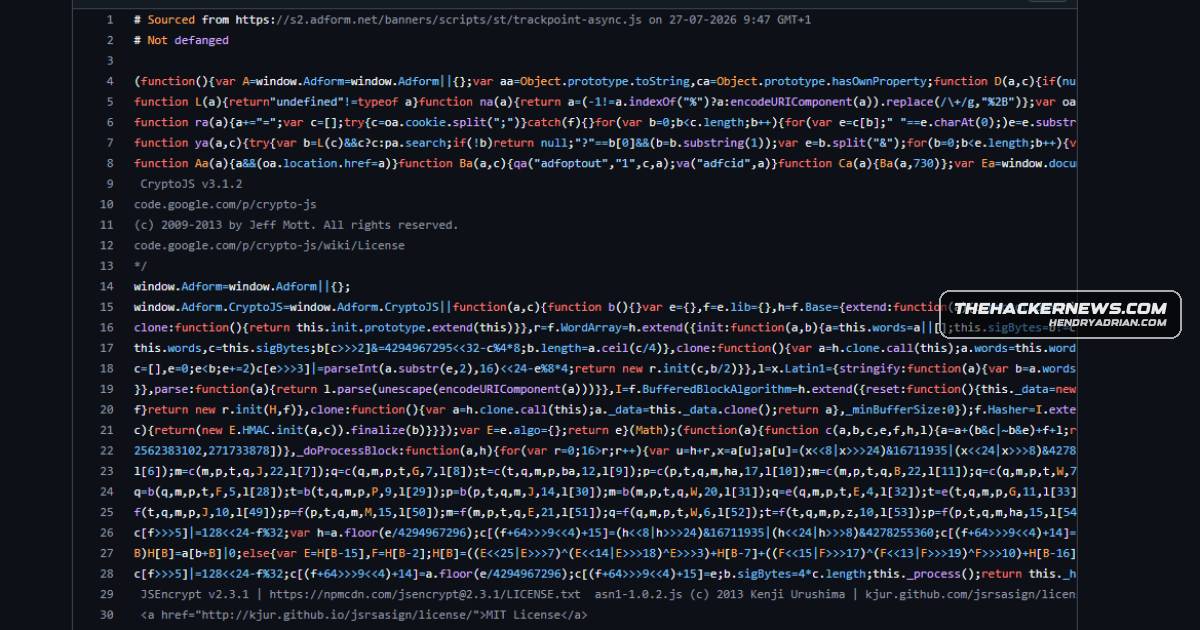
A compromised Adform script rewrote Bitcoin, Ethereum and Tron addresses on pages that loaded it. Adform removed the code July 27, 2026, but exposure scope and any diverted funds remain unknown; sample analysis details clipboard, form-field and page-data behaviors.
Key points
- The compromised trackpoint-async.js, served from s2.adform[.]net, could replace Bitcoin, Ethereum and Tron addresses on downstream sites loading the shared script.
- A captured sample contains two malicious blocks with replacement strings obfuscated using a six-byte XOR key; they targeted clipboard activity, page text and form fields.
- The script also hooked input and textarea value setters and intercepted copy, cut, paste and input events, allowing it to rewrite addresses entered or pasted into pages.
- One block attempted a request to 84.32.102.230:7744 containing the page hostname and path. Whether the request reached the operator is unknown; Adform said it found no evidence of visitor or website data transmission.
- Adform said the code operated only while an affected page was open and was not designed to install software or establish persistence.
- Adform detected and removed the code on July 27, 2026, notified customers and advised clearing browser caches and checking wallet addresses before sending funds.
- The exposure period, number of affected sites and visitors, attacker identity, and whether any funds were diverted remain unknown. Adform's July 27 date and researcher Kevin Beaumont's report of activity over the prior week are unreconciled.
Article Details
- Attack Vectors
- Attackers modified Adform’s shared trackpoint-async.js resource, exposing downstream sites that loaded it to the malicious script.
- The script replaced Bitcoin, Ethereum, and Tron addresses in copied text and in form fields, including values entered or written programmatically.
- One malicious block attempted an HTTP request to an outside server on page load, including the visited page’s hostname and path; whether the request reached an operator is not established.
- Defensive Notes
- Adform removed the malicious code on July 27, 2026, notified affected clients, and reported the incident to authorities.
- Adform advised users to clear their browser cache and verify wallet addresses before sending funds.
- Adform said the code operated only while the affected page was open and was not designed to install software or establish persistence.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | s2[.]adform[.]net | Host serving Adform’s compromised trackpoint-async.js resource. |
MITRE ATT&CK
T1059.007 · JavaScriptThe compromised JavaScript resource ran browser-side code that rewrote cryptocurrency wallet addresses.T1071.001 · Web ProtocolsThe script attempted an HTTP request to an outside server containing the page hostname and path; successful transmission is not established.T1115 · Clipboard DataThe script monitored copy events, attempted to read the clipboard, and replaced copied wallet addresses.T1195.002 · Compromise Software Supply ChainAttackers compromised Adform’s shared script, creating a supply-chain risk for downstream sites that loaded it.T1565.002 · Transmitted Data ManipulationThe script altered wallet addresses in page text and form fields before users could send funds.