Datadog Finds Pre-Prompt Code Execution Paths in Trusted Coding-Agent Projects
Summary
Datadog describes how trusted repositories can run code before a coding agent's first prompt: Codex can start project-configured MCP processes, while Claude Code can run a repository-controlled Git wrapper through PATH settings.
Key points
- Opening a trusted repository in a coding agent may allow project-controlled code to run before the user sends a prompt.
- In Codex, a project-scoped MCP configuration can start a local attacker-controlled process without user interaction.
- In Claude Code, a project-controlled PATH can cause startup Git probes to execute a repository-provided Git wrapper.
- The demonstrated paths do not require a model response or shell-command approval.
- Hooks and skills are not the only execution paths; editor tasks, environment settings, runtime startup files, and repository executables can also matter.
- The article recommends opening unfamiliar repositories in disposable environments without sensitive credentials and inspecting referenced files at the exact revision being used.
- For detection, monitor coding-agent process ancestry, executable paths, working directories, environment, and timing, especially for activity before the first prompt.
Article Details
- Attack Vectors
- A project-scoped MCP configuration in Codex can start a repository-controlled local process when the project is opened, before the first prompt and without a model response or command approval.
- A project-controlled PATH in Claude Code settings can place a repository’s Git wrapper before system Git, causing automatic startup Git probes to execute it.
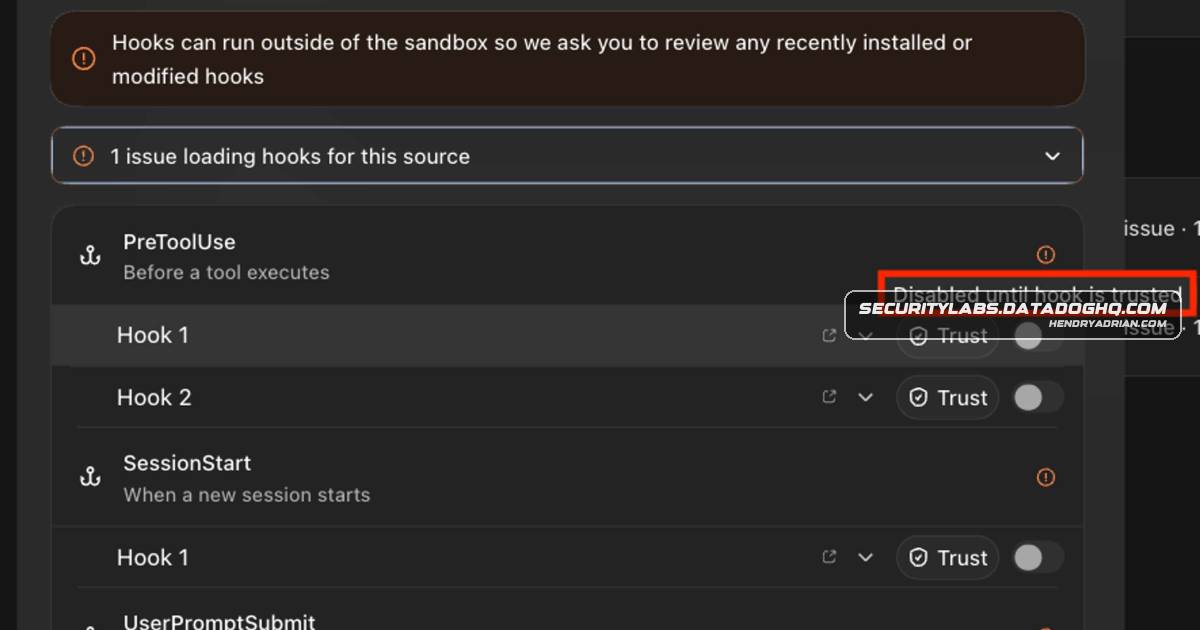
- Project-controlled hooks, skills, editor tasks, environment variables, runtime startup files, and ordinary executables are described as potential project-open execution paths.
- Defensive Notes
- Open unfamiliar repositories in disposable environments without sensitive credentials.
- Inspect project configuration, referenced files, executables earlier in PATH, and the exact revision that will run; search results are investigative leads, not proof of safety.
- Monitor coding-agent processes that spawn Git, Python, Node.js, or shell executables from the workspace, considering process ancestry, resolved executable path, working directory, environment, and timing.
MITRE ATT&CK
Vendors
Products
AI Guard for Coding AgentsAI Guard for Coding AgentsClaude CodeIn another example, three malicious npm packages installed Claude Code SessionStart hooks that executed whenever compromised projects reopened (MAL-2026-3648).CodexClaude Code and Codex both support them.Visual Studio CodeIn the Contagious Interview campaign described by Microsoft, fake recruiters convinced developers to clone and trust malicious projects, after which Visual Studio Code ran a project task.Workload ProtectionWorkload Protection