cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2387 articles

Threat Research · thehackernews.com

Amazon Ties Debug and Chalk npm Hijack to North Korean Group, Citing Incomplete Evidence

Amazon Threat Intelligence links the September 2025 debug/chalk hijack to the group behind the axios compromise with medium confidence, but the article identifies gaps in the public evidence, including a typo-crypto package-history and hash mismatch.
Jul 30, 2026
Threat Research · crowdstrike.com

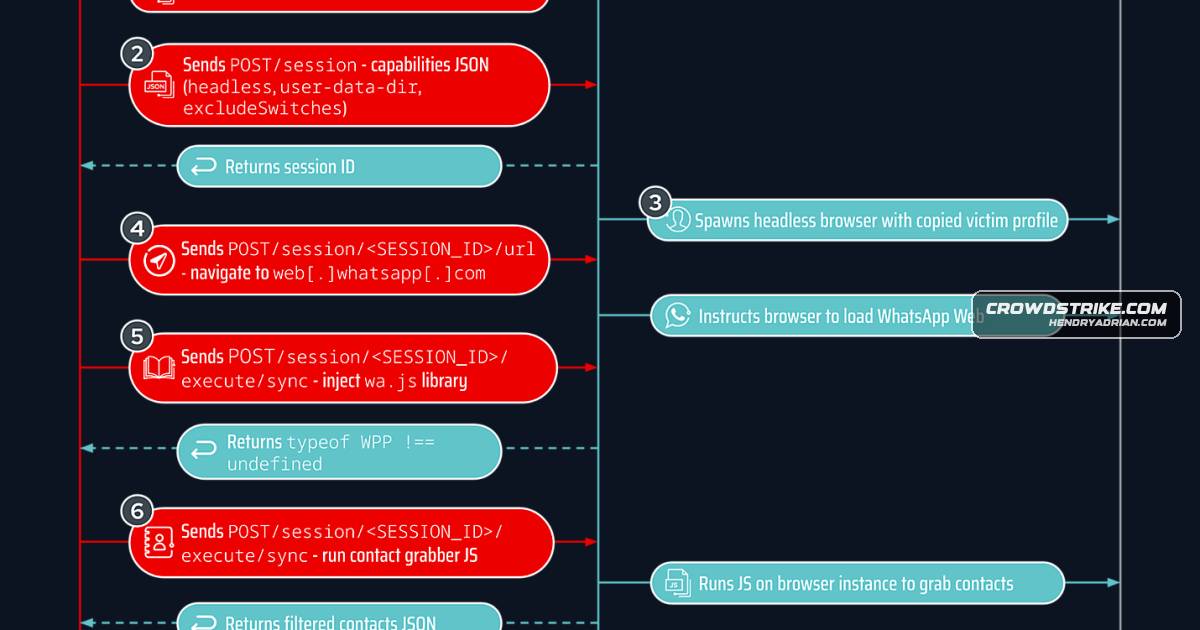
Astaroth Adds WhatsApp Web Spambot to Spread Malware in Brazil

CrowdStrike reports that Astaroth added a WhatsApp Web spambot in Q4 2025, using hidden browser automation to send malware to Brazilian contacts. Code overlap links it to Vareg, though the relationship between operators remains uncertain.

Jul 30, 2026
Threat Research · bleepingcomputer.com

Proofpoint Details Laundry Bear’s OWA Zero-Day Campaign and OWAReaper Backdoor

Proofpoint reports that Laundry Bear used CVE-2026-42897 in crafted OWA emails to deliver OWAReaper, which can maintain mailbox access through server-side permissions and cached messages, steal credentials, and communicate or exfiltrate data through multiple channels.

Jul 30, 2026
Threat Research · jamf.com

How GPU DMA Bypasses Four Samsung Galaxy Kernel Protections

The article explains how a Qualcomm KGSL vulnerability, CVE-2025-21479, can let GPU DMA bypass Samsung kernel protections, corrupt a process page table, disable SELinux and inject code into Android's init process.

Jul 30, 2026
Threat Research · cloudsek.com

Tax-Themed Phishing Campaigns Target Indian Taxpayers With Malware and Credential Theft

CloudSek analyzes tax-themed scams targeting Indian taxpayers, including WhatsApp-delivered malware and fake tax portals. The report details a Windows loader, its cloud-hosted second stage, campaign indicators, and steps to avoid or respond to infection.

Jul 30, 2026
Threat Research · asec.ahnlab.com

AhnLab Links State-Sponsored Attacks and Gunra Ransomware Through Shared Tools and Infrastructure

AhnLab’s report analyzes attacks exploiting Korean financial security software to deliver backdoors or Gunra ransomware, finding shared vulnerabilities, malware, SSH fingerprints and infrastructure that may indicate limited collaboration.

Jul 29, 2026
Threat Research · thehackernews.com

Compromised Joyfill npm Packages Deliver DEV#POPPER-Linked RAT via Blockchain C2

Socket reports that two compromised Joyfill npm packages run malware on import, using blockchain-based payload retrieval to deliver a RAT and a separate branch associated with an OmniStealer-like infostealer. Developers are advised to remove the packages and rotate keys

Jul 29, 2026
Threat Research · resecurity.com

Langflow CVE-2026-0770 Enables Unauthenticated RCE Through Code Validation Endpoint

CVE-2026-0770 lets unauthenticated attackers execute code through Langflow’s /api/v1/validate/code endpoint because validation used Python exec(). The article reports active exploitation and advises upgrading, investigating exposed instances, and rotating credentials.

Jul 29, 2026
Threat Research · huntress.com

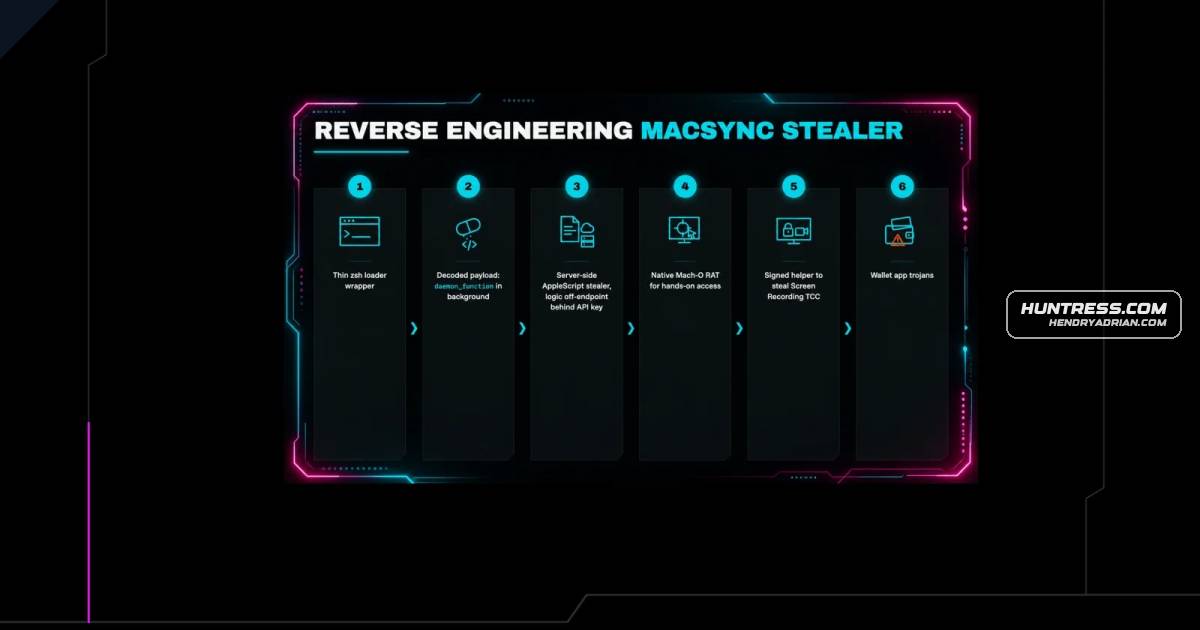
Fake Claude Install Guide Delivers MacSync Stealer and RAT to macOS Users

Huntress reverse-engineered MacSync, a six-stage macOS malware chain delivered through a fake Claude install guide in a sponsored search result. It steals credentials and wallet recovery phrases, installs a persistent RAT, and can trojanize wallet apps.

Jul 29, 2026
Threat Research · cofense.com

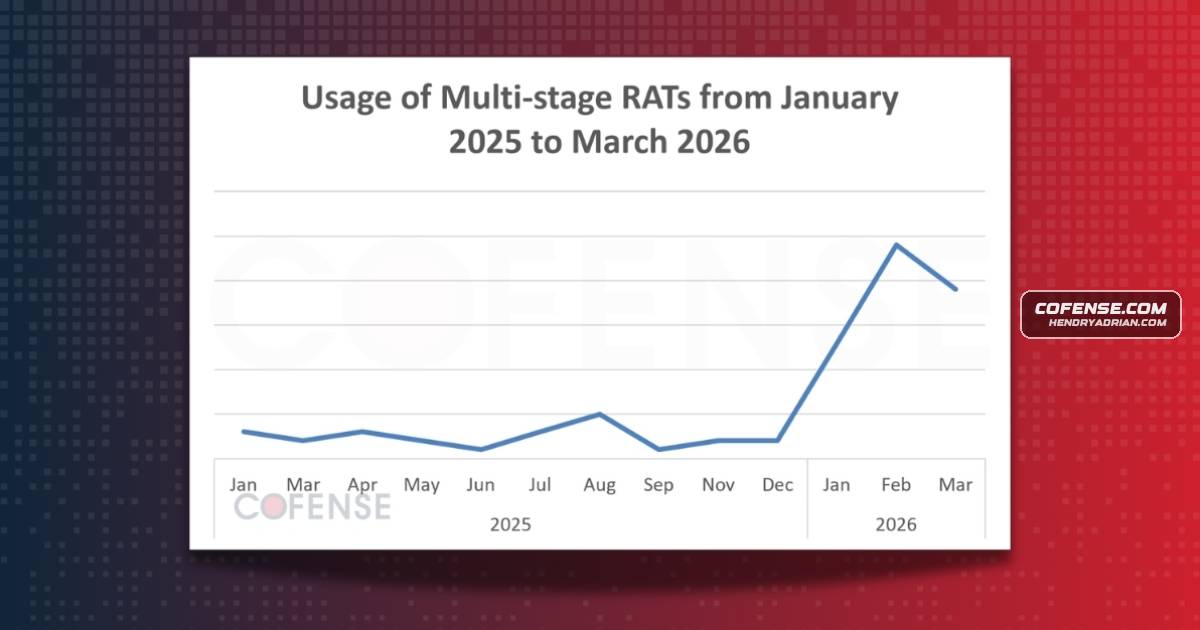
Threat Actors Expand Abuse of Legitimate Remote-Access Tools in Multi-Stage Campaigns

Cofense reports rising multi-stage campaigns that use phishing to install legitimate remote-access tools, which then fetch additional RATs or payloads via command-and-control servers. Attackers use the access to maintain persistence and may sell it to other threat actor

Jul 29, 2026
Threat Research · trendmicro.com

Trend Micro Tracks 35,538 Fake Sites Exploiting the 2026 World Cup

Trend Micro tracked 35,538 World Cup-related malicious sites from January to June 2026. The scams included fake merchandise shops, ticket-site clones stealing payment details and one-time passwords, and bogus streaming pages that harvested data or redirected users.

Jul 29, 2026
Threat Research · socket.dev

Distributed npm Packages Deliver Cross-Platform RAT Targeting Alibaba Developers

Researchers uncovered a targeted campaign that spreads malicious functionality across npm packages impersonating Alibaba’s private packages. The chain delivers a cross-platform RAT with data theft, command execution, persistence, and lateral-movement capabilities.

Jul 28, 2026
Threat Research · thehackernews.com

Tengu Botnet Uses Hardware Watchdog to Reboot Linux Devices After Process Termination

Nozomi’s analysis describes Mirai-derived Tengu’s watchdog-triggered reboot and other persistence methods, Telnet brute-force delivery, and DDoS and payload capabilities. The article establishes no infection scale or real-world victims.

Jul 28, 2026
Threat Research · thehackernews.com

Anthropic Says Claude Mythos Preview Found HAWK-256 Key-Recovery Attack and Faster Reduced-Round AES Method

Anthropic says Claude Mythos Preview helped derive a HAWK-256 key-recovery attack using a hidden lattice symmetry and sped up a seven-round AES-128 attack 200–800x; both remain impractical, and HAWK-256 is a challenge parameter.

Jul 28, 2026
Threat Research · sophos.com

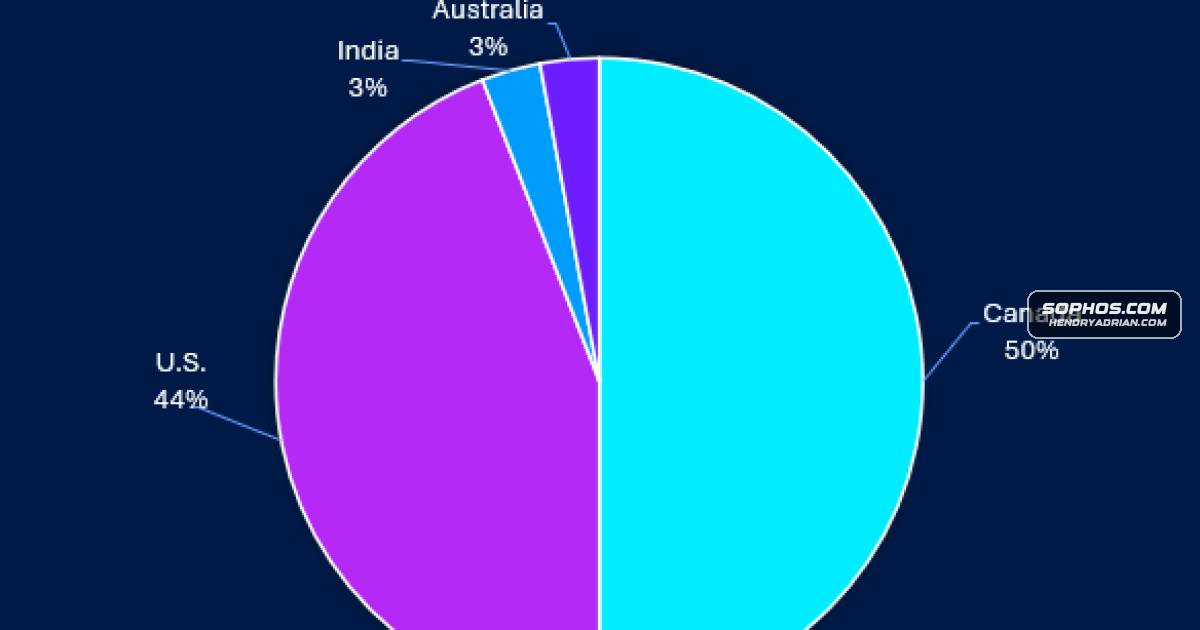
Sophos Details STAC4749 Teams Vishing Campaign Leading to Chaos Ransomware

Sophos tracked STAC4749, a Teams-vishing campaign targeting dozens of North American organizations from February to June 2026. Operators used remote-access tools and evolving backdoors; at least three intrusions led to Chaos ransomware.

Jul 28, 2026
Threat Research · wiz.io

Wiz Finds Internet-Exposed MCP Servers Leaking Sensitive Data and Cloud Credentials

Wiz Research found unauthenticated Internet-exposed MCP servers at organizations including Fortune 500 companies, with some exposing sensitive data, destructive tools, code execution, or temporary cloud credentials.

Jul 28, 2026
Threat Research · socket.dev

Compromised Joyfill npm Beta Releases Deliver DEV#POPPER RAT

Socket researchers found import-time malware in two Joyfill npm beta releases. The implant retrieves payloads through blockchain transactions and can deliver a remote-access trojan; separate captured payloads include a credential-stealing Python program.

Jul 28, 2026
Threat Research · proofpoint.com

TA488 Uses Outlook Web Access XSS to Deploy Persistent OWAReaper Implant

Proofpoint reports that TA488 exploited CVE-2026-42897 in Outlook Web Access to target government and other organizations with OWAReaper, a browser-based implant designed to steal credentials and maintain mailbox access.

Jul 28, 2026
Threat Research · securelist.com

Mirage Kitten Uses NightLedger and WebSocket Tunnelers in Espionage Campaign

Kaspersky researchers attribute NightLedger, ArcBridge and BridgeHead to Mirage Kitten, reporting their use in espionage targeting aerospace, aviation, defense and telecom organizations across the Middle East, Europe and Africa. Initial access remained unclear for most

Jul 28, 2026
Threat Research · stepsecurity.io

StepSecurity Details Import-Triggered RAT in Compromised Joyfill npm Packages

StepSecurity found six 2773 prereleases of @joyfill/components and @joyfill/layouts contained an import-triggered payload with blockchain-based C2, a Socket.IO RAT, persistence and a Python credential stealer. Sandbox runs saw no C2 callback.

Jul 28, 2026
Threat Research · hunt.io

Flying Eagle Android RAT: Leaked Code, 170 Servers and Night Dragon

Researchers traced a fake Chinese Public Security Bureau app to the Flying Eagle Android RAT, identified 170 related servers, and linked leaked code to criminal channels distributing modified builds and a likely successor, Night Dragon.

Jul 28, 2026
Threat Research · circleid.com

Check Point Research Maps TDS-Driven Malware Operation Through DNS Analysis

Check Point Research traced fake project portals to CloudFront-hosted JavaScript staging and gated TDS redirects that led selected users toward RemusStealer, AnimateClipper, and SessionGate. DNS and WHOIS analysis expanded the investigation to 30 network IoCs.

Jul 27, 2026
Threat Research · asec.ahnlab.com

AtlasRAT Analysis Reveals Four-Stage In-Memory Loader and Modular RAT Capabilities

Researchers detail AtlasRAT’s four-stage Windows loader, modular RAT functions, persistence techniques, and hunting indicators. Evidence suggests a builder-based development system, but does not establish a conclusive link to Silver Fox.

Jul 27, 2026
Threat Research · thehackernews.com

Dysphoria IoT Botnet Uses Blockchain C2 and Infected-Device Relays

Researchers describe Dysphoria’s spread through weak IoT credentials and flaws, and its use of blockchain records and infected-device relays. Reported bot counts and attack capacity have not been independently verified.

Jul 27, 2026
PreviousPage 39 of 100 Next
© 2026 cyber.hendryadrian.com