
DNS Investigation Maps ErrTraffic ClickFix Infrastructure
Summary
DNS/WHOIS analysis of 71 ErrTraffic ClickFix domain indicators found 12 of 16 associated IPs flagged as malicious, 12 email-connected domains, and historical resolution data. Sekoia reported WordPress-focused clusters and fake AI lures; LenAI involvement was suspected.
Key points
- Sekoia analyzed the ErrTraffic ClickFix distribution framework and identified 71 domain indicators.
- The two studied clusters focused on WordPress servers, used a built-in traffic distribution system, concealed C2 infrastructure within blockchain infrastructure, and used fake AI tools such as Google Antigravity and ChatGPT as lures.
- Researchers suspected LenAI involvement but assessed that the Analytics and Beer clusters were likely operated by different, unnamed threat actors.
- The DNS analysis found eight client IP addresses communicating with six domain indicators in 45 DNS queries from April 20 to June 15, 2026, across four ASNs.
- The article reports that 30 indicators resolved to 16 IP addresses, 12 of which were identified as weaponized in other malicious campaigns.
- Historical DNS data showed 566 domain-to-IP resolutions for 70 indicators; the article says all 70 continued to resolve in 2026.
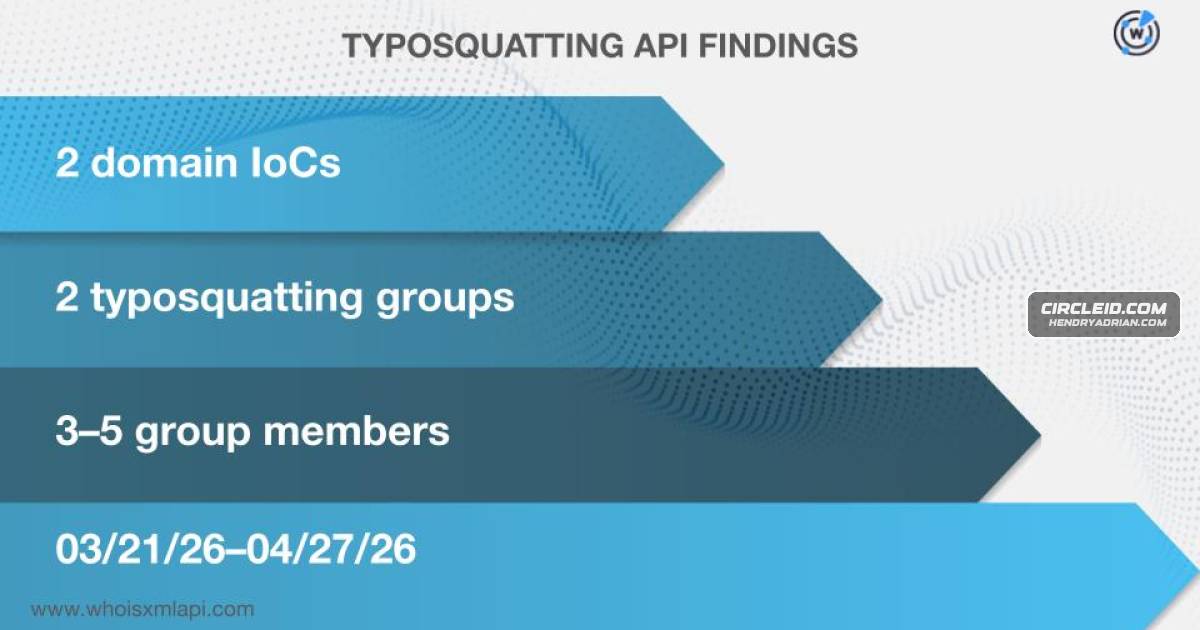
- Reverse WHOIS searches found 12 email-connected domains. The analysis also identified typosquatting groups involving finework[.]top and sandman[.]bond.
Article Details
- Attack Vectors
- The campaign used the ErrTraffic ClickFix distribution framework and focused on WordPress servers.
- Fake AI tools, including Google Antigravity and ChatGPT, were used as lures.
- The clusters reportedly used a built-in TDS function and concealed command-and-control infrastructure within blockchain-related infrastructure.
- Defensive Notes
- The article recommends corroborating threat findings with supplementary investigation, noting that entities initially identified as malicious may later be deemed harmless.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | abrikos[.]xyz | ErrTraffic domain IoC with historical domain-to-IP resolutions recorded from March 2022 to May 2026. |
| DOMAIN | anakondabob[.]club | ErrTraffic domain IoC with historical domain-to-IP resolutions recorded in May 2026. |
| DOMAIN | bobik[.]cfd | ErrTraffic domain IoC with historical domain-to-IP resolutions recorded in May 2026. |
| DOMAIN | cloud-safe[.]click | ErrTraffic domain IoC reported in the First Watch Malicious Domains Data Feed as likely registered with malicious intent. |
| DOMAIN | finework[.]top | ErrTraffic domain IoC; reported as bulk-registered with look-alike domains and associated with typosquatting. |
| DOMAIN | sandman[.]bond | ErrTraffic domain IoC; reported as bulk-registered with look-alike domains and associated with typosquatting. |
| DOMAIN | webanalytics-cdn[.]sbs | ErrTraffic domain IoC with historical domain-to-IP resolutions recorded from February to April 2026. |
MITRE ATT&CK
T1036 · MasqueradingThe investigation found campaign domains in typosquatting groups and reported look-alike domains registered alongside finework[.]top and sandman[.]bond.T1566 · PhishingThe campaign used fake AI tools, including Google Antigravity and ChatGPT, as lures to draw victims into the activity.T1583.001 · DomainsThe investigation identified 71 campaign domain IoCs, including domains reported as bulk-registered with look-alikes.
Threat Actors
Products
ChatGPTFake AI tools such as Google Antigravity and ChatGPT were used as lures.ClickFixThe campaign leveraged the ErrTraffic ClickFix malware distribution framework.ErrTrafficThe campaign leveraged the ErrTraffic ClickFix malware distribution framework.Google AntigravityFake AI tools such as Google Antigravity and ChatGPT were used as lures.WordPressThe activity focused on WordPress servers and used a built-in TDS function.