Fake CAPTCHA PDFs Funnel Search Traffic to Malware and Scams
Summary
Netskope traced more than 12,700 FakeCaptcha PDFs on Webflow’s CDN to an active traffic-distribution network that filters visitors and routes them to malware, ad landers, or a premium-SMS scam.
Key points
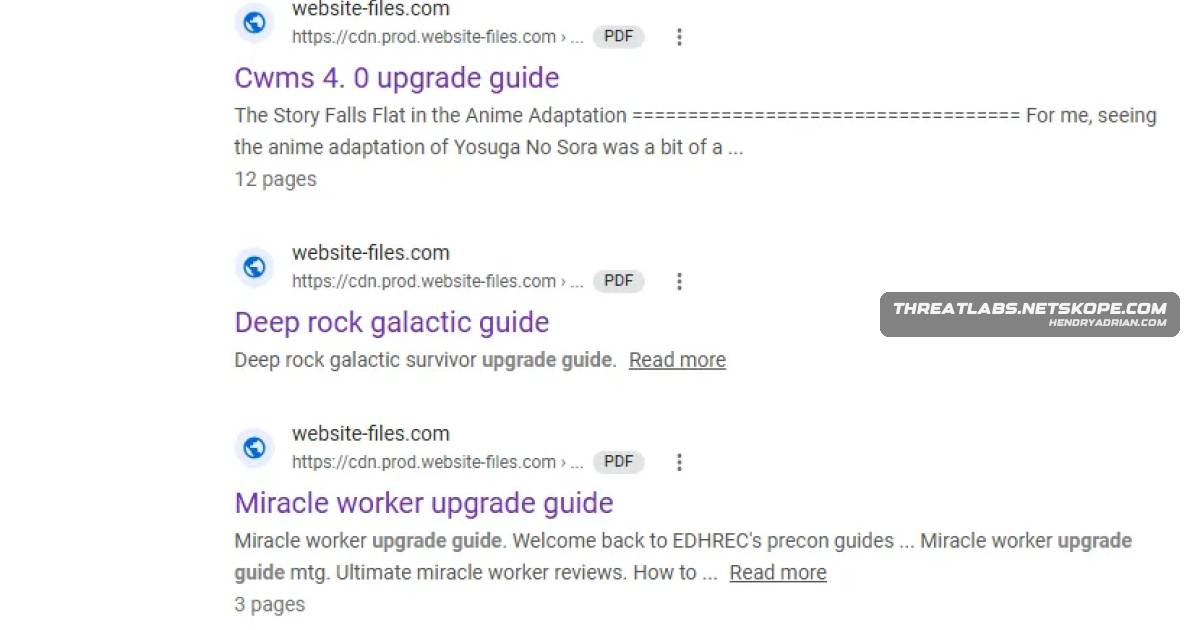
- The PDFs pose as upgrade guides, use SEO text to surface in search results, and lead visitors through a fake CAPTCHA into a traffic-distribution system.
- The system filters visitors by IP and autonomous system, Cloudflare Turnstile and JWT checks, then geography and device; rejected visitors are sent to ad landers.
- Netskope found more than 12,700 structurally similar PDFs; a tighter match identified about 2,480 files in two clusters dating to May 2025.
- Telemetry showed Google accounted for about 98% of referrers; AI assistants appeared as referrers in roughly 3% of environments with observed downloads.
- Observed destinations included a Legion Loader distribution hub, a reseller TDS gate, and a Spanish-language premium-SMS subscription scam; the scam’s connection to this TDS is inferred.
- Netskope recommends detection based on stable PDF structure and wwNN router subdomains, since lure domains rotate; it also describes coverage for documents, TDS infrastructure, and payloads.
Article Details
- Attack Vectors
- Search-engine-optimized FakeCaptcha PDFs hosted on Webflow's CDN lure users into a traffic-distribution system that filters visitors and routes qualifying traffic to malware or scam infrastructure.
- The TDS uses an IP and autonomous-system check, a Cloudflare Turnstile challenge followed by a Joken JSON Web Token, and geo- and device-based filtering.
- A documented Legion Loader distribution page used a fake CAPTCHA to hijack the clipboard and instruct victims to press Win+R and paste a command that installs an MSI.
- A Spanish-language scam used a QR-code fake CAPTCHA and mobile-device checks to direct victims to a phone-number-harvesting page that triggered a premium-rate SMS subscription.
- Defensive Notes
- Netskope recommends detecting stable PDF structure and the wwNN router-subdomain pattern, alongside rotating lure domains.
- The article recommends blocking newly observed lure domains and TDS infrastructure rather than only alerting on them.
- The article says blocking Webflow's shared CDN is not an option; Netskope describes coverage at PDF download, network infrastructure, and payload stages.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | berapt-medii[.]com | Legion Loader distribution hub and malware distribution point. |
| DOMAIN | binonelola[.]com | Listed in the 2026 lure pool and reported as payload infrastructure contacted by a dropper. |
| DOMAIN | bovetewa[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | chromovira[.]org | FakeCaptcha routing domain in the premium-SMS scam flow. |
| DOMAIN | dutabuz[.]com | 2025 lure domain in the FakeCaptcha traffic-distribution operation. |
| DOMAIN | godoxevez[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | gowixese[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | jufewine[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | maxudijuz[.]com | 2026 lure domain in the FakeCaptcha traffic-distribution operation. |
| DOMAIN | nurepikis[.]com | 2026 lure domain in the FakeCaptcha traffic-distribution operation. |
| DOMAIN | pofezaf[.]com | 2026 lure domain in the FakeCaptcha traffic-distribution operation. |
| DOMAIN | riwitamo[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | scorenetsystems[.]pro | Scam landing-page domain used in the premium-SMS subscription trap. |
| DOMAIN | solidlinkpro[.]info | Phone-number-harvesting page in the premium-SMS subscription trap. |
| DOMAIN | tugoduzak[.]com | 2026 lure domain in the FakeCaptcha traffic-distribution operation. |
| DOMAIN | vimemug[.]com | Listed as a 2026 lure domain in the operation. |
| DOMAIN | ww19[.]nurepikis[.]com | Example wwNN traffic-router domain used to route visitors through the TDS. |
| DOMAIN | ww80[.]tugoduzak[.]com | Example wwNN traffic-router domain used to route visitors through the TDS. |
| DOMAIN | yfdpco1[.]com | TDS reseller gate domain using the sk-park[.]php gate. |
| DOMAIN | yfdpco2[.]com | Listed as a stage-2 TDS gate and shared hub. |
| DOMAIN | yfdpco4[.]com | TDS reseller gate domain using the sk-park[.]php gate. |
| DOMAIN | zuwufag[.]com | 2025 lure domain in the FakeCaptcha traffic-distribution operation. |
| IPV4 | 185[.]53[.]179[.]200 | IP listed for the ww80 traffic router. |
| IPV4 | 188[.]72[.]236[.]249 | IP listed for the berapt-medii[.]com Legion Loader hub. |
| IPV4 | 208[.]91[.]196[.]46 | IP listed for the yfdpco gate backend. |
| IPV4 | 212[.]92[.]104[.]119 | TDS entry-gate IP listed as an indicator. |
| SHA256 | 87b8b76762eac941c562c6c8eefb8402f48fc70fcfe360a274b12e75dd5726e2 | Hash of the reported Documentos[.]pdf.exe dropper sample. |
MITRE ATT&CK
Malware
Products
Advanced Threat ProtectionAt the PDF download, threat intelligence signatures block known malicious documents inline, and the Advanced Threat Protection cloud sandbox detects Patient Zero samples and rotated variants by behavior.Claudewe saw these downloads, the referrer was not a search results page but an AI assistant: Google Gemini, Claude, and, in one case, an enterprise assistant deployed internally by an organization.Cloudflare TurnstileSecond, a Cloudflare Turnstile challenge, followed by a Joken JSON Web Token, rejects bots that pass the IP check.Google Geminiwhere we saw these downloads, the referrer was not a search results page but an AI assistant: Google Gemini, Claude, and, in one case, an enterprise assistant deployed internally by an organization.Netskope OneNetskope OneNetskope Threat ProtectionNetskope Threat Protection covers the Legion Loader payload family should a victim reach the distribution hub.Webflowfactory has stamped out more than 12,700 structurally similar FakeCaptcha documents and parked them on Webflow’s content delivery network, where Google indexes them as ordinary “upgrade guides.” Each document is a
Countries
AustraliaExposure skewed to the English-speaking world, led by the United States, India, Australia, the United Kingdom, and Canada: across 26 countries in total.CanadaExposure skewed to the English-speaking world, led by the United States, India, Australia, the United Kingdom, and Canada: across 26 countries in total.IndiaExposure skewed to the English-speaking world, led by the United States, India, Australia, the United Kingdom, and Canada: across 26 countries in total.United KingdomExposure skewed to the English-speaking world, led by the United States, India, Australia, the United Kingdom, and Canada: across 26 countries in total.United StatesExposure skewed to the English-speaking world, led by the United States, India, Australia, the United Kingdom, and Canada: across 26 countries in total.