
Microsoft Tracks 250+ ClickFix Domains Hiding macOS Infostealer Lures
Summary
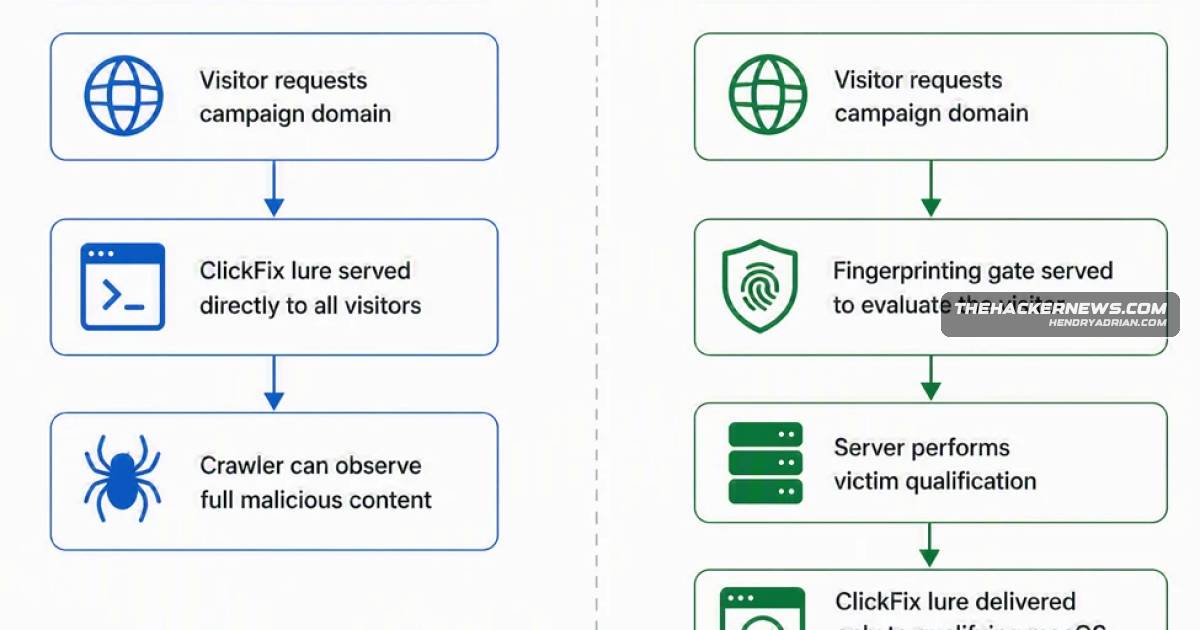
Microsoft tracked more than 250 domains using server-side fingerprinting to hide fake macOS download lures from crawlers and sandboxes. The analyzed command-driven chain delivered AMOS; the wider cluster also distributed MacSync.
Key points
- Microsoft tracked more than 250 front-end domains using a server-side gate to decide which pages visitors see.
- The gate checks browser and device signals, including platform, screen dimensions, WebGL, timezone, iframe status, touch support and analyst-oriented probes.
- Selected Mac users receive a fake GitHub-style download page; crawlers, sandboxes and other visitors may see a blank or unrelated page.
- The attack requires victims to paste and run an obfuscated Terminal command, which fetches scripts; Microsoft’s analyzed chain launched Atomic Stealer (AMOS).
- Microsoft said the wider domain cluster also distributed MacSync, but did not map every domain to a payload.
- The stealer targets credentials, browser data, authentication stores, cryptocurrency wallets and sensitive files; Microsoft did not disclose victim numbers, sectors or operator identities.
- Microsoft recommends hunting for fingerprinting-gate artifacts, shared infrastructure and /curl/ paths, as well as unusual Terminal activity.
Article Details
- Attack Vectors
- Selected Mac users are shown a fake GitHub-style software download page after server-side fingerprinting qualifies their browser and environment.
- The attack relies on the victim copying and running an obfuscated command in Terminal; the command retrieves scripts and launches Atomic Stealer (AMOS).
- Microsoft said the wider domain cluster also distributed MacSync, but did not map every domain to a payload.
- Defensive Notes
- Do not follow website, CAPTCHA, chat, or download instructions that ask users to paste text into Terminal.
- Hunt for the fingerprinting gate, including self-submitting fingerprint forms, hidden fingerprint fields, and the mode:"php" artifact; do not treat an apparently benign response as proof that a domain is safe.
- Monitor browsing followed by unusual Terminal activity, including curl piped into zsh, Base64 decoding, osascript, and archive creation followed by outbound HTTP POST requests.
- Microsoft recommends blocking shared staging infrastructure and /curl/ paths rather than relying only on disposable front-end domains.
- Apple's macOS 26.4 added a Terminal confirmation prompt in specified circumstances, and XProtect can trace pasted commands and block activity associated with known malware.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | applefilevault[.]com | Cited by Microsoft as an example of a front-end domain in the malicious ClickFix cluster. |
| DOMAIN | filecopperbasket[.]sbs | Cited by Microsoft as an example of a front-end domain in the malicious ClickFix cluster. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes an obfuscated command and an encoded staging address in the attack chain.T1059.004 · Unix ShellThe victim-run command uses Terminal to retrieve scripts and launch the malware.T1059.007 · JavaScriptA JavaScript gate script fingerprints visitors and sends the resulting information to the server, which selects the response.T1105 · Ingress Tool TransferThe command contacts a /curl/<id> path to retrieve further scripts.T1204.004 · Malicious Copy and PasteThe attack requires the victim to copy and paste a command into Terminal and run it.T1497.001 · System ChecksThe server-side gate checks platform, screen dimensions, WebGL signals, and other environment details to distinguish genuine Macs from virtual or emulated environments and hide the lure from sandboxes.
People
Malware
Atomic macOS Stealer (AMOS)The attack chain leads to Atomic Stealer (AMOS) and sometimes MacSync, and it still depends on the victim pasting and running an obfuscated Terminal command.Atomic StealerThe attack chain leads to Atomic Stealer (AMOS) and sometimes MacSync, and it still depends on the victim pasting and running an obfuscated Terminal command.MacSyncThe attack chain leads to Atomic Stealer (AMOS) and sometimes MacSync, and it still depends on the victim pasting and running an obfuscated Terminal command.
Vendors
Products
macOSMicrosoft tracked a macOS ClickFix operation across more than 250 front-end domains that uses server-side fingerprinting to hide the lure from crawlers and sandboxes while serving targeted Mac users a fake softwareTerminalThe attack chain leads to Atomic Stealer (AMOS) and sometimes MacSync, and it still depends on the victim pasting and running an obfuscated Terminal command.XProtectSeparately, XProtect can trace commands pasted into any terminal emulator, inspect their process tree and network artifacts, and block activity associated with known malware.