UNC6671 Uses Vishing and AiTM Phishing Across Multiple Extortion Brands
Summary
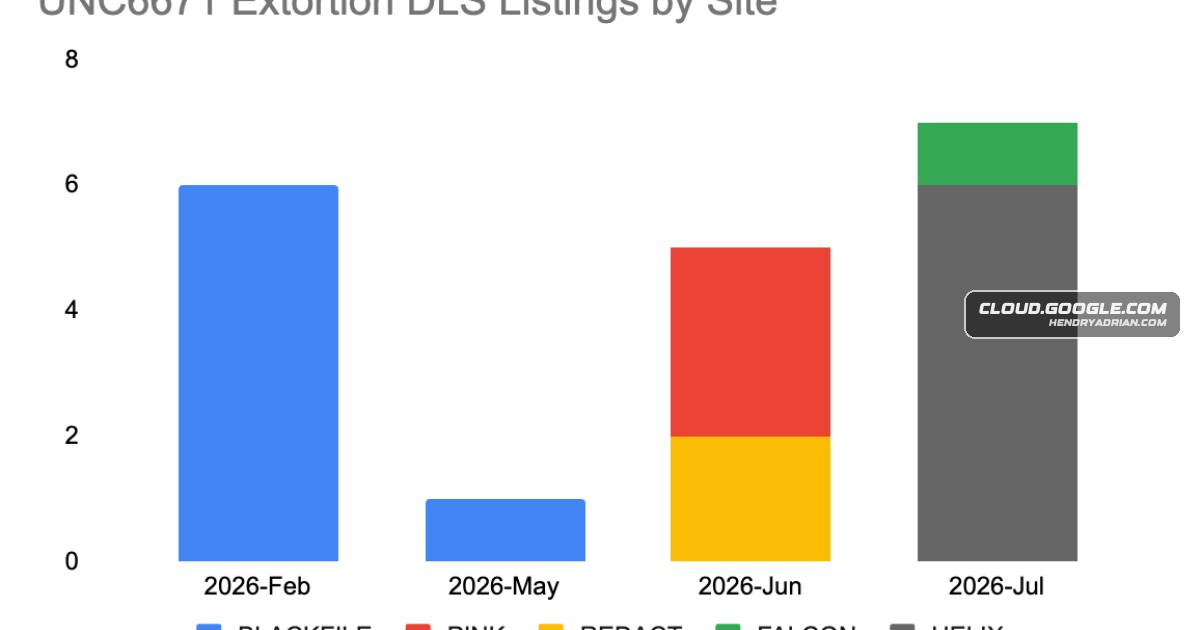
Google GTIG links UNC6671 activity across BlackFile, Redact, Pink, Helix, and Falcon, detailing helpdesk vishing, AiTM credential theft, SaaS data exfiltration, changing targets, and defenses.
Key points
- UNC6671 reportedly impersonates IT helpdesk staff in calls to employees’ personal phones, directing them to spoofed portals that steal credentials and MFA tokens.
- The group uses AiTM infrastructure to establish session access, then scripts data exfiltration from Microsoft 365 and Okta.
- Overlapping domains, phishing templates, and victim targeting link activity associated with BlackFile, Redact, Pink, Helix, and Falcon, though shared services or splintered actors remain possible explanations.
- GTIG observed targeting shift toward financial, legal, private equity, and professional-services organizations, alongside a faster pace of domain provisioning in June and July 2026.
- Recent activity included unauthorized password resets for non-SSO applications and deletion of related security notifications and alerts.
- GTIG recommends phishing-resistant MFA, consistent SSO controls, session and device restrictions, and monitoring identity-provider and SaaS audit logs for suspicious access and scripted file activity.
- GTIG says identified phishing domains were added to Google Safe Browsing and provides IOCs and detection rules; it cautions that domains can be short-lived and source IPs change.
Article Details
- Attack Vectors
- UNC6671 uses voice phishing, often calling employees on personal mobile numbers and sometimes spoofing legitimate helpdesk phone numbers.
- Callers impersonate IT helpdesk staff and use urgent security-migration pretexts, including enabling FIDO2 passkeys or updating MFA enrollment, to direct employees to tailored credential-harvesting portals.
- Adversary-in-the-Middle infrastructure intercepts credentials and MFA tokens; the article reports that session persistence is then established.
- Operators use compromised email accounts to initiate unauthorized password resets for non-SSO enterprise applications and delete related confirmations, security notifications, and alerts.
- Automated scripts are used to exfiltrate data from enterprise SaaS and cloud environments, including Microsoft 365 and Okta.
- Defensive Notes
- Enforce phishing-resistant authenticators, including FIDO2-compliant security keys, passkeys, and platform authenticators, across SSO environments and identity providers.
- Integrate business-critical SaaS applications and cloud platforms with a standard SSO platform to apply consistent security controls.
- Shorten session lifetimes, enforce idle timeouts and step-up authentication, and use token-theft mitigations such as IP session binding, Device-Bound Session Credentials, and Continuous Access Evaluation.
- Restrict authentication to trusted network sources and require corporate-managed devices with MDM and EDR.
- Enable credential protections such as Google Workspace Password Alert and Microsoft Defender SmartScreen and Credential Protection.
- Monitor identity-provider audit logs for MFA registration events preceded by authentication failures or abandoned push challenges.
- Treat FileAccessed events as high priority for detection when scripting-library user agents or unusually high access volumes indicate possible SaaS exfiltration.
- Alert on SSO authentication from commercial VPN providers or unassociated residential proxy pools when activity diverges from employee geographic baselines.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | activatemypasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | activatepasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | activatepasskeyportal[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | add-passkey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | addmypasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | addoktapasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | addpasskey2fa[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | addssopasskey[.]com | Phishing domain hosting a credential-harvesting template used to target organizations later extorted under Falcon. |
| DOMAIN | addyourpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | assignpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | checkpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | createmfa[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | createmypasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | createpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | createssopasskey[.]com | Phishing domain hosting a credential-harvesting template and used in targeted helpdesk-vishing campaigns. |
| DOMAIN | deploypasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | enablepasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | enablepasskey2fa[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | enrollpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | hubpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | idokta[.]com | Phishing domain used to target an organization extorted under the BlackFile brand. |
| DOMAIN | keyokta[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | keysyncos[.]com | Phishing infrastructure targeting multiple organizations later listed on the Helix data leak site. |
| DOMAIN | makepasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | mspasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | myaccountsecurity[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | myconnectkey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | mynewpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | myoktasso[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | mypasskeyid[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | mypasskeysso[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | mysecurepasskey[.]com | Phishing infrastructure used as an intermediate bridge between extortion-brand infrastructure. |
| DOMAIN | myssopasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | newpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | oktaenroll[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | oktaportalsso[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | oskeyconnect[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | oskeysync[.]com | Phishing infrastructure targeting multiple organizations later listed on the Helix data leak site. |
| DOMAIN | passkey-check[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkey-connect[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkey-setup[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyactivation[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyadd[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeycenter[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeycreate[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeycreator[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeydeploy[.]com | Phishing infrastructure used to target an organization extorted by Pink and linked through intermediate targets to other extortion brands. |
| DOMAIN | passkeyenable[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyenroll[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyhelpdesk[.]com | Phishing domain used to target organizations extorted under Falcon and Helix and to host matching credential-harvesting templates. |
| DOMAIN | passkeymfa[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyms[.]com | Phishing infrastructure used as an intermediate bridge to another credential-harvesting infrastructure cluster. |
| DOMAIN | passkeyokta[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyportal[.]com | Helix-related phishing infrastructure; also described as a bridge from a BlackFile victim to Helix infrastructure. |
| DOMAIN | passkeyportalsetup[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyregister[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyregistration[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyrollout[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyset[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeystatus[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeysupport[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | passkeyuser[.]com | Phishing domain used to target a BlackFile victim, with intermediate targets bridging to other extortion-brand infrastructure. |
| DOMAIN | portalpasskey[.]com | Phishing domain used to target organizations extorted under the Falcon brand. |
| DOMAIN | portalsetuphub[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | registerpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | secure-passkey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | secureauthpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | setpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | setupsso[.]com | Phishing domain used to target an organization extorted under BlackFile and linked through intermediate targets to Pink infrastructure. |
| DOMAIN | setupssopasskey[.]com | Phishing domain used to target an organization extorted under the BlackFile brand. |
| DOMAIN | sqfepjvmrd[.]xyz | Listed as a phishing-domain indicator in the article's IOC table. |
| DOMAIN | ssopasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | startpasskey[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| DOMAIN | startpasskeysetup[.]com | Listed as a phishing-domain indicator associated with UNC6671 targeting. |
| IPV4 | 107[.]128[.]45[.]122 | Residential-proxy infrastructure used for Microsoft 365 and Okta activity. |
| IPV4 | 185[.]178[.]208[.]153 | Phishing reverse-proxy infrastructure. |
| IPV4 | 193[.]34[.]212[.]132 | Phishing-kit backend proxy. |
| IPV4 | 195[.]140[.]213[.]114 | Infrastructure identified for automated SaaS data exfiltration. |
| IPV4 | 195[.]140[.]213[.]115 | Infrastructure identified for automated SaaS data exfiltration. |
| IPV4 | 23[.]234[.]75[.]84 | Infrastructure identified for automated SaaS data exfiltration. |
| IPV4 | 31[.]7[.]56[.]52 | Panel AiTM reverse-proxy infrastructure. |
| IPV4 | 31[.]7[.]56[.]61 | Panel AiTM reverse-proxy infrastructure. |
| IPV4 | 38[.]42[.]59[.]171 | Residential-proxy infrastructure used for Microsoft 365 and Okta activity. |
| IPV4 | 47[.]218[.]103[.]146 | Residential-proxy infrastructure used for Microsoft 365 and Okta activity. |
| IPV4 | 76[.]103[.]148[.]180 | Residential-proxy infrastructure used for Microsoft 365 and Okta activity. |
MITRE ATT&CK
T1056.003 · Web Portal CaptureLookalike login portals and AiTM credential-harvesting panels capture employee credentials and MFA tokens.T1070.008 · Clear Mailbox DataOperators delete password-reset confirmations, security notifications, and other alerts from compromised email accounts to reduce detection.T1530 · Data from Cloud StorageAutomated scripts are used to exfiltrate data from enterprise cloud and SaaS environments, including Microsoft 365 and Okta.T1550.004 · Web Session CookieThe article reports that session persistence is established after AiTM interception of authentication credentials and MFA tokens.T1557 · Adversary-in-the-MiddleThe article describes AiTM infrastructure intercepting credentials and MFA tokens during authentication.T1566.004 · Spearphishing VoiceUNC6671 uses voice phishing calls, including helpdesk impersonation and urgent security-migration pretexts, to direct targeted employees to credential-harvesting portals.
People
Threat Actors
Vendors
GoogleGoogle Threat Intelligence Group (GTIG) continues to track UNC6671 actively conducting compromises leading to data theft extortion, despite the alleged announced retirement of the BlackFile extortion brand in May 2026.MicrosoftOnce session persistence is established, the actors deploy automated scripts for data exfiltration from enterprise cloud environments, including Microsoft 365 and Okta.OktaOnce session persistence is established, the actors deploy automated scripts for data exfiltration from enterprise cloud environments, including Microsoft 365 and Okta.
Products
Credential ProtectionFor Microsoft 365 environments, configure Microsoft Defender SmartScreen and Credential Protection to block credential submissions on unverified sites.Entra IDIntegrating business-critical applications with a standard SSO platform such as Entra ID or Okta allows consistent application of security controls across disparate platforms.Google Safe BrowsingAt the time of publication, identified phishing domains have been added to Google Safe Browsing.Google SecOpsGoogle SecOps customers have access to automated detection rules under the Okta and Microsoft 365 rule packs that identify the vishing, MFA modification, and programmatic streaming activity described in this report:Google WorkspaceDeploy Endpoint and Browser Credential Guarding: Enable Google Workspace Password Alert to trigger automated administrative alerts or resets if corporate password hashes are entered into unauthorized domains.Microsoft 365Once session persistence is established, the actors deploy automated scripts for data exfiltration from enterprise cloud environments, including Microsoft 365 and Okta.Microsoft Defender SmartScreenFor Microsoft 365 environments, configure Microsoft Defender SmartScreen and Credential Protection to block credential submissions on unverified sites.OktaOnce session persistence is established, the actors deploy automated scripts for data exfiltration from enterprise cloud environments, including Microsoft 365 and Okta.Okta Fastpassroaming security keys, passkeys, and platform authenticators (e.g., Windows Hello for Business, Okta Fastpass) across all SSO environments and enterprise identity providers (IdPs).Windows Hello for Businesssuch as FIDO2-compliant roaming security keys, passkeys, and platform authenticators (e.g., Windows Hello for Business, Okta Fastpass) across all SSO environments and enterprise identity providers (IdPs).
Countries
Industries
Aerospace & DefenseConstruction & Engineering, Legal, Aerospace & Defense, Financial Services, Technologybusiness servicesBusiness Services, TechnologyConstruction & EngineeringHealthcare, Construction & EngineeringEnergyFinancial Services, Energy, HealthcareFinancial rating agenciesBy July 2026, the target profile narrowed to focus on the financial and legal sectors, with observed infrastructure directed at private equity firms, law firms, and financial rating agencies.Financial ServicesWe also examine the evolution of UNC6671's targeting including recent activity focused on financial services, private equity, and professional services, and provide hardening guidance to help organizations protectHealthcareBetween April and May 2026, we observed domains broadly designed to target mature, large-scale enterprises across multiple industries including the manufacturing, real estate, healthcare, and insurance sectors.HospitalityIn June 2026, targeting transitioned toward large technology, transportation, and hospitality organizations, seemingly focusing on entities holding valuable intellectual property, software source code, or sensitive VIPInsuranceof the BlackFile brand in May 2026 to sow confusion among threat intelligence analysts and cyber insurance negotiators, thereby damaging the brand's reputation.LegalBy July 2026, the target profile narrowed to focus on the financial and legal sectors, with observed infrastructure directed at private equity firms, law firms, and financial rating agencies.ManufacturingBetween April and May 2026, we observed domains broadly designed to target mature, large-scale enterprises across multiple industries including the manufacturing, real estate, healthcare, and insurance sectors.Media & EntertainmentFinancial Services, Healthcare, Media & EntertainmentPrivate equityexamine the evolution of UNC6671's targeting including recent activity focused on financial services, private equity, and professional services, and provide hardening guidance to help organizations protect themselvesProfessional ServicesUNC6671's targeting including recent activity focused on financial services, private equity, and professional services, and provide hardening guidance to help organizations protect themselves from this threat.real estateBetween April and May 2026, we observed domains broadly designed to target mature, large-scale enterprises across multiple industries including the manufacturing, real estate, healthcare, and insurance sectors.Retail & Consumer GoodsRetail & Consumer Goods, Healthcare, LegalTechnologyIn June 2026, targeting transitioned toward large technology, transportation, and hospitality organizations, seemingly focusing on entities holding valuable intellectual property, software source code, or sensitive VIPTransportationIn June 2026, targeting transitioned toward large technology, transportation, and hospitality organizations, seemingly focusing on entities holding valuable intellectual property, software source code, or sensitive VIPUtilitiesFinancial Services, Real Estate, Legal, Healthcare, Transportation, Utilities, Construction & Engineering, Retail & Consumer Goods, Hospitality