cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2386 articles

Threat Research · zscaler.com

ChainDrop npm Worm Steals Developer Credentials and Spreads Malicious Packages

Zscaler details ChainDrop, a Shai-Hulud variant that poisoned npm packages, stole credentials, and spread through developer tokens. It uses Ethereum-based C2 and IDE hooks, and may trigger destructive activity when stolen tokens are revoked.
Aug 11, 2026
Threat Research · sophos.com

Threat actors abuse Deno to run fileless malware in four intrusion cases

Sophos analyzed four 2026 intrusions in which attackers used malicious MSI installers and script loaders to deploy Deno, then ran obfuscated JavaScript in memory for host fingerprinting and command-and-control.

Aug 11, 2026
Threat Research · levelblue.com

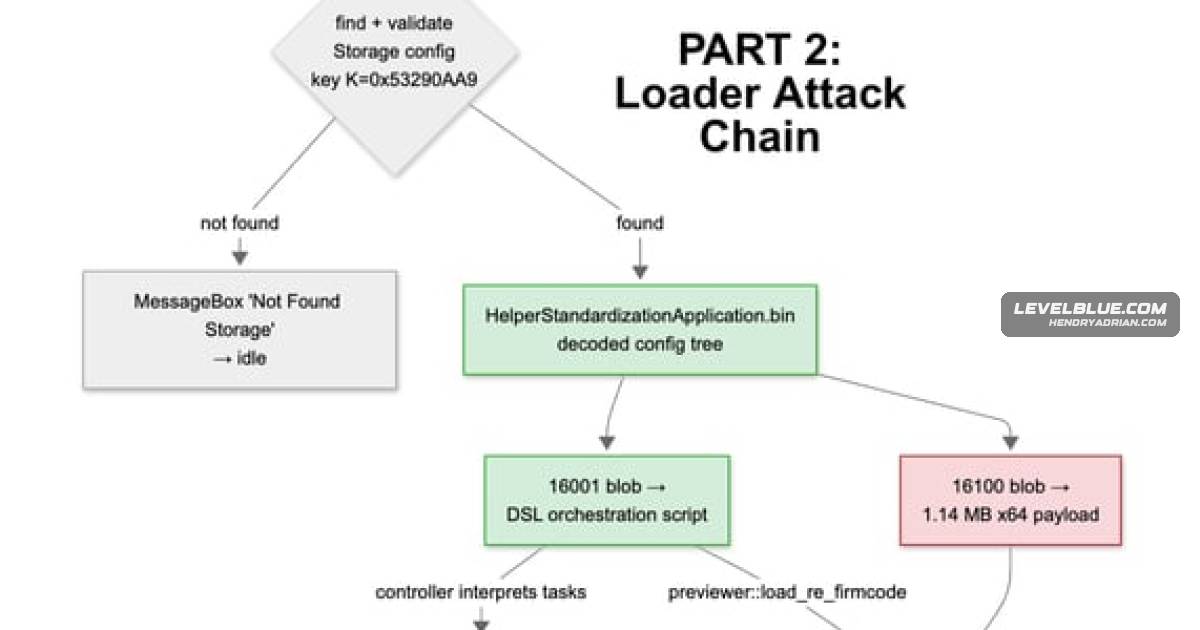
Research Uncovers CNCMachineRMS RAT at End of BabaDeda Loader Chain

An investigation traces a ClickFix infection through signed WinWrapIDE.exe, four decoy DLLs and BabaDeda to CNCMachineRMS, a RAT with shell, file, screenshot, persistence and account-backdoor capabilities.

Aug 10, 2026
Threat Research · cisa.gov

Joint Advisory Details Gunra Ransomware Intrusions and Linux Recovery Weakness

A joint agency advisory details Gunra ransomware’s VPN exploitation, credential theft, MFA bypass and double extortion. It also describes a Linux encryption weakness that may allow recovery and recommends patching, segmentation and isolated backups.

Aug 10, 2026
Threat Research · asec.ahnlab.com

Larva-26010 Targets Korean Web Servers to Install SoftEther VPN

AhnLab details attacks from April to August 2026 in which Larva-26010 targeted Korean web servers and MS-SQL systems, installing SoftEther VPN, web shells, and SqlShell. The initial intrusion method remains unknown.

Aug 10, 2026
Threat Research · wiz.io

Researchers Trace Metabase SQL Injection to Unchecked User-ID in Password-Reset Requests

Wiz researchers reverse engineered an actively exploited Metabase SQL injection flaw affecting versions 1.58 and later. They traced it to an unchecked user-id value in password-reset requests and urged self-hosted users to patch.

Aug 10, 2026
Threat Research · cloudsek.com

TXTBOOK Campaign Targets T-Bank With 993 Malicious npm Packages and a Sliver Implant

CloudSEK details TXTBOOK, a dependency-confusion campaign that published 993 malicious npm packages mimicking T-Bank’s private namespace. The packages can execute a Sliver implant, delivered through DNS TXT records, if resolved inside the bank’s network.

Aug 10, 2026
Threat Research · any.run

Researchers Infiltrate DPRK IT Worker Scheme, Exposing Lazarus-Linked Operatives’ Tools and Infrastructure

Researchers posed as a DeFi startup to hire suspected Famous Chollima operatives and monitor their work, documenting forged identities, remote-access practices, tools, infrastructure, and risks from trusted insider access.

Aug 10, 2026
Threat Research · zscaler.com

Abyssos RAT Uses Modular C2 Commands for Credential Theft, File Exfiltration, and Remote Access

Zscaler ThreatLabz analyzes Abyssos, a modular Windows RAT with encrypted C2 communications, extensive remote-control and data-theft commands, obfuscation, and optional anti-analysis checks.

Aug 10, 2026
Threat Research · hunt.io

Research details toolkits targeting Ukrainian IP cameras and routers

Hunt.io analyzed two exposed directories documenting credential theft, SQL injection, camera and router exploitation, and proxy tooling. One cataloged 58 compromised Ukrainian cameras; government and military attacks and exploitation by the second operation were unして

Aug 10, 2026
Threat Research · asec.ahnlab.com

Phishing Receipts Deliver ScreenConnect for Persistent Remote Access

AhnLab describes phishing emails that use fake transaction receipts and a malicious PDF to install ScreenConnect, giving attackers persistent remote access to compromised systems.

Aug 9, 2026
Threat Research · genians.co.kr

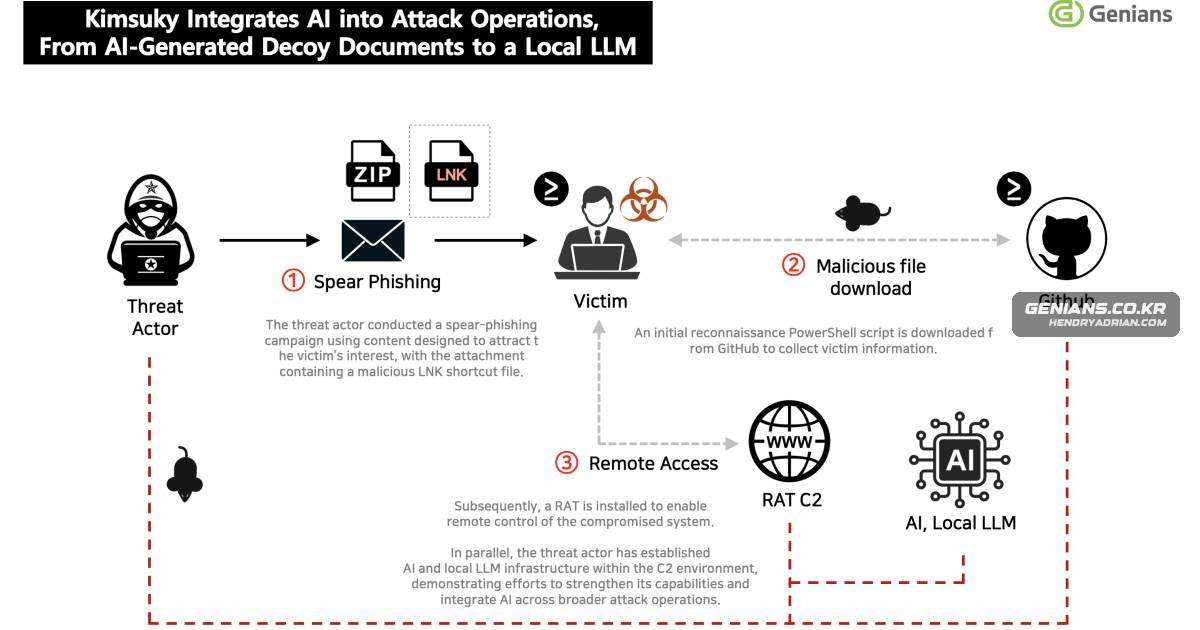
Kimsuky Uses AI-Generated Decoys and Experiments with Local LLMs

Genians’ analysis of Kimsuky-linked Operation GitPower details spear-phishing attacks using malicious LNK files, PowerShell and Git-based C2, and evidence the group is experimenting with local LLMs and AI development tools.

Aug 9, 2026
Threat Research · bleepingcomputer.com

Kaspersky Finds Head Mare Exploiting TrueConf Flaws to Trojanize Installers

Kaspersky says Head Mare exploited TrueConf Server flaws to replace client installers with PhantomCore backdoors and deploy PhantomGraph for command execution and credential theft. TrueConf patched affected versions in updates released June 18.

Aug 8, 2026
Threat Research · securityweek.com

RovoBlast One-Click Attack Could Exfiltrate Enterprise Data Through Atlassian Rovo

Varonis researchers demonstrated that a crafted link could seed prompts into Atlassian Rovo and trigger its ResearchAgent to expose internal data. Atlassian fixed the flaw before publication.

Aug 8, 2026
Threat Research · thehackernews.com

Email CSS Attacks Can Escape Webmail Boundaries to Steal Credentials and Tokens

PortSwigger researchers showed how HTML and CSS in email can escape webmail message boundaries to steal credentials and tokens, hijack UI actions, and manipulate AI email tools. Proofs of concept span major providers; some issues were fixed, while others remained.

Aug 8, 2026
Threat Research · elastic.co

Elastic Traces Coding-Agent-Parented Tunnels and LaunchAgent Persistence on macOS

Elastic analyzed macOS telemetry showing Claude Code-parented credentialed requests to tunnel-hosted URLs, Cloudflare tunneling, and LaunchAgent persistence. The activity may have exposed a local admin app; the evidence did not establish an intrusion.

Aug 8, 2026
Threat Research · opensourcemalware.com

Researchers Detail npm Worm, WEL1DROPPER Campaign and DPRK-Linked NullReceiver C2 Technique

The episode analyzes an npm worm that compromised 400+ packages and stole credentials, a campaign publishing over 1,000 malicious npm packages, and a DPRK-linked technique that hides C2 IPs in empty Ethereum transfers.

Aug 8, 2026
Threat Research · censys.com

Mirai-Derived Botnets Rebound as Exposed IoT Devices Remain Vulnerable

Censys finds Mirai-derived botnets recovering after 2026 takedowns, while exposed ADB services and outdated Boa software persist. The analysis links this resilience to insecure IoT supply chains, weak defaults, and limited consumer ability to update devices.

Aug 7, 2026
Threat Research · thehackernews.com

ClickFix Campaign Uses macOS Stealer That Can Drain Crypto Wallets

A ClickFix lure prompts macOS users to run a Terminal command that downloads a Go-based stealer. Huntress says it can collect credentials and redirect some or all funds from supported cryptocurrency wallets to attacker-controlled accounts.

Aug 7, 2026
Threat Research · thehackernews.com

Nearly 800 Malicious npm Packages Deliver Cross-Platform Malware via WEL1DROPPER

Researchers describe nearly 800 malicious npm packages using WEL1DROPPER to deliver OS-specific payloads, with DNS TXT fallback, platform-specific evasion and persistence, and a Linux chain leading to Sliver.

Aug 7, 2026
Threat Research · circleid.com

Genians Details APT37 NarwhalRAT Campaign and Infrastructure

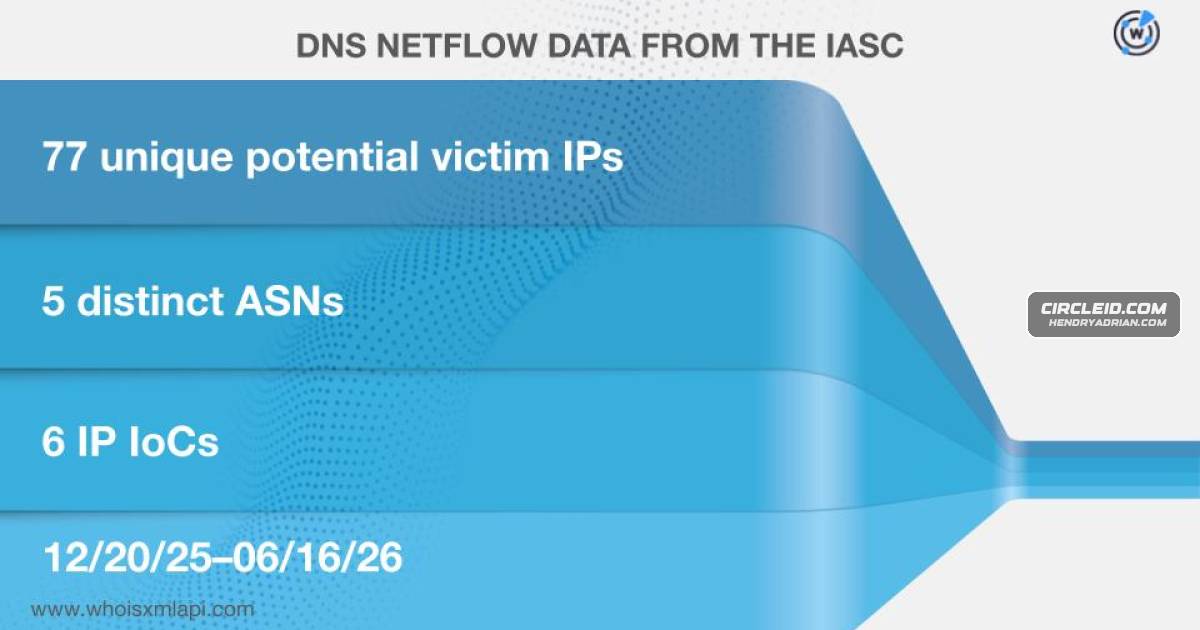
Genians researchers describe an APT37 campaign using NarwhalRAT, likely delivered through spearphishing and malicious LNK files. Their infrastructure analysis identified network indicators and 77 IP addresses potentially associated with victims.

Aug 7, 2026
Threat Research · levelblue.com

Fake App Stores and Software Updates Deliver Unauthorized ScreenConnect Clients

LevelBlue researchers traced a phishing campaign using fake app stores, meeting pages and document portals to distribute unauthorized ScreenConnect clients. Shared web resources and DNS artifacts linked related infrastructure.

Aug 7, 2026
Threat Research · thehackernews.com

Researchers Detail WordPress Login XSS Chain to PHP Execution

WordPress patched CVE-2026-64638, a pre-auth reflected XSS in its login screen. pwn[.]ai demonstrated a chain to PHP execution, but it requires an administrator to interact with an attacker-controlled page; WordPress says escalation depends on social engineering.

Aug 7, 2026
Threat Research · securityweek.com

NMFTA Finds Remote Code Execution Flaws in Bendix Truck Brake Controller

NMFTA says reverse-engineering found serious flaws in Bendix EC80 brake controllers, including potential remote code execution and traction-control disablement. Tests triggered ECU failures; a 2024 recall covered an estimated 450,000 units.

Aug 7, 2026
PreviousPage 35 of 100 Next
© 2026 cyber.hendryadrian.com