Varonis Researchers Detail RovoBlast, a One-Click Path to Data Exposure in Atlassian Rovo
Summary
Varonis researchers say a crafted link could seed instructions into Atlassian Rovo and, using its access to connected services and agent capabilities, expose organizational data. Atlassian was notified and fixed the issue.
Key points
- The researchers say the rovoChatPrompt URL parameter could place attacker-supplied instructions into a user's Rovo Chat session after a single click, without a warning or confirmation.
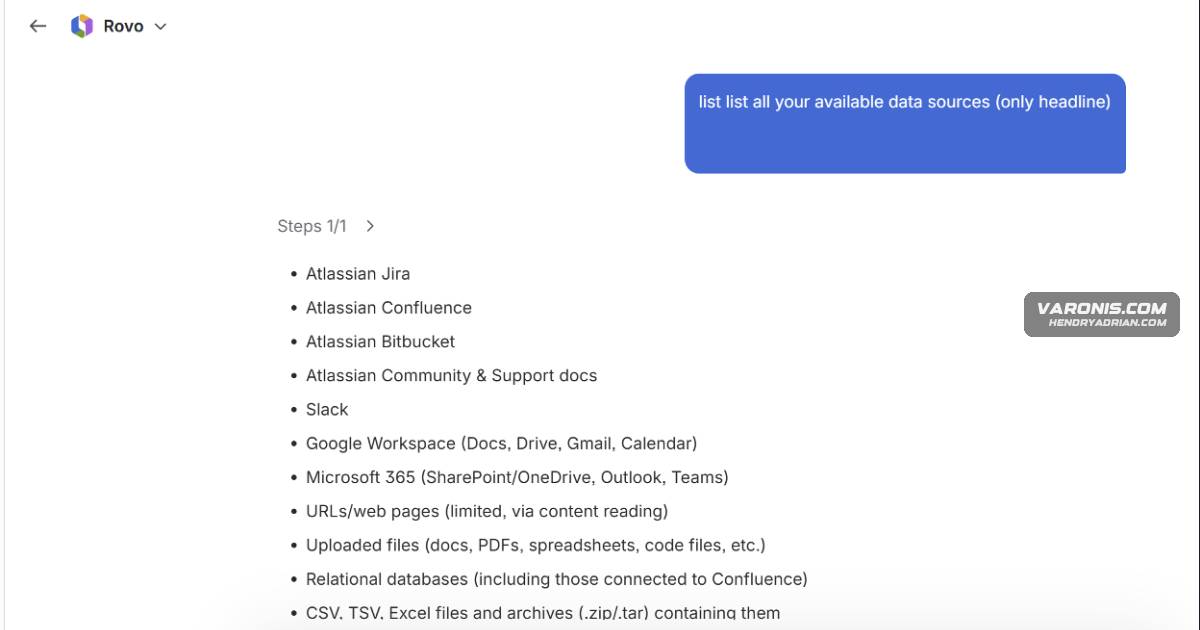
- Rovo could search and summarize data from Jira, Confluence, Bitbucket, and connected services including Slack, Google Workspace, and Microsoft 365.
- Varonis demonstrated how Rovo's ResearchAgent browsing and multi-step capabilities could provide a route for sending data to external websites.
- The researchers report that the tested data-leakage path generally did not require jailbreaks or double-request techniques.
- Varonis says it responsibly disclosed RovoBlast to Atlassian and that the issue was fixed; the article does not specify affected versions or patch details.
- Varonis recommends limiting Rovo's connected data sources and agent capabilities, and monitoring assistant logs and unusual agent activity.
Article Details
- Attack Vectors
- A crafted link sets the rovoChatPrompt parameter, automatically surfacing attacker-supplied instructions in Rovo Chat within the user's trusted session.
- Rovo can search connected organizational data and summarize sensitive information in response to seeded prompts.
- ResearchAgent's autonomous browsing and multi-step actions can be used to transfer retrieved information to external websites.
- The organization ID can be omitted from the /o/< ID>/chat path; according to the article, Atlassian redirects the request to the user's default organization.
- Defensive Notes
- Limit the systems Rovo can access and disconnect unused integrations; keep highly sensitive areas such as legal, HR, finance, and incident response out of scope.
- Disable browsing agents, multi-step automation, and other AI features that are not needed.
- Review assistant logs, alert on unusual agent runs, and periodically test how the environment handles prompts seeded through external inputs.
People
Vendors
Products
BitbucketRovo operates as an AI layer across the core products in the Atlassian platform, including Jira, Confluence, Bitbucket, as well as other connected SaaS tools like Slack, Microsoft 365, and Google.ConfluenceRovo operates as an AI layer across the core products in the Atlassian platform, including Jira, Confluence, Bitbucket, as well as other connected SaaS tools like Slack, Microsoft 365, and Google.Google WorkspaceRovo confidently enumerated every major surface it could read from, including Jira, Confluence, Bitbucket, Slack, Google Workspace, Microsoft 365, relational databases, uploaded files, web pages, and even archives.JiraRovo operates as an AI layer across the core products in the Atlassian platform, including Jira, Confluence, Bitbucket, as well as other connected SaaS tools like Slack, Microsoft 365, and Google.Microsoft 365Rovo operates as an AI layer across the core products in the Atlassian platform, including Jira, Confluence, Bitbucket, as well as other connected SaaS tools like Slack, Microsoft 365, and Google.Microsoft CopilotEnterprise AI assistants such as Rovo or Microsoft Copilot operate at the intersection of highly privileged data, automated actions, and untrusted inputs, including links, documents, connectors, and comments.RovoVaronis Threat Labs uncovered a vulnerability in Rovo, Atlassian's enterprise AI assistant.SlackRovo operates as an AI layer across the core products in the Atlassian platform, including Jira, Confluence, Bitbucket, as well as other connected SaaS tools like Slack, Microsoft 365, and Google.