cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2381 articles

Threat Research · thehackernews.com

Cling Botnet Exploits Realtek SDK Flaw and Hides C2 in STUN Traffic

Researchers say Cling botnet operators are exploiting the patched Realtek Jungle SDK flaw CVE-2021-35394 and other device vulnerabilities. The malware uses STUN traffic for command-and-control, persistence, proxying, tunneling, propagation, and DoS attacks.
Oct 5, 2026
Threat Research · opensourcemalware.com

Malicious RubyGems Packages Deploy Reverse Shells and Cryptocurrency-Theft Toolkit

Researchers identified 42 malicious RubyGems packages that use reverse shells or a toolkit to hijack cryptocurrency transactions and steal wallet data. The article details the malware’s delivery, persistence, and operation.

Oct 5, 2026
Threat Research · stepsecurity.io

StepSecurity Reports Credential-Stealing Backdoor in @subql/common 5.8.3

StepSecurity reports that @subql/[email protected] contains a payload that runs on install or import, collects credentials, and supports exfiltration and remote commands via ci-artifacts[.]dev. Its analysis found no evidence of execution on victim systems.

Oct 5, 2026
Threat Research · cloudsek.com

CloudSEK Finds Gentlemen Ransomware Affiliate’s Exposed Servers and Stolen Data

CloudSEK reports that Gentlemen affiliate Azazel used stolen CI/CD secrets and other techniques to compromise more than two dozen organizations, steal about 6TB of data, and operate a separate extortion site. Exposed servers revealed the operation.

Oct 5, 2026
Threat Research · hexastrike.com

FLEXRAT Stealer and RAT Uses Fake ChilloutVR Mods to Steal Credentials

Researchers detail FLEXRAT, a stealer and remote-access tool delivered through fake ChilloutVR mod sites and Dropbox downloads. It steals browser credentials and Discord data, captures screens, enables remote control, and establishes persistence.

Oct 4, 2026
Threat Research · thehackernews.com

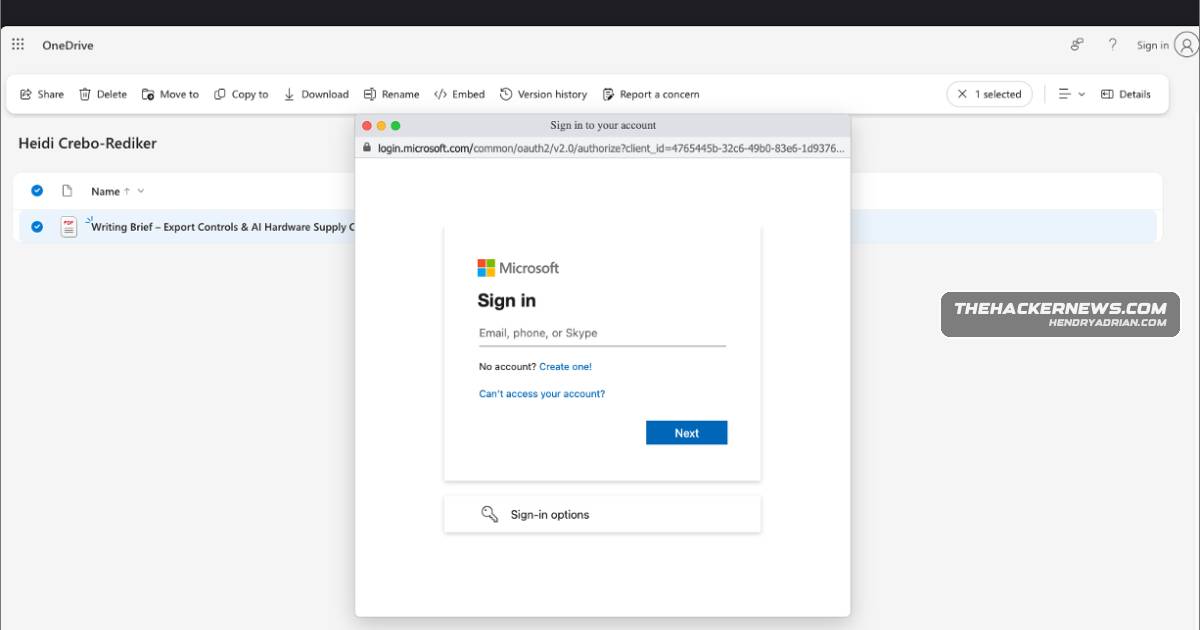
TA419 Uses Frameless BitB Phishing to Target U.S. AI Policy Experts

China-aligned TA419 targeted U.S. AI policy experts with phishing that used impersonation, shortened links, redirects, and a Frameless BitB adversary-in-the-middle page to steal Microsoft credentials and session cookies.

Oct 4, 2026
Threat Research · thehackernews.com

Warlock Exploits SharePoint Flaws to Disable Defenses and Deploy Ransomware

Warlock has exploited SharePoint flaws in attacks on organizations across Europe, Africa, and Latin America, using web shells, BYOVD, and SYSVOL staging to disable security tools and deploy ransomware.

Oct 3, 2026
Threat Research · bleepingcomputer.com

Warlock Ransomware Group Exploits SharePoint Flaws and Disables Security Tools

Researchers detail Warlock attacks that exploited SharePoint flaws, used a vulnerable driver to disable protection on at least 40 hosts, and deployed ransomware across organizations in Europe, Africa, and Latin America.

Oct 2, 2026
Threat Research · thehackernews.com

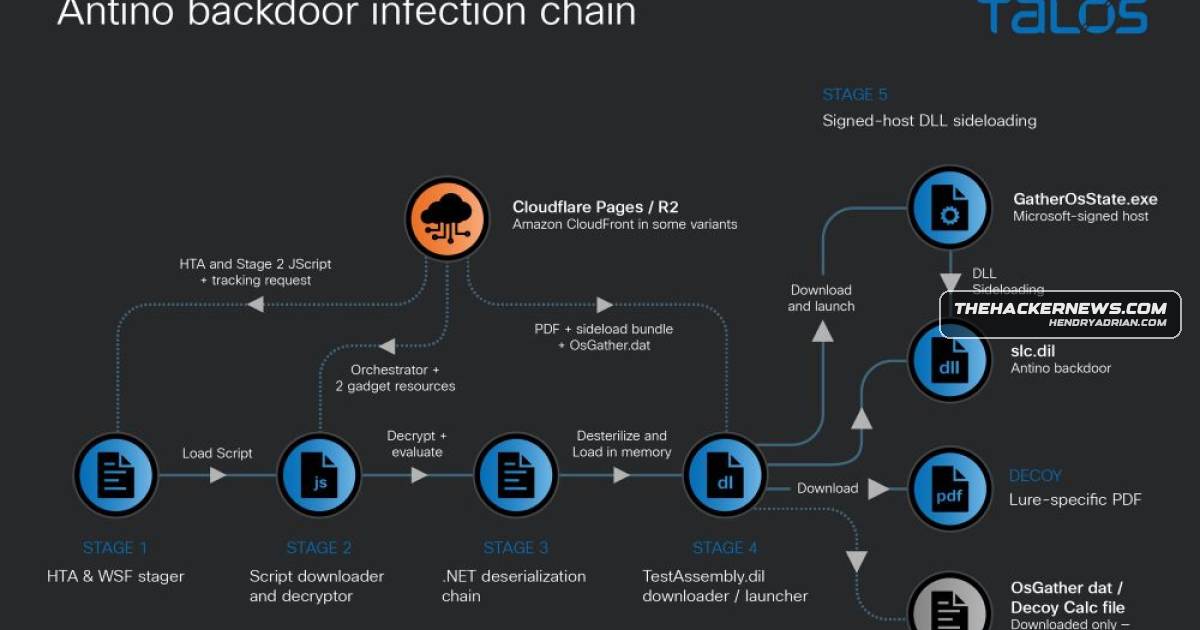
UAT-11587 Uses Antino Backdoor and Microsoft 365 for Espionage Campaign

Cisco Talos reports that UAT-11587 targeted government and policy organizations in Asia and Syria with Antino, a Rust backdoor delivered through spear-phishing and using Outlook and OneDrive for command-and-control.

Oct 2, 2026
Threat Research · helpnetsecurity.com

China-Aligned TA419 Uses Fake OneDrive Pages to Target US AI Policy Experts

Proofpoint says China-aligned TA419 impersonated policy figures to phish US AI experts, using fake OneDrive pages and browser-in-the-browser techniques to steal Microsoft credentials, MFA codes, and session cookies.

Oct 2, 2026
Threat Research · rogueauthority.org

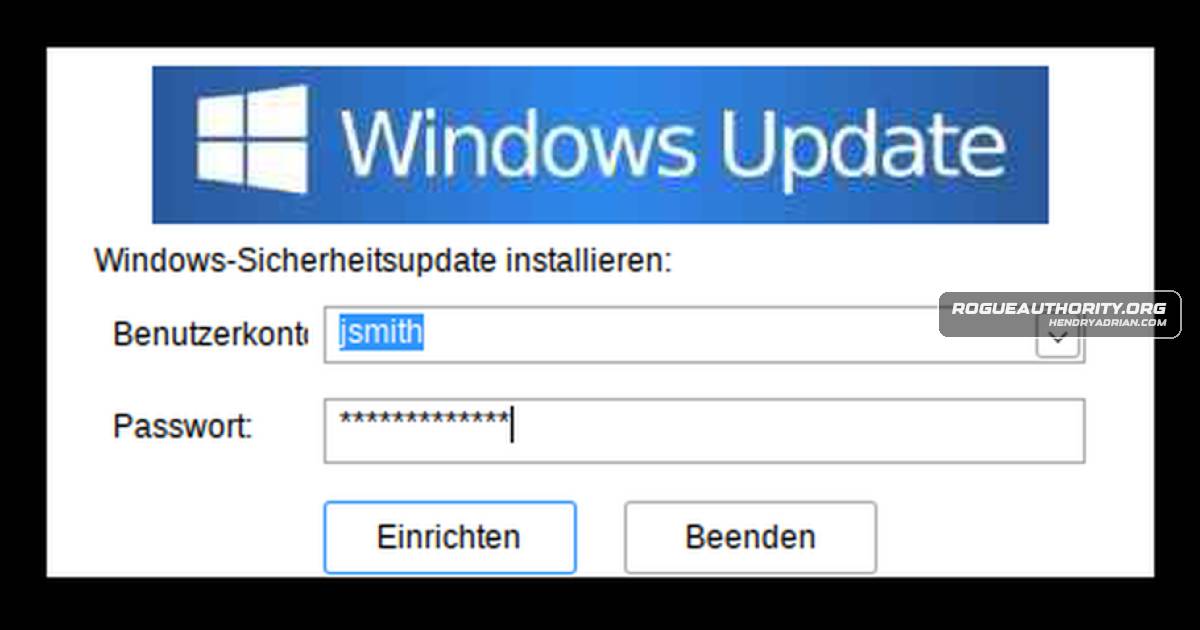
Fake Windows Update Steals Passwords and Logs Every Attempt

PolicyMgr.exe impersonates a German Windows Update prompt, saves every entered password in a local text file before checking it, and has no built-in upload capability. Researchers link it to another tool signed with the same certificate.

Oct 2, 2026
Threat Research · securityweek.com

Fake Zoom Installer Delivers CloudSyncD Backdoor to macOS Users

Researchers report CloudSyncD, a persistent macOS backdoor delivered through a fake Zoom installer. It profiles infected Macs and exfiltrates system and user details; deployment-stage builds have been observed.

Oct 2, 2026
Threat Research · rapid7.com

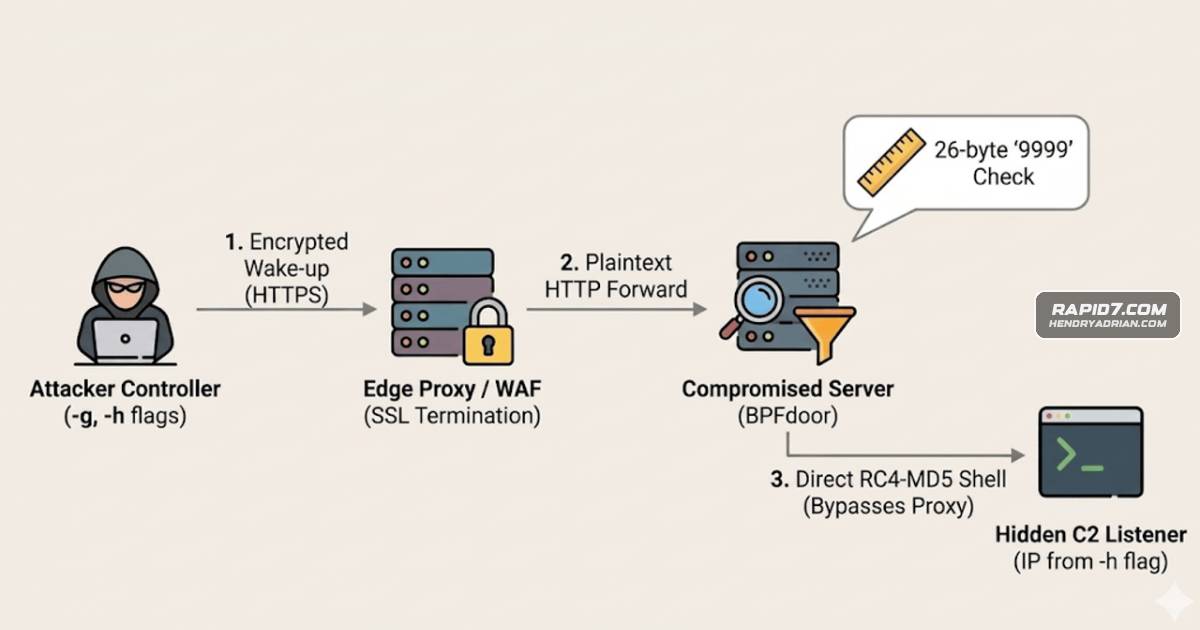
Rapid7 Details BPFDoor and AVERAT Activity Targeting Network-Edge Appliances

Rapid7 analyzes BPFDoor, Rekoobe, and AVERAT samples targeting telecom and mail-security appliances in South Korea and Taiwan, detailing SMTP-based command-and-control, stealth techniques, compromised-device relays, and detection opportunities.

Oct 2, 2026
Threat Research · securityweek.com

Storm-2603 Expands SharePoint Exploitation in Attacks on Critical Infrastructure

Symantec says Storm-2603 continues exploiting SharePoint flaws in attacks on critical infrastructure and other organizations, deploying webshells, tools to disable security software, and Warlock ransomware.

Oct 2, 2026
Threat Research · socket.dev

Socket traces a VS Code theme cluster across marketplaces to GlassWorm-linked malware

Socket links a cluster of VS Code themes across Visual Studio Marketplace and Open VSX to two confirmed malicious extensions, including one assessed as GlassWorm with high confidence. Reported Marketplace extensions were removed.

Oct 2, 2026
Threat Research · thehackernews.com

Researchers Detail Self-Healing WordPress Backdoor With Blockchain-Based C2

Researchers describe SC, a WordPress backdoor that restores itself from files, the database, plugins, and shared memory, and uses Ethereum for C2. Separately, attackers are exploiting the wpForo plugin’s CVE-2026-1581 flaw.

Oct 2, 2026
Threat Research · darkreading.com

Linux Backdoors Mimic South Korean and Taiwanese Mail Security Appliances

Researchers describe Linux backdoors that mimic Asian mail-security appliances, use stealthy command-and-control over SMTP port 25, and exploit compromised edge devices as relays. Suggested detection includes checking for deleted executables and unexpected raw packetส.

Oct 2, 2026
Threat Research · circleid.com

Researchers Trace Fake Installer Campaign Assessed as Consistent with Silver Fox Activity

Researchers analyzed indicators from a Microsoft-tracked fake-installer campaign assessed with moderate confidence as consistent with prior Silver Fox activity, finding related domains and other artifacts. No nation-state attribution has been made.

Oct 2, 2026
Threat Research · netskope.com

Underground Malware Operation Drains Crypto Accounts Through Injected Browser Sessions

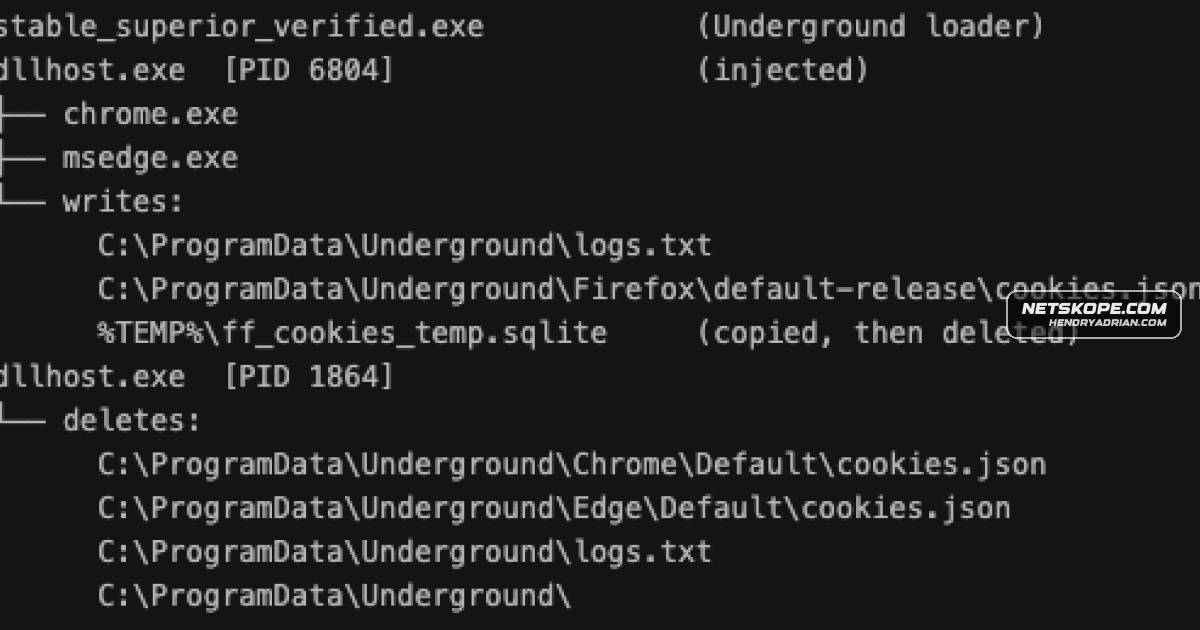
Netskope details an Aotera/Tedy loader delivering a Vidar-class stealer that hijacks browser sessions to drain crypto accounts and replace copied wallet addresses. Researchers estimate about $100,000 stolen from at least 350–430 victims.

Oct 1, 2026
Threat Research · cisecurity.org

CIS Links SLTT Remus C2 Traffic to Three Malware Delivery Chains

CIS CTI traced Remus infostealer activity from March to September 2026 and analyzed three delivery chains. Remus targets browser credentials and sessions, which can help attackers bypass MFA, and supports blockchain-based C2 rotation.

Oct 1, 2026
Threat Research · malwarebytes.com

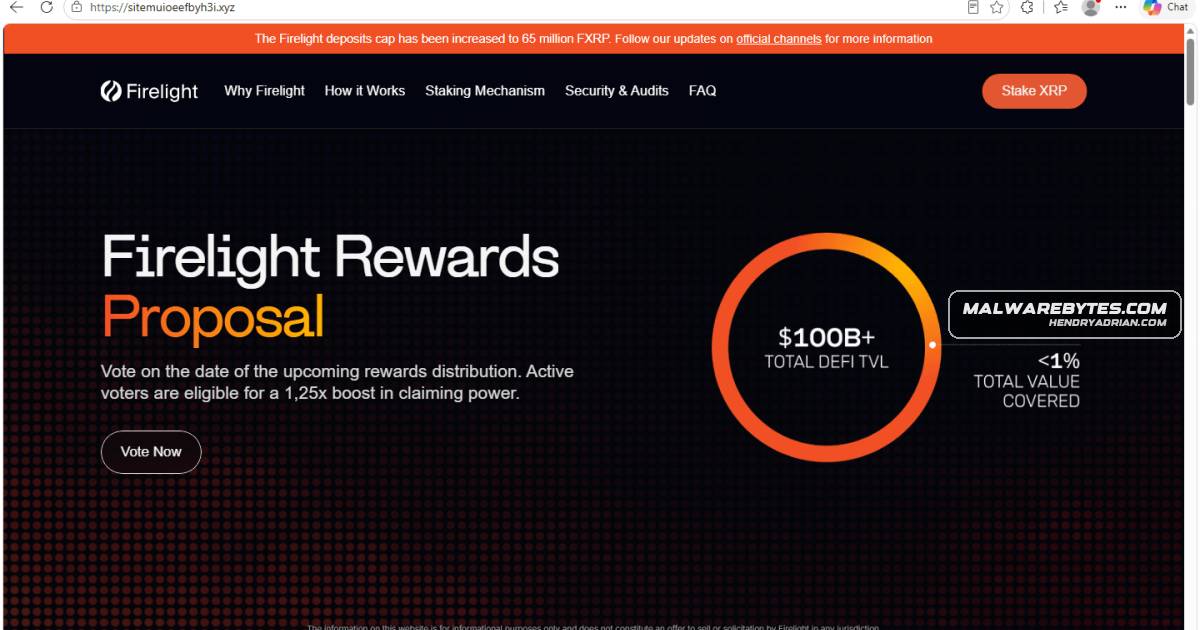
Fake Crypto Rewards-Voting Sites Aim to Drain Users’ Wallets

Malwarebytes found 70 fake crypto-project websites that lure users with rewards votes, then prompt them to connect wallets—potentially leading to malicious signatures or token approvals.

Oct 1, 2026
Threat Research · dti.domaintools.com

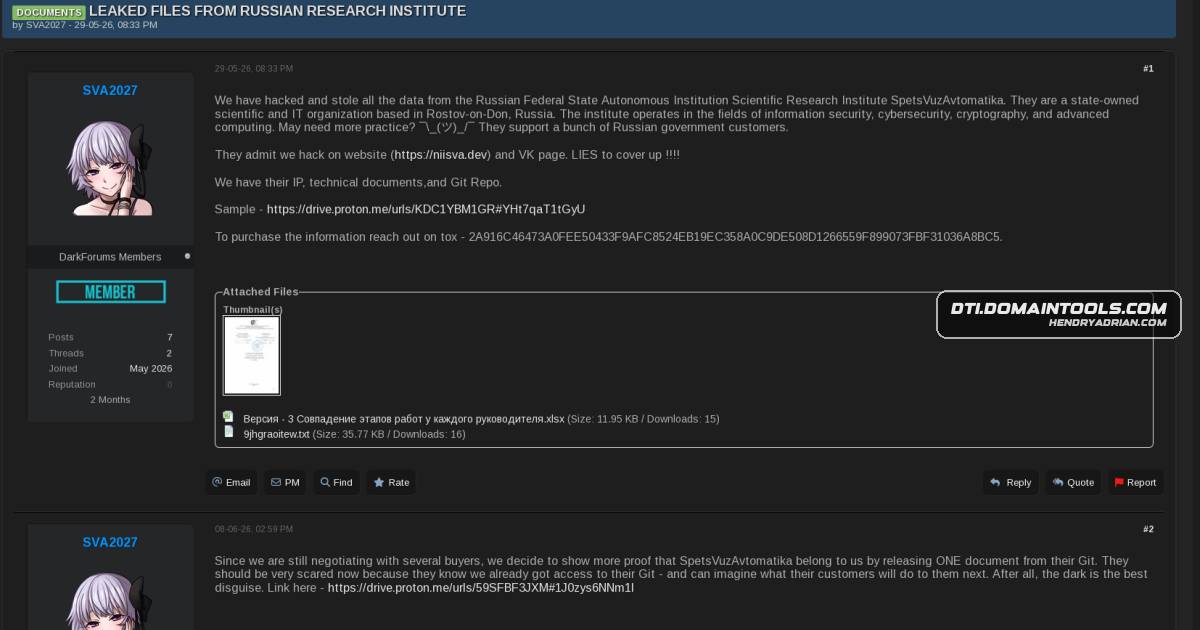
Leak Reveals Russian Institute’s Apparent SVR-Linked Cyber Development Ecosystem

Leaked Spetsvuzavtomatika documents describe tools for reconnaissance, network access, credential theft, data collection and covert operations. The files appear authentic, but do not prove that every capability was deployed or identify how the leak occurred.

Oct 1, 2026
Threat Research · levelblue.com

TIKTOUK Toolkit Collects WordPress, Email, and Cloud Credentials

LevelBlue analyzes TIKTOUK, a toolkit that probes WordPress, retrieves exposed configuration and plugin settings to recover email credentials, and scans JavaScript for secrets. Telemetry and a leaked panel indicate active, large-scale credential collection.

Oct 1, 2026
Threat Research · blog.sucuri.net

SC WordPress Malware Uses Self-Rebuilding Loaders and Blockchain-Controlled Backdoor

Researchers analyzed SC malware that keeps reinfecting WordPress sites through mutually restoring files, database copies, and shared memory. Its backdoor hides an admin account, disables security plugins, and retrieves instructions via public Ethereum RPC gateways.

Oct 1, 2026
PreviousPage 16 of 100 Next
© 2026 cyber.hendryadrian.com