Cling Botnet Exploits Realtek SDK Flaw and Hides C2 in STUN Traffic
Summary
Researchers say Cling botnet operators are exploiting the patched Realtek Jungle SDK flaw CVE-2021-35394 and other device vulnerabilities. The malware uses STUN traffic for command-and-control, persistence, proxying, tunneling, propagation, and DoS attacks.
Key points
- Nozomi Networks observed a rise in attempts to exploit critical RCE flaw CVE-2021-35394 in Realtek Jungle SDK beginning around September 5, 2026; some attempts delivered Cling.
- Cling embeds exploit logic for command-injection and RCE flaws affecting routers and DVRs from multiple vendors, and targets Linux devices across several processor architectures.
- The malware persists by copying itself into system paths and modifying startup files; it can also replace wget while relocating the original binary.
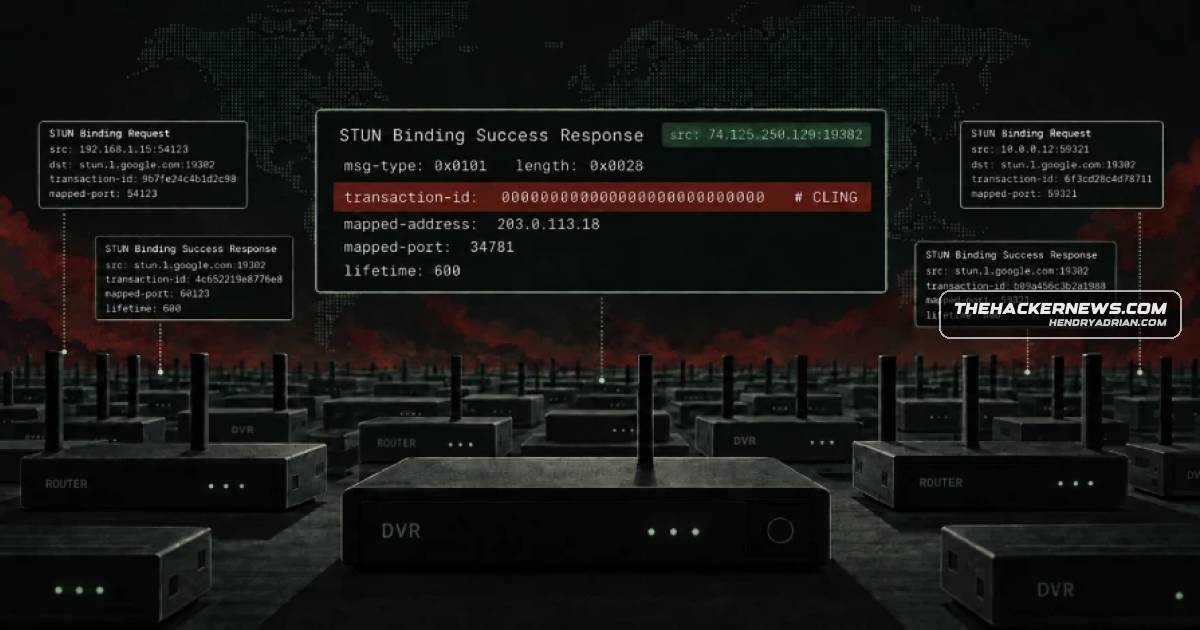
- Cling uses STUN-related traffic to register infected hosts and receive commands. Researchers say one server returned responses tailored to the bot's traffic, and commands appeared to originate from Google's public STUN service.
- Its commands support worm-like propagation, TCP tunneling, proxying, remote control, and denial-of-service attacks.
- Fortinet describes ClingSTUN as a backconnect proxy backdoor that abuses public STUN infrastructure to discover mapped addresses and maintain NAT bindings.
Article Details
- Attack Vectors
- Attempts to exploit CVE-2021-35394 in Realtek Jungle SDK to gain remote code execution and deploy Cling.
- Shell-script downloaders fetch malware payloads for multiple Linux architectures.
- Cling embeds exploits for command-injection and remote-code-execution vulnerabilities in routers and DVRs, enabling self-propagation.
- The malware establishes persistence by copying itself to system paths and modifying init files, or by replacing wget while relocating the original binary.
- Cling uses STUN-like traffic to register infected hosts and receive commands, and can launch proxies, TCP tunnels, and denial-of-service attacks.
- Defensive Notes
- Patch CVE-2021-35394 and other applicable vulnerabilities in internet-facing devices.
- Monitor for Cling-related file and startup changes, including copies named .cling, modifications to init files, and unexpected replacement of wget.
- Investigate unusual STUN traffic, including nonconforming registration messages and unexpected commands embedded in transaction ID fields.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 145[.]249[.]115[.]184 | STUN server reported by Nozomi Networks to return unusual responses and be tailored to Cling's STUN traffic for sending operator commands. |
MITRE ATT&CK
T1037.004 · RC ScriptsCling achieves persistence by appending its executable paths to SysV and BusyBox startup files.T1059.004 · Unix ShellShell-script downloaders are used to fetch malware payloads.T1090 · ProxyCling can launch a proxy and turns infected systems into remotely controlled proxy nodes.T1105 · Ingress Tool TransferShell-script downloaders fetch Cling payloads for different Linux architectures.T1190 · Exploit Public-Facing ApplicationThe malware is delivered after attempts to exploit vulnerabilities in internet-facing devices, including CVE-2021-35394.T1498 · Network Denial of ServiceOperator commands can direct Cling to perform denial-of-service flooding against a specified target.
CVE
Malware
ClingThreat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling.ClingSTUNdevices to establish a persistent foothold. The cybersecurity company has given it the name ClingSTUN.