Rapid7 Details BPFDoor and AVERAT Activity Targeting Network-Edge Appliances
Summary
Rapid7 analyzes BPFDoor, Rekoobe, and AVERAT samples targeting telecom and mail-security appliances in South Korea and Taiwan, detailing SMTP-based command-and-control, stealth techniques, compromised-device relays, and detection opportunities.
Key points
- The research covers a newly observed BPFDoor variant, a BPF Rekoobe build associated with South Korean targets, and six AVERAT builds deployed against Taiwanese appliances.
- AVERAT uses outbound SMTP on port 25, including EHLO and STARTTLS, to disguise encrypted command-and-control traffic as normal mail activity; it can run shells, transfer files, and proxy connections.
- BPFDoor and Rekoobe use raw sockets and BPF filters to detect magic-packet triggers, with process-name spoofing tailored to software found in target environments.
- A dropper stages payloads under ordinary-looking names in /sbin, launches them, then deletes the files while the processes continue running; its watchdog can recreate staging artifacts.
- The AVERAT infrastructure includes compromised NAS, network appliances, and a DVR used as relays. Rapid7 says the device profile matches broader ORB patterns but found no overlap confirming membership in a named ORB network.
- Defenders should investigate unexpected raw packet sockets and BPF filters, unlinked running executables, suspicious port-25 callbacks, process masquerading, and the documented staging paths and process sequence.
Article Details
- Attack Vectors
- A local dropper, run after access was established, stages itself and AVERAT on an appliance, launches both, and deletes the staged files while the processes continue running.
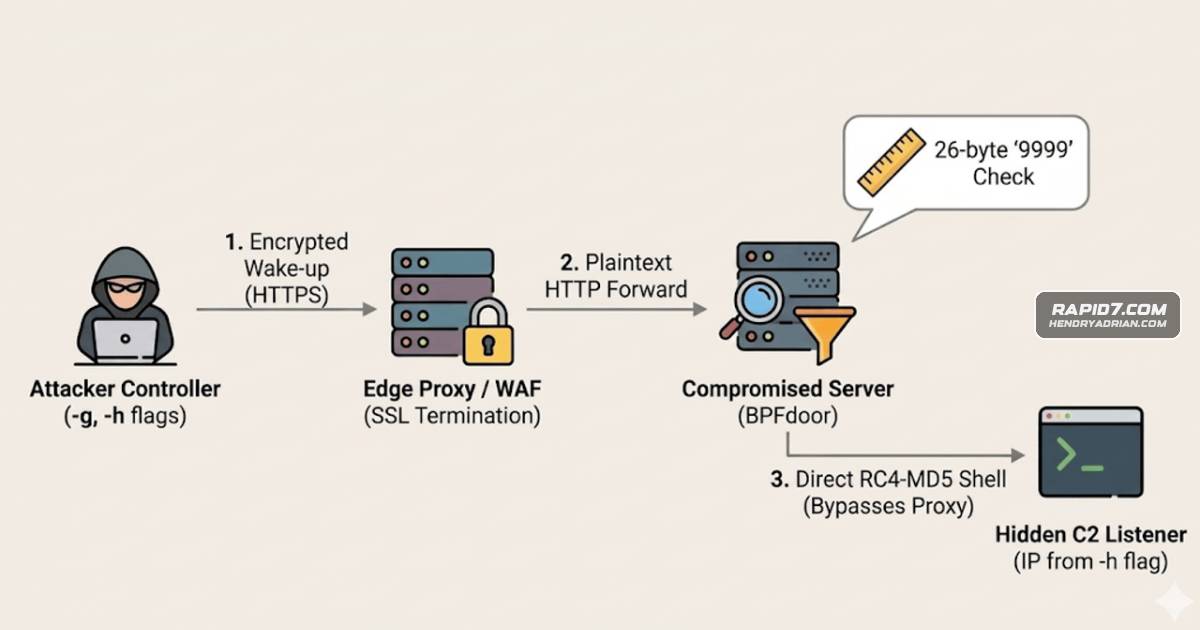
- BPFDoor and Rekoobe use packet filters to wait for specially crafted traffic before opening interactive access. A newer BPFDoor controller can carry its trigger in an HTTPS POST through an edge proxy.
- AVERAT uses outbound SMTP on port 25, requests STARTTLS, and then establishes its own encrypted command-and-control session. Its configured relays are compromised Taiwanese consumer or SMB devices.
- The BPF Rekoobe sample filters for traffic with both source and destination port 25, matching an SMTP relay traffic pattern expected on a SpamSniper appliance.
- Defensive Notes
- Hunt for processes whose /proc/<pid>/exe target ends in (deleted), and inspect executable memory mappings without backing files.
- Alert on the appliance staging directory, a shell script with a .php extension, watchdog markers, and the sequence of copying binaries into /sbin, executing them, and deleting them roughly ten seconds later.
- Investigate unexpected raw packet sockets and classic BPF filters, and review outbound port-25 connections from processes that are not mail services.
- Preserve short-lived staged binaries and collect process arguments, open file descriptors, socket metadata, and historical DNS records.
- Restrict management access to routers, DVRs, and other edge appliances; monitor NFS or SMB mounts that could permit an adjacent host to write executables.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| HOSTNAME | mx[.]zxopfds[.]com | AVERAT command-and-control hostname. |
| HOSTNAME | mx1[.]wwstifsteel[.]com | AVERAT command-and-control hostname. |
| HOSTNAME | spam[.]suwaccqi[.]com | AVERAT command-and-control hostname. |
| IPV4 | 1[.]34[.]200[.]85 | Compromised third-party Dahua recorder used as an AVERAT C2 relay. |
| IPV4 | 122[.]116[.]138[.]33 | Compromised third-party embedded appliance used as an AVERAT C2 relay. |
| IPV4 | 59[.]125[.]211[.]65 | Compromised third-party Synology NAS used as an AVERAT C2 relay. |
| SHA256 | 2bedc26d4b29b435c21962beed7db21188a0219a0d28334bba8b4fb1656d7b15 | ShareTech-appliance dropper hash. |
| SHA256 | 2fe2dd402ee6f9c578fce6dd4b36daaa407e99133e5dd502f2afca80feb60150 | AVERAT implant hash. |
| SHA256 | 4435fcd6862921092614dbeaa880e4192352984686ebcd98f0ba13ee8e226ef9 | Data-plane BPFDoor sample hash. |
| SHA256 | 4925bcca085ec504f51191645da278d8e96698d91f3c6df44146336c697b4de8 | AVERAT implant hash. |
| SHA256 | 652508a9cf40bee883dc0e5e219dfeba71fe7dac591d01c89f74c21f73b4963f | Rekoobe backdoor hash; its BPF filter matches traffic using port 25 in both directions. |
| SHA256 | 7e667ba5f9df912e02275d3cfe3809d16f822fe776f4035c84b118ebd925b1b5 | SpamSniper-disguised BPFDoor sniffer hash. |
| SHA256 | 925c041807d4fb9dfe2ad84f963c2a4c60ea1289f6a0bdccbfb944478ffc2cf2 | AVERAT implant hash. |
| SHA256 | a37ea9897221d4495b538de72b74f2aa1d2ff09b7b6dcedd395aee58931adbf3 | SpamSniper-disguised BPFDoor sniffer hash. |
| SHA256 | a4379e115d3c4420f5d4b92561022d6e0897990e7297be65c033d47de68e6a6a | AVERAT implant hash. |
| SHA256 | a65048eb30661e27f8edc2dd8d8c77ec87faec1f1750f6e04e7ecaf069a32858 | AVERAT implant hash. |
| SHA256 | a6f3b7f932761fb1fd5e74123f2482e36c65dd13e769af2ce08c65da195bfa7a | Data-plane BPFDoor sample hash. |
| SHA256 | bf8135f46ecedfe5bd06fcecbb2e721c2367ff765b18f4aa3f868e6597f49e47 | AVERAT implant hash. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryAVERAT check-ins report network interfaces.T1027 · Obfuscated Files or InformationBPFDoor hides strings with a rotating substitution alphabet, while AVERAT keeps operational configuration in an encrypted blob.T1027.013 · Encrypted/Encoded FileThe dropper carries encrypted blobs containing paths and a script; AVERAT stores keys, hosts, ports, and timing state in an encrypted configuration blob.T1033 · System Owner/User DiscoveryAVERAT check-ins report the current user and logged-in users.T1036.004 · Masquerade Task or ServiceBPFDoor and Rekoobe samples rewrite their process identities to resemble Linux or appliance-specific daemons.T1036.005 · Match Legitimate Resource Name or LocationThe dropper stages malicious binaries in /sbin as ntpdate and udevds before executing them.T1037 · Boot or Logon Initialization ScriptsRapid7 says the dropper's location in the appliance add-on package directory makes relaunch by firmware package startup at boot very likely.T1041 · Exfiltration Over C2 ChannelAVERAT supports downloading files from an infected host over its command-and-control connection.T1057 · Process DiscoveryAVERAT can enumerate running processes and their command lines.T1059.004 · Unix ShellThe dropper executes a shell script that stages its payloads; AVERAT can also open interactive shell sessions.T1070.003 · Clear Command HistoryThe Rekoobe-based sample sets HISTFILE=/dev/null and zeroes history-size variables to prevent commands from entering shell history.T1070.004 · File DeletionThe dropper's script deletes both staged /sbin binaries about ten seconds after launching them.T1071.003 · Mail ProtocolsAVERAT connects outbound on port 25, issues EHLO, and requests STARTTLS before its encrypted C2 session.T1082 · System Information DiscoveryAVERAT check-ins report the host's name and OS version.T1083 · File and Directory DiscoveryAVERAT commands enumerate directory contents and recursively walk directory trees.T1090 · ProxyAVERAT can open a proxy or port-forward channel through an infected appliance.T1105 · Ingress Tool TransferAVERAT supports uploading files to an infected host in chunks.T1129 · Shared ModulesAVERAT has a command to load or unload a shared-object module.T1133 · External Remote ServicesAll three AVERAT relays expose PPTP on port 1723; Rapid7 assesses the matching PPTP service as operator-installed for VPN access.T1140 · Deobfuscate/Decode Files or InformationThe dropper decrypts its embedded blobs to obtain staging paths and a script; AVERAT decrypts its operational configuration.T1205 · Traffic SignalingBPFDoor waits for magic packets, including triggers carried in crafted HTTPS POST requests through edge proxies.T1205.002 · Socket FiltersBPFDoor and BPF Rekoobe attach packet filters that select specially crafted trigger traffic before the implants respond.T1480 · Execution GuardrailsThe dropper takes its installation branch only if /tmp/flag exists and its .php staging script does not.T1529 · System Shutdown/RebootAVERAT has a command to reboot the appliance after flushing filesystem buffers.T1562.004 · Disable or Modify System FirewallThe data-plane BPFDoor samples contain iptables NAT-redirect staging and teardown logic.T1564.001 · Hidden Files and DirectoriesAVERAT stores its callback interval in a hidden state file such as /var/lib/.db.T1573.001 · Symmetric CryptographyAVERAT establishes an encrypted session after STARTTLS using shared secrets; the Rekoobe-based sample uses AES-CBC for its command interface.T1584.008 · Network DevicesThe article identifies three compromised NAS, embedded-appliance, and recorder hosts repurposed as AVERAT C2 relays.
Malware
AVERATRekoobe build seen against South Korean targets, a dropper, and six builds of a Linux implant we track as AVERAT, deployed against Taiwanese appliances. Additionally, we provide source code details of the Rapid7BPFDoorsoftware and device conventions of the telecom environments they target. The set spans a newly observed BPFDoor variant, a BPF Rekoobe build seen against South Korean targets, a dropper, and six builds of a LinuxRekoobeof the telecom environments they target. The set spans a newly observed BPFDoor variant, a BPF Rekoobe build seen against South Korean targets, a dropper, and six builds of a Linux implant we track as AVERAT,
Vendors
DahuaNetKlass Technology certificate valid from 2004 to 2014, MD5-signed with a 1024-bit key. 1.34.200.85 is a Dahua DH-XVR5116HS-I3 recorder. These are victim hosts repurposed as operational relays, selected on consistentNetKlass Technologyinterface, HTTP Basic realms named SMB on 8081, 8082 and 10443, and a self-signed NetKlass Technology certificate valid from 2004 to 2014, MD5-signed with a 1024-bit key. 1.34.200.85 is a DahuaShareTechThe dropper derives its encryption key from the string ShareTech and lives in the appliance's own add-on package directory. The BPFDoor variants seen against South Korean systems impersonate the PID file of SpamSniper,Synology59.125.211.65 is a Synology NAS belonging to a Taiwanese fuel-retail business, still serving a Laravel-based "cloud management system" on 81/82 behind a Let's Encrypt certificate that expired in October 2021, alongside
Products
Dahua DH-XVR5116HS-I3Technology certificate valid from 2004 to 2014, MD5-signed with a 1024-bit key. 1.34.200.85 is a Dahua DH-XVR5116HS-I3 recorder. These are victim hosts repurposed as operational relays, selected on consistentSpamSniperpackage directory. The BPFDoor variants seen against South Korean systems impersonate the PID file of SpamSniper, a Korean anti-spam product, and rotate through ten Linux daemon names. Across the samples, each
Tools
Rapid7 BPFDoor controllerdeployed against Taiwanese appliances. Additionally, we provide source code details of the Rapid7 BPFDoor controller introduced in our April 2026 blog, Stealthy BPFDoor Variants are a Needle That Looks Like Hay.Tiny Shellas legitimate on hosts actually running that class of infrastructure. Once triggered, it opens a stock Tiny Shell session and dispatches single-byte 'S'/'U'/'D' commands — interactive shell, upload, download — the