Underground Malware Operation Drains Crypto Accounts Through Injected Browser Sessions
Summary
Netskope details an Aotera/Tedy loader delivering a Vidar-class stealer that hijacks browser sessions to drain crypto accounts and replace copied wallet addresses. Researchers estimate about $100,000 stolen from at least 350–430 victims.
Key points
- Victims are infected through lure archives containing setup.exe, a trojanized DLL, and encrypted data; how the archives are distributed is unknown.
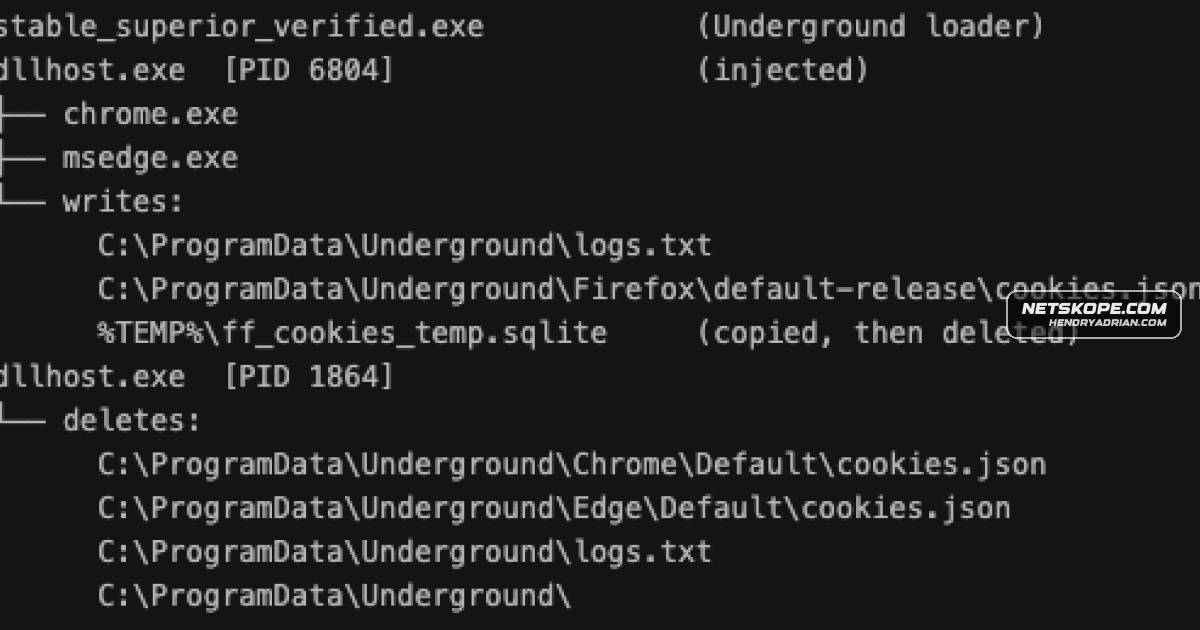
- The loader injects its payload into dllhost.exe, then launches Chrome or Edge under the victim’s profile to access authenticated sessions.
- The Vidar-class stealer collects browser credentials, cookies, messaging data, wallet information, and screenshots.
- Injected scripts drain Binance accounts by disabling withdrawal allow lists, converting balances to Bitcoin, and withdrawing funds; webmail injections disguise confirmation messages.
- A clipboard clipper replaces copied wallet addresses with operator-controlled addresses across multiple cryptocurrencies.
- The campaign uses rotating Cloudflare-fronted gates, including quick-neo[.]com, and a custom /api/machine/* protocol.
- Researchers estimate roughly $100,000 in proceeds and at least 350–430 victims. Blocking a gate does not remove the implant; Netskope recommends endpoint checks and behavioral URI detection.
Article Details
- Attack Vectors
- Victims open versioned 7z or zip lure archives containing setup.exe, a trojanized msys-crypto-3.dll, and encrypted data.bin; how the archives reach victims is unknown.
- The loader injects a self-decrypting payload into suspended dllhost.exe, which launches Chrome or Edge under the victim's browser profile and injects scripts into authenticated sessions.
- Injected browser scripts automate cryptocurrency exchange account draining and disguise withdrawal-confirmation emails in webmail.
- A clipboard clipper replaces copied cryptocurrency wallet addresses with operator-controlled addresses.
- Defensive Notes
- Treat contact with a blocked gate as an active infection; blocking network traffic does not remove the implant.
- Hunt for dllhost.exe injection, Chrome or Edge launched by dllhost.exe, /api/machine/* requests, and files or PNG-named artifacts associated with C:ProgramDataUnderground and AppDataLocal.
- Use behavioral URI detection alongside domain reputation because the operator rotates gate domains.
- Verify exchange withdrawals through a separate channel because injected webmail scripts can rewrite confirmation messages.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | easybooters[.]com | Operator log endpoint domain used to report account-drain steps. |
| DOMAIN | quick-neo[.]com | Rotating gate domain used by the malware's command-and-control protocol. |
| DOMAIN | slow-sky[.]com | Rotating malicious gate domain serving the operator's configuration. |
| DOMAIN | true-lie[.]com | Rotating gate domain used by the operation. |
| IPV4 | 95[.]164[.]53[.]76 | Underground loader telemetry panel used to record loader-stage events. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/048466C5/startCrypt | Loader telemetry URL used to report a startCrypt event. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/29A5FDA7/failed/1769331221 | Loader telemetry URL used to report a failed stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/29A5FDA7/startLoader/1769331211 | Loader telemetry URL used to report a startLoader event. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/8320e1a4/startloader/1767499038 | Loader telemetry URL used to report a startloader event. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/8320E1A4/success/1767499039 | Loader telemetry URL used to report a successful stage. |
| URL | hxxp[:]//95[.]164[.]53[.]76/new/log/D9D278DD/success/1696492954 | Loader telemetry URL used to report a successful stage. |
| URL | hxxps[:]//easybooters[.]com/newlog[.]php | Operator log endpoint identified in the deobfuscated Binance-drain configuration. |
MITRE ATT&CK
T1055 · Process InjectionThe loader injects a self-decrypting payload into suspended dllhost.exe and injects scripts into browser sessions.T1057 · Process DiscoveryThe loader compares running processes against a hard-coded list of analysis and monitoring processes.T1105 · Ingress Tool TransferThe setup binary launches the loader, which stages components from the lure archive.T1119 · Automated CollectionThe stealer automatically collects browser cookies and passwords, messaging data, wallet data, and screenshots.T1204 · User ExecutionInfection begins when the victim opens a lure archive containing setup.exe.T1497.001 · System ChecksThe loader checks for virtual-machine and sandbox agents as part of its anti-analysis behavior.T1518.001 · Security Software DiscoveryThe loader checks for debugging, monitoring, and network-analysis tools, including IDA, Wireshark, and Process Explorer.T1562.001 · Disable or Modify ToolsThe injected exchange script disables the withdrawal allow list before draining funds.
Malware
AoteraNetskope Threat Labs uncovered the Underground builder, an Aotera/Tedy-based operation that injects a Vidar-class stealer into Windows processes and uses browser-session injection to drain cryptocurrency exchangeTedyNetskope Threat Labs uncovered the Underground builder, an Aotera/Tedy-based operation that injects a Vidar-class stealer into Windows processes and uses browser-session injection to drain cryptocurrency exchangeVidarNetskope Threat Labs uncovered the Underground builder, an Aotera/Tedy-based operation that injects a Vidar-class stealer into Windows processes and uses browser-session injection to drain cryptocurrency exchange
Vendors
Products
Binance#UndergroundCloudflareThe campaign rotates Cloudflare-fronted gates, abuses Chrome or Edge sessions, and has generated about $100,000 in on-chain proceeds from at least 350 to 430 victims.EdgeThe campaign rotates Cloudflare-fronted gates, abuses Chrome or Edge sessions, and has generated about $100,000 in on-chain proceeds from at least 350 to 430 victims.GmailAPI paths, and withdraws the funds to an 11-address Bitcoin reserve pool. A webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords inGoogle ChromeThe campaign rotates Cloudflare-fronted gates, abuses Chrome or Edge sessions, and has generated about $100,000 in on-chain proceeds from at least 350 to 430 victims.Outlookand withdraws the funds to an 11-address Bitcoin reserve pool. A webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24Protonthe funds to an 11-address Bitcoin reserve pool. A webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages, andYahoowithdraws the funds to an 11-address Bitcoin reserve pool. A webmail injection covering Gmail, Outlook, Yahoo, and Proton then watches for the exchange’s withdrawal confirmation, using keywords in about 24 languages,
Tools
Burp Suiteradare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machineCharlesdnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), andCutteror monitoring environment. The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, BurpdnSpyan analysis or monitoring environment. The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles,FiddlerOllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio),Fridadebuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor,IDASoftware Discovery – The loader checks for debugging, monitoring, and network-analysis tools such as IDA, Wireshark, and Process Explorer (‘covers debuggers and disassemblers … network sniffers … processOllyDbgdetect an analysis or monitoring environment. The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler,PEStudioFiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware, VirtualBox, QEMU guest tools).Pinand disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, ProcessProcess ExplorerThe loader checks for debugging, monitoring, and network-analysis tools such as IDA, Wireshark, and Process Explorer (‘covers debuggers and disassemblers … network sniffers … process monitors’)Process Hacker(Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware, VirtualBox, QEMU guest tools).Process Monitor(Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite), process monitors (Process Monitor, Process Explorer, Process Hacker, PEStudio), and virtual-machine and sandbox agents (VMware,radare2environment. The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark, Fiddler, Charles, Burp Suite),WiresharkDiscovery – The loader checks for debugging, monitoring, and network-analysis tools such as IDA, Wireshark, and Process Explorer (‘covers debuggers and disassemblers … network sniffers … process monitors’)x64dbgto detect an analysis or monitoring environment. The list covers debuggers and disassemblers (IDA, x64dbg, OllyDbg, dnSpy, Cutter, radare2), instrumentation frameworks (Frida, Pin), network sniffers (Wireshark,