cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2381 articles

Threat Research · malwarebytes.com

BlueKit Phishing Kit Steals Sessions and Uses AI to Help Launch Attacks in 10 Minutes

Malwarebytes researchers detail BlueKit, a phishing-as-a-service toolkit with templates for 97 brands, SMS delivery, session and device-data theft, and an AI assistant. Operators claim attackers can set up a phishing site in about 10 minutes.
Oct 7, 2026
Threat Research · thehackernews.com

Fake Cloudflare Checks on 100+ Compromised Websites Deliver LunexStealer

CERT-UA says UAC-0277 compromised more than 100 websites to show fake Cloudflare checks that trick visitors into running commands and installing LunexStealer, which can steal browser data and access files.

Oct 7, 2026
Threat Research · huntress.com

Phishing Campaign Uses Power BI to Deliver Rogue ScreenConnect Clients

Huntress traced a phishing campaign abusing Power BI links to fingerprint targets and install multiple rogue ScreenConnect clients. The tools enabled persistent access; a retroactive hunt linked one client configuration to 22 other endpoints.

Oct 7, 2026
Threat Research · infostealers.com

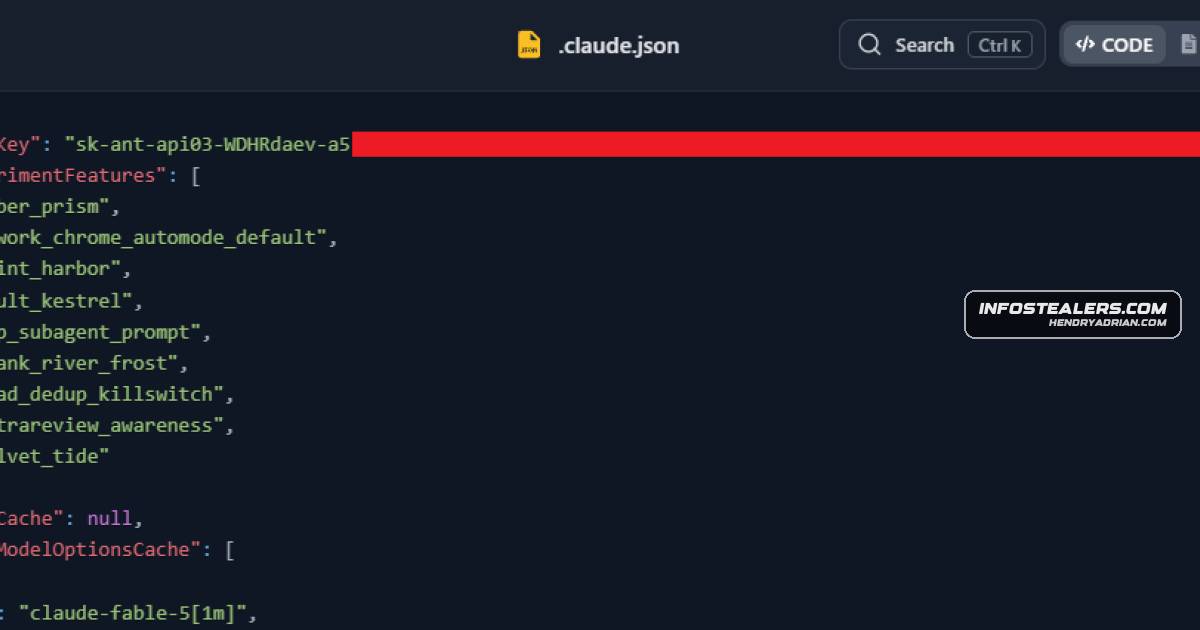
Warden Infostealer Targets AI Coding Tools, Developer Credentials and Crypto Wallets

Warden Stealer is reported to target credentials and data from browsers, AI coding tools, developer environments, and cryptocurrency wallets. The article describes its collection, evasion, and wallet-bruteforcing capabilities.

Oct 7, 2026
Threat Research · crowdstrike.com

CrowdStrike Details ARTEX-Enabled Attacks on South Korean Financial Organizations

CrowdStrike linked infrastructure and Claude Code artifacts to a late September–early October 2026 campaign targeting South Korean financial organizations, where data was reportedly exfiltrated using ARTEX and LLMs.

Oct 7, 2026
Threat Research · ccb.belgium.be

The Gentlemen Ransomware Group Scales Through Affiliates and Pre-Compromised FortiGate Access

The Russian-speaking Gentlemen ransomware operation has rapidly expanded since splitting from Qilin, using an affiliate-friendly platform and a reported pool of pre-compromised FortiGate devices and VPN credentials to enable intrusions.

Oct 7, 2026
Threat Research · cofense.com

Fake Hotel Guest Complaints Deliver EtherRAT and TONResolver via Blockchain-Based C2

Cofense details campaigns targeting hotel staff with fake guest complaints that deliver EtherRAT or TONResolver. The malware retrieves changeable C2 addresses from public blockchains, complicating conventional infrastructure takedowns.

Oct 7, 2026
Threat Research · bleepingcomputer.com

PoeLLM Malware Targets Exposed AI Servers in Cryptomining Campaign

PoeLLM has compromised more than 3,400 exposed servers, using an unusual poem-based method to retrieve C2 addresses and turning infected systems into cryptomining hosts, scanners, and exploit launchpads.

Oct 7, 2026
Threat Research · thehackernews.com

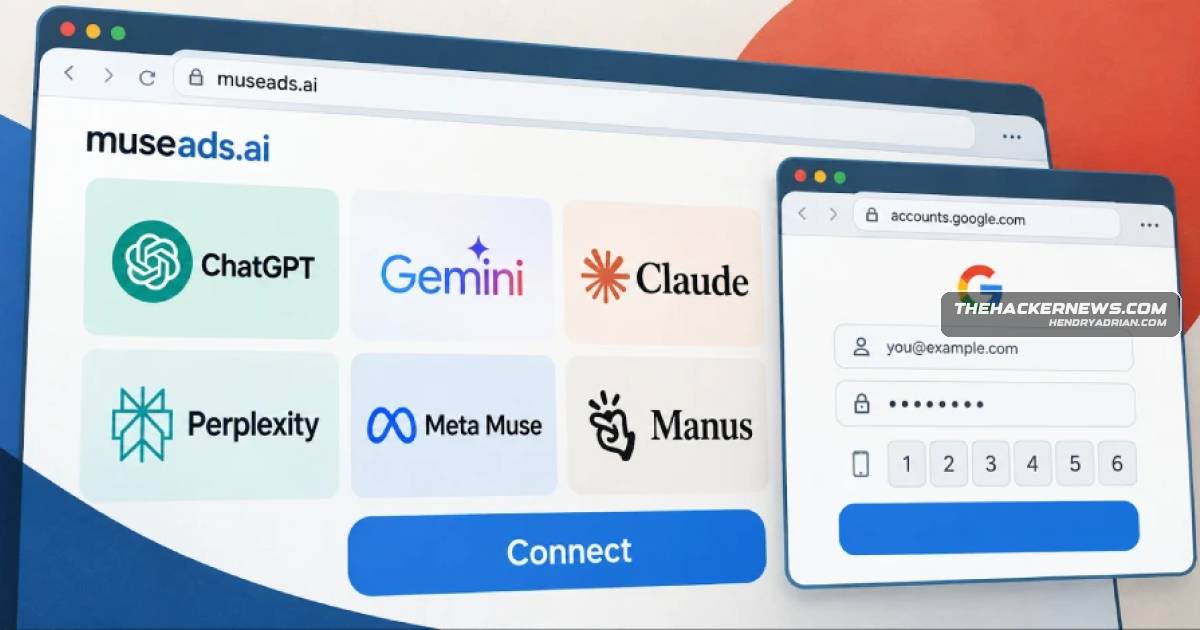
Phishing Platform Uses Fake AI Ad Portals to Steal Credentials and MFA Codes

Researchers say a human-operated phishing platform impersonates AI advertising tools, using fake in-browser login windows to steal credentials and MFA codes from targeted business and advertising accounts.

Oct 6, 2026
Threat Research · thehackernews.com

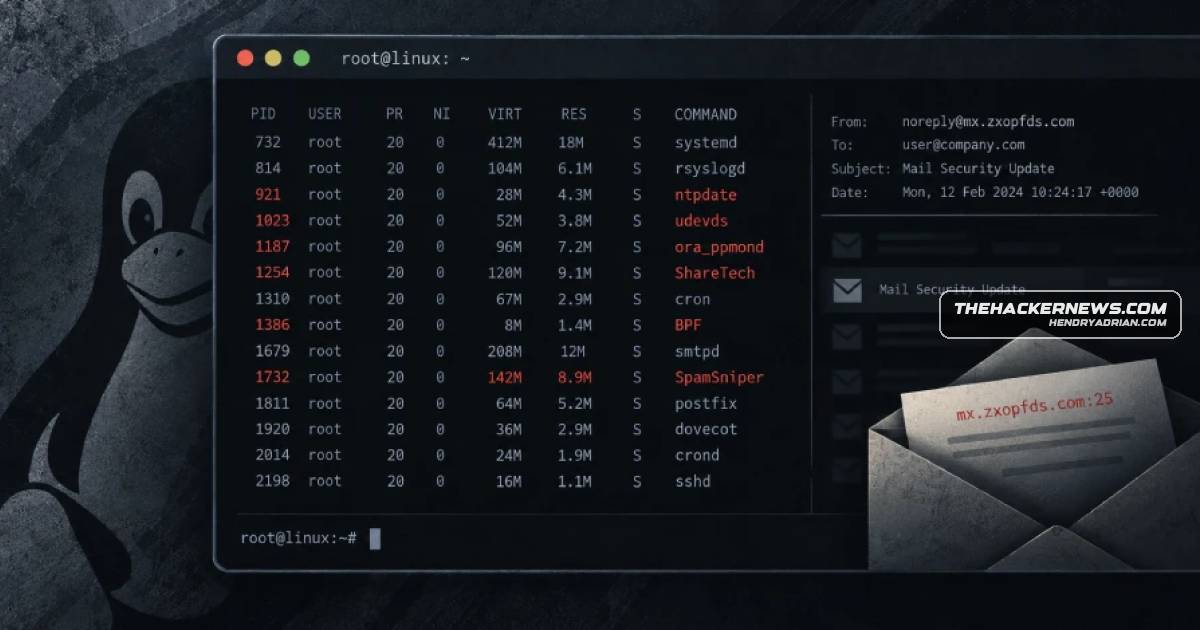
Linux Backdoors Masquerade as Email Security Tools on South Korean and Taiwanese Appliances

Rapid7 describes BPFDoor, Rekoobe, and a newly reported implant called AVERAT targeting telecom and network appliances in South Korea and Taiwan, using trusted product names and email-like traffic to evade detection.

Oct 6, 2026
Threat Research · socradar.io

CyberXero Used AI-Assisted Campaigns to Target Ukrainian Critical Infrastructure

Researchers uncovered CyberXero, a financially motivated access broker using AI-assisted tools in global campaigns and targeted operations against Ukrainian energy organizations. An exposed directory revealed infrastructure, session logs, and data from more than 628,000

Oct 6, 2026
Threat Research · ic3.gov

FBI and Secret Service Detail FortiBleed Campaign Targeting Exposed Fortinet Gateways

An FBI and Secret Service advisory describes a global campaign using reused or leaked credentials to compromise exposed Fortinet gateways, with possible administrator lockouts and ransomware access. It recommends credential resets, MFA, and restricted management access.

Oct 6, 2026
Threat Research · unit42.paloaltonetworks.com

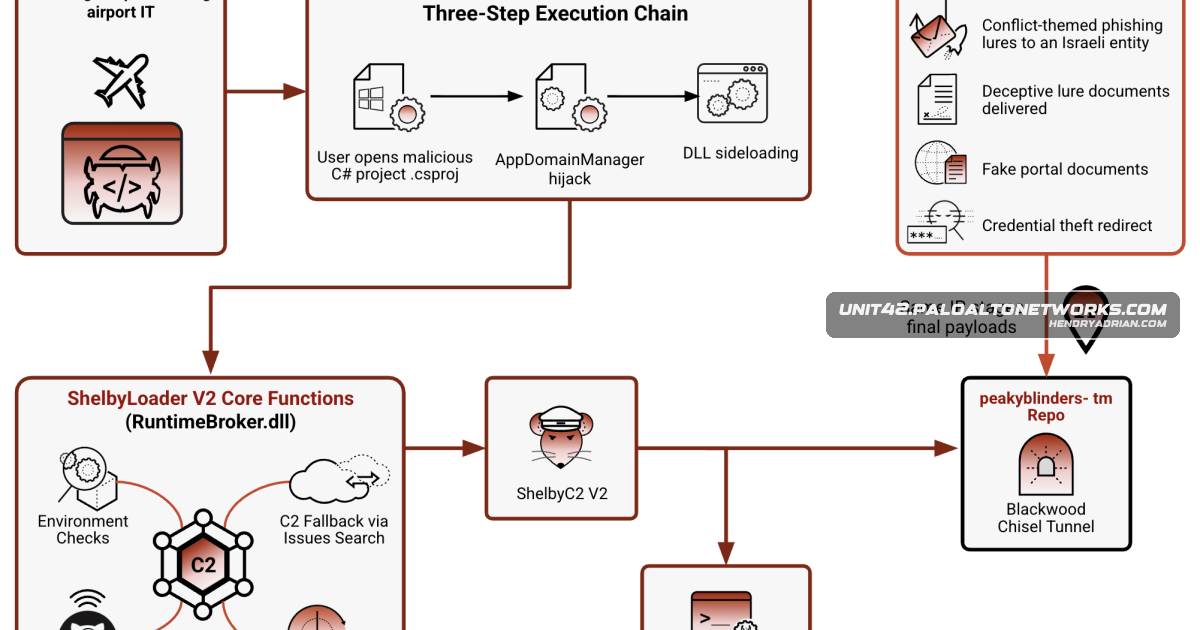
Iranian-Aligned Blinder Tunnel Campaign Targets Iraqi Critical Infrastructure

Unit 42 details a campaign that used fake Dubai Airports recruitment lures and a trojanized Visual Studio project to target an Iraqi infrastructure-sector individual, deploying malware that used GitHub for command and control.

Oct 6, 2026
Threat Research · thehackernews.com

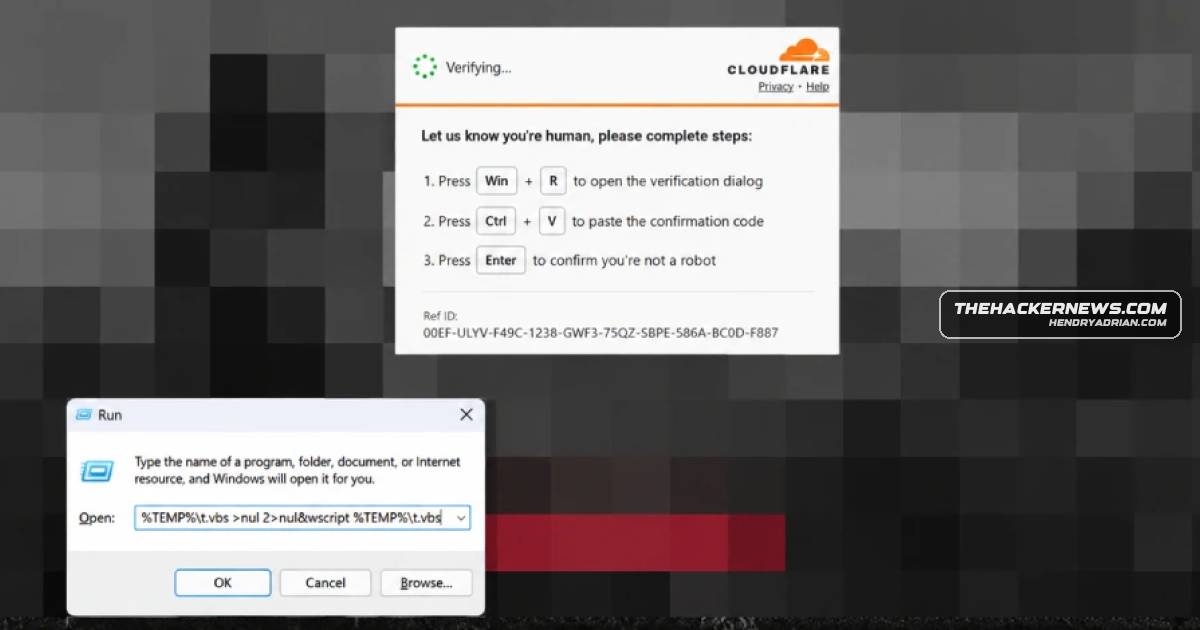
ClickFix Attack Hides Malware in Browser Cache to Bypass Windows Run Limits

Microsoft describes a ClickFix attack that stages a VBScript payload in browser cache to evade Windows Run’s input limit, then uses PowerShell and in-memory malware to target browser and device credentials.

Oct 6, 2026
Threat Research · hunt.io

Hunt.io Maps BraZetsu Access-Broker Infrastructure Across Two VPS Providers

Hunt.io used certificate, DNS and scan data to link BraZetsu-associated panel and C2 infrastructure across Contabo and Njalla VPSs. The services went quiet in June; the researchers recommend hunting naming and port patterns.

Oct 6, 2026
Threat Research · huntress.com

Huntress Reconstructs an Akira Ransomware Attack from Forensic Artifacts

Huntress analysts reconstructed parts of an Akira ransomware attack using endpoint artifacts after its agent was installed post-compromise, limiting telemetry. They traced RDP access, antivirus shutdown, suspected credential dumping, tunneling and file-encryption clues.

Oct 6, 2026
Threat Research · bleepingcomputer.com

Fake ChatGPT, Gemini and Other AI Sites Steal Ad Account Credentials and MFA Codes

Researchers uncovered a phishing campaign using fake AI sites and browser-in-the-browser login windows to steal advertising account credentials and MFA codes from agency staff, media buyers and administrators.

Oct 6, 2026
Threat Research · any.run

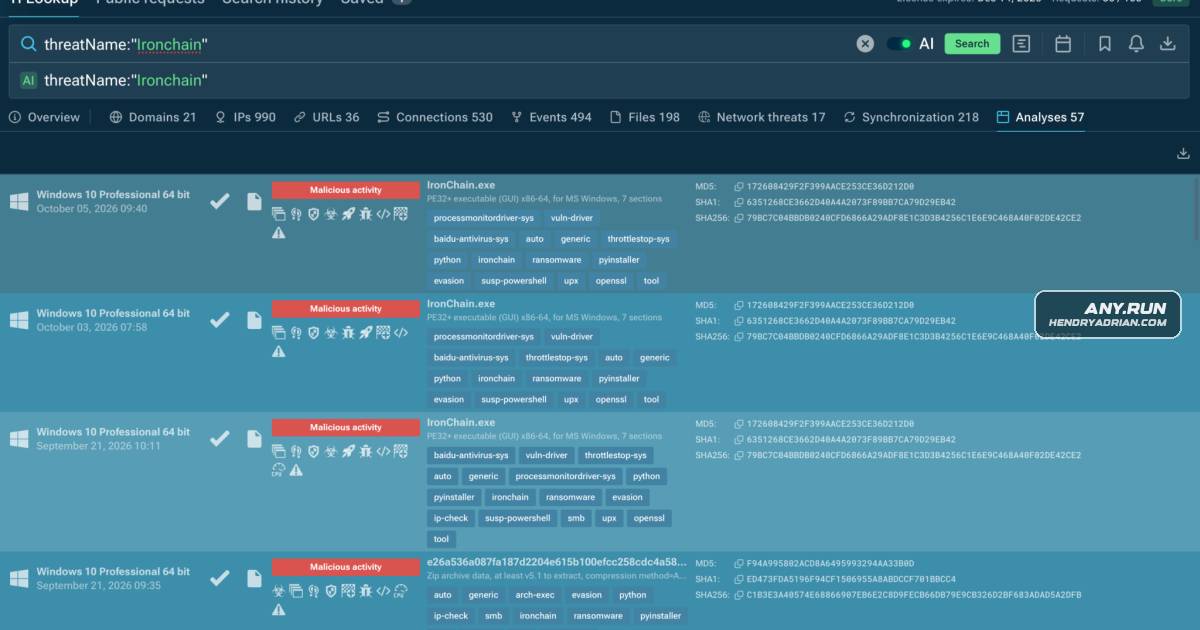
IronChain Ransomware’s Encryption Design May Make Files Unrecoverable

Analysis of a September 2026 IronChain build finds encryption that lacks the key material needed for reliable restoration, four bundled drivers but only one matching process-kill interface, and code flaws that alter execution and file targeting.

Oct 6, 2026
Threat Research · crowdstrike.com

CrowdStrike Researchers Show How Attackers Can Bypass LLM Safety Classifiers

CrowdStrike researchers found that attackers can split harmful tasks into benign requests to a protected LLM, then use an unfiltered model to reassemble the answers into offensive code. The approach worked in 9 of 10 tested categories.

Oct 6, 2026
Threat Research · securitylabs.datadoghq.com

How Attackers Test Stolen AWS Keys for Amazon Bedrock Access

Datadog researchers detail tools that validate AWS credentials for Bedrock access by enumerating models and attempting inference. They observed similar activity at 12 organizations and recommend investigating unexpected Bedrock API calls.

Oct 6, 2026
Threat Research · helpnetsecurity.com

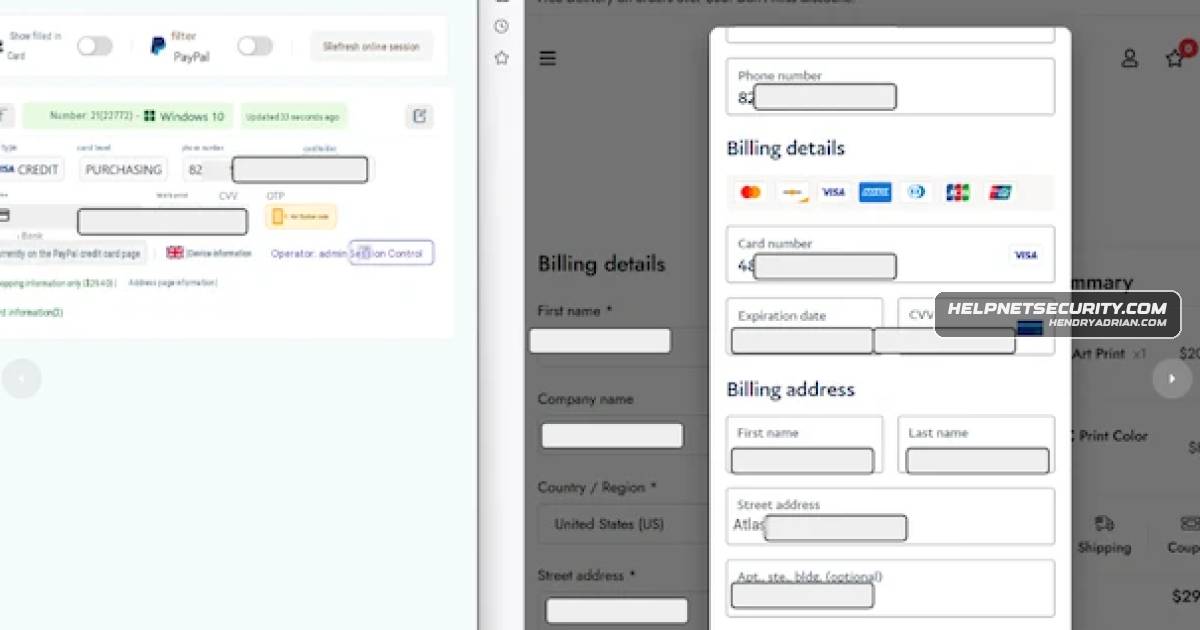
Milk Dragon Phishing Kit Uses Fake Social Media Discounts to Steal Cards and OTPs

Group-IB says the Milk Dragon kit uses fake Facebook and TikTok discounts to direct shoppers to stores that capture payment card details and one-time passwords, with 258 phishing pages linked to victims in 66 countries.

Oct 5, 2026
Threat Research · securityweek.com

ClingSTUN Linux Backdoor Uses STUN for Proxying and Exploits Dozens of Flaws

FortiGuard Labs reports that the ClingSTUN Linux backdoor exploits dozens of flaws to spread, persists across reboots, and uses STUN servers to maintain proxy connections and receive remote commands.

Oct 5, 2026
Threat Research · feeds.fortinet.com

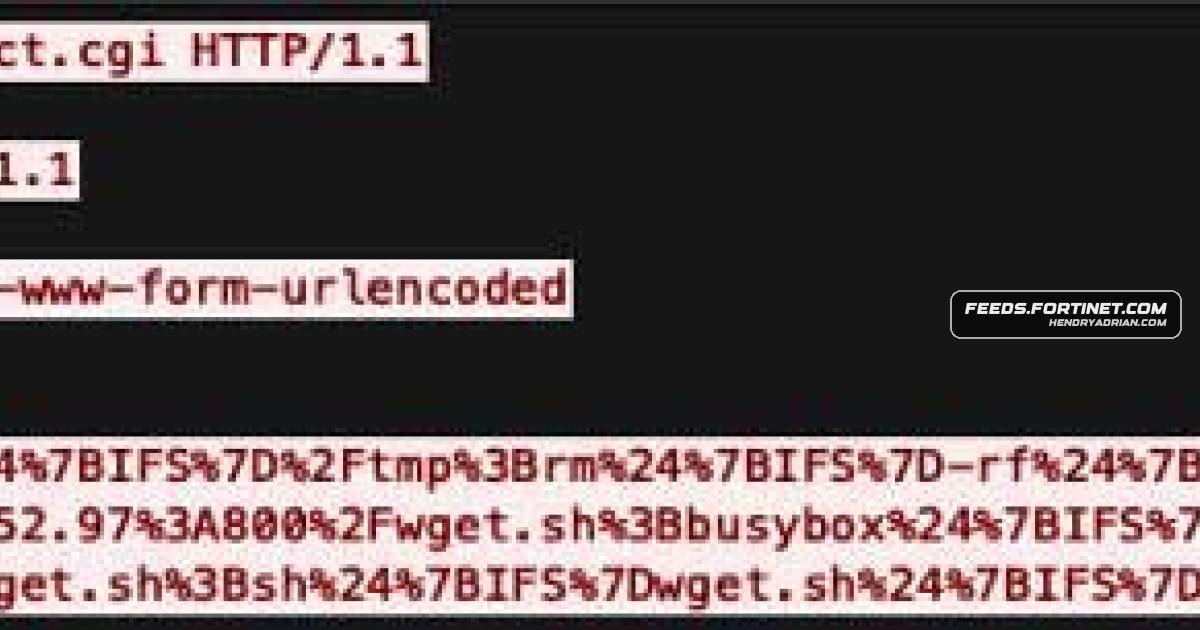
ClingSTUN Linux Backdoor Abuses Public STUN Services to Control Compromised IoT Devices

Fortinet details ClingSTUN, a persistent Linux backdoor that exploits unpatched IoT-device vulnerabilities, uses public STUN services for NAT traversal, and turns compromised systems into remotely controlled proxy nodes.

Oct 5, 2026
Threat Research · levelblue.com

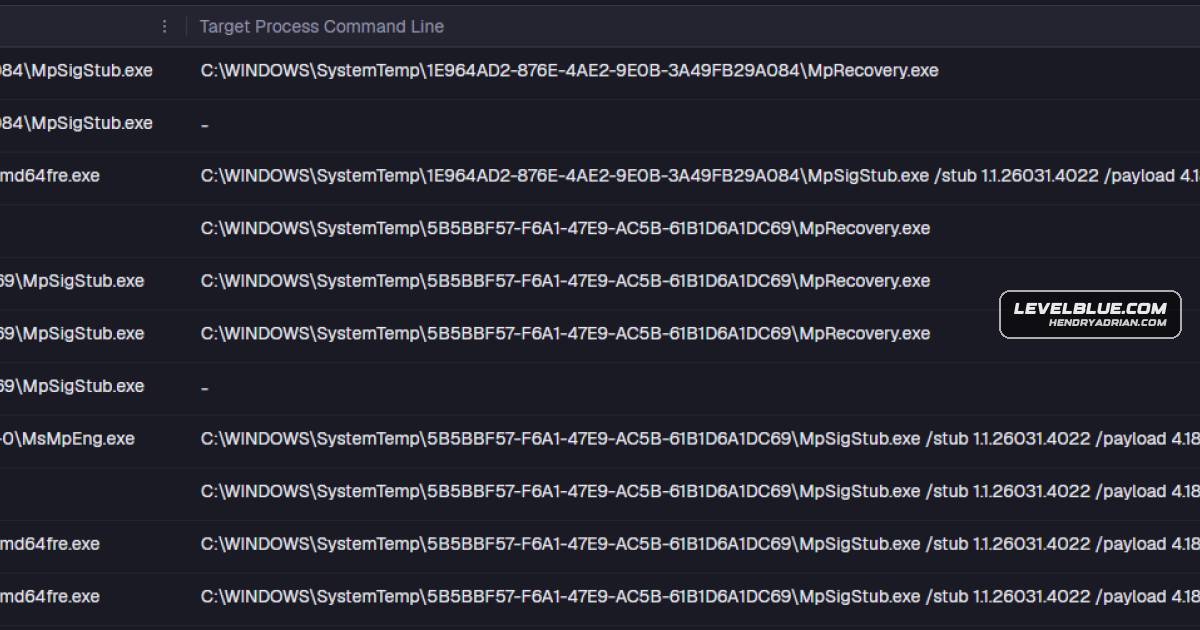
BigDiskBuster PoC Can Silently Block Microsoft Defender Updates by Exhausting Disk Space

LevelBlue reproduced and analyzed BigDiskBuster, a proof of concept that repeatedly claims available disk space during Defender updates, causing them to fail while real-time protection remains active.

Oct 5, 2026
PreviousPage 15 of 100 Next
© 2026 cyber.hendryadrian.com