UAT-11587 Uses Antino Backdoor and Microsoft 365 for Espionage Campaign
Summary
Cisco Talos reports that UAT-11587 targeted government and policy organizations in Asia and Syria with Antino, a Rust backdoor delivered through spear-phishing and using Outlook and OneDrive for command-and-control.
Key points
- Talos links UAT-11587 to attacks on 16 entities across eight Asian countries and organizations in Syria.
- The campaign uses tailored spear-phishing, spoofed sender identities, and fake Gmail attachment previews to deliver HTA or WSF stagers.
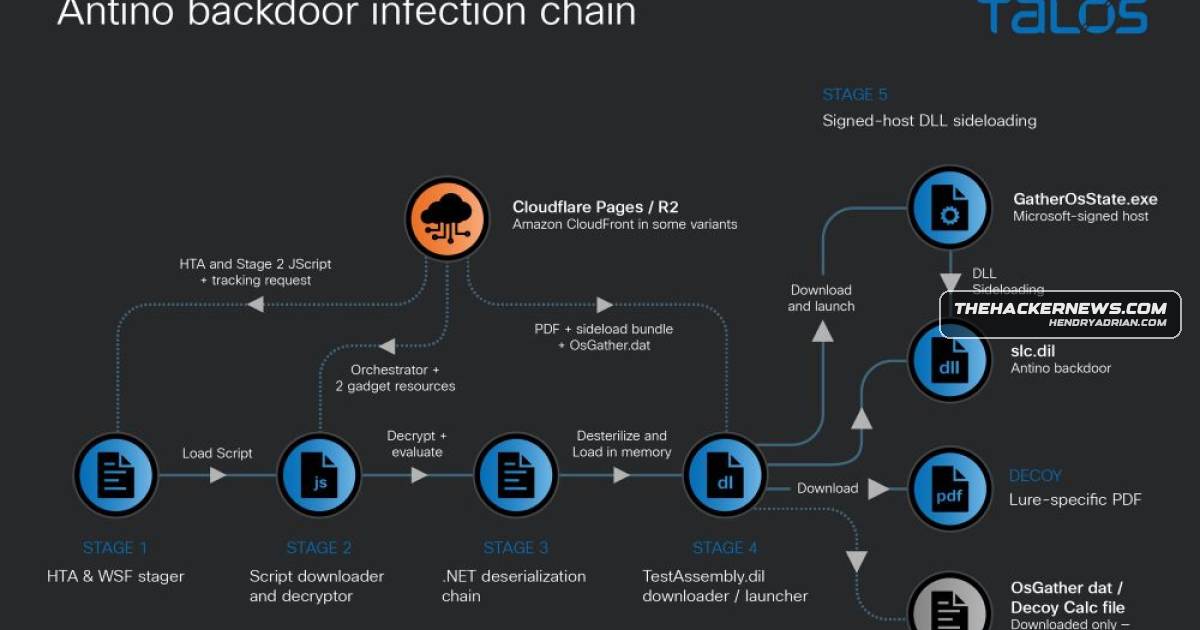
- A multi-stage chain deploys Antino, a Rust-compiled Windows backdoor, through DLL sideloading.
- Antino uses Outlook to retrieve commands and OneDrive for heartbeat and file transfer, avoiding a dedicated C2 server.
- The backdoor supports host reconnaissance, command and PowerShell execution, file transfer, shellcode loading, and persistence.
- Talos assesses the actor as China-nexus with high confidence, citing language and metadata clues, targeting, and other campaign indicators.
Article Details
- Attack Vectors
- Spear-phishing emails with spoofed sender identities and tailored lures.
- Emails replicated Gmail’s attachment-preview widget; its apparent attachment card linked to an attacker-controlled Cloudflare Pages URL.
- The linked URL delivered an HTA or WSF stager, followed by a JavaScript downloader and decryptor and a .NET downloader and launcher.
- The Antino implant was launched through DLL sideloading using the legitimate Microsoft-signed GatherOsState.exe binary.
- Antino used Outlook for command exchange and OneDrive for heartbeat and file transfer.
- Defensive Notes
- Talos noted that the abuse of Windows Scripted Diagnostics to execute attacker-controlled PowerShell can complicate attribution to the original implant, but observable PowerShell, file-creation, and Registry telemetry remains.
- Monitor for Outlook mailbox command polling, including messages with the subject prefix command_req_[session_id], and unusual OneDrive activity associated with the implant.
- Review email sender authenticity and inspect HTML email bodies for replicated attachment previews and links to attacker-controlled pages.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | d32tpl7xt7175h[.]cloudfront[.]net | CloudFront domain referenced by a JavaScript downloader associated with UAT-11587. |
MITRE ATT&CK
T1057 · Process DiscoveryAntino can list running processes.T1059.001 · PowerShellAntino executes PowerShell scripts, including attacker-controlled PowerShell through Windows Scripted Diagnostics.T1059.003 · Windows Command ShellAntino can execute commands using cmd.exe.T1083 · File and Directory DiscoveryAntino can enumerate directories.T1102.002 · Bidirectional CommunicationAntino uses Outlook for command exchange and OneDrive for heartbeat and file transfer as its command-and-control channel.T1105 · Ingress Tool TransferThe staged chain downloads the JavaScript downloader, lure document, decoy executable, and Antino backdoor.T1566.002 · Spearphishing LinkSpear-phishing emails linked to an attacker-controlled Cloudflare Pages URL that delivered the initial HTA or WSF file.T1574.002 · DLL Side-LoadingThe Antino implant was launched by DLL sideloading with the legitimate Microsoft-signed GatherOsState.exe binary.
People
Threat Actors
CL-STA-0049Named as a China-aligned cluster with tactical similarities to Jewelbug.Earth AluxNamed as a China-aligned cluster with tactical similarities to Jewelbug.Ink DragonNamed as a China-aligned cluster with tactical similarities to Jewelbug.JewelbugCisco Talos assessed UAT-11587 to share some level of overlap with Jewelbug, but reported no established connection between the espionage campaign and Jewelbug’s financially motivated activity.REF7707Named as a China-aligned cluster with tactical similarities to Jewelbug.UAT-11587Cisco Talos tracking name for the threat actor responsible for the Antino espionage campaign.
Malware
Vendors
CiscoCisco Talos is tracking the cluster under the moniker UAT-11587.Cloudflare“The entire attachment card was wrapped in an anchor tag pointing to an attacker-controlled [Cloudflare Pages] URL.MicrosoftThe campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection.
Products
GmailThe campaign used spoofed senders and fake Gmail attachment previews to improve phishing success.Microsoft 365 Apps for EnterpriseThe campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection.Microsoft OneDriveThe campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection.Microsoft WindowsA China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino.OutlookThe campaign relies on spear-phishing, spoofed identities, and Microsoft 365-based command-and-control through Outlook and OneDrive to deliver multi-stage malware and evade detection.
Countries
CambodiaThe activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamedChinaA China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino.IndiaThe activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamedMyanmargovernment and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino.Pakistanwhich has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino.PhilippinesThe activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamedSyriaA China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino.TaiwanThe activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamedThailandhas targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino.
Industries
Civil societyThe threat actor was first detected in September 2025 in connection with a spear-phishing campaign directed against Taiwan’s academic, think tank, and civil society policy community.GovernmentA China-nexus threat actor tracked as UAT-11587 has targeted government and policy organizations across Asia and Syria using a new Rust-based Windows backdoor called Antino.Policy research“Its lures and observed targets include Taiwanese political, legislative, civil defense, and policy research subjects, together with regional government, maritime, diplomatic, and security themes.