Predictable Session-Cookie Secret Enabled Impersonation of 95 Accounts in Authorized Testing
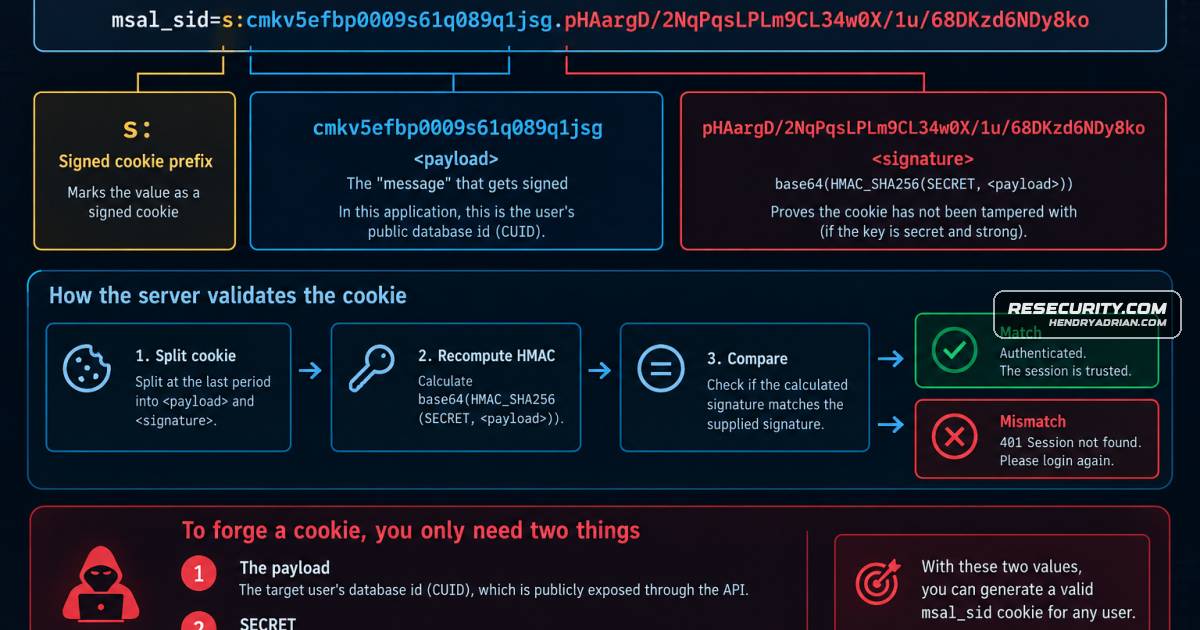
Researchers found that a hard-coded cookie-signing secret and publicly exposed user IDs let them forge sessions for 95 of 241 tested accounts, including administrators, in an authorized staging assessment, bypassing application-level SSO and MFA.