
Researchers Trace Phishing Campaign Using Invisible Unicode Characters to Evade Email Filters
Summary
Microsoft investigated a high-volume phishing campaign that used invisible Unicode tag characters to split financial lure words and evade email filters. Further analysis linked 165 artifacts to the campaign, including 158 not detected by the cited VirusTotal engines.
Key points
- The attackers used Unicode tag characters to split financial terms such as “funding,” hindering email filters’ ability to parse the lures.
- Microsoft identified 148 phishing domains but published 20 in its report; the article’s analysis assembled 165 connected artifacts.
- The researchers report that 158 of the 165 artifacts were not detected by the VirusTotal engines they checked.
- The analysis examined 20 domain indicators and 25 IP indicators, including historical DNS resolutions and network communications.
- Researchers found 137 additional domains connected through a public email address in a historical WHOIS record.
- The article cautions that some entities labeled malicious may later prove harmless and recommends further investigation.
Article Details
- Attack Vectors
- A high-volume phishing campaign used invisible Unicode tag characters to split financial lure words such as “funding,” preventing email filters from parsing them.
- Defensive Notes
- The article recommends conducting supplementary investigations to corroborate whether entities identified as threats or malicious are harmful.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | advancefundingboost[.]com | Domain IoC associated with the phishing campaign. |
| DOMAIN | digitalcapitalboost[.]com | Domain IoC identified as likely registered with malicious intent. |
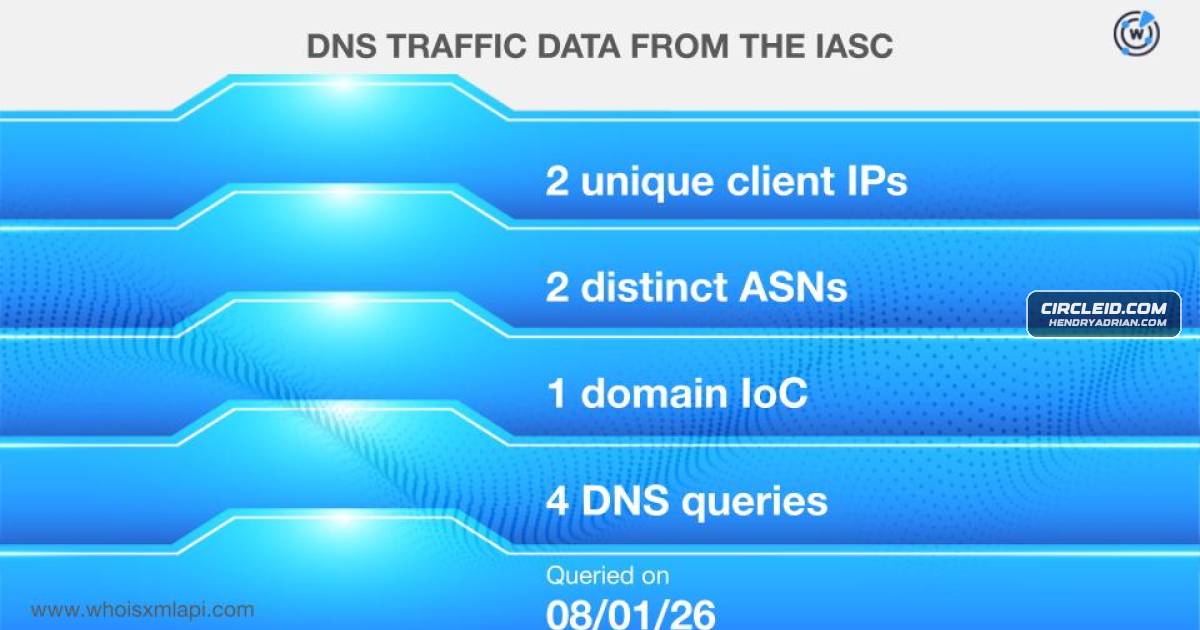
| DOMAIN | directcapitalboost[.]com | Domain IoC associated with the phishing campaign; client IP addresses queried it. |
| DOMAIN | fundingexpresscapital[.]com | Domain IoC identified as likely registered with malicious intent. |
| DOMAIN | guardiancapitalway[.]com | Domain IoC identified as likely registered with malicious intent. |
| DOMAIN | harboradvancefunding[.]com | Domain IoC associated with the phishing campaign. |
| DOMAIN | onlinedirectfinance[.]com | Domain IoC associated with the phishing campaign. |
| DOMAIN | ourbusinessloans[.]com | Domain IoC associated with the phishing campaign. |
| IPV4 | 173[.]236[.]20[.]10 | IP IoC included in the article’s list of campaign-related IP indicators. |
| IPV4 | 173[.]236[.]20[.]13 | IP IoC included in the article’s list of campaign-related IP indicators. |
| IPV4 | 173[.]236[.]20[.]2 | IP IoC included in the article’s list of campaign-related IP indicators. |
| IPV4 | 173[.]236[.]20[.]23 | IP IoC included in the article’s list of campaign-related IP indicators. |
| IPV4 | 173[.]236[.]20[.]7 | IP IoC included in the article’s list of campaign-related IP indicators. |