New Spyder Downloader Uses Sandbox Evasion and Targets South Asian Police
Summary
Analysis of two Windows downloader builds finds sandbox checks, persistence, and plain-HTTP beaconing. Their settings and target labels suggest a rewritten Spyder tool aimed at South Asian police; public sandbox runs received no next stage.
Key points
- The two Windows builds, compiled in February and April 2026, share encryption keys and code routines but differ substantially from publicly described older Spyder samples.
- Encrypted settings identify the C2 server as cloudwindowapps[.]com and include target labels “AJK Police” and “POLICE”; the researchers assess the Spyder link as likely, not certain.
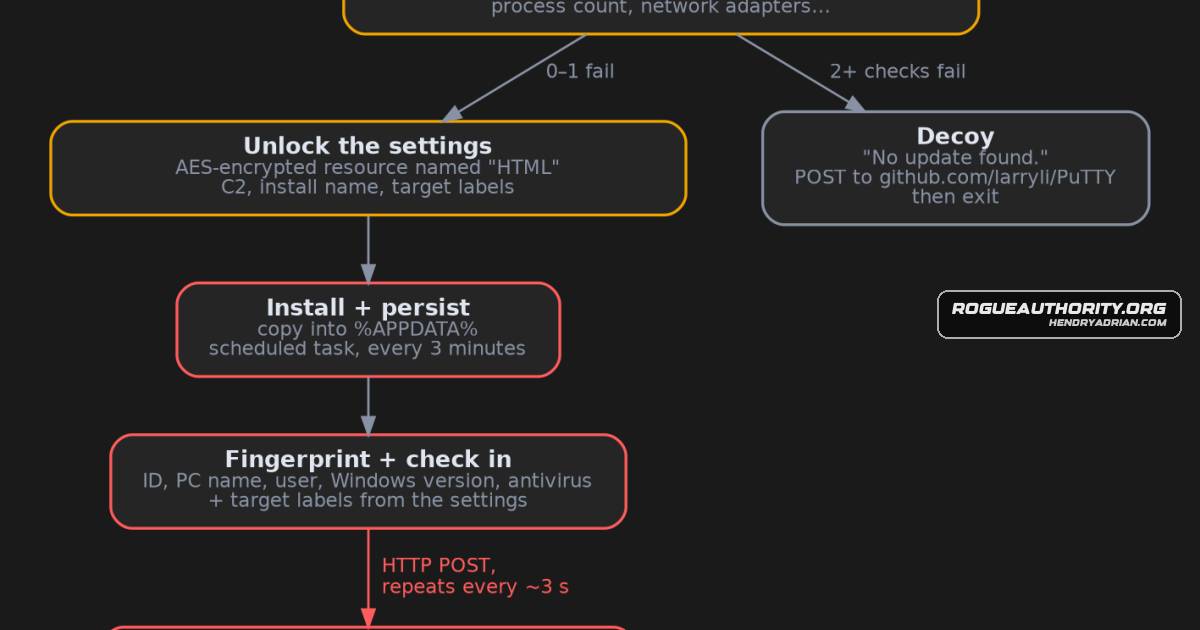
- Roughly 16 checks for virtual machines, debuggers, analysis tools, and other lab indicators can divert the malware to a harmless “No update found” decoy.
- On a real computer, the malware copies itself into an AppData folder, creates a scheduled task, and sends system and target-profile details over unencrypted HTTP.
- The server returned “0” in April sandbox runs and “page not found” by May; no public run received a next-stage payload.
- The researchers found no shared code with older Spyder builds. They link the suspected Patchwork connection to earlier, hedged research rather than new evidence.
Article Details
- Attack Vectors
- Two Windows downloader builds, a1bx5.exe and inpo.exe, carry encrypted per-build settings and contact cloudwindowapps[.]com/enclose-pdf over plain HTTP.
- The malware checks for virtual machines, debuggers, analysis tools, network-adapter characteristics, and process counts; two failed checks trigger a decoy “No update found.” message and exit.
- On a real computer, the downloader copies itself into an APPDATA subfolder and creates a scheduled task that runs every three minutes.
- The malware sends host and user information, antivirus status, and target labels to its server, then polls for instructions and a possible next stage.
- The signed a1bx5.exe build is padded with 10,000,000 zero bytes; the article says this may help evade tools that skip files above a size threshold.
- The downloader sends a decoy request to github[.]com/larryli/PuTTY. The article explicitly states GitHub is not involved in the attack and this request is set dressing.
- Defensive Notes
- Block and hunt cloudwindowapps[.]com and HTTP POST requests to /enclose-pdf, especially those using the user agent WinHTTP Example/1.0 and the data=UID=…&Agnt=…&Profile=…&AgMal=… body pattern.
- Investigate systems containing %APPDATA%\Compser\ or %APPDATA%\Mythlcsoft\, or scheduled tasks named WinHelper or RAS Right Template Management.
- Treat unexpected signed programs cautiously; the article notes that a valid signature does not establish that a program is safe.
- Sandbox results may show only the decoy behavior because the malware uses multiple environment checks to avoid analysis.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cloudwindowapps[.]com | C2 domain used by both new downloader builds; defenders are advised to block and hunt it. |
| SHA256 | 0c69637c2f54822a2f6c796a7800192474742d6f309b3d6aa82ecb10690a7097 | SHA-256 hash identified for the inpo.exe malware build. |
| SHA256 | 1753abbd3a79ff9db264b3e05bbbd2fa6f0b983de1a66c341a8a4cc71b4d6429 | SHA-256 hash of an older Spyder build labeled SINDH-INT. |
| SHA256 | 2f21da16f2e697a95deb0f89575c1ea2594a78ef5d76a038638c8f1b651d4ae5 | SHA-256 hash of an older Spyder build labeled ATU. |
| SHA256 | 34e260c301ee81b228d35ac721b06a3aa41fb5b07835078b5b4e2941fef8aa85 | SHA-256 hash of an older Spyder build labeled NP-CDR. |
| SHA256 | 708330999388ad7235dee0920264d88f2468e04d2fb4ef097c479f328f566c5b | SHA-256 hash of another older Spyder build labeled NP-CDR. |
| SHA256 | 85608993639100b235ad96975fa96e9cfdc600e6a77a8e76d08b10beec4b037b | SHA-256 hash of an older Spyder build labeled CTTC. |
| SHA256 | bf9445ded122ee5853bb45d69b390ed5a0b36baa0c48adc7a8fa65e526116720 | SHA-256 hash of an older Spyder build labeled AJK POL. |
| SHA256 | eddd65e1156513894bead38dc88a77bf7b39d3665015878334cbf49f81ddde08 | SHA-256 hash identified for the a1bx5.exe malware build. |
| URL | hxxp[:]//cloudwindowapps[.]com/enclose-pdf | C2 URL used by both new builds for check-ins and polling. |
| URL | hxxp[:]//myprivatedrives[.]com/ticket_line/certificate[.]php | C2 URL listed for older Spyder builds used for comparison. |
| URL | hxxp[:]//myprivatedrives[.]com/ticket_line/openai[.]php | C2 URL listed for older Spyder builds used for comparison. |
| URL | hxxp[:]//nodejsupdates[.]com/ticket_line/afa[.]php | C2 URL listed for older Spyder builds used for comparison. |
| URL | hxxp[:]//nodejsupdates[.]com/ticket_line/certificate[.]php | C2 URL listed for older Spyder builds used for comparison. |
MITRE ATT&CK
T1033 · System Owner/User DiscoveryThe check-in includes the logged-in username.T1036 · MasqueradingThe malware displays a fake “No update found.” message under the title “Update Check Successful” as a decoy.T1036.005 · Match Legitimate Resource Name or LocationThe malware uses an update-check disguise and sends a request to a GitHub PuTTY project as cover traffic.T1055 · Process InjectionThe downloader checks whether a debugger is attached and whether analysis-tool processes or windows are present.T1057 · Process DiscoveryThe downloader checks the process count as part of its environment screening.T1071.001 · Web ProtocolsThe article reports plain, unencrypted HTTP communications with the C2 server.T1082 · System Information DiscoveryThe check-in reports the Windows version and computer name.T1105 · Ingress Tool TransferThe downloader's code can save and launch a file received as a next stage, although no public sandbox run received one.T1497.001 · System ChecksThe downloader checks for virtual machines and analysis environments before choosing whether to proceed or show its decoy.T1518.001 · Security Software DiscoveryThe downloader reports the installed antivirus product, or NoAV, in its check-in.T1547.001 · Registry Run Keys / Startup FolderThe downloader establishes recurring execution by creating a Windows scheduled task.
People
Threat Actors
Dropping ElephantThe article explicitly identifies Dropping Elephant as another name for Patchwork, which QiAnXin researchers linked to Spyder.HangoverThe article explicitly identifies Hangover as another name for Patchwork, which QiAnXin researchers linked to Spyder.PatchworkQiAnXin researchers attributed Spyder to Patchwork, also called Dropping Elephant or Hangover; the article characterizes this link as likely rather than proven for the new builds.
Malware
RemcosEarlier Spyder campaigns delivered screenshot and document-theft tools and, in 2023, the Remcos remote-access tool, but that doesn’t tell us what this one delivers.SpyderThose settings show that the tool is most likely Spyder, a downloader that security researchers link to the Patchwork espionage group, in a new version that shares no code we could find with the publicly described one.
Vendors
Products
CloudflareIn April, the server, an ordinary web application behind Cloudflare, answered every check-in with a one-character reply.Microsoft Trusted SigningTwo builds, one codebase: a1bx5.exe (signed with a three-day Microsoft Trusted Signing certificate) and inpo.exe (unsigned).Microsoft WindowsWe looked at two Windows programs that report to the same server, cloudwindowapps[.]com.PuTTYIt also sends a web request to a Chinese-localised fork of the PuTTY SSH client on GitHub (github[.]com/larryli/PuTTY), the kind of traffic an “update checker” would plausibly make. GitHub is not involved in the attack;
Tools
ANY.RUNTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.capaTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.FLOSSTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.gdbTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.KesaKodeTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.MalcatTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.pefileTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.pycryptodomeTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.PythonTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.Recorded Future TriageTools used: Malcat, capa, FLOSS, KesaKode, a sandboxed Wine run with gdb, Python (pefile, pycryptodome), ANY.RUN and Recorded Future Triage.
Countries
Industries
GovernmentQiAnXin dates Patchwork’s activity back to 2009 and describes it as mostly targeting government, military and research organisations across Asia.MilitaryQiAnXin dates Patchwork’s activity back to 2009 and describes it as mostly targeting government, military and research organisations across Asia.PoliceOne build is labelled AJK Police.ResearchAnd fields 5 and 8 are target labels: earlier public research on Spyder describes the same “profile” and “mail” settings and notes that they name the victim organisation.