cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2379 articles

Threat Research · bleepingcomputer.com

Citizen Lab Links Targeted Ad Campaign to Zero-Click Candiru Spyware Attacks

Citizen Lab linked targeted ads to Candiru spyware attacks against at least 45 Al Jazeera devices in 2024–2025, describing how ad code selected targets and tracing network activity to spyware infrastructure.

Oct 16, 2026
Threat Research · unit42.paloaltonetworks.com

Unit 42 Details AI-Assisted Espionage Campaign Targeting Government Linux Systems

Unit 42 describes CL-UNK-1211 activity targeting government Linux infrastructure from October 2025 to April 2026, including web shells, credential theft, a custom RAT and attempted data exfiltration. AI-generated code is suggested, not confirmed.

Oct 15, 2026
Threat Research · thehackernews.com

Citizen Lab Links Candiru Spyware Infections at Al Jazeera to Zero-Click Ads

Citizen Lab says targeted ads delivered zero-click Candiru spyware to at least 45 Al Jazeera devices in 2024 and 2025. Google and ad platforms removed or restricted Discover-Tech after the findings.

Oct 15, 2026
Threat Research · thehackernews.com

Silent Lynx Uses WinRAR Flaw to Deploy Reverse Shells in CIS Government Attacks

Researchers attribute attacks on government organizations across the CIS to Silent Lynx, describing phishing and other delivery methods, including crafted WinRAR archives exploiting CVE-2025-8088 to deploy custom reverse shells.

Oct 15, 2026
Threat Research · thehackernews.com

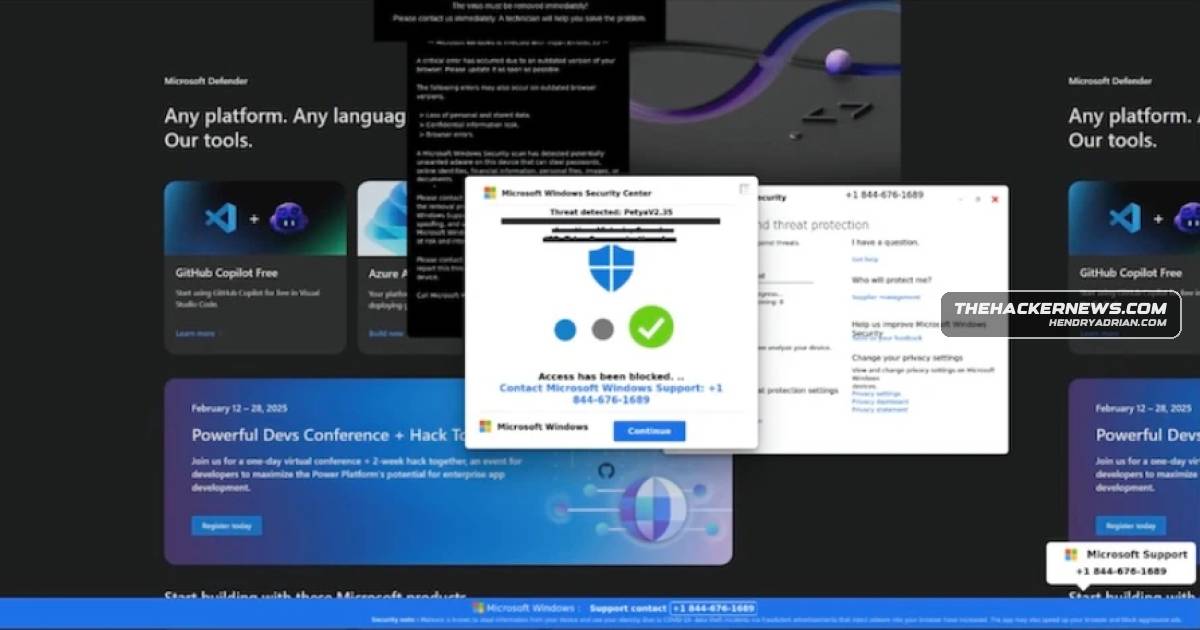
Help TDS Linked to Hotejka as More Than 20,000 Cloudflare Pages Domains Host Tech Support Scams

Infoblox links Help TDS to Hotejka, which it suspects succeeded ROI777. Since April 2026, the operation has reportedly used more than 20,000 Cloudflare Pages domains to route users to tech support scams and other affiliate content.

Oct 15, 2026
Threat Research · infoblox.com

Researchers Link Hotejka to Help TDS and Detect Its Cloudflare Pages Domains in Advance

Infoblox researchers link Hotejka to the Help TDS tech-support scam operation and describe detecting its Cloudflare Pages domains about seven days before use, reducing exposure among their cloud customers.

Oct 15, 2026
Threat Research · securityweek.com

CikaBika RAT Uses Discord for Command and Control

Darktrace reports a campaign delivering the Rust-based CikaBika RAT through document-themed lures. The malware uses Discord for command and control and can collect system data, execute commands, and exfiltrate files via Ngrok.

Oct 15, 2026
Threat Research · securityweek.com

Hirudo Android RAT Replaces Banking Apps With Trojanized Versions

ThreatFabric describes Hirudo, an Android banking RAT that replaces targeted Indonesian banking apps with modified copies designed to hide security checks while stealing credentials and enabling remote device control.

Oct 15, 2026
Threat Research · thehackernews.com

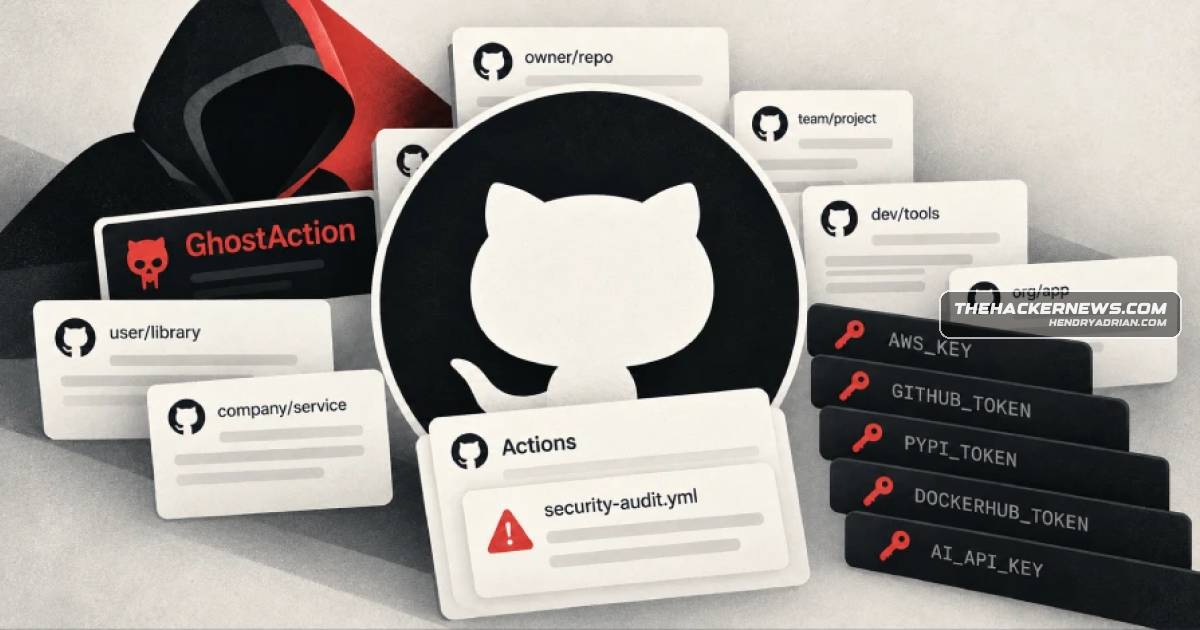
GhostAction Targets 30,000+ Repositories After Compromising About 1,900 GitHub Accounts

GitGuardian reports that a GhostAction wave targeted over 30,000 repositories, using compromised GitHub accounts to deploy workflows that scan for secrets. GitHub began blocking the workflow on October 9, 2026.

Oct 15, 2026
Threat Research · cyble.com

GhostBat RAT Uses Android Accessibility Overlays to Steal PINs

Cyble reports that GhostBat RAT targets Android users in India through mParivahan- and eChallan-themed campaigns. Its latest variant uses Accessibility Service overlays to capture financial-app PINs and Firebase Remote Config to manage malware capabilities and C2.

Oct 15, 2026
Threat Research · hornetsecurity.com

Fake Purchase and Bank Alerts Drive Tech Support Scam Calls

Hornet Security identified over 150,000 messages and more than 40 callback numbers from September 18 to October 2, 2026. Its calls found operators following transaction scripts; the numbers were associated with Onoff, but the users were not identified.

Oct 15, 2026
Threat Research · cloud.google.com

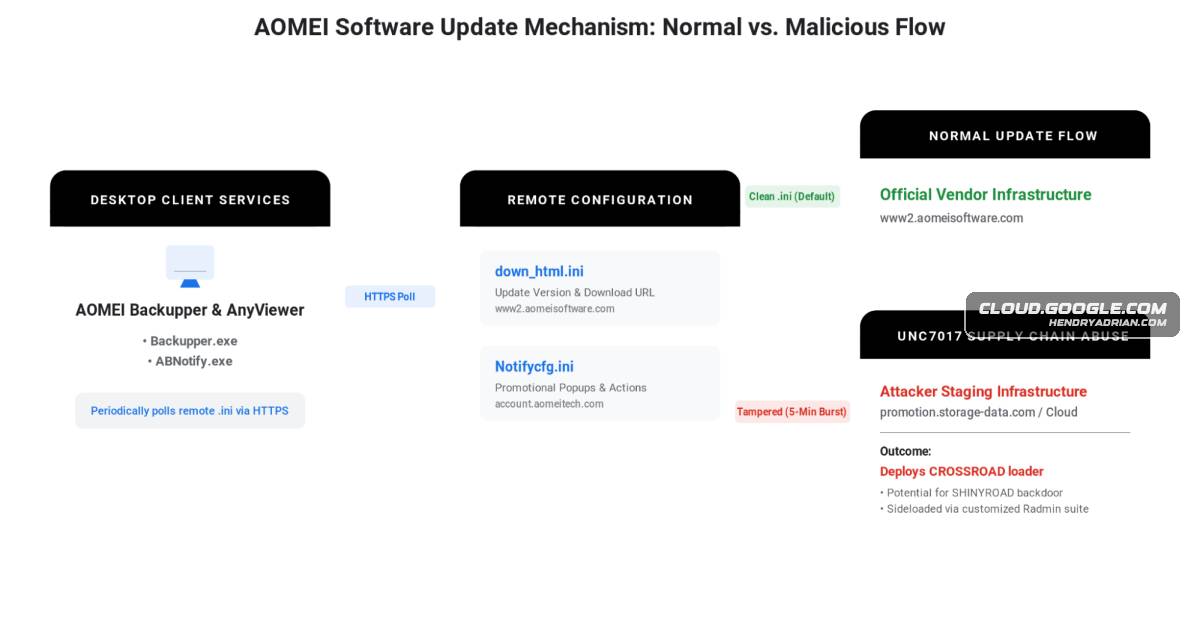
UNC7017 Used Brief AOMEI Update Tampering to Deliver CROSSROAD and SHINYROAD

Google Threat Intelligence Group and Mandiant detail UNC7017’s brief tampering of AOMEI update configurations, which redirected some clients to malware and enabled WebDAV NTLM credential coercion. AOMEI says it took corrective action.

Oct 15, 2026
Threat Research · cloud.google.com

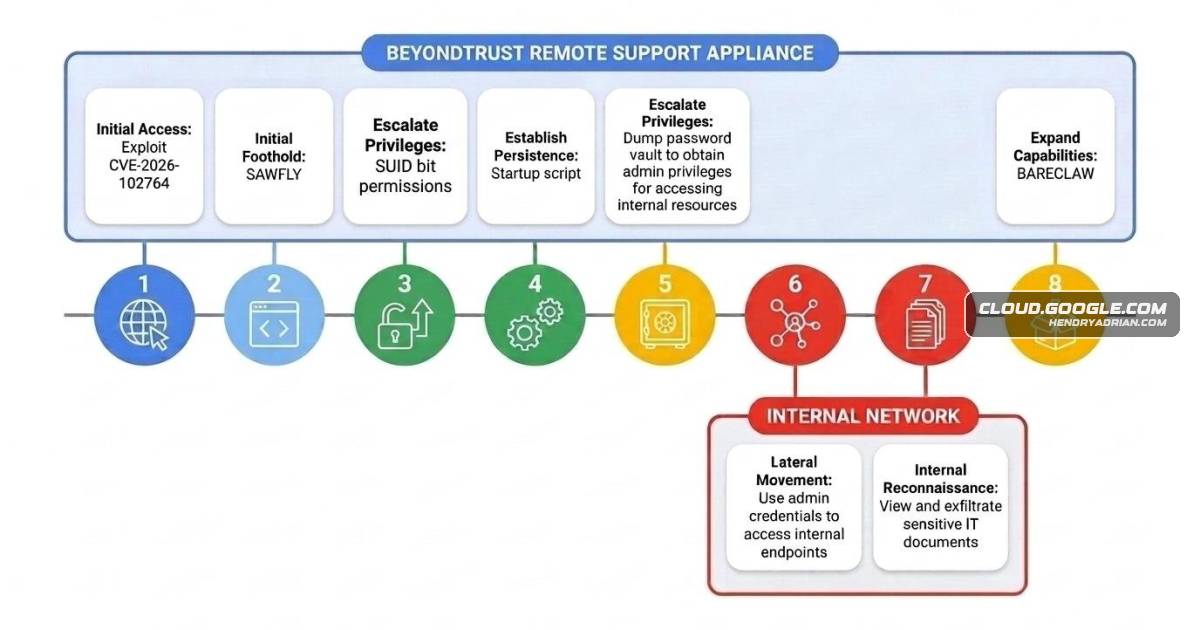
Mandiant Details ARMORY CASTLE’s Exploitation of BeyondTrust Remote Support

Mandiant reports ARMORY CASTLE exploited CVE-2026-102764 as a zero-day, using custom malware to gain persistent root access, target credentials and move through BeyondTrust Remote Support environments. It urges patching and investigation.

Oct 15, 2026
Threat Research · security.com

Aoki Infostealer Adds AI Coding Assistant Credentials to Its Targets

Symantec researchers say newer Aoki infostealer samples target credentials and session files for AI coding assistants, alongside data from browsers, wallets, password managers and other apps. Stolen tokens could expose connected developer services.

Oct 15, 2026
Threat Research · reversinglabs.com

ReversingLabs Maps a Midnight Blizzard-Linked Campaign from Two Malware Hashes

ReversingLabs traced two Anthropic-published malware hashes to additional stagers, delivery shortcuts and infrastructure. Its analysis found the staging server still serving malware on October 5, while noting that some links to the campaign remain uncertain.

Oct 15, 2026
Threat Research · securitylabs.datadoghq.com

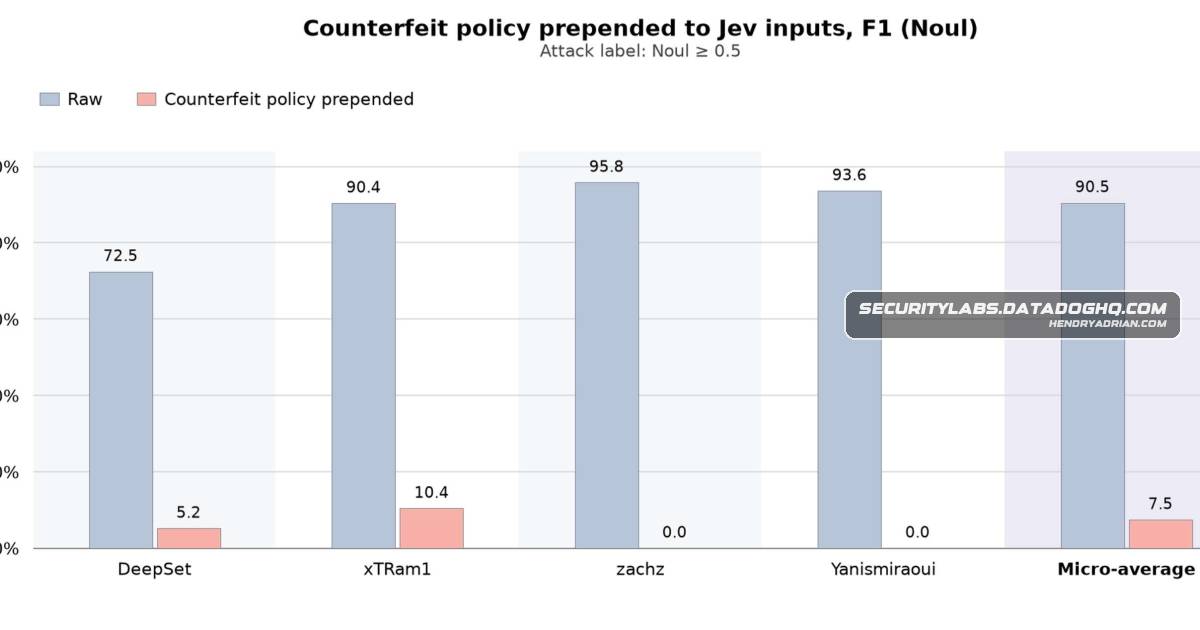
Counterfeit Policies Steer Jev Classifier and Lower LangChain Tool-Risk Scores

Datadog researchers found that prepending counterfeit policies to untrusted content sharply reduced Jev’s prompt-injection detection and lowered LangChain tool-risk scores in a test scenario. The benchmark did not test downstream agent compromise.

Oct 15, 2026
Threat Research · hunt.io

Exposed Files Reveal PaperCut Exploitation, a Second RCE Path and Attacker Tooling

Researchers analyzed exposed attacker directories tied to a PaperCut campaign, uncovering a second XML-RPC RCE path, credential theft and persistent SOCKS5 pivots. Actor files documented 1,005 hosts across 45+ countries and 45 live pivots.

Oct 15, 2026
Threat Research · unit42.paloaltonetworks.com

FortiManager Intrusion Exposes 500+ Firewalls and Deploys PEERSTITCH Implant

Unit 42 says attackers exploited FortiManager and FortiOS flaws to steal configurations and credentials for 500+ firewalls, then used PEERSTITCH, a memory-resident implant, to intercept traffic and maintain access.

Oct 14, 2026
Threat Research · socprime.com

Volexity Details Ivanti Connect Secure Zero-Day Exploitation and Root-Level Attack Chain

Volexity traced active exploitation of Ivanti Connect Secure CVE-2026-104935, chained with a separate privilege-escalation zero-day. The observed actor reached root access and targeted credentials and Active Directory data; Ivanti has issued fixes for CVE-2026-104935.

Oct 14, 2026
Threat Research · rogueauthority.org

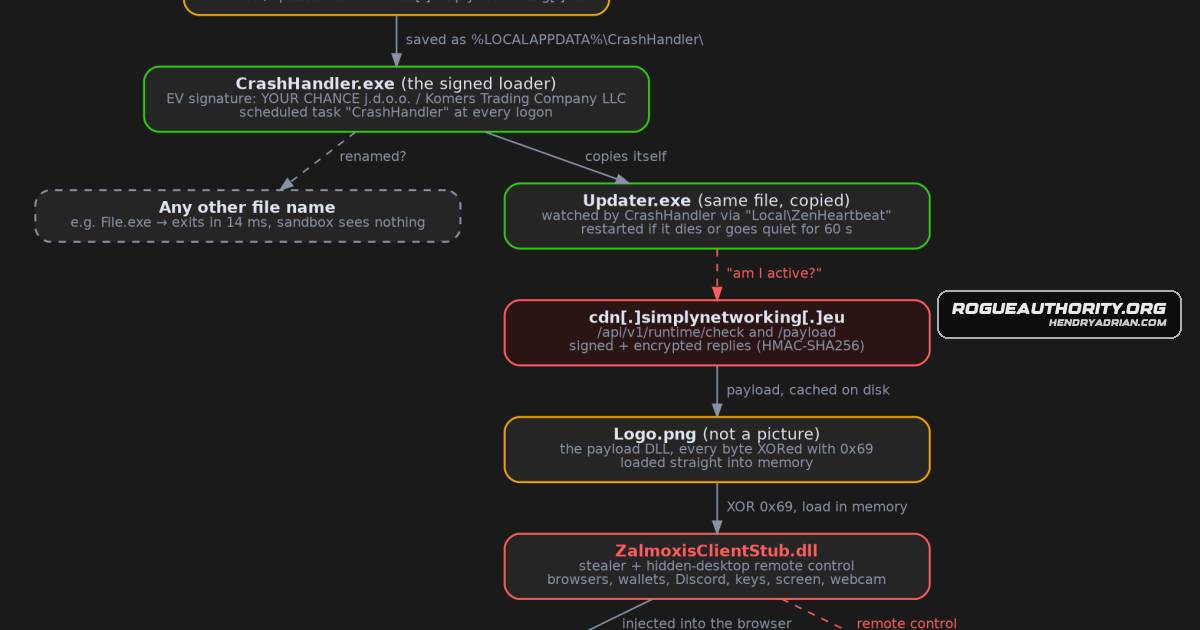
Zalmoxis Stealer Hides Behind Signed Loader and Name-Based Execution

Researchers analyzed a signed loader that activates only under specific filenames, installs persistence, and retrieves the Zalmoxis stealer. The malware targets browser data, crypto wallets, and Chrome’s App-Bound Encryption key.

Oct 14, 2026
Threat Research · asec.ahnlab.com

Researchers Trace ARTEX-Based Tools and Exploit Artifacts in Bob Research Labs Environment

AhnLab researchers found ARTEX-derived tools distributed under altered names and analyzed a Bob Research Labs environment containing CVE-2026-75650 exploit artifacts and an IRC implant. They also found exposed source code, credentials, logs, and attack tools.

Oct 14, 2026
Threat Research · rapid7.com

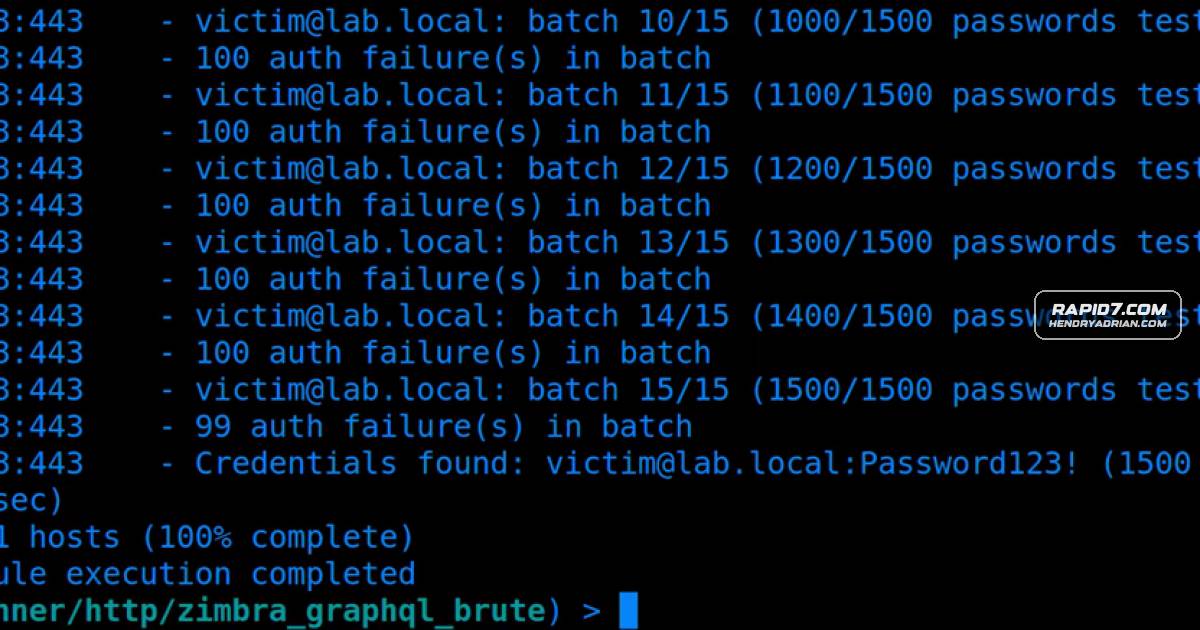
Rapid7 details five Zimbra flaws enabling password guessing, email impersonation, mailbox access and mail exfiltration

Rapid7 analyzes five Zimbra flaws that enable unauthenticated password guessing, sender impersonation, cross-user mailbox reads and persistent email exfiltration. Fixes are available for three; no public fix is listed for two.

Oct 14, 2026
Threat Research · microsoft.com

Microsoft Details Phishing-Kit Ecosystem Behind Billion-Message Campaigns

Microsoft describes a Chinese-language phishing ecosystem that enabled over one billion phishing emails and SMS messages targeting more than 75,000 organizations since January 2026. Its investigation also helped disrupt key developers and infrastructure.

Oct 14, 2026
Threat Research · malwarebytes.com

Fake Calendly Pages Impersonate Meta Careers to Steal Facebook and Google Logins

Malwarebytes describes fake Meta interview-booking pages that steal Facebook and Google credentials, 2FA codes, and personal details, then relay them to attackers attempting real-time account access.

Oct 14, 2026
PreviousPage 11 of 100 Next
© 2026 cyber.hendryadrian.com