Fake WatchGuard VPN Site Harvests Credentials, Then Delivers Genuine Signed Client
Summary
Huntress says a fake WatchGuard VPN site collected server, username and password details, then delivered the genuine signed installer. In the investigated case, the user may have submitted credentials once; the domain was offline by Oct. 13.
Key points
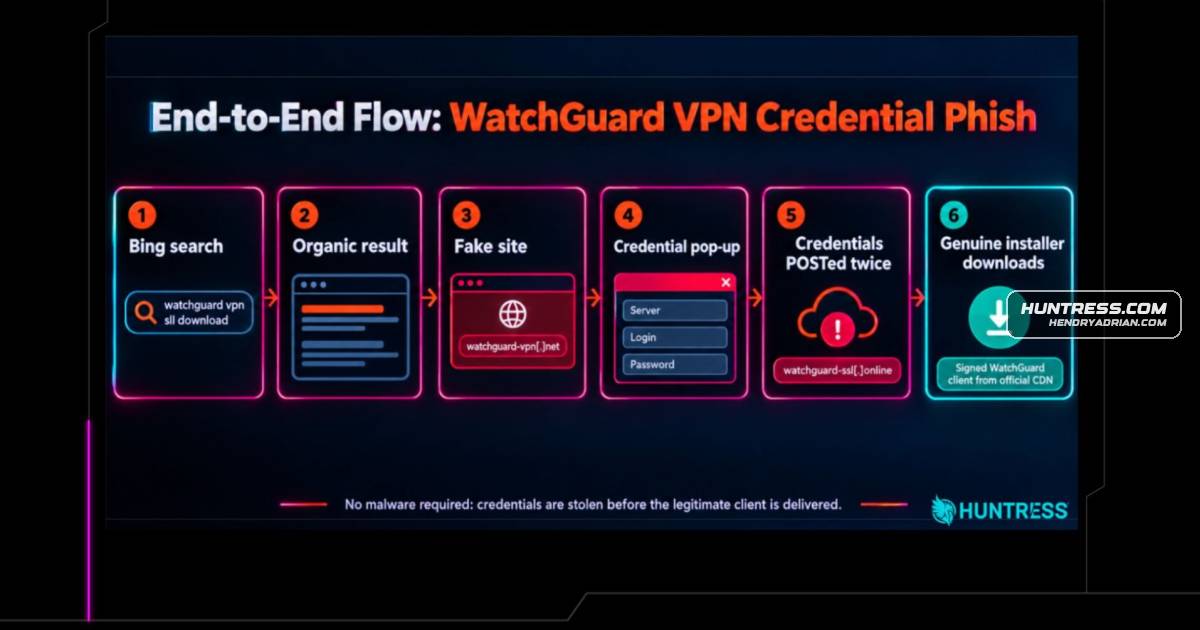
- On Oct. 7, an administrator searching Bing for a VPN download clicked the lookalike site watchguard-vpn[.]net; Huntress says the evidence supports SEO poisoning rather than malvertising.
- The fake download flow prompted for the VPN server, login and password, then sent the details to watchguard-ssl[.]online. The JavaScript rejected the first submission, prompting users to try again.
- After a second submission, the site offered the genuine WatchGuard installer from the company’s CDN. Huntress verified its signature and reported that the binary had not been modified since signing.
- In the investigated case, browser history showed no installer download. Huntress said this suggests the user did not complete both prompts, though they may have entered credentials once.
- Huntress Managed Defender flagged the activity 21 seconds after the malicious site loaded, and its SOC provided remediation steps before the attack could escalate.
- Huntress reported that watchguard-vpn[.]net was offline by Oct. 13. The domain had been registered again in August after an earlier January observation; available evidence did not establish whether the same operators controlled both registrations.
- Huntress advises resetting passwords for affected accounts, enabling MFA, monitoring for unusual VPN logins, blocking the identified infrastructure and directing users to official VPN download links.
Article Details
- Attack Vectors
- A lookalike WatchGuard VPN download site appeared in search results, which Huntress classified as SEO poisoning.
- The fake site presented a download page and a browser pop-up that collected the victim's VPN server address, username, and password.
- The pop-up deliberately rejected the first credential submission and prompted the victim to enter the details again, potentially collecting a second set.
- After the second submission, the page offered the genuine, WatchGuard-signed VPN installer from WatchGuard's CDN, making the interaction appear legitimate.
- Defensive Notes
- If credentials were entered on the site, reset the password for every affected account and treat the associated VPN endpoint as known to the attacker.
- Enforce MFA and monitor SSL VPN logins from hosting providers, unfamiliar ASNs, or countries where the account has not previously connected.
- Block the reported lure and credential-collection domains and their associated IP addresses.
- Publish and bookmark official VPN-client download links in client documentation.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | watchguard-ssl[.]online | Credential-collection domain that received JSON POSTs containing submitted VPN details. |
| DOMAIN | watchguard-vpn[.]net | Lookalike WatchGuard VPN download site used to present the credential-harvesting prompt. |
| IPV4 | 158[.]94[.]209[.]19 | Reported hosting IP for the watchguard-ssl[.]online credential collector. |
| IPV4 | 80[.]249[.]132[.]140 | Reported hosting IP for the watchguard-vpn[.]net lure site. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationThe lure site impersonated the legitimate WatchGuard website and presented itself as a WatchGuard VPN download and support page.T1056.003 · Web Portal CaptureThe fake download page used a browser pop-up to capture the victim's VPN server address, username, and password.T1608.006 · SEO PoisoningHuntress classified the lookalike site's search-result placement as SEO poisoning.
People
Threat Actors
Vendors
HuntressIn early October, Huntress investigated an incident that started with a fake download site for the WatchGuard Mobile VPN with SSL, watchguard-vpn[.]net. The malicious website used a browser pop-up prompt to steal theMicrosoftTwo months later, Microsoft Threat Intelligence reported activity linked specifically to watchguard-vpn[.]com. Microsoft attributed this wider campaign iteration to Storm-2561, a financially motivated actor that hasWatchGuardHomeBlogClean Install, Stolen Creds: Fake WatchGuard VPN Site Serves Genuine Signed Client
Products
Huntress Managed DefenderOn October 7, Huntress Managed Defender flagged suspicious activity that stemmed back to activity from a user account at a managed service provider. Further investigation into the incident revealed that an administratorWatchGuard Mobile VPN with SSLOctober, Huntress investigated an incident that started with a fake download site for the WatchGuard Mobile VPN with SSL, watchguard-vpn[.]net. The malicious website used a browser pop-up prompt to steal the