cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · ncsc.gov.uk

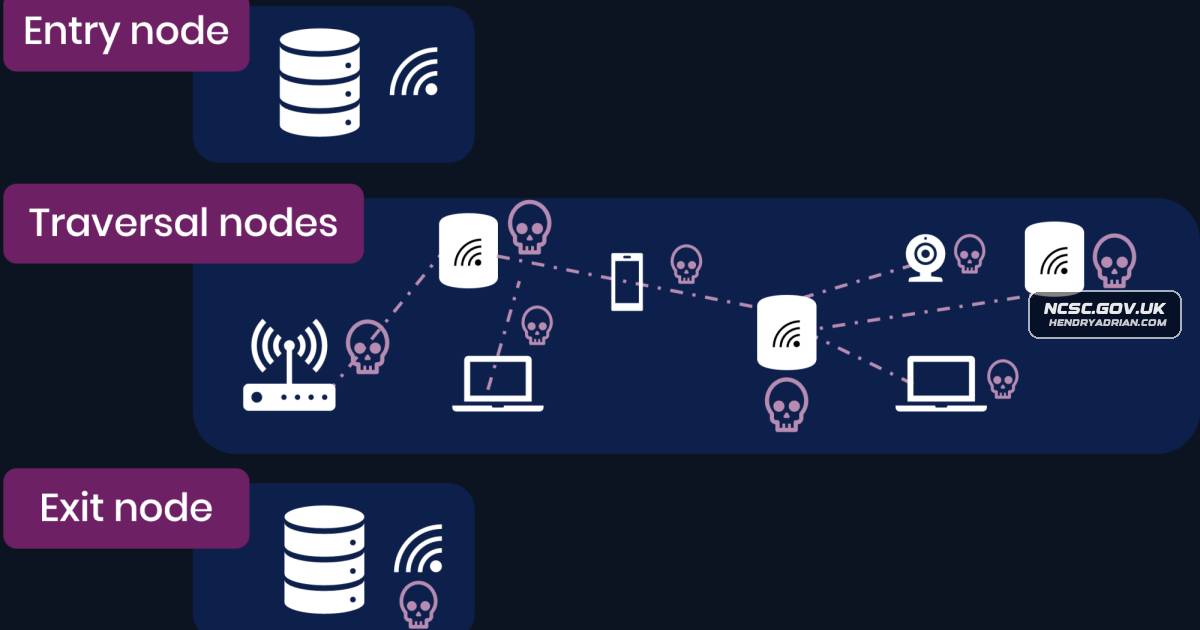
NCSC Recommends Defenses Against China-Nexus Covert Networks of Compromised Devices

The NCSC recommends network monitoring, stronger remote-access controls, threat-feed use, and active hunting to help organisations defend against China-nexus covert networks of compromised devices.
Apr 23, 2026
Detection & Defense · bleepingcomputer.com

How to Secure Helpdesk Password Resets Against Social Engineering

A sponsored guide explains how attackers can exploit helpdesk password resets and recommends stronger identity checks, self-service adoption, secure temporary credentials, activity monitoring, and helpdesk training.

Apr 23, 2026
Detection & Defense · ncsc.gov.uk

NCSC Advises Organizations on Defending Against China-Nexus Covert Device Networks

The NCSC and partner agencies advise organizations to map and baseline edge-device traffic and use adaptive defenses against China-nexus actors’ changing networks of compromised routers and other devices.

Apr 23, 2026
Detection & Defense · microsoft.com

Microsoft Details Detection Strategies for Jasper Sleet’s Fake IT Worker Campaign

Microsoft describes how North Korea-aligned Jasper Sleet uses AI-assisted fake identities to seek remote IT roles, and recommends correlating HR, communications, and onboarding telemetry to detect suspicious activity.

Apr 21, 2026
Detection & Defense · thehackernews.com

How to Protect Backups and Improve Ransomware Recovery

The article explains how ransomware can undermine backups and disaster recovery, and recommends isolated, immutable backups, separate credentials, validated restore points, automated recovery workflows, and regular testing under simulated attack conditions.

Apr 21, 2026
Detection & Defense · guardsix.com

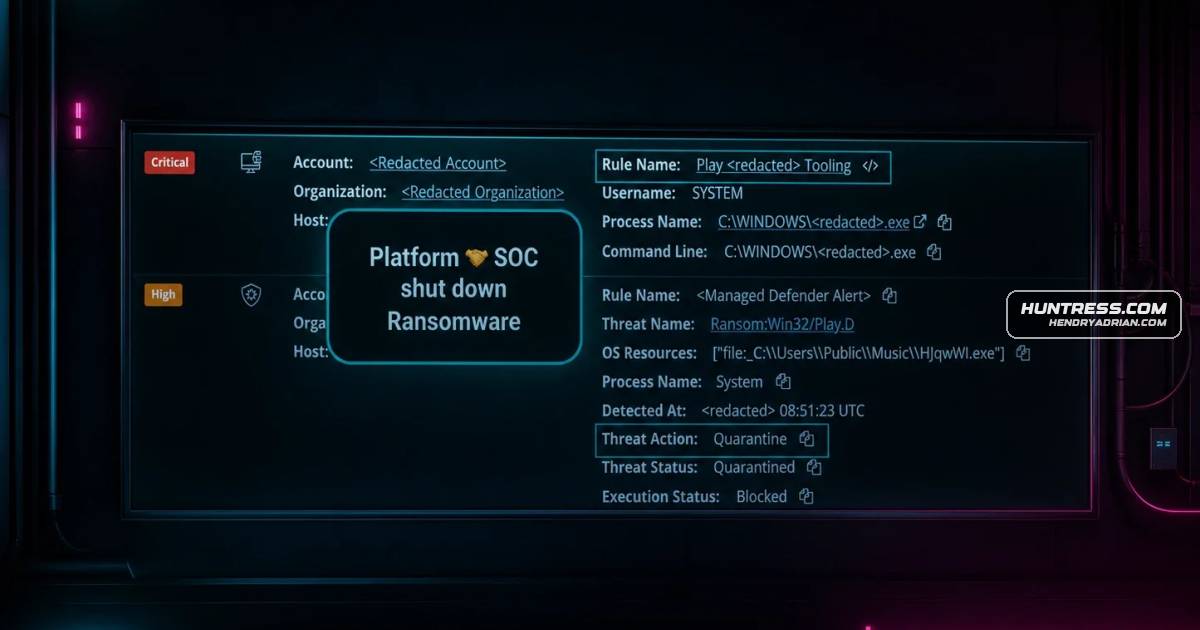
BlueHammer, RedSun PoCs Target Defender for Privilege Escalation and Update Disruption

The article details BlueHammer’s Defender TOCTOU exploit, RedSun’s SYSTEM-level binary overwrite, and UnDefend’s update blocking, with detection queries and defenses. Huntress says actors are trying to operationalize the tools; Microsoft patched BlueHammer’s linked CVE-

Apr 21, 2026
Detection & Defense · hunt.io

How to Hunt Malicious Infrastructure Using Scan Data and TLS Certificates

A Hunt.io walkthrough shows how to pivot from an IP associated with AsyncRAT through domains, ports, protocol responses, TLS certificates, and JA4X fingerprints to identify potentially related malware infrastructure.

Apr 21, 2026
Detection & Defense · attackiq.com

AttackIQ Releases NightSpire Ransomware Emulation for Defense Testing

AttackIQ released an emulation based on internal analysis of NightSpire samples, covering host discovery and file encryption to help organizations test security controls. The article also describes the group’s reported tactics and ransomware behavior.

Apr 17, 2026
Detection & Defense · securitylabs.datadoghq.com

Dependency Cooldowns Can Slow Malicious Package Releases, but Do Not Eliminate Supply-Chain Risk

Recent malicious releases in npm, PyPI, and GitHub Actions show how quickly compromised dependencies can spread. Cooldowns and package-scanning or blocking tools reduce exposure, but cannot prevent delayed malware or vulnerabilities in already-published packages.

Apr 17, 2026
Detection & Defense · huntress.com

Huntress Urges VPN Hardening After Intrusions Exploited Weak Authentication and Access Controls

Huntress describes intrusions involving compromised VPN access and urges organizations to enforce MFA, restrict privileges, disable unused accounts, centralize logs, and monitor suspicious logins.

Apr 17, 2026
Detection & Defense · cloud.google.com

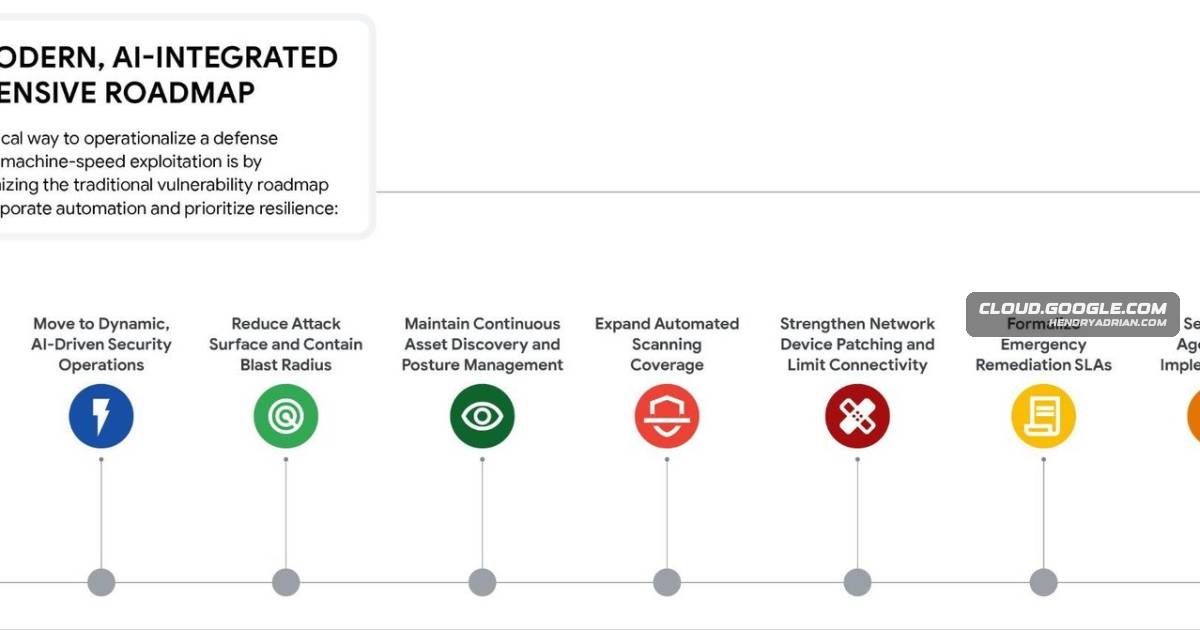
Google Details Enterprise Defenses for AI-Accelerated Vulnerability Exploitation

Google outlines an enterprise defense roadmap for AI-accelerated vulnerability discovery and exploitation, emphasizing automated vulnerability management, code and CI/CD security, continuous asset visibility, zero-trust controls, and safeguards for AI agents.

Apr 16, 2026
Detection & Defense · toxsec.com

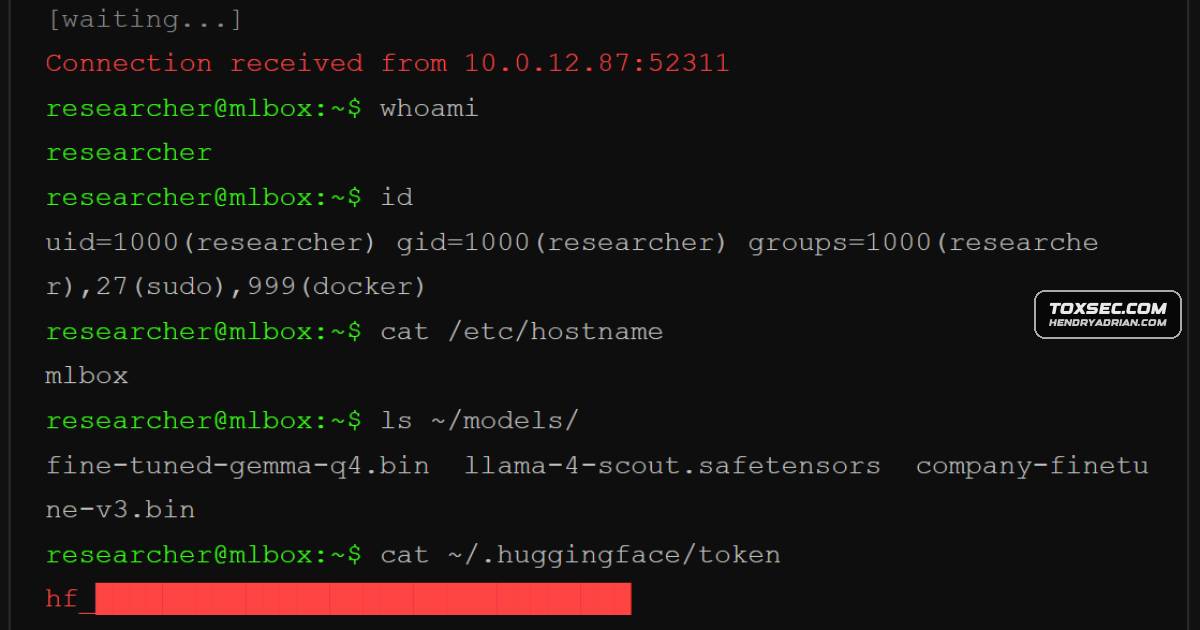
How to Secure Locally Run Open-Weight AI Models

The guide explains how pickle-based model files can enable code execution and how poisoned weights may carry sleeper-agent behavior into local models. It recommends safetensors, hash and uploader checks, isolated testing, and layered runtime and network controls.

Apr 16, 2026
Detection & Defense · wiz.io

Guide: How to Harden GitHub Actions Against Supply-Chain Attacks

An updated guide to hardening GitHub Actions after recent supply-chain compromises, with advice on limiting permissions and secrets, pinning actions, protecting workflows, and securing runners.

Apr 15, 2026
Detection & Defense · thehackernews.com

How to Reduce the Risk of Session Cookie Theft Bypassing MFA

Stolen browser session cookies can be replayed to bypass MFA after login. The article recommends shorter session lifetimes, token rotation, device binding, continuous context evaluation, session anomaly monitoring, and endpoint controls.

Apr 14, 2026
Detection & Defense · bleepingcomputer.com

5 Ways Zero Trust Can Strengthen Identity Security

A sponsored guide outlines five Zero Trust practices for identity security, including least privilege, continuous device-aware authentication, limiting lateral movement, managing third-party access, and centralized governance.

Apr 14, 2026
Detection & Defense · thehackernews.com

IRONSCALES Executive Advocates Layered Email Defense Alongside Microsoft Defender

An IRONSCALES executive recommends augmenting Microsoft’s email protections with API-integrated behavioral detection, automated response, and targeted user training to address business email compromise and impersonation.

Apr 13, 2026
Detection & Defense · huntress.com

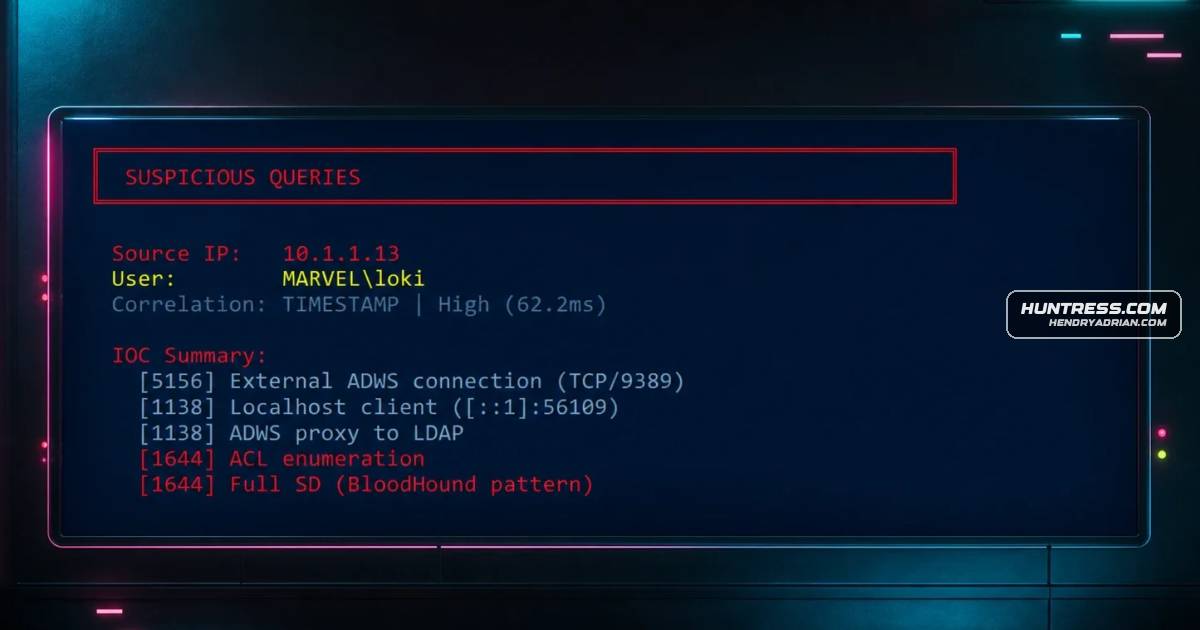
Correlating Windows Events 5156 and 1644 to Attribute ADWS Queries

A tested method correlates Windows Events 5156 and 1644 to attribute Active Directory Web Services LDAP queries to their source IP, using port matching when logs are retained or a roughly 60–80 ms time window.

Apr 9, 2026
Detection & Defense · huntress.com

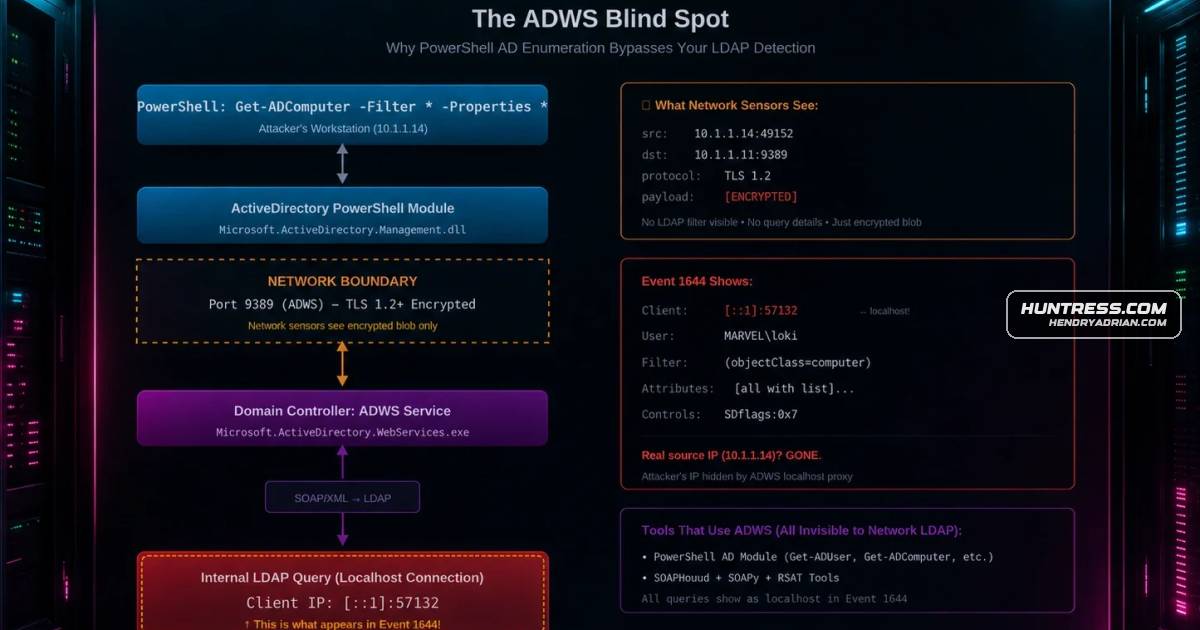
Correlating ADWS Events Can Detect PowerShell Active Directory Enumeration

Huntress describes how PowerShell AD enumeration over encrypted ADWS can evade network LDAP detection, and explains correlating domain-controller events to reveal queries, requested attributes and security-descriptor enumeration.

Apr 8, 2026
Detection & Defense · trendmicro.com

Fake Claude Code GitHub Releases Deliver Vidar, GhostSocks and PureLog Malware

Trend Micro reports that attackers used fake GitHub releases exploiting attention around a Claude Code packaging error to distribute Vidar, GhostSocks and PureLog Stealer. It offers detection guidance and recommendations to reduce exposure.

Apr 7, 2026
Detection & Defense · bleepingcomputer.com

Why Basic Credential Monitoring Falls Short Against Infostealers

Lunar-sponsored analysis argues that monthly checks and generic breach tools miss infostealer-derived credentials, session cookies and forensic context. It reports collecting 4.17 billion compromised-credential records in 2025 and recommends continuous monitoring, autom

Apr 6, 2026
Detection & Defense · toxsec.com

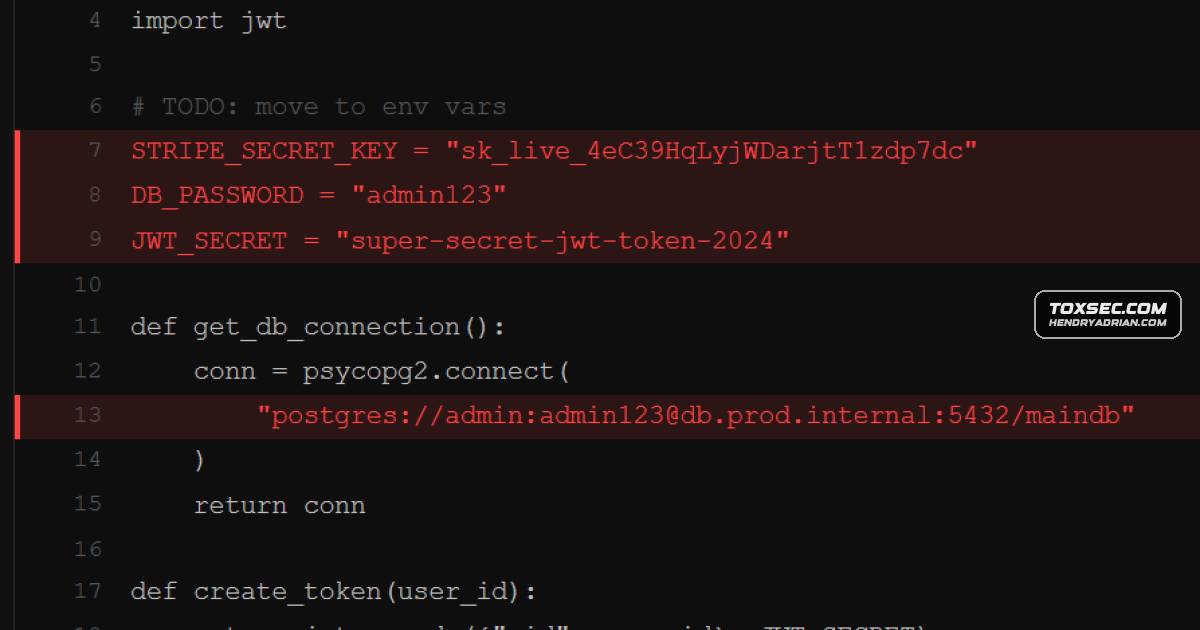
How to Prevent AI-Generated Code from Leaking Hardcoded Secrets

AI-generated code can expose hardcoded credentials in source files, Git history, and client-side bundles. The article recommends Gitleaks for pre-commit scanning, TruffleHog for deeper scans and credential verification, and rotating exposed keys.

Apr 5, 2026
Detection & Defense · microsoft.com

Microsoft Details PHP Webshell Tradecraft and Defender Hunting Guidance for Linux Hosting

Microsoft describes attackers using exposed web applications and hosting tools such as cPanel to deploy PHP webshells, encoded payloads and cron persistence on Linux hosts, and provides Defender detections, Copilot promptbooks and hunting queries.

Apr 2, 2026
Detection & Defense · cloud.google.com

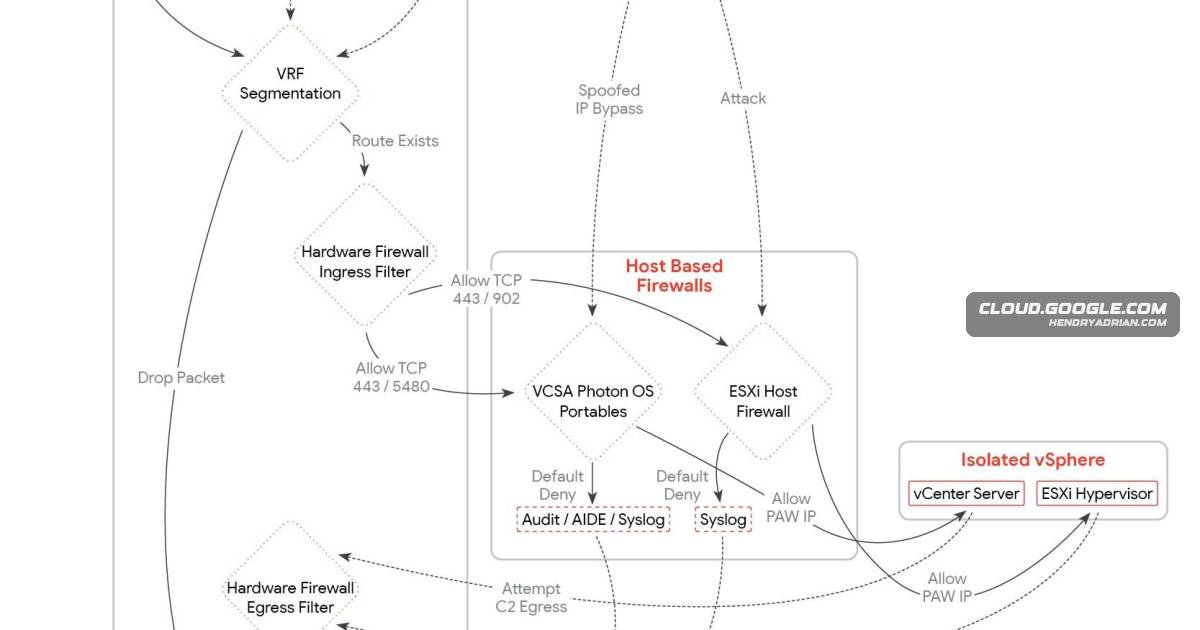
Guide Outlines Defenses Against BRICKSTORM Activity Targeting VMware vSphere

The guide presents four phases for hardening vCenter and ESXi against BRICKSTORM activity: baseline controls, privileged identity protections, network segmentation, and forensic visibility using Photon OS firewalls, auditd, AIDE, and remote logging.

Apr 2, 2026
Detection & Defense · elastic.co

Elastic Details Higher-Order Rules for Correlating Security Alerts

Elastic describes Higher-Order Rules that correlate endpoint, network, and observability alerts across entities and time to prioritize detections, with ES|QL examples, operational trade-offs, and reported alert-volume results.

Apr 1, 2026
PreviousPage 18 of 27 Next
© 2026 cyber.hendryadrian.com