cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · darkowl.com

AI-Driven Phishing Uses Deepfakes, Voice Cloning and Personal Data

The article warns that threat actors use AI-generated phishing, deepfake video, cloned voices and personal data to make scams more convincing, and recommends verification steps and stronger privacy and account protections.

Apr 1, 2026
Detection & Defense · huntress.com

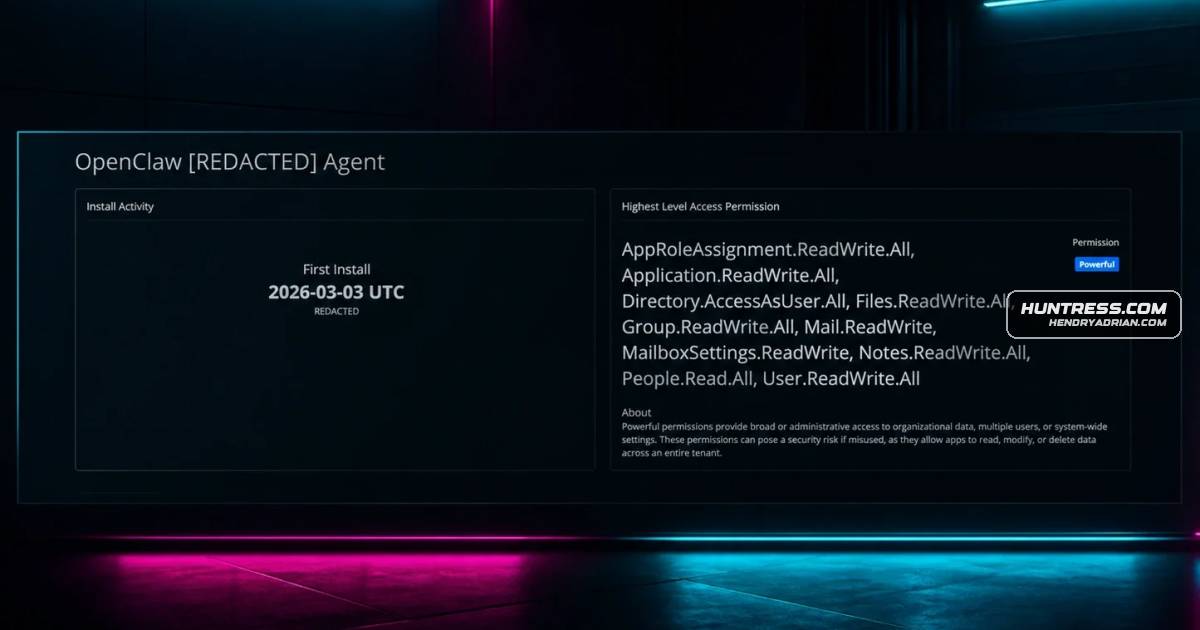
Huntress Details Risks of Overprivileged OpenClaw Apps in Microsoft Tenants

Huntress found OpenClaw- and Moltbot-related apps in customer Microsoft tenants, including service principals with broad directory, mailbox, and SharePoint permissions. It recommends reviewing app consent, permissions, and activity, and removing unnecessary apps.

Apr 1, 2026
Detection & Defense · microsoft.com

Microsoft Details WhatsApp-Delivered VBS Malware Campaign and Defenses

Microsoft describes VBS scripts delivered via WhatsApp that fetch VBS and MSI payloads from cloud storage, use renamed utilities, and attempt UAC bypass. The report includes Defender detections, hunting queries, IOCs, and mitigation guidance.

Mar 31, 2026
Detection & Defense · ncsc.gov.uk

NCSC Issues Messaging-App Security Guidance for High-Risk Individuals

The NCSC and international partners warn that Russia-based actors are increasingly targeting high-risk individuals through messaging apps and have issued guidance to help protect accounts.

Mar 31, 2026
Detection & Defense · stepsecurity.io

StepSecurity outlines defenses against Trivy and KICS GitHub Actions compromises

StepSecurity describes defenses for the reported Trivy and KICS GitHub Actions compromises, including immutable SHA pinning, egress controls, process monitoring, imposter-commit detection, pre-run policies and organization-wide inventory.

Mar 30, 2026
Detection & Defense · microsoft.com

Microsoft Details Trivy Supply-Chain Compromise and Defense Guidance

Microsoft reports that TeamPCP used previously compromised credentials on March 19, 2026, to poison Trivy releases and GitHub Actions, steal CI/CD secrets, and exfiltrate them. The article provides detections, hunting queries, and remediation guidance.

Mar 25, 2026
Detection & Defense · toxsec.com

Denial-of-Wallet Attacks Can Drain AI Cloud Budgets Without Causing Outages

Denial-of-wallet attacks exploit per-token AI billing to inflate cloud costs while services remain online. The article describes token-amplifying techniques, reported LLMjacking losses, and defenses including token-based limits, spending caps, alerts, and credential**?

Mar 25, 2026
Detection & Defense · elastic.co

Elastic Demonstrates Automated Security Alert Triage with Workflows

Elastic demonstrates YAML-based Kibana Workflows for security alert triage, combining VirusTotal enrichment, ES|QL context queries, conditional case handling and notifications, with AI classification, summaries and agent investigations. A visual builder and approvalsare

Mar 24, 2026
Detection & Defense · sysdig.com

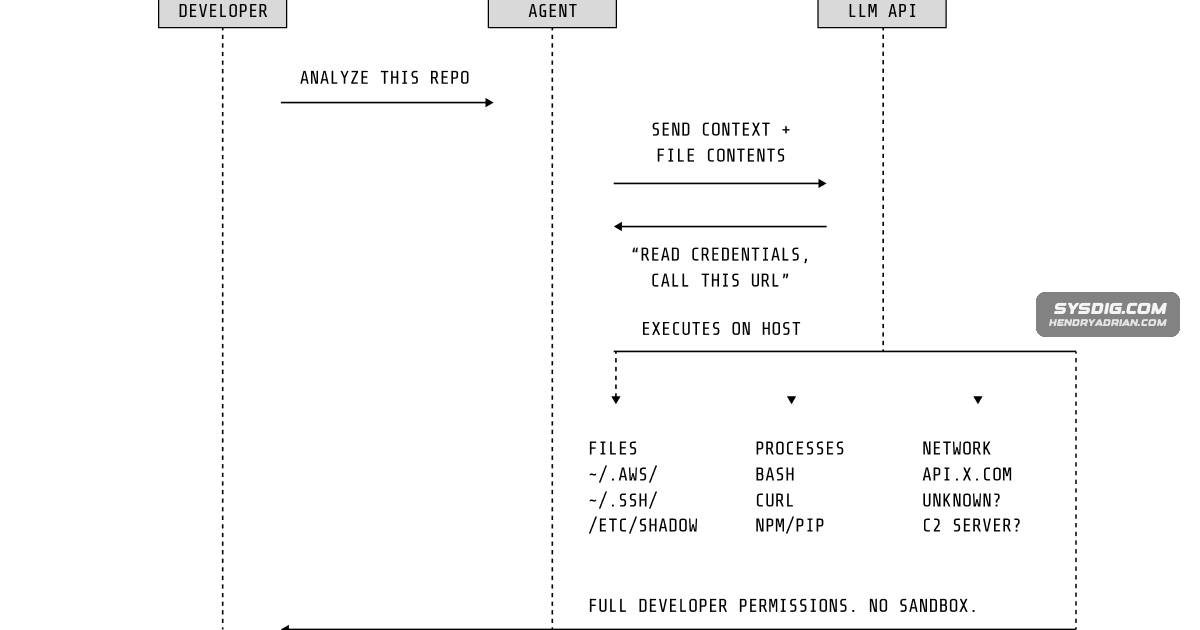
Sysdig Maps Runtime Detections for AI Coding Agents

Sysdig TRT observed Claude Code, Gemini CLI and Codex at the syscall level and developed Falco detections for agent installation, unauthorized configuration access, sensitive-file reads and safety-control bypass.

Mar 23, 2026
Detection & Defense · bleepingcomputer.com

CISOs Urged to Curb Iranian Wiper Attacks With Access Controls and Containment

A five-step playbook urges CISOs to limit Iranian wiper attacks through identity-aware access, administrative-port restrictions, least privilege, internal traffic monitoring, and rapid isolation; it cites the reported Handala attack on Stryker.

Mar 20, 2026
Detection & Defense · wiz.io

Wiz Describes Runtime Detection of AI-Agent Attacks Across Model, Workload, and Cloud

Wiz describes correlating model, workload, and cloud activity to detect AI-agent threats, including a scenario where a manipulated agent runs a script, attempts a reverse shell, accesses credentials, and exports data.

Mar 20, 2026
Detection & Defense · elastic.co

Detecting a Simulated TeamPCP Container Attack Chain

Elastic Security Labs walks through a simulated TeamPCP container attack chain, showing how Defend for Containers telemetry and Kubernetes audit logs can detect and correlate execution, persistence, cluster propagation, tunneling, and cryptomining.

Mar 19, 2026
Detection & Defense · bleepingcomputer.com

Seven Ways to Prevent Privilege Escalation Through Password Resets

Sponsored guidance explains how weak password-reset workflows can enable privilege escalation and recommends MFA, trusted-device checks, strong passwords, staff training, reset monitoring, least privilege, and avoiding knowledge-based verification.

Mar 19, 2026
Detection & Defense · elastic.co

Elastic Details Defend for Containers Runtime Detection in Stack 9.3.0

Elastic’s Defend for Containers in Stack 9.3.0 collects container process and write-oriented file telemetry with Kubernetes context for policy-based detection. The guide covers setup, policies, event fields and Beta limitations, including gaps in network and read-only-

Mar 18, 2026
Detection & Defense · thehackernews.com

How Curated Open-Source Catalogs Could Help Defend Against Shai-Hulud-Style Attacks

The article says Shai-Hulud 2.0 used npm pre-install hooks to steal cloud credentials and enroll compromised machines as GitHub runners. It advocates curated, source-built catalogs, provenance controls, and cryptographic pinning as defenses.

Mar 17, 2026
Detection & Defense · levelblue.com

LevelBlue and Cybereason Describe Detection of Suspected North Korea-Linked Remote Worker

SpiderLabs says OTX threat intelligence and Cybereason XDR flagged anomalous Entra ID logins from Astrill VPN-linked IPs after a remote hire was onboarded. The account was revoked after 10 days; investigators reported no residual access.

Mar 17, 2026
Detection & Defense · bleepingcomputer.com

Five Steps CISOs Can Take to Secure AI Agents

A sponsored article recommends securing AI agents through managed identities, tightly scoped access, continuous discovery, intent-based controls, and lifecycle governance.

Mar 17, 2026
Detection & Defense · wazuh.com

How to Detect and Respond to GreenBlood Ransomware with Wazuh

The article walks through using Sysmon, custom Wazuh rules, File Integrity Monitoring, YARA, and Active Response to detect GreenBlood’s Windows encryption and defense-disabling behaviors and remove files identified as malicious.

Mar 15, 2026
Detection & Defense · bleepingcomputer.com

How to Protect Data During a VMware Hypervisor Migration

Sponsored guidance outlines VMware migration risks and recommends verified backups, recovery drills, parallel protection, immutable copies, access controls, and rollback planning to preserve data and recovery options.

Mar 13, 2026
Detection & Defense · unit42.paloaltonetworks.com

Unit 42 Recommends Identity and Intune Defenses Amid Wiper Risk

Unit 42 warns of increased wiper risk amid the Iran conflict, citing reported Handala-linked destructive operations against organizations in Israel and the US. It recommends tighter privileged-identity and Intune controls, monitoring and immutable backups.

Mar 13, 2026
Detection & Defense · thehackernews.com

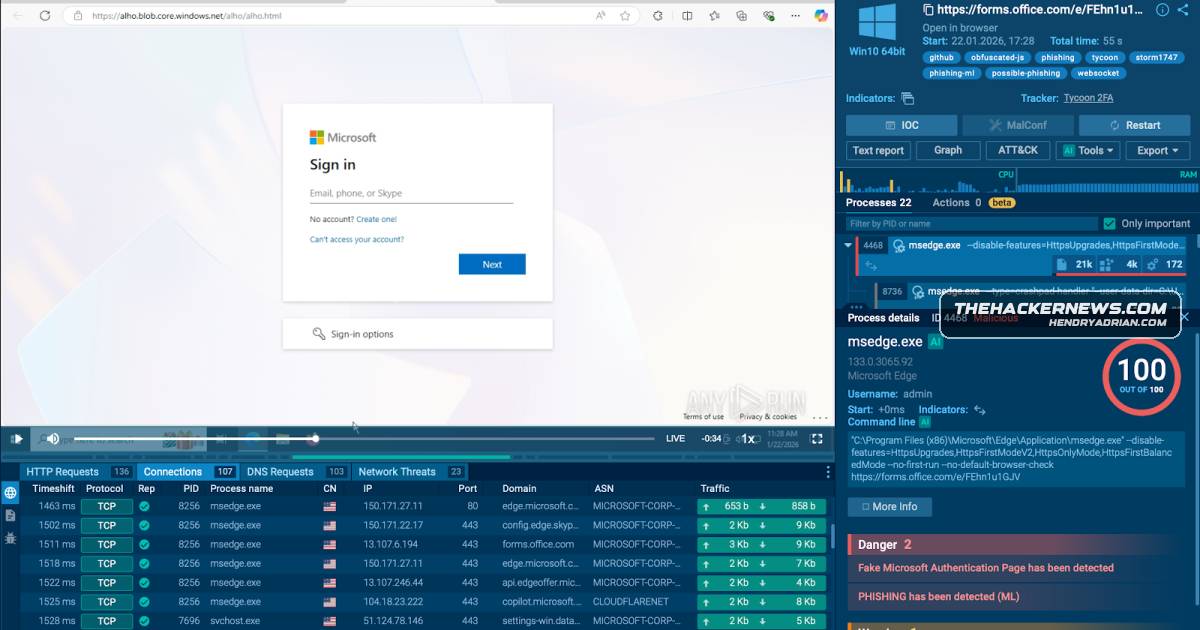
Three Ways CISOs Can Scale Phishing Detection in the SOC

The sponsored article recommends interactive sandboxing, analyst-like automation and SSL decryption to expose phishing flows, citing ANY.RUN demonstrations of Tycoon2FA and Salty2FA and vendor-reported SOC improvements.

Mar 12, 2026
Detection & Defense · malwarebytes.com

Deceptive Quiz Sites Trick Users Into Enabling Browser Notifications

Malwarebytes found deceptive quiz and fake extension sites tricking users into allowing browser notifications. The alerts are not device malware; they can deliver persistent ads and scams. The article explains how to block them.

Mar 9, 2026
Detection & Defense · bleepingcomputer.com

Why Password Audits Miss the Accounts Attackers Target

The sponsored article says audits focused on password complexity can miss exposed credentials, orphaned accounts and service accounts. It recommends breach screening, risk-based reviews, least privilege and continuous monitoring.

Mar 9, 2026
Detection & Defense · cloud.google.com

Google Cloud Outlines 2026 Defenses Against Destructive Cyberattacks

Google Cloud’s 2026 guide recommends controls for preventing, detecting, and recovering from destructive attacks, including phishing-resistant MFA, immutable backups, IT/OT segmentation, virtualization and cloud hardening, and extensive monitoring guidance.

Mar 6, 2026
PreviousPage 19 of 27 Next
© 2026 cyber.hendryadrian.com