cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

625 articles

Detection & Defense · thehackernews.com

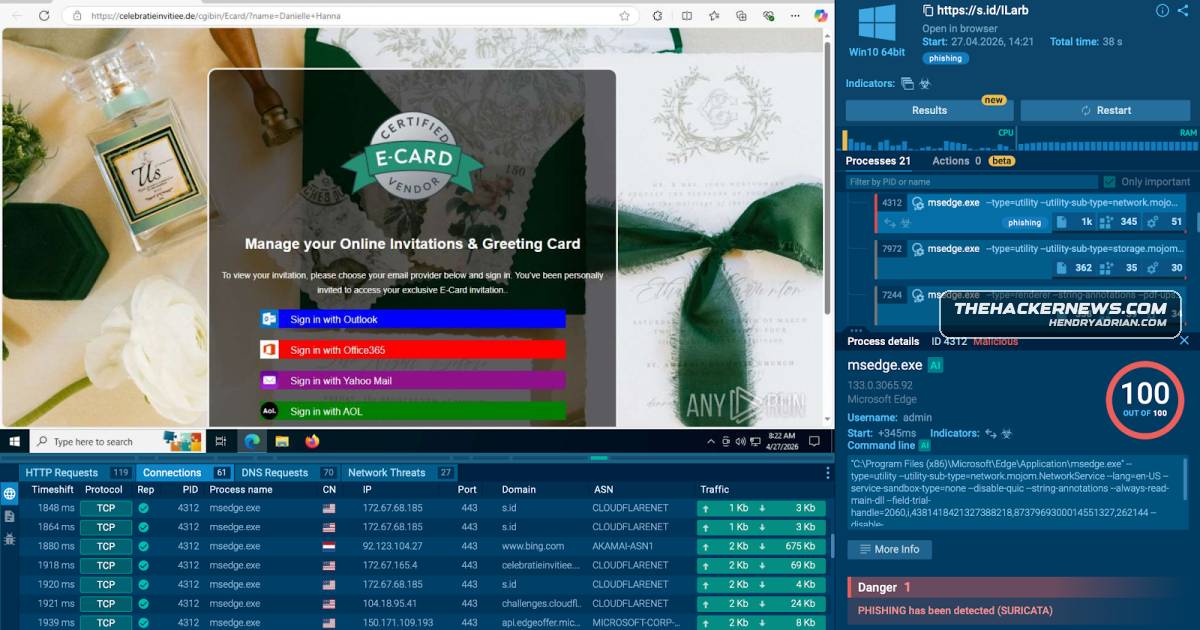
How SOC Teams Can Investigate Phishing with Sandboxing and Threat Intelligence

A sponsored article describes an ANY.RUN analysis of a fake-invitation phishing campaign targeting U.S. organizations and outlines using sandboxing and threat intelligence to find related activity and inform SOC response.
May 18, 2026
Detection & Defense · bleepingcomputer.com

Five Steps to Manage Shadow AI Without Slowing Employees

The sponsored guide recommends inventorying AI tools and their OAuth permissions, setting approved-tool and data-use policies, speeding reviews, monitoring browser activity, and coaching employees to reduce shadow AI exposure.

May 18, 2026
Detection & Defense · huntress.com

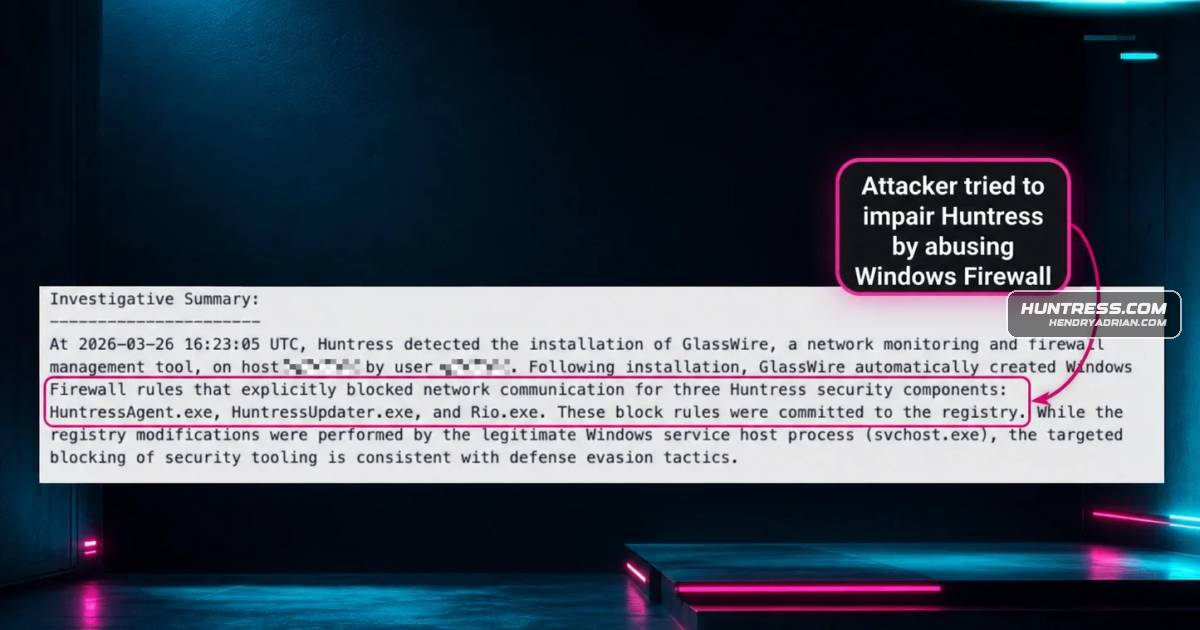
How Attackers Disable AV and EDR—and How to Defend Against It

Attackers use firewall rules, agent removal, and BYOVD to disable endpoint defenses. Huntress describes detection and remediation measures and cites 2026 incidents involving EnCase and Huawei drivers.

May 18, 2026
Detection & Defense · ic3.gov

FBI Warns of ShinyHunters Extortion Risks After LMS Disruption

The FBI says ShinyHunters claimed an attack that disrupted an online learning management system, which is now operational. It warns of possible extortion and spearphishing risks and advises verifying contacts, avoiding payment, and reporting suspected incidents.

May 15, 2026
Detection & Defense · toxsec.com

How to Secure AI-Generated Code: Three Checks for Vibe Coding

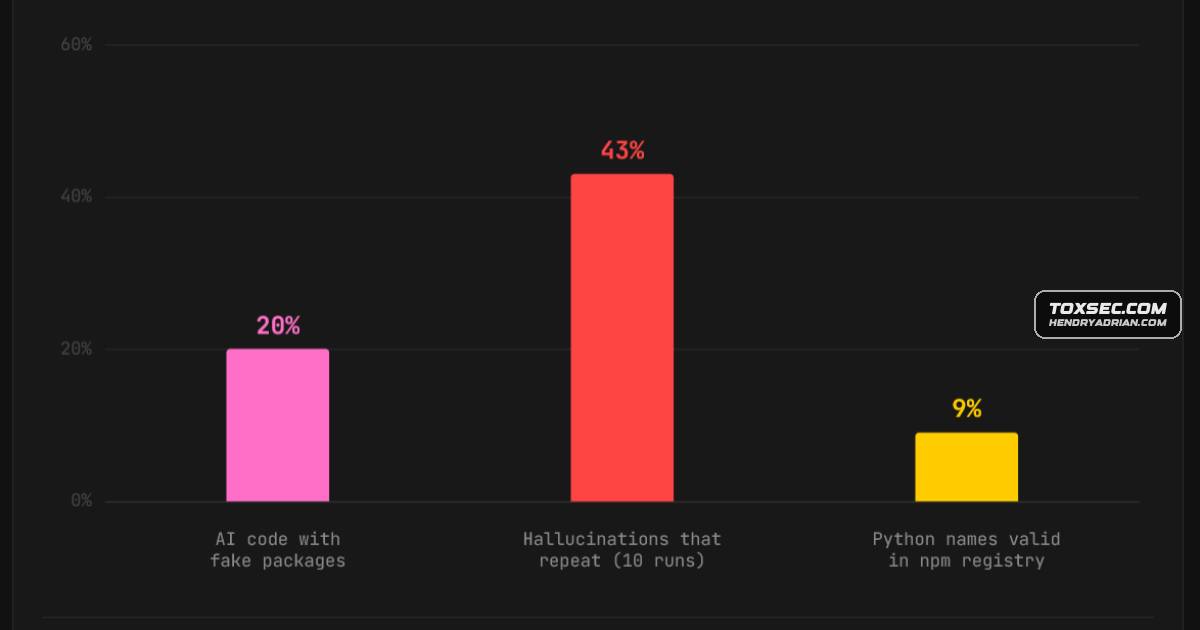
AI coding can introduce hardcoded secrets, hallucinated dependencies and insecure code. The article recommends secret scanning, package checks, security rules and Semgrep, while noting logic flaws still need human review or dynamic testing.

May 15, 2026
Detection & Defense · opensourcemalware.com

How Malware Abuses npm Lifecycle Scripts and VS Code Tasks

The article explains how malicious packages and repositories abuse automatic npm scripts and VS Code tasks to run malware, then outlines ways to reduce risk, including disabling scripts or task autoruns by default and reviewing untrusted repositories.

May 14, 2026
Detection & Defense · cyberbuilders.substack.com

How Security Teams Can Prepare for AI-Accelerated Cyber Threats

The article argues that AI speeds up vulnerability discovery and attacks but does not replace core security work. It recommends strengthening continuous vulnerability management, MFA, segmentation, automation, and governance.

May 13, 2026
Detection & Defense · bleepingcomputer.com

Why Password Resets Alone May Not Evict Attackers from Active Directory

Password resets may leave cached hashes, active Kerberos tickets, service-account credentials, forged tickets, or malicious AD permissions usable. The sponsored guide recommends terminating sessions, resetting KRBTGT twice for serious compromises, rotating credentials,,

May 11, 2026
Detection & Defense · elastic.co

Elastic Details Detection and Mitigation for Linux Copy Fail and DirtyFrag Bugs

Elastic Security Labs describes detection and mitigation for the Linux privilege-escalation bugs Copy Fail, Copy Fail 2, and DirtyFrag. Copy Fail is reported exploited in the wild; guidance includes syscall-based detection, kernel patching, and targeted hardening.

May 9, 2026
Detection & Defense · elastic.co

Guide Uses Elastic and Cloudflare to Block Traefik Scanners

The guide uses Elastic Security to detect Traefik probing from repeated 403 and 404 responses, then automatically blocks source IPs through a Cloudflare WAF workflow. It also explains how to reuse the response for other detections.

May 9, 2026
Detection & Defense · wiz.io

Wiz Outlines a Four-Pillar Framework for AI-Era Threat Readiness

Wiz proposes a defensive framework for faster AI-era vulnerability response: reduce exposure, accelerate patching, use AI for deeper code analysis, and automate threat investigation and containment.

May 8, 2026
Detection & Defense · bleepingcomputer.com

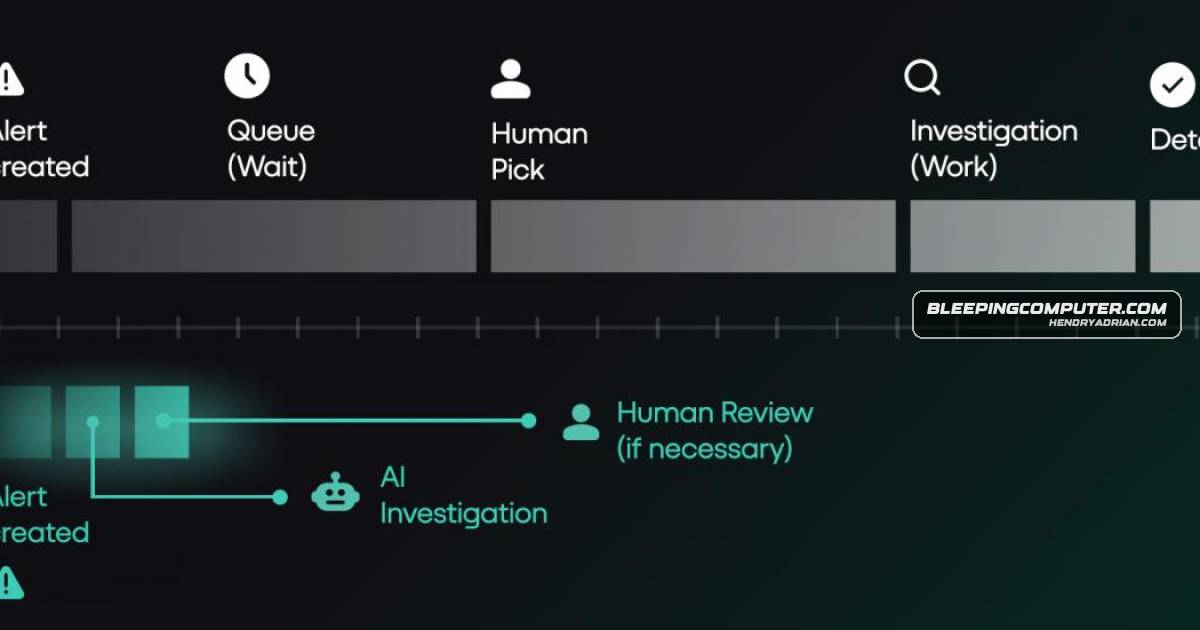
Why Hiring More SOC Analysts May Not Fix Alert Backlogs

A sponsored Prophet Security article argues that SOC alert backlogs require operating-model changes, not just more hires. It offers a capacity diagnostic, reports vendor customer results, and outlines cases where human-led investigations remain important.

May 8, 2026
Detection & Defense · wiz.io

Practical Defenses Against Malicious Package Updates

A practical guide to reducing package supply-chain risk through dependency minimization, update cooldowns, lockfiles, restricted install scripts, registry controls, isolated environments, and honeytokens.

May 4, 2026
Detection & Defense · wazuh.com

Wazuh Guide Demonstrates Detecting Kubernetes Attacks with Audit Logs

A Wazuh guide configures Kubernetes audit logging and custom rules, then uses Stratus Red Team to emulate credential theft, RBAC abuse, privilege escalation and container-breakout techniques and validate alerts.

May 2, 2026
Detection & Defense · elastic.co

Elastic Demonstrates Osquery-Based DFIR From Alert to Root Cause

Elastic demonstrates using Osquery and Elastic Security to reconstruct an illustrative phishing-to-Mimikatz execution from endpoint artifacts without a disk image, then reuse forensic queries as scheduled detections.

May 2, 2026
Detection & Defense · crowdstrike.com

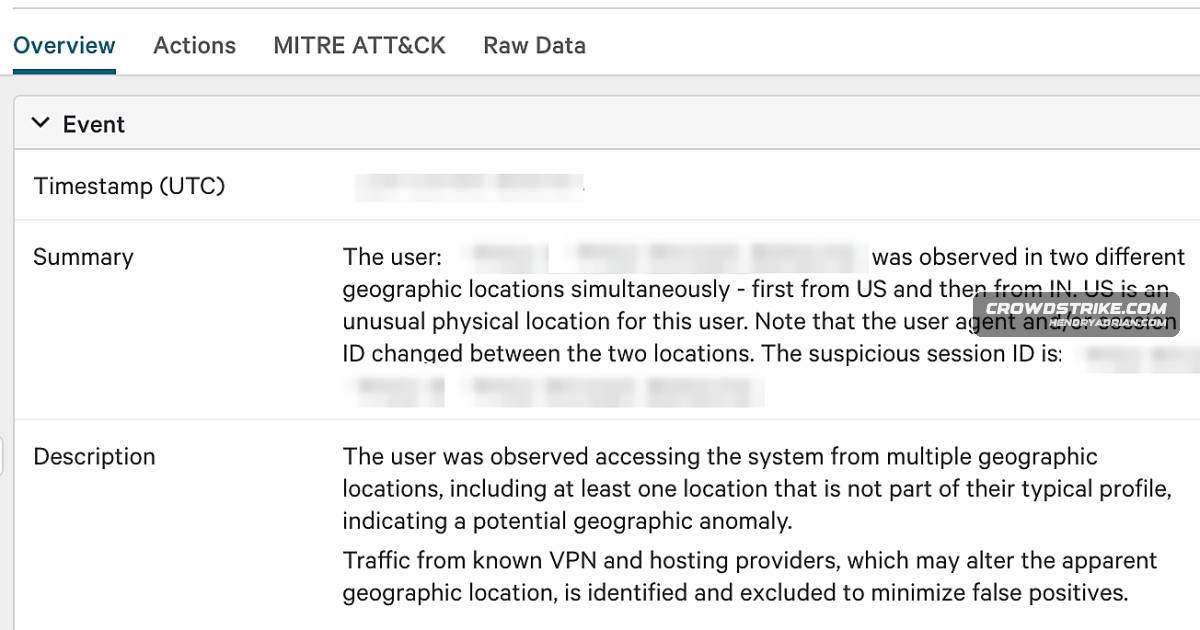
CrowdStrike Details SaaS Intrusions by CORDIAL SPIDER and SNARKY SPIDER

CrowdStrike says CORDIAL SPIDER and SNARKY SPIDER use vishing and AiTM pages to steal IdP credentials and session tokens, manipulate MFA, hide alerts, and rapidly exfiltrate SaaS data; it outlines Falcon Shield detections and configuration defenses.

May 1, 2026
Detection & Defense · elastic.co

Elastic Open-Sources CI/CD Abuse Detector Using Regex Signals and Claude Analysis

Elastic Security Labs open-sourced cicd-abuse-detector, a CI template combining 50+ regex and metadata signals with Claude analysis to flag suspicious workflow changes across GitHub Actions, GitLab CI, and Azure DevOps.

Apr 29, 2026
Detection & Defense · bleepingcomputer.com

Vercel Breach Highlights Risks of Shadow AI and OAuth Sprawl

The sponsored article argues that employee-approved OAuth links to AI and other SaaS apps can expose enterprise accounts, using Vercel’s fallout from Context.ai as an example, and recommends restricting consent and auditing integrations across SaaS.

Apr 29, 2026
Detection & Defense · toxsec.com

Slopsquatting Targets AI-Hallucinated Package Names; slopcheck Screens Dependencies

Attackers can register package names hallucinated by AI coding assistants and add malicious install hooks. A 2025 study found nearly 20% of sampled AI-generated code referenced nonexistent packages; the article describes slopcheck’s registry checks and CI controls.

Apr 28, 2026
Detection & Defense · hackingarticles.in

Using EVENmonitor to Detect Active Directory Attacks in Real Time

A hands-on guide shows how EVENmonitor streams Domain Controller Security logs over MS-EVEN6 and maps Windows event IDs and forensic fields to detect common Active Directory attacks, from DCSync and credential attacks to account and group changes.

Apr 27, 2026
Detection & Defense · elastic.co

Elastic Details OpenTelemetry Monitoring for Claude Code and Cowork

Elastic’s InfoSec team describes collecting Claude Code and Cowork OpenTelemetry data in Elasticsearch for agent auditing, session reconstruction, permission analysis, and EDR correlation, with self-managed and managed ingestion options.

Apr 25, 2026
Detection & Defense · bleepingcomputer.com

How DORA’s Article 9 Shapes Credential Management for Financial Firms

A sponsored Passwork article explains how DORA Article 9 applies to credential controls, recommending phishing-resistant MFA, least privilege, credential vaulting and continuous monitoring, then promotes Passwork’s self-hosted password manager and audit features.

Apr 24, 2026
Detection & Defense · wazuh.com

Using Wazuh to Detect and Respond to BQTLock Ransomware

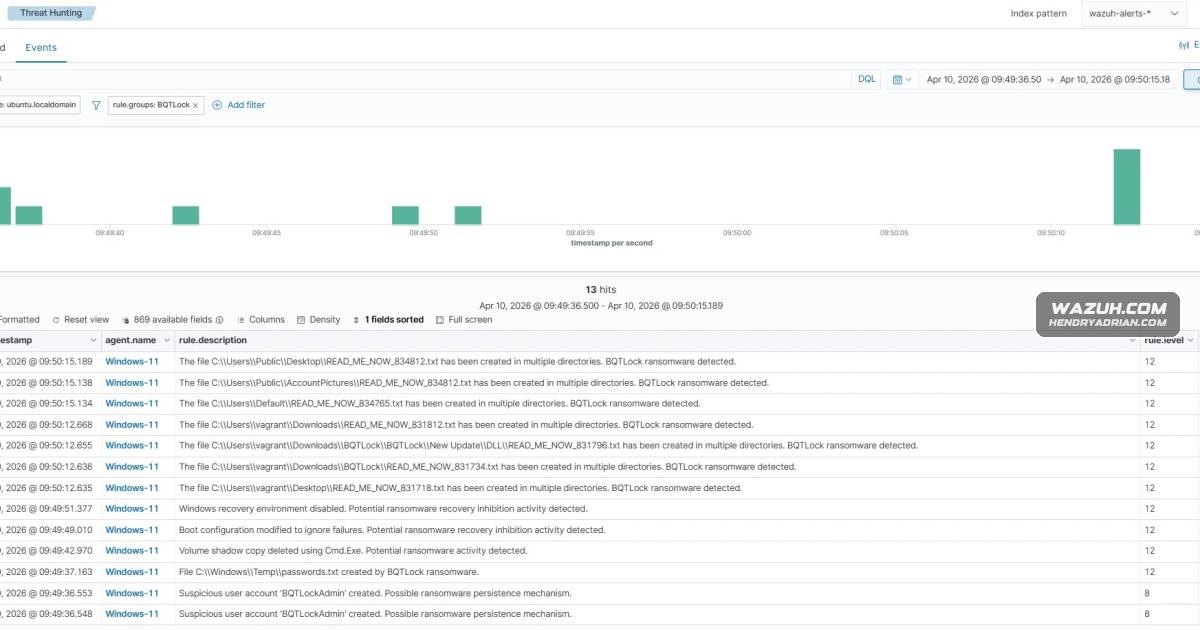
A Wazuh guide shows how to detect BQTLock activity on Windows using Sysmon, custom rules and hash lists, then configure Active Response to remove detected files.

Apr 23, 2026
Detection & Defense · cisa.gov

Agencies Urge Defenses Against China-Nexus Covert Networks of Compromised Devices

A joint advisory describes China-nexus actors’ use of dynamic networks of compromised routers and IoT devices, and recommends monitoring, access controls, and active hunting to defend against them.

Apr 23, 2026
PreviousPage 17 of 27 Next
© 2026 cyber.hendryadrian.com