
Unit 42 Details CL-STA-1087 Espionage Campaign Targeting Southeast Asian Militaries
Summary
Unit 42 describes CL-STA-1087, a suspected China-linked espionage cluster active in Southeast Asian military networks since at least 2020, using custom tools to maintain access and collect targeted C4I-related intelligence.
Key points
- Unit 42 attributes a campaign dating to at least 2020 to CL-STA-1087, which targeted Southeast Asian military organizations.
- The cluster reportedly sought specific files on military capabilities, organizational structures, and cooperation with Western armed forces rather than bulk data.
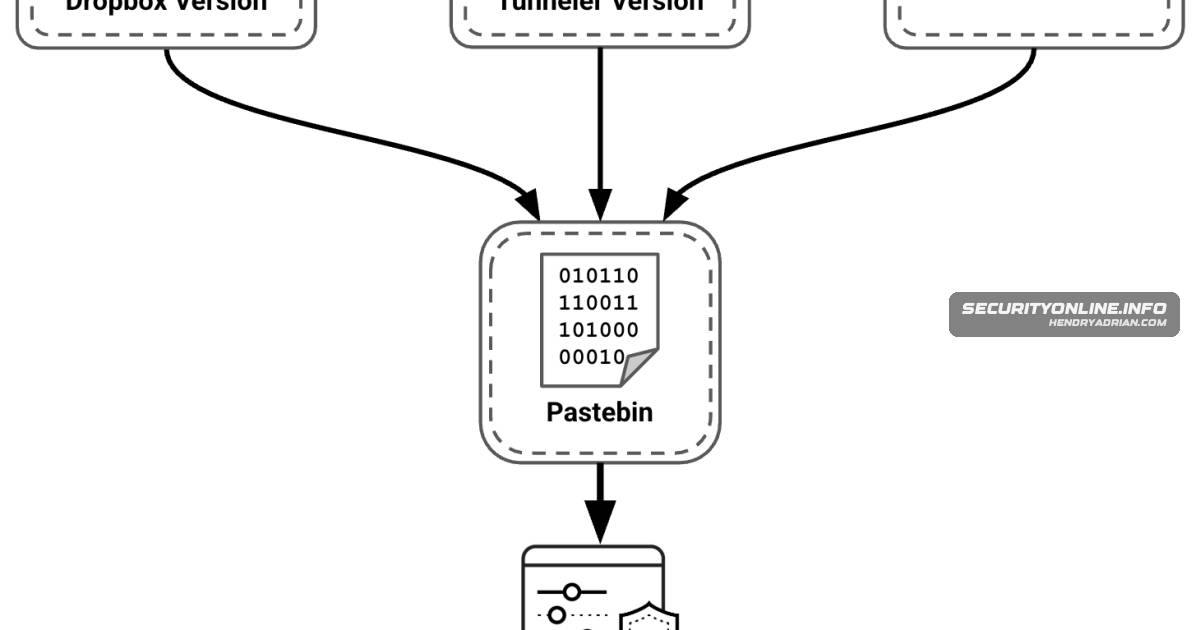
- AppleChris used custom HTTP verbs and a dead drop resolver to conceal command-and-control traffic.
- MemFun used in-memory execution, process hollowing, and anti-forensic checks; Getpass harvested plaintext passwords and NTLM hashes.
- The investigation describes timestomping, sleep timers of up to 120 seconds, and dormant periods as stealth and persistence measures.
- Unit 42 assesses the cluster as probably China-linked, citing China-based infrastructure, Simplified Chinese on C2 login pages, and activity aligned with UTC+8 business hours.
Article Details
- Attack Vectors
- The cluster used custom HTTP verbs and a dead drop resolver to conceal AppleChris command-and-control traffic.
- MemFun used process hollowing to run malicious code under the guise of legitimate Windows processes.
- Getpass harvested plaintext passwords and NTLM hashes.
- The attackers used timestomping and sleep timers of up to 120 seconds to evade detection and automated sandboxes.
- The attackers searched for and collected files about military capabilities, organizational structures, and collaboration with Western armed forces.
MITRE ATT&CK
T1003 · OS Credential DumpingGetpass harvested plaintext passwords and NTLM hashes; the article describes it as a custom version of Mimikatz.T1005 · Data from Local SystemThe attackers collected targeted files concerning military capabilities, organizational structures, and collaboration with Western armed forces.T1055.012 · Process HollowingMemFun used process hollowing to run malicious code under the guise of legitimate Windows processes.T1059.001 · PowerShellCortex XDR agents detected suspicious PowerShell activity on networks where the attackers had established a foothold.T1070.006 · TimestompSome variants used timestomping to make malicious files appear as old as legitimate system files.T1071.001 · Web ProtocolsAppleChris used custom HTTP verbs for command-and-control traffic.T1083 · File and Directory DiscoveryThe attackers searched for specific files concerning military capabilities, organizational structures, and collaboration with Western armed forces.T1102.001 · Dead Drop ResolverAppleChris used a dead drop resolver to hide its command-and-control traffic.T1497.003 · Time Based ChecksSome variants used sleep timers of up to 120 seconds to outlast automated security sandboxes.
Threat Actors
Malware
AppleChrisThe group practices strategic operational patience and uses custom tools like AppleChris, MemFun, and Getpass to target C4I systems and harvest highly specific military intelligence.GetpassThe group practices strategic operational patience and uses custom tools like AppleChris, MemFun, and Getpass to target C4I systems and harvest highly specific military intelligence.MemFunThe group practices strategic operational patience and uses custom tools like AppleChris, MemFun, and Getpass to target C4I systems and harvest highly specific military intelligence.
Products
Cortex XDRThe investigation began when Cortex XDR agents detected suspicious PowerShell activity on networks where the attackers had already established a foothold.Microsoft WindowsMemFun Backdoor: A multi-stage, in-memory platform that employs “anti-forensic checks” and “process hollowing” to run malicious code under the guise of legitimate Windows processes.