
Socket Finds Six Malicious Packagist Themes Bundling Trojanized JavaScript
Summary
Socket researchers identified six malicious ophimcms Composer themes on Packagist that bundle JavaScript for URL exfiltration, redirects, ad injection and click hijacking. One redirect chain uses infrastructure linked to FUNNULL.
Key points
- The six malicious ophimcms themes distribute their payloads in bundled JavaScript, often disguised as jQuery; the article says the PHP code is not malicious.
- One payload sends current page URLs to userstat[.]net; this chain has no geographic restriction, and the article says its attribution to FUNNULL is unconfirmed.
- A separate payload in theme-dy loads a second stage from union[.]macoms[.]la and redirects qualifying mobile visitors, with checks including local time, referrer and administrator cookies.
- Other analyzed behaviors include ad injection, click hijacking, full-screen ad overlays, unauthorized analytics and anti-debugging.
- Socket links the union[.]macoms[.]la payload to FUNNULL using previously documented infrastructure indicators and reports it was updated on March 10, 2026.
- The article reports approximately 2,750 total installs across the six packages and says Socket submitted takedown requests.
- Recommended steps include removing affected themes, auditing bundled JavaScript and checking outbound requests for the identified infrastructure.
Article Details
- Attack Vectors
- Six malicious Composer packages under the ophimcms namespace on Packagist distribute trojanized JavaScript assets disguised as legitimate libraries.
- The bundled JavaScript loads a second-stage payload from union[.]macoms[.]la, redirecting qualifying mobile visitors to gambling and adult content.
- JavaScript in theme-dy, theme-mtyy, and theme-rrdyw sends the visitor's current page URL to userstat[.]net.
- Other package payloads inject desktop or mobile ads, hijack clicks, and load third-party ad scripts.
- The theme-motchill payload displays a full-screen ad overlay; theme-legend uses anti-debugging behavior and redirects when developer tools are detected.
- Defensive Notes
- Remove affected themes and audit bundled JavaScript, including code appended after a library's closing IIFE or injected into the Sizzle engine.
- Audit outbound requests for userstat[.]net, union[.]macoms[.]la, 23[.]225[.]52[.]67:4466, and cre-ads[.]com.
- Check localStorage for keys prefixed MPAd_ and notify users if an affected theme was deployed because their browsing activity may have been exfiltrated.
- Flag Composer packages that bundle JavaScript vendor libraries without integrity verification, and monitor for the reported Caesar-cipher and custom Base64 obfuscation patterns.
- Treat domains resolving through .nqsaaskw[.]com CNAMEs as FUNNULL infrastructure, as recommended by the article.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cre-ads[.]com | Ad-network domain whose external script is loaded by the theme-pcc click-hijacking payload. |
| DOMAIN | dxtv1[.]com | Identified as a FUNNULL device-routing redirect hub. |
| DOMAIN | im[.]ue8im[.]com | Ad-image hosting domain used by the theme-rrdyw desktop ad-injection payload. |
| DOMAIN | union[.]macoms[.]la | FUNNULL-attributed second-stage payload and mobile redirect infrastructure. |
| DOMAIN | userstat[.]net | URL-exfiltration C2 domain receiving the current page URL from injected JavaScript. |
dev@ophim[.]cc | Package-publisher email attributed in the article to packages carrying FUNNULL-linked payloads. | |
opdlnf01@gmail[.]com | Package-publisher email attributed in the article to packages carrying ad-injection, click-hijacking, and anti-debugging payloads. | |
| HOSTNAME | b0ca39f0[.]nqsaaskw[.]com | Intermediate hostname in the reported DNS route for union[.]macoms[.]la, associated with FUNNULL infrastructure. |
| HOSTNAME | g941875[.]cdn[.]nqsaaskw[.]com | Reported DNS destination in the routing chain for union[.]macoms[.]la, associated with FUNNULL CDN infrastructure. |
| HOSTNAME | oss-cn-guangzhou[.]ailyunoss[.]com | Alibaba Cloud typosquat identified in the FUNNULL redirect chain. |
| SHA256 | fdfcbf04343f4eb89bab9eaf40fee178d9002a42c7949c9bbd24c0e8831a04b0 | SHA-256 hash identified for the malicious union[.]macoms[.]la/jquery.min-3.6.8.js payload. |
| URL | hxxp[:]//23[.]225[.]52[.]67:4466/vip344[.]html | Hardcoded ad-injection C2 endpoint used by the injected desktop ad script. |
| URL | hxxps[:]//cre-ads[.]com/G0bJZf9Uj1 | Specific external ad script loaded by the click-hijacking payload. |
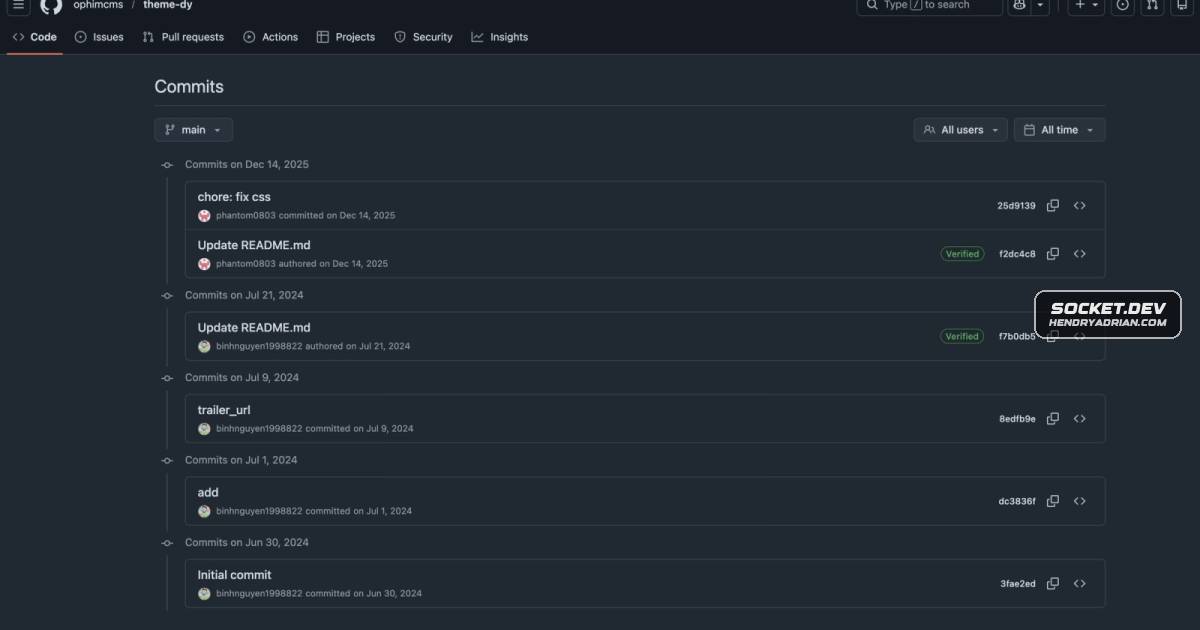
| URL | hxxps[:]//github[.]com/binhnguyen1998822 | GitHub account linked through commit history to creation of theme-dy, which contains malicious payloads. |
| URL | hxxps[:]//github[.]com/ophimcms | GitHub organization through which the article reports the malicious packages were published. |
| URL | hxxps[:]//github[.]com/phantom0803 | GitHub account linked through commit history to the package organization and malicious package operation. |
| URL | hxxps[:]//union[.]macoms[.]la/jquery.min-3.6.8.js | Specific URL from which the FUNNULL-linked second-stage JavaScript payload is fetched. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe FUNNULL second-stage payload uses rotating strings, Base64 and RC4 encryption, and wrapper functions with offset indirection.T1041 · Exfiltration Over C2 ChannelInjected JavaScript sends the current page URL to userstat[.]net as a query parameter when loading a remote script.T1059.007 · JavaScriptInjected JavaScript executes in visitors' browsers to exfiltrate page URLs, inject ads, hijack clicks, and redirect users.T1195.002 · Compromise Software Supply ChainMalicious Composer packages published under the ophimcms namespace on Packagist delivered trojanized JavaScript assets.T1204.001 · Malicious LinkThe theme-pcc payload hijacks clicks on page links, opening the intended destination in a new tab while redirecting the current window to an ad URL.T1583.008 · MalvertisingThe article attributes redirect and malvertising infrastructure, including union[.]macoms[.]la, to FUNNULL-operated infrastructure.
Threat Actors
binhnguyen1998822The article links this GitHub account through commit history to creating theme-dy, which carried malicious payloads; it notes the operation may involve collaborating account operators or one operator using multiple accounts.FUNNULLThe article attributes union[.]macoms[.]la and related redirect infrastructure to FUNNULL and reports its infrastructure was used in this malicious package campaign.phantom0803The article links this GitHub account through commit history to the package organization and reports it later contributed to theme-dy, which carried malicious payloads; it leaves open whether the accounts represent collaborators or one operator using multiple accounts.
Vendors
Products
ComposerSocket’s Threat Research Team identified six malicious Composer packages under the ophimcms namespace on Packagist that bundle trojanized JavaScript (disguised as jQuery) to exfiltrate URLs, inject ads, hijack clicks,OphimCMSSocket’s Threat Research Team identified six malicious Composer packages under the ophimcms namespace on Packagist that bundle trojanized JavaScript (disguised as jQuery) to exfiltrate URLs, inject ads, hijack clicks,PackagistSocket’s Threat Research Team identified six malicious Composer packages under the ophimcms namespace on Packagist that bundle trojanized JavaScript (disguised as jQuery) to exfiltrate URLs, inject ads, hijack clicks,